

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 paradoxis/dnsrpc-bof
Beacon Object File (BOF) implementation of the dnscmd.exe functionality used to obtain remote code execution on an ADIDNS server by exploiting the…
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
 flatl1neapt/cve-2018-15982
Flash sources for CVE-2018-15982 used by NK
 hypnguyen1209/cve-2026-62911
Proof-of-concept exploit for CVE-2026-62911: pre-auth RCE on Microsoft Exchange via NTLM relay to MRSProxy, writing an ASPX webshell for SYSTEM…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
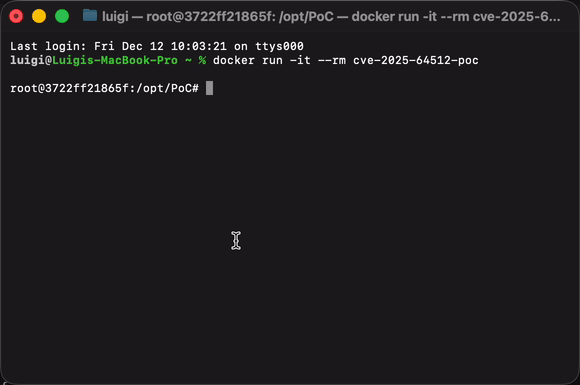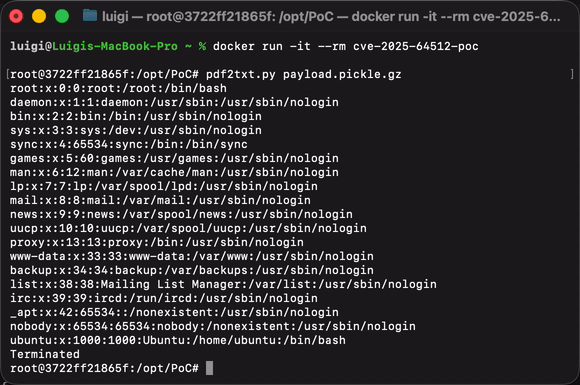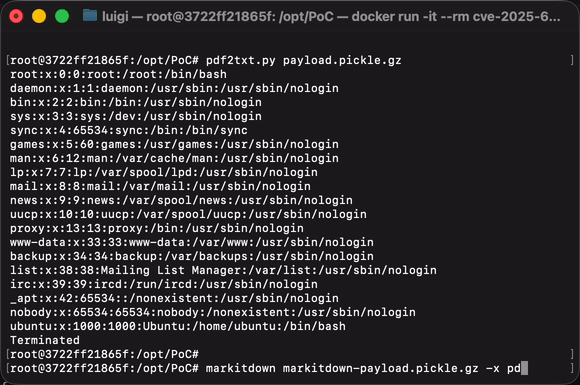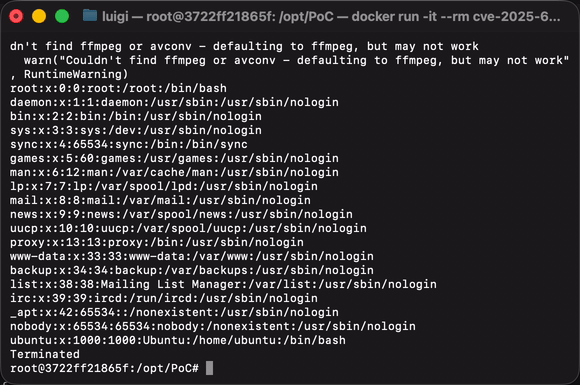 luigigubello/cve-2025-64512-polyglot-poc
A Proof-of-Concept for CVE-2025-64512 using a polyglot file.
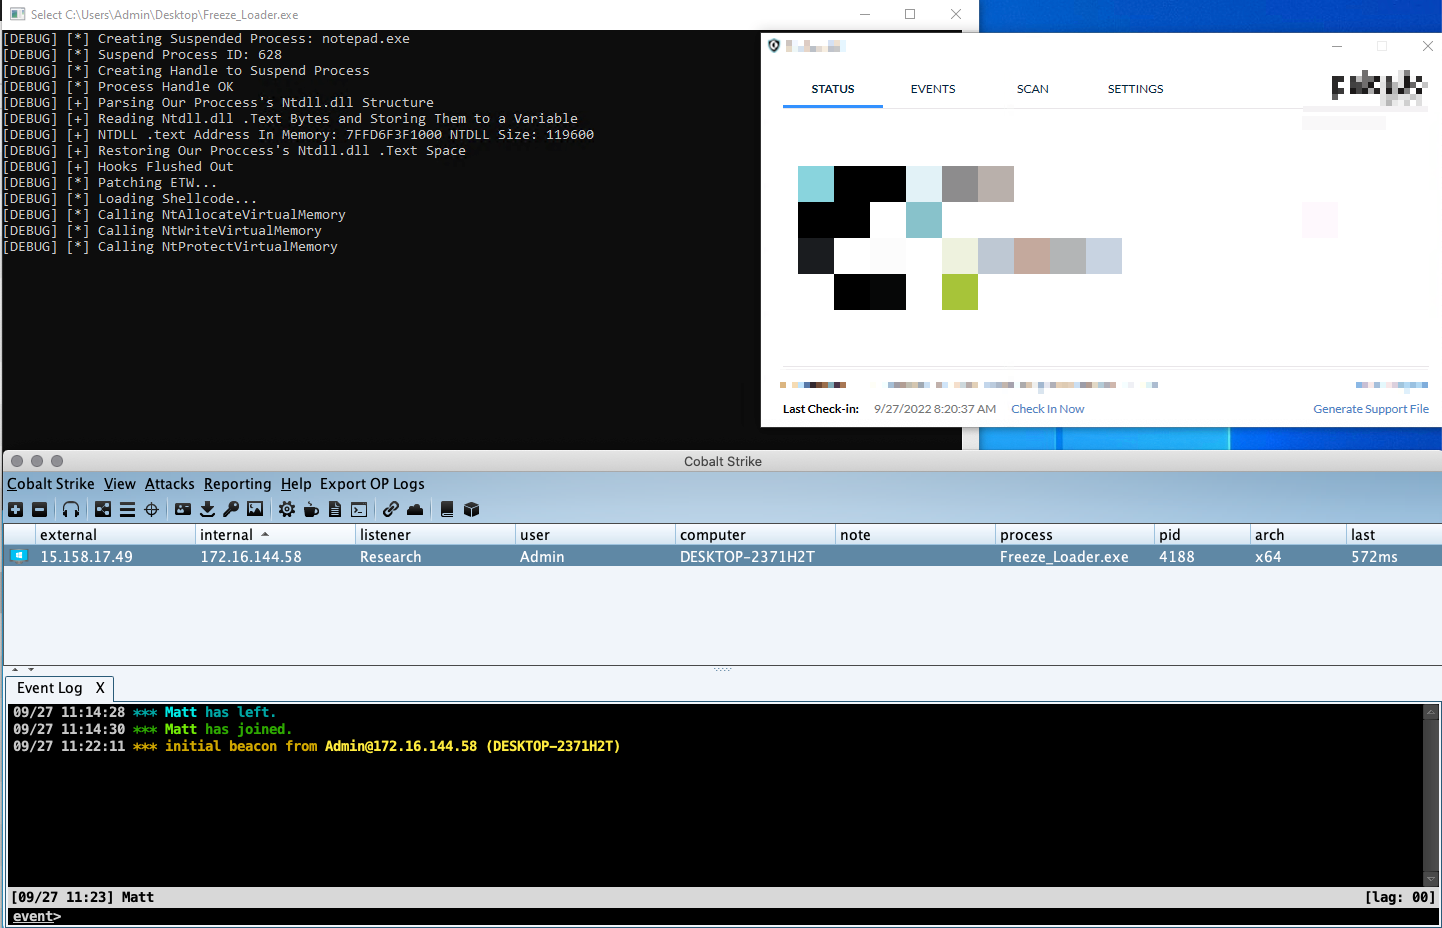 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
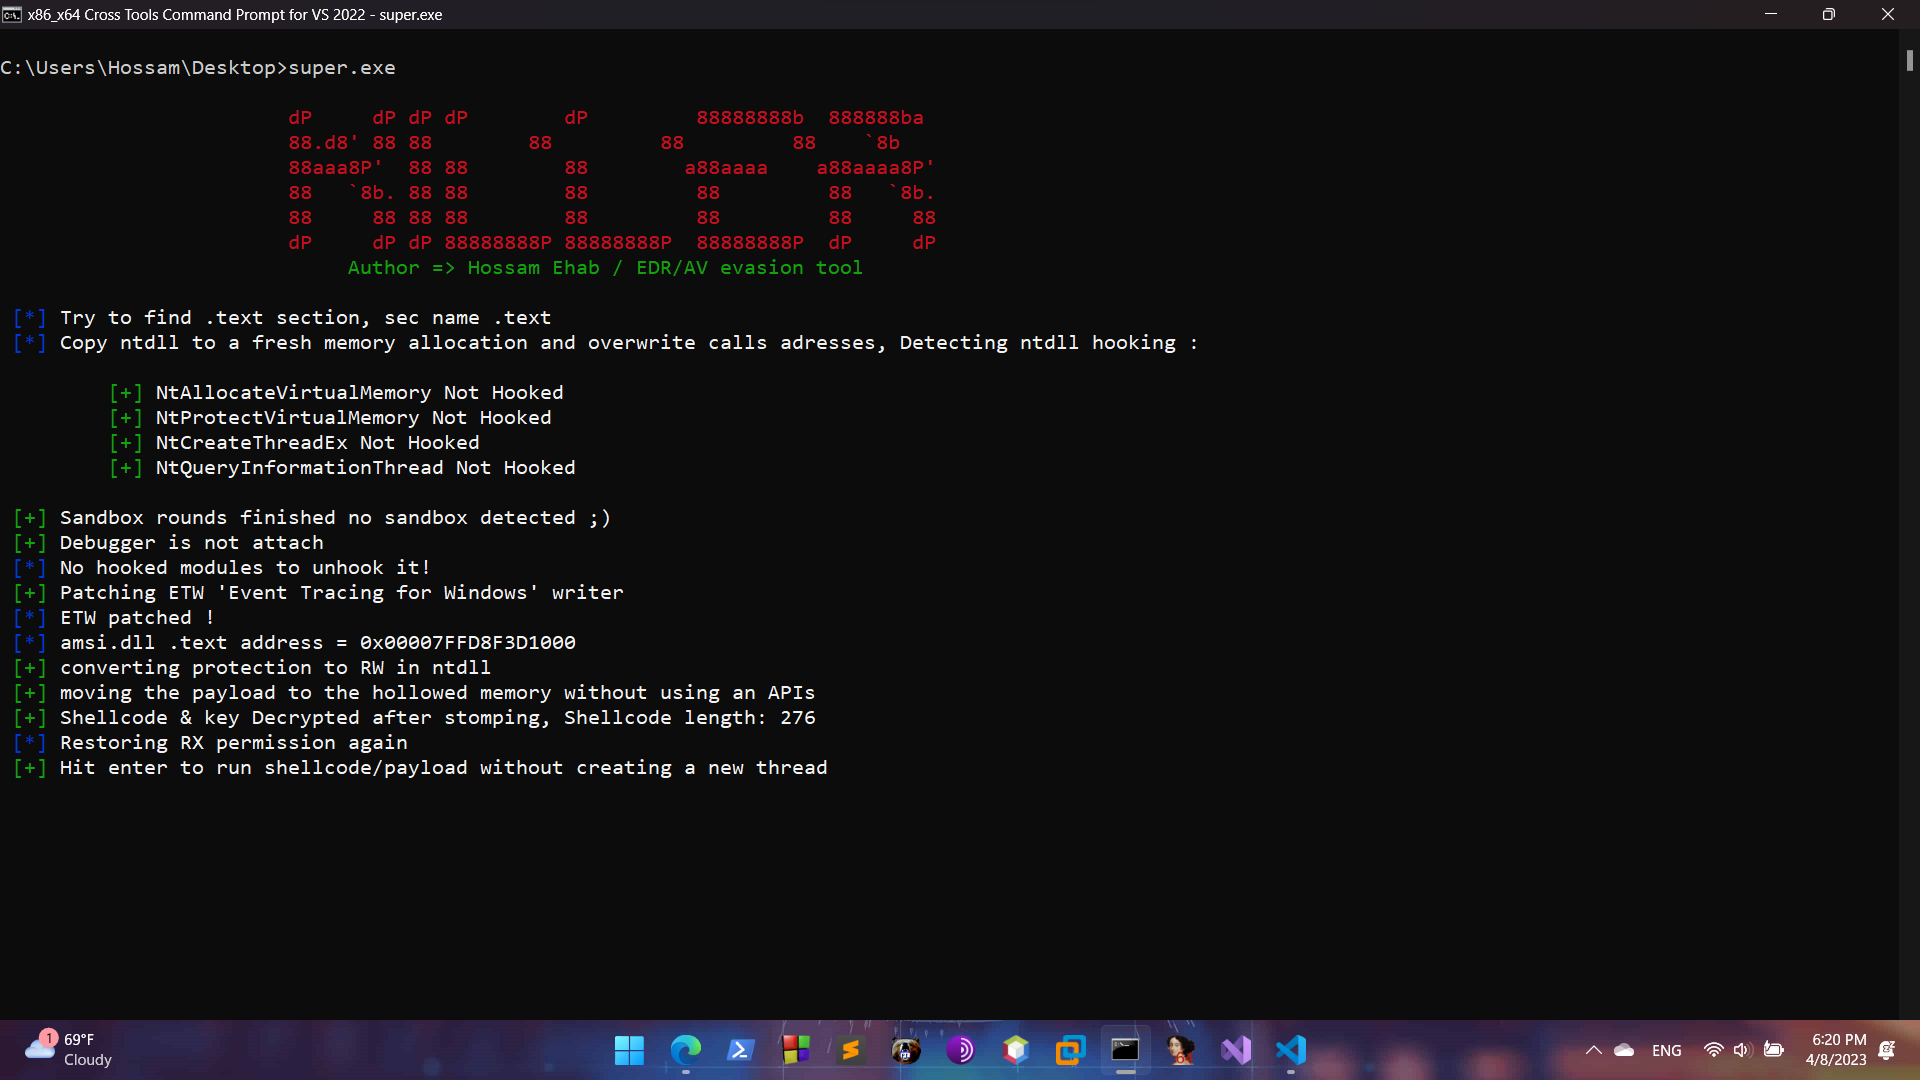 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 d00mfist/mystikal
macOS Initial Access Payload Generator
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…