
Wildfire
 defineid/wildfire
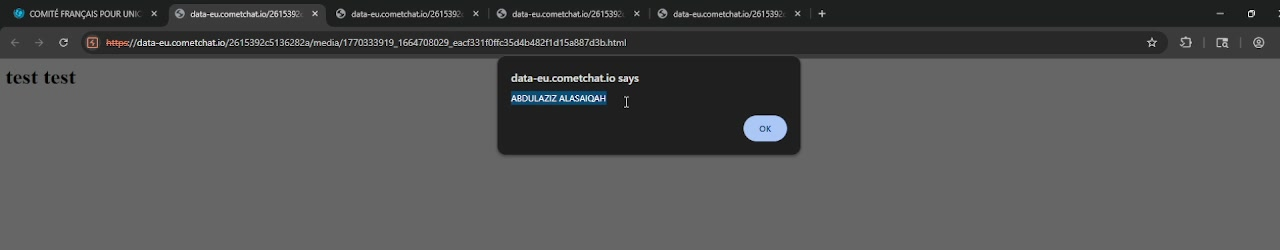
CVE-2026-39154, Stored XSS in CometChat JS SDK
api-securityexploitationpayload-development+4
defineid/wildfireCVE-2026-39154, Stored XSS in CometChat JS SDK
 g33xter/cve-2021-28079
Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
 kcl04/xss-pocs
Cross-Site Scripting Proof of Concepts
 jscamposx/hack
Repositorio de investigación de seguridad que contiene una Prueba de Concepto (PoC) para la vulnerabilidad CVE-2021-4034 (PwnKit) y utilidades de…
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 tw1sm/badger-builder
badger-builder is an AI-assisted tool for generating dynamic Brute Ratel C4 profiles
 yosef0x01/cve-2022-30507-poc
PoC for Arbitrary Code Execution in Notable
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
 mesh3l911/cve-2021-32160
Exploiting a Reflected Cross-Site Scripting (XSS) attack to create a privileged user through the Webmin's add users feature then getting a reverse…
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.
 mesh3l911/cve-2021-32157
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
 stuub/appsmith-1.98-stored-xss-exploit
Automating the exploitation of CVE-2026-7299 - Stored XSS via Database Table/Column Names in SQL Autocomplete within Appsmith =>1.99. Initial…
 jarm222/cve-2025-26244
The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…
 boku7/cve-2020-23839
Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal
 nouvexr/wing-ftp-server-7.4.4-rce-authenticated
Wing FTP Server provides an administrative Lua scripting console accessible via its web interface. Authenticated administrators are able to execute…
 writegsqword/cve-2024-39840-poc
Proof-of-concept exploit for CVE-2024-39840, a remote code execution vulnerability in Factorio 1.1.86. Adapted from a detailed writeup, demonstrating…