
gEnclave
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
authenticationcryptographyencryption-decryption-tools+7
2
renich/genclaveCentralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 kayes817/cve-2022-1257
Proof-of-concept exploit for CVE-2022-1257 that extracts and decrypts stored credentials from the McAfee Agent database (ma.db) using PowerShell.
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 hotpotcookie/cve-2022-44877-white-box
Red Team utilities for setting up CWP CentOS 7 payload & reverse shell (Red Team 9 - CW2023)
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
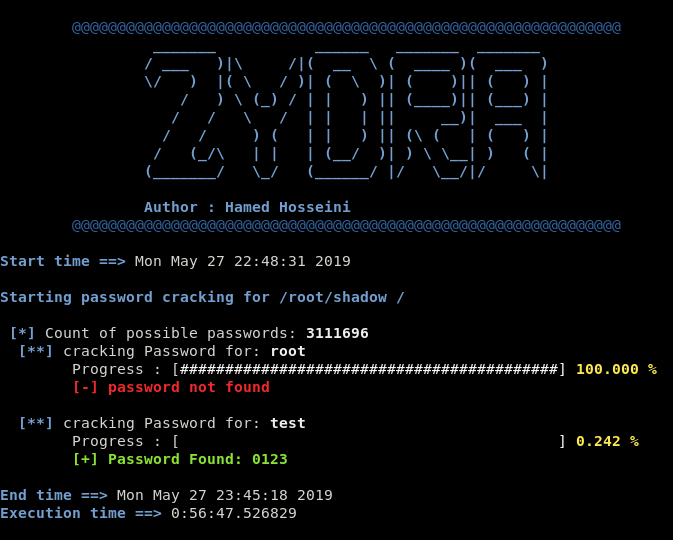 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
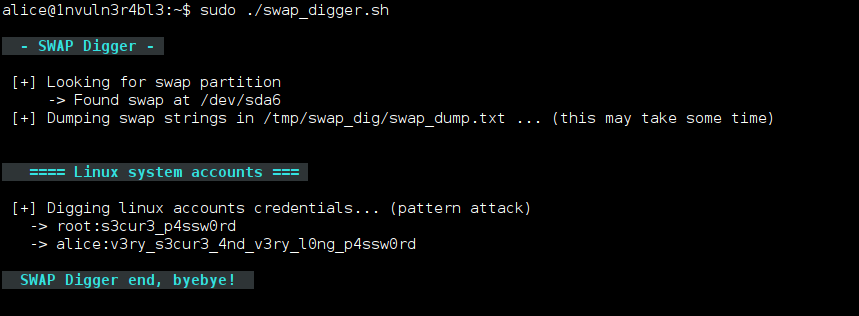 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
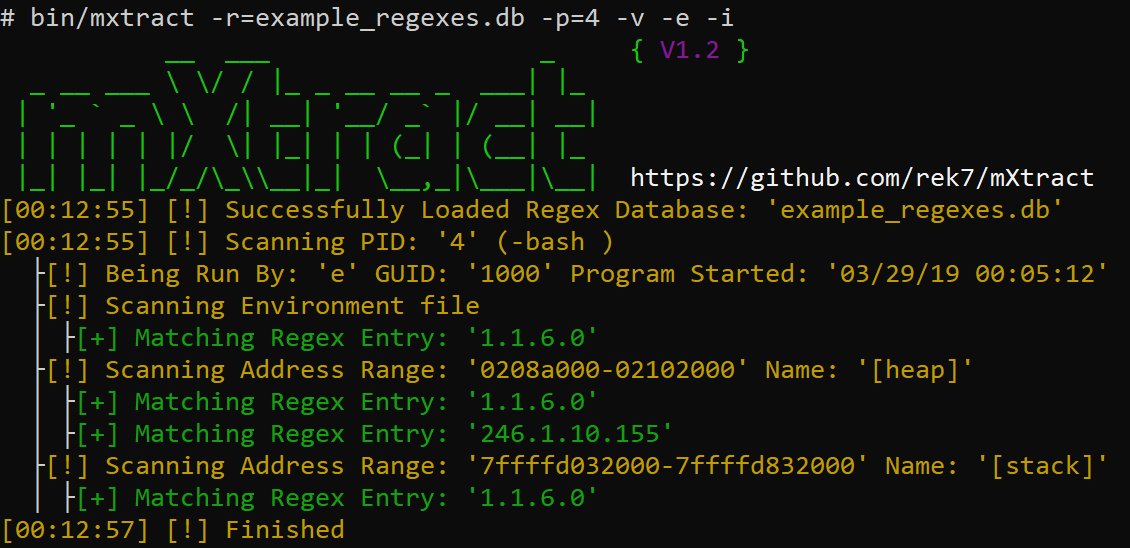 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
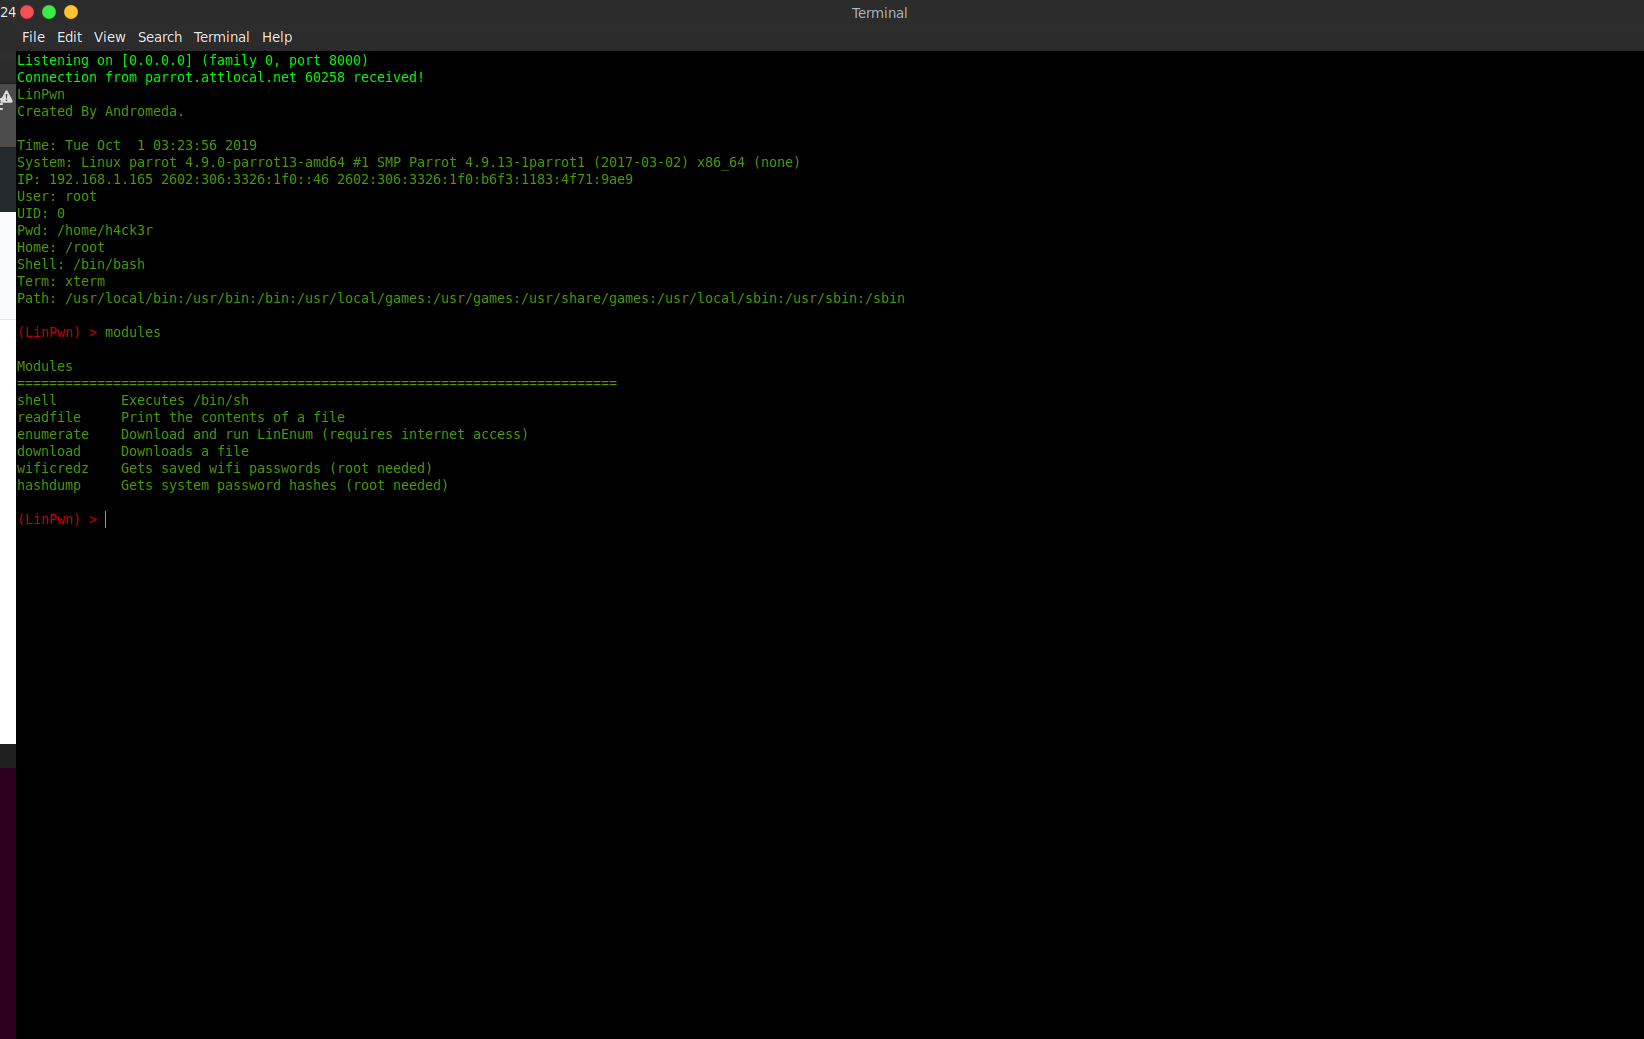 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.