Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071

🦄 A curated list of privacy & security-focused software and services

WiFi Penetration Testing Guide

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

Tool made to automate tasks of pentesting.

Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC

InfoHound is an OSINT to extract a large amount of data given a web domain name.

Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC

Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…

CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction

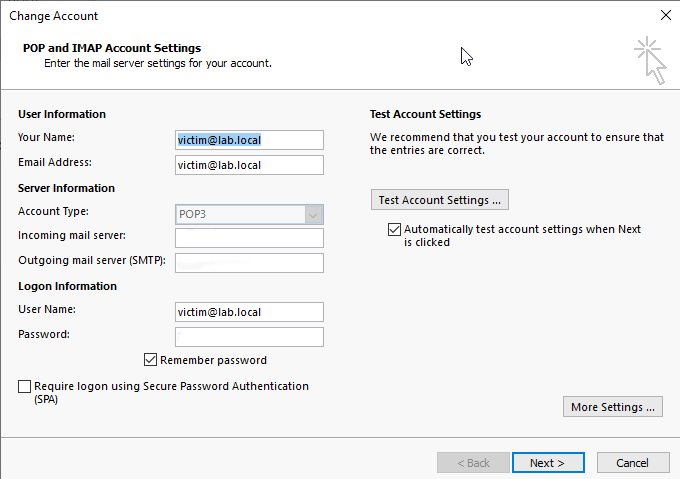
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…

TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…

A free, open-source cybersecurity app for non techy people.

Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…

Detailed vulnerability assessment and exploitation report for CVE-2024-21413 (Moniker Link) in Microsoft Outlook, including attack path, NetNTLMv2…

Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…

Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…