

cve-2019-9053-py3
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
educationexploitationpassword-cracking+3
vedantrana73/cve-2019-9053-py3Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 azrenom/cms-made-simple-2.2.9-cve-2019-9053
Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 p1ckzi/cve-2022-35513
CVE-2022-35513 | blink1-pass-decrypt
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 itzr1g/cve-2019-9053
Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…
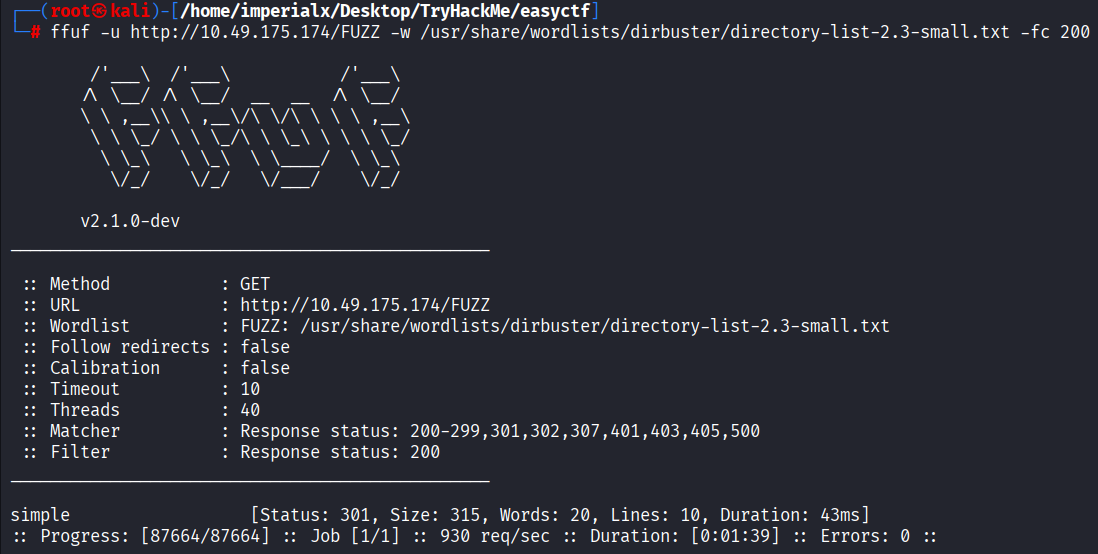 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…