
VMkatz
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
digital-forensicsexploitationforensics+7
nikaiw/vmkatzExtract Windows credentials directly from VM memory snapshots and virtual disks
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
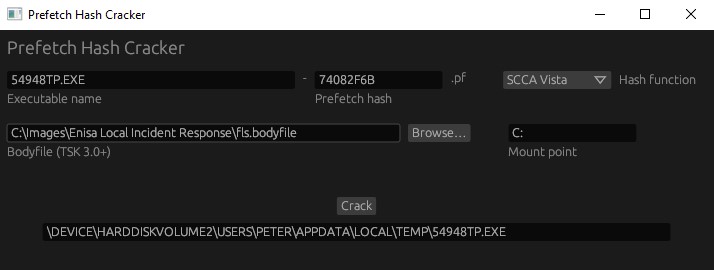 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…