Grafana-Decryptor-for-CVE-2021-43798

Decrypts Grafana DataSource passwords by exploiting CVE-2021-43798 directory traversal to retrieve configuration files and derive encryption keys.

Decrypts Grafana DataSource passwords by exploiting CVE-2021-43798 directory traversal to retrieve configuration files and derive encryption keys.

Exploit script for CVE-2021-27211

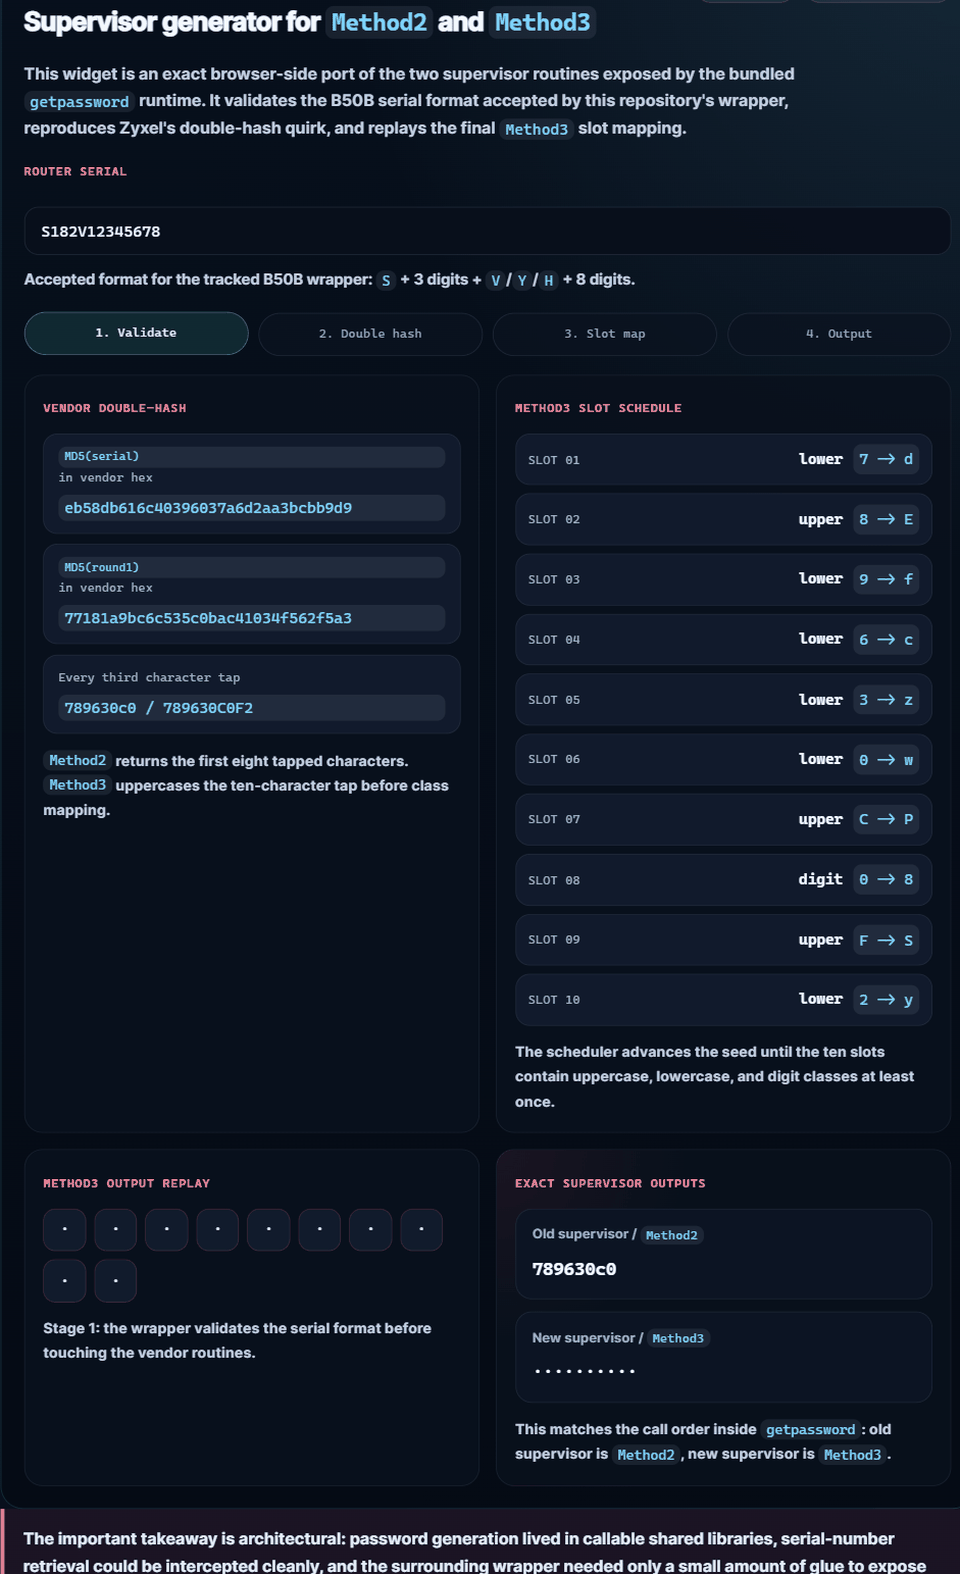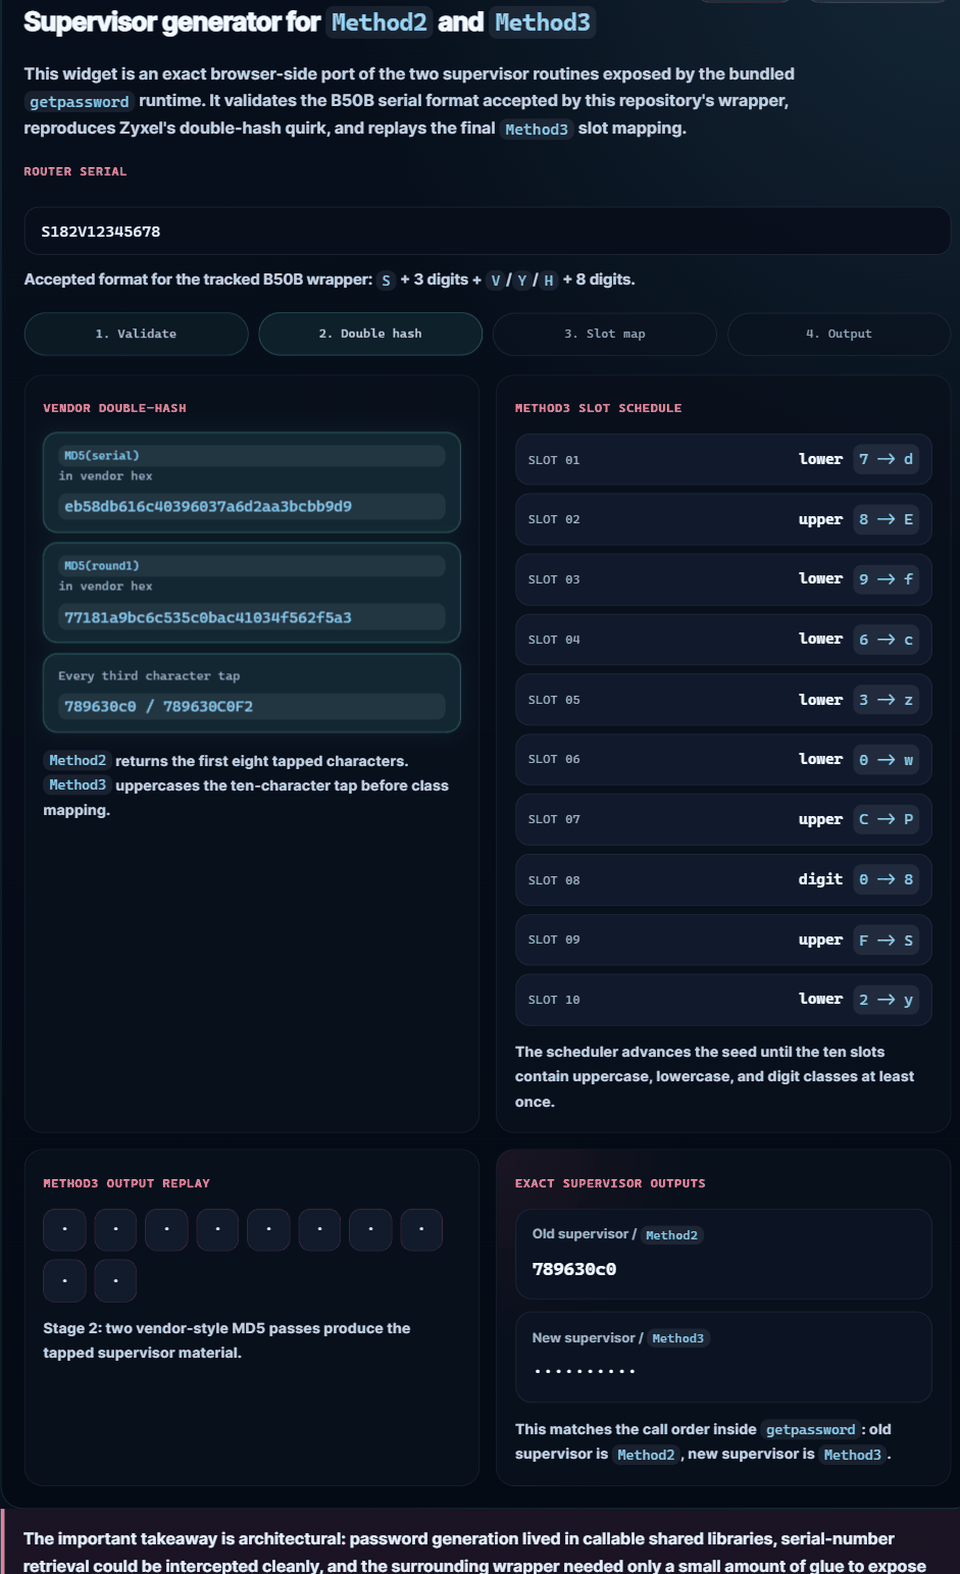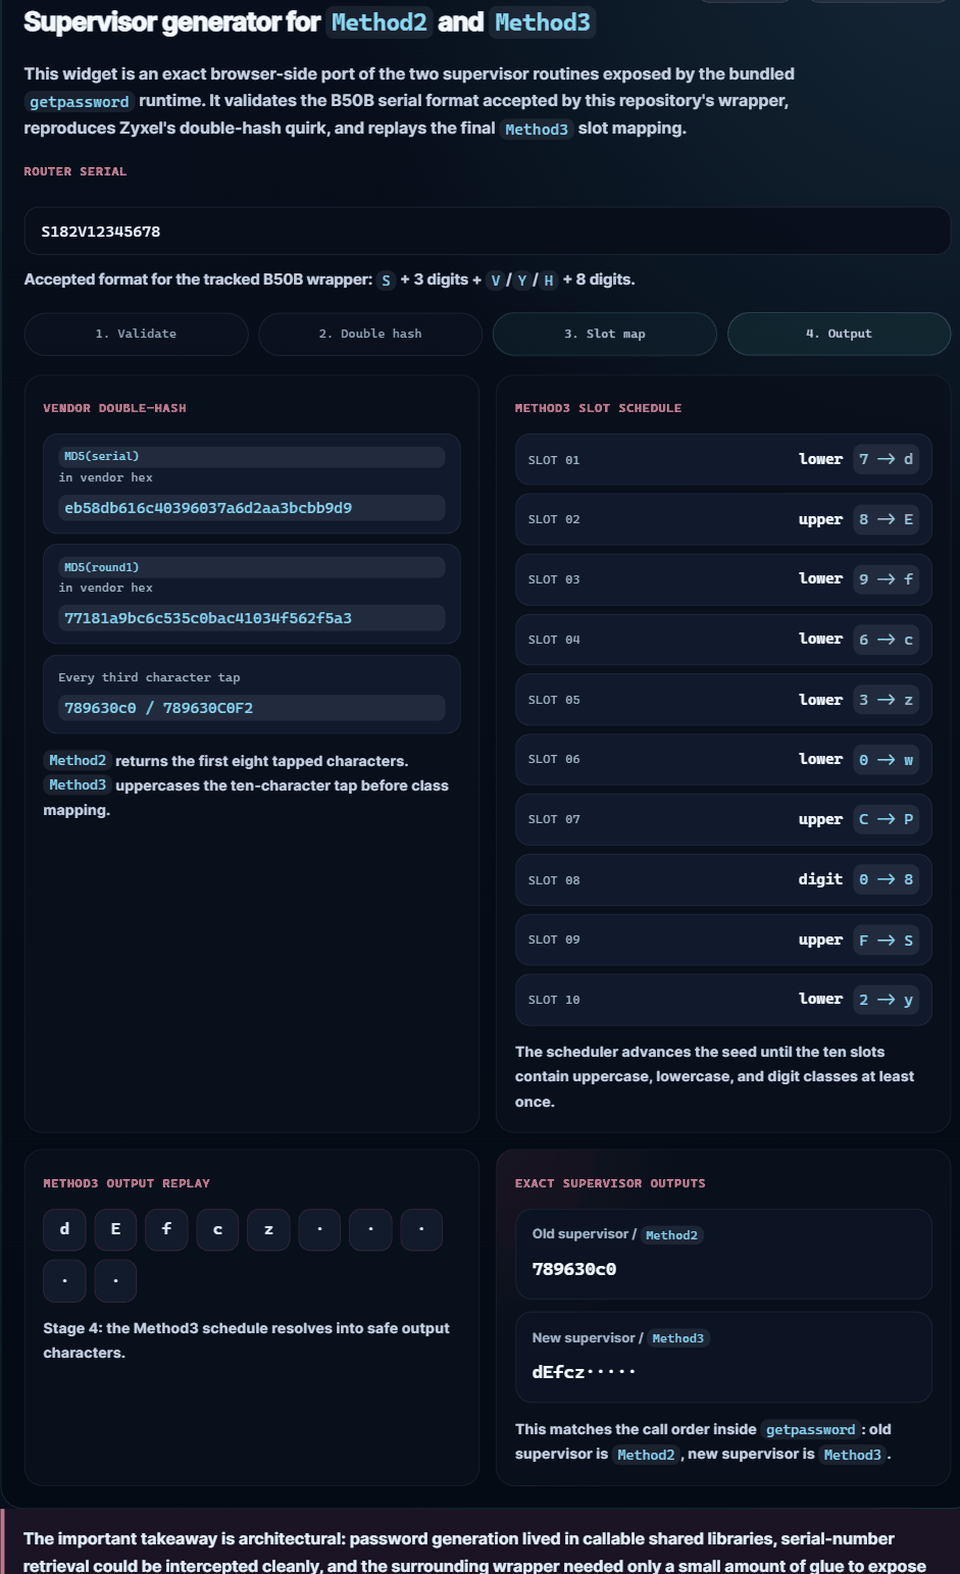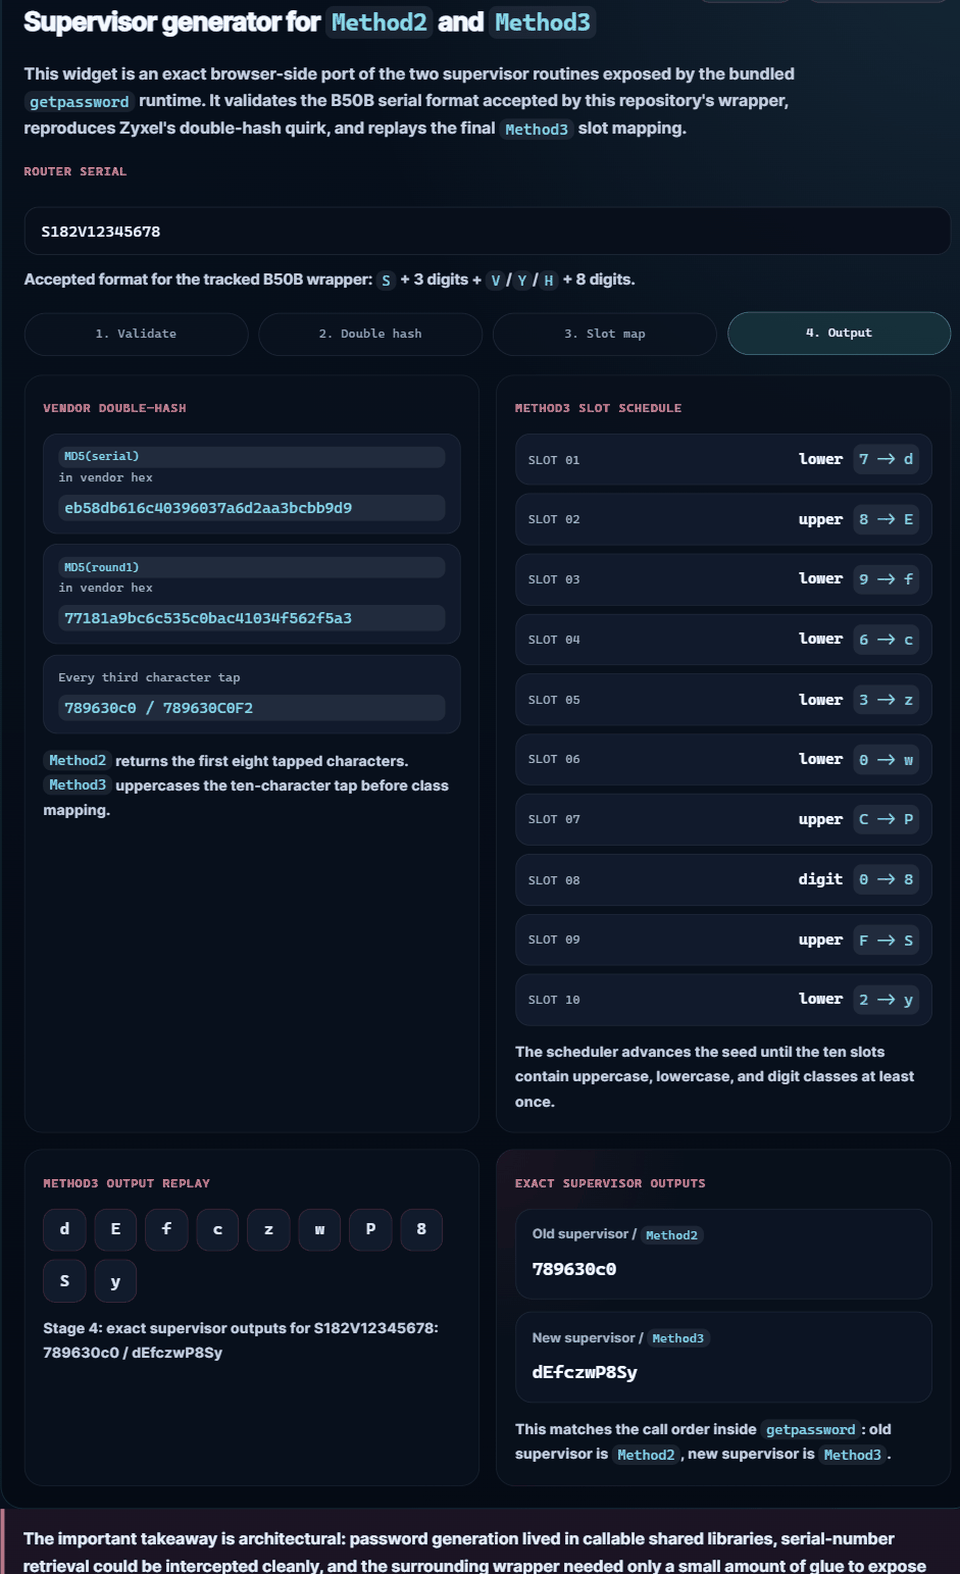
Zyxel super-admin credential exposure write-up across CPE/ONT/LTE/5G firmware, with an adapted VMG8825-B50B genpass lab.

Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…

CVE-2021-43798 MiNi Exploitation Framework

C-Ark Credential Decoder for #CVE-2021-31796

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…