
PyLadon
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
command-and-controlexploitationlateral-movement+6
535 years ago
k8gege/pyladonLadon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 yucaerin/cve-2024-55555
Laravel Crypto Killer Mass Scanner (CVE-2024-55555)
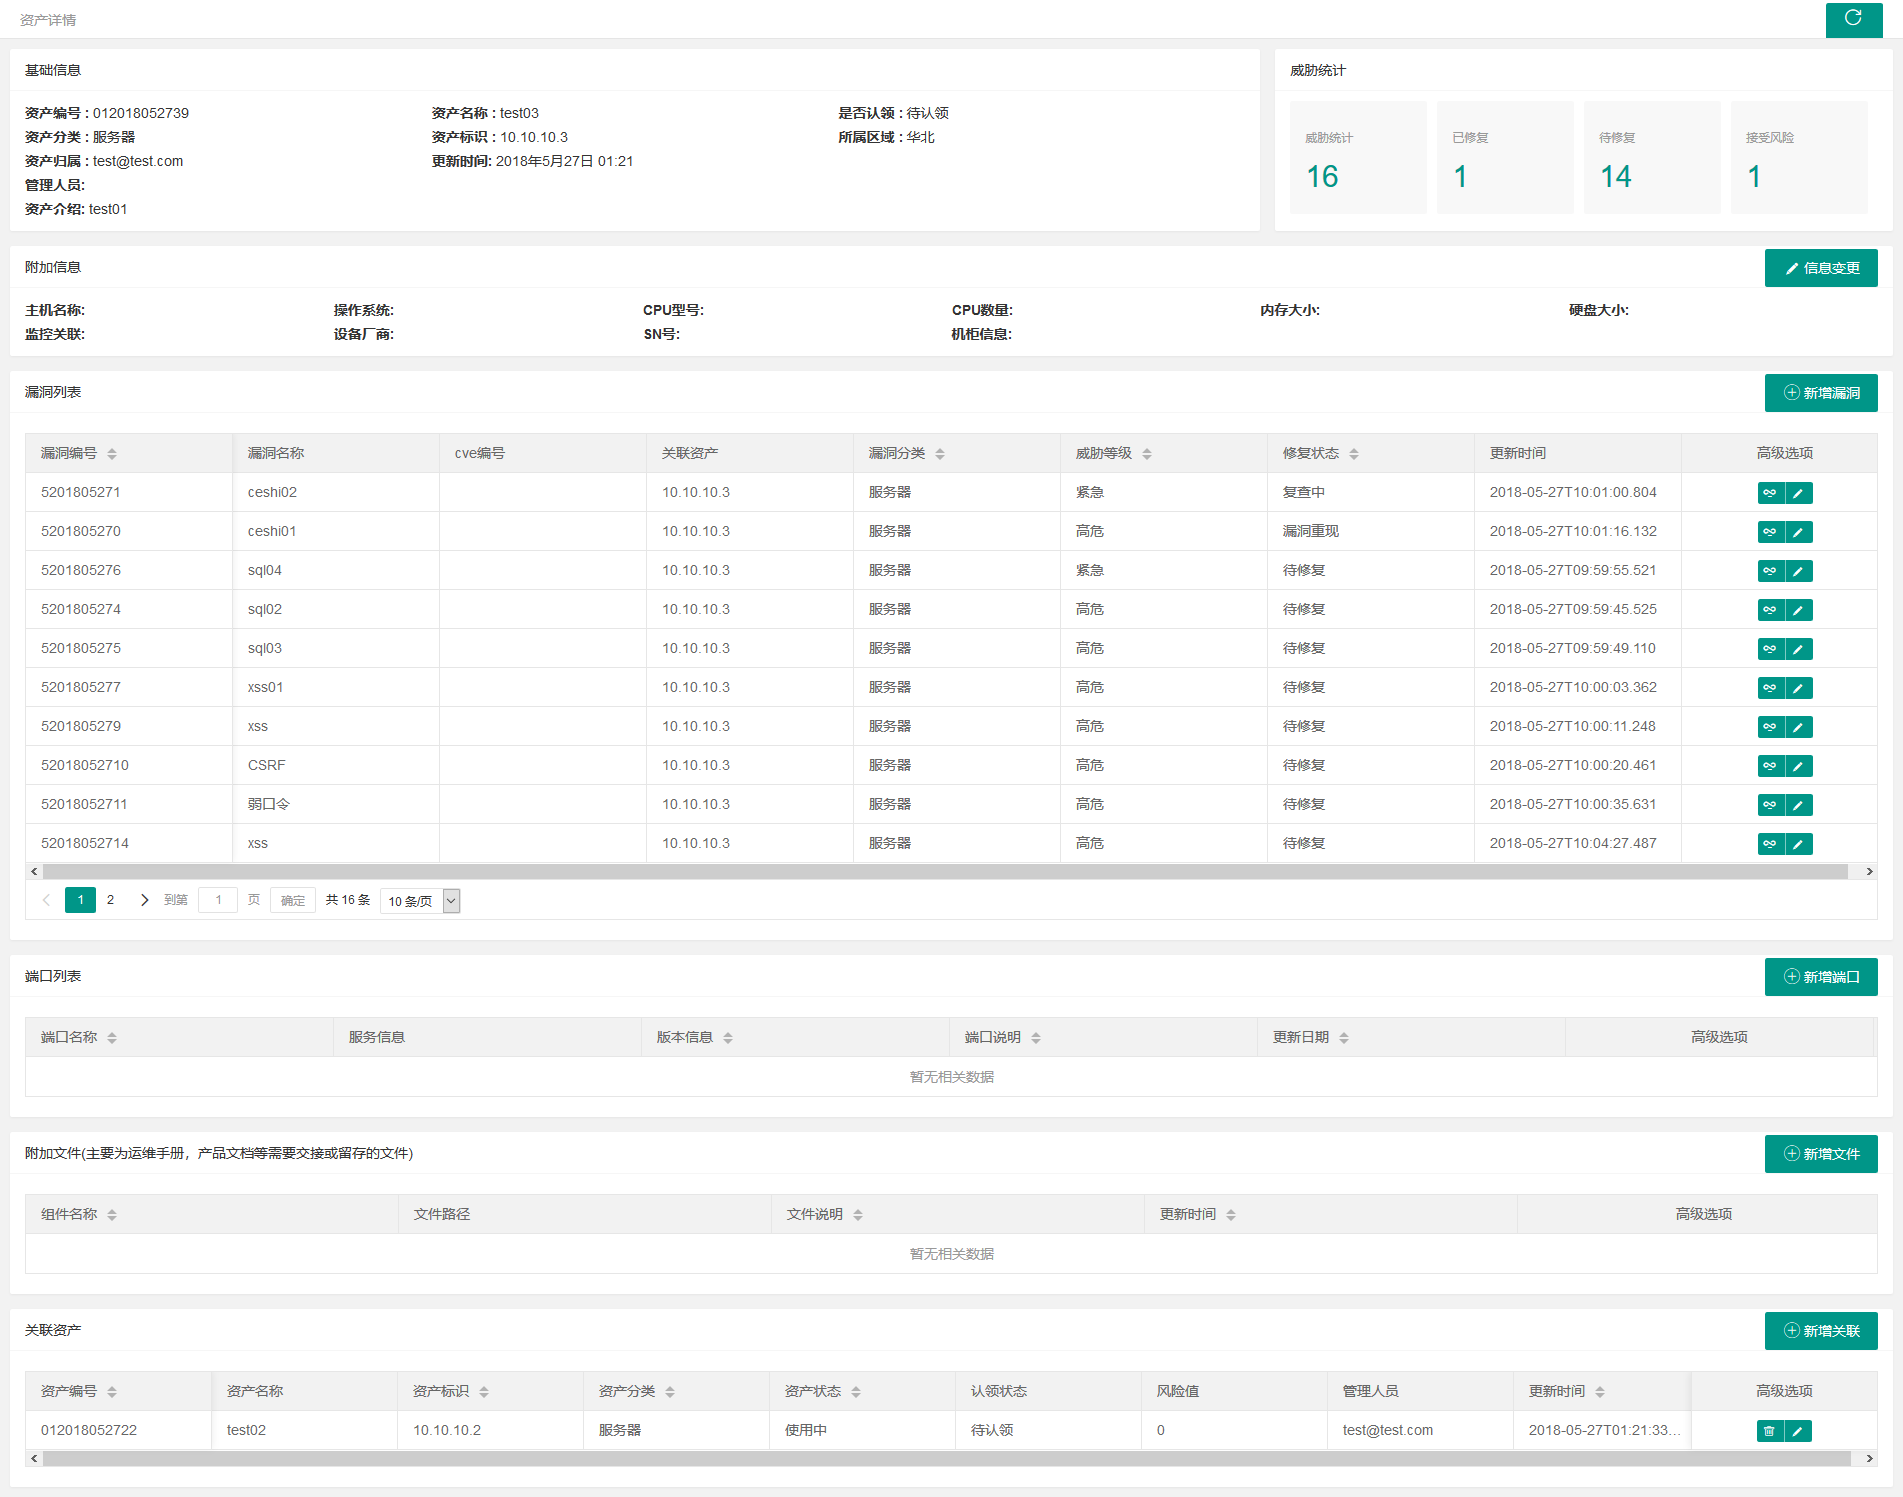 we1h0/securitymanageframwork
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
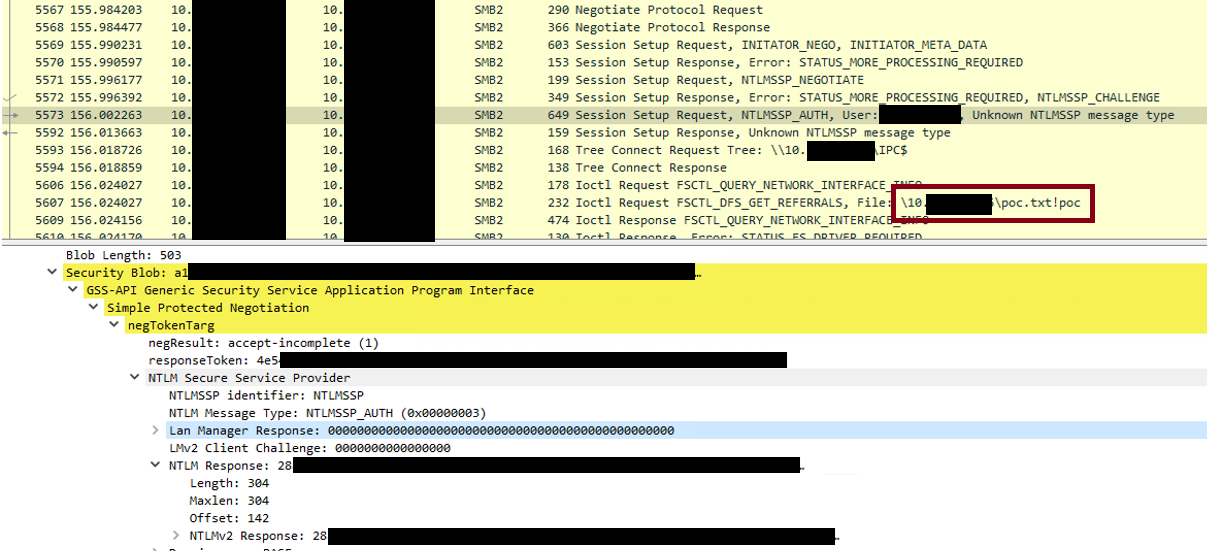 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
 ekultek/pybelt
The hackers tool belt
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.