CVE-2024-1698-NotificationX-WordPress-Plugin-SQL-Injection-to-Admin-Credential-Extraction

Unauthenticated time-based blind SQL injection exploit for NotificationX WordPress plugin (CVE-2024-1698) that extracts admin username and password…

Unauthenticated time-based blind SQL injection exploit for NotificationX WordPress plugin (CVE-2024-1698) that extracts admin username and password…

A tool which can be used to generate password list or dictionary from the details of the target

Exploit for CVE-2025-44203 targeting a race condition in HotelDruid 3.0.0/3.0.7 that leaks admin credentials and causes denial of service. Includes a…

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…

CVE-2021-43798 MiNi Exploitation Framework

CVE-2023-31290 Scanner

SolarView vuln

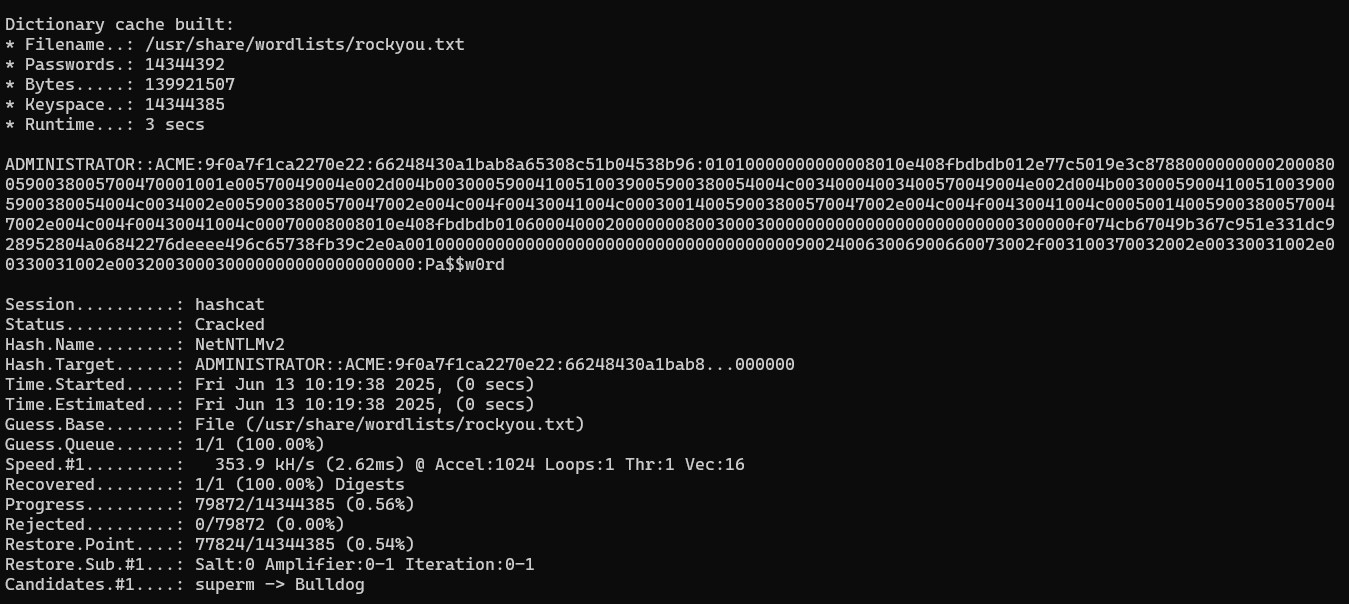
CVE-2025-24071: NTLMv2 Hash Disclosure via .library-ms File

Extracts passwords from Fortinet VPN leak dumps associated with CVE-2022-40684, processing subfolders for vpn-passwords.txt and outputting cleaned…

This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…

A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine

CVE-2023-39144 disclosure: cleartext password exposure in Element55 Maketime appliance admin pages, enabling privilege escalation via…

Python script to execute CVE-2025-24071

Exploit for the CVE-2024-37010: access other user's external storage & lateral movement

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…