
wi-fi-fortress-auditor
 jawadasghar471600-dot/wi-fi-fortress-auditor
Wi-Fi Security Audit & WPA2 Password Testing Guide 2026: Master Monitor Mode
defensive-toolshash-analysisinformation-gathering+7
3
jawadasghar471600-dot/wi-fi-fortress-auditorWi-Fi Security Audit & WPA2 Password Testing Guide 2026: Master Monitor Mode
 occasionpuffbird12/airstrike
Audit Wi-Fi security on Linux with monitor mode, handshake capture, and offline WPA/WPA2 password testing in one guided GUI
 ehabhussein/snmpvlan
SNMP scanner and brute-forcer targeting Cisco Nexus switches (5000/6000) to exploit CVE-2014-3341, enumerate VLANs, crack SNMP community strings, and…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 randomuser1983/ikeabuser
A simple tool wrapper to automate the enumeration, fingerprinting, and PSK extraction of an IPSec VPN gateway.
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
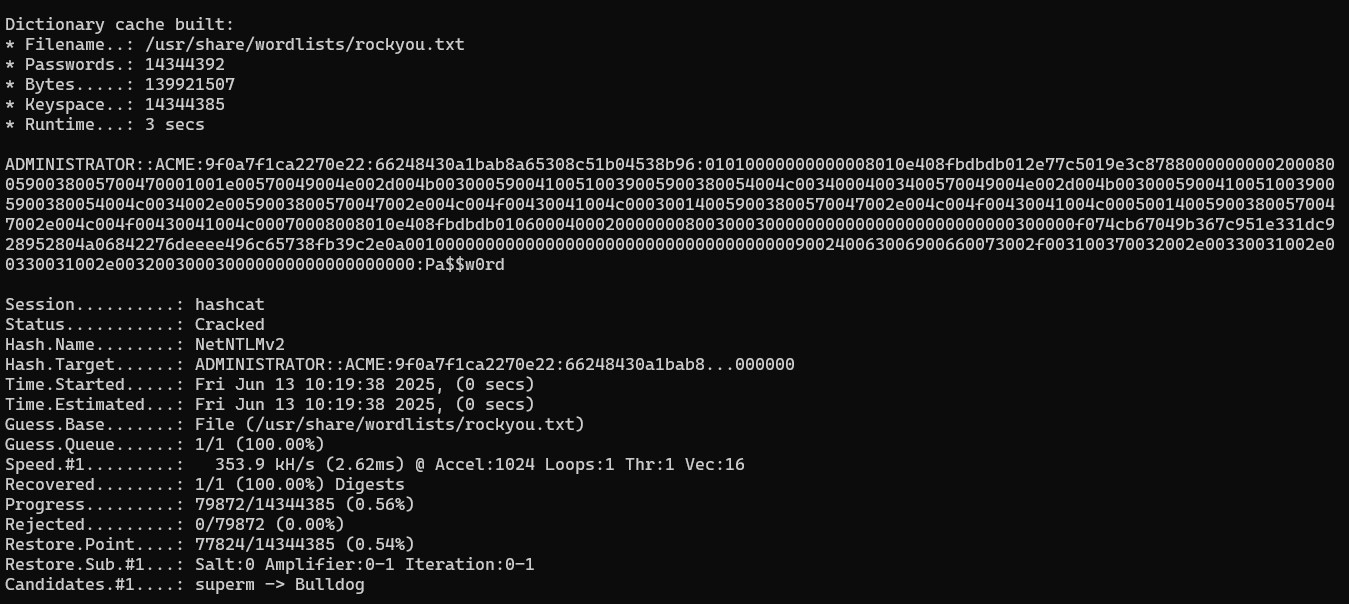 deshanfer94/cve-2025-24071-poc-ntlmhashdisclosure-
CVE-2025-24071: NTLMv2 Hash Disclosure via .library-ms File
 sallocinavalcante/lab-smb-responder-cve-2024-21413
Laboratorio criado para PenTest da Vuln CVE 2024-214113(MONIKER LINK).