
HTB-Pterodactyl-Writeup
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
ctfeducationexploitation+9
v0idw1re/htb-pterodactyl-writeupHackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 sallocinavalcante/lab-smb-responder-cve-2024-21413
Laboratorio criado para PenTest da Vuln CVE 2024-214113(MONIKER LINK).
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
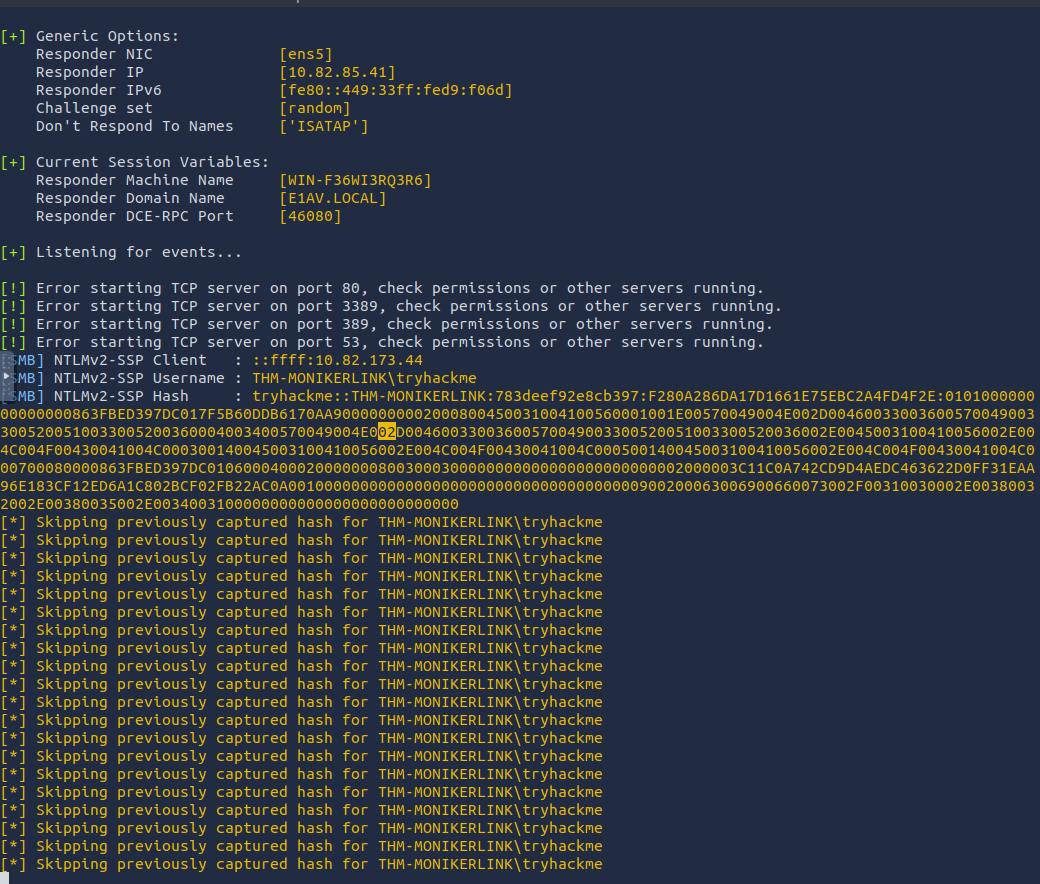 securenetexpert/cve-2024-21413-moniker-link-writeup
Technical write-up on CVE-2024-21413 (Moniker Link vulnerability)
 fbm31/audit-blackbox-web-to-root
Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
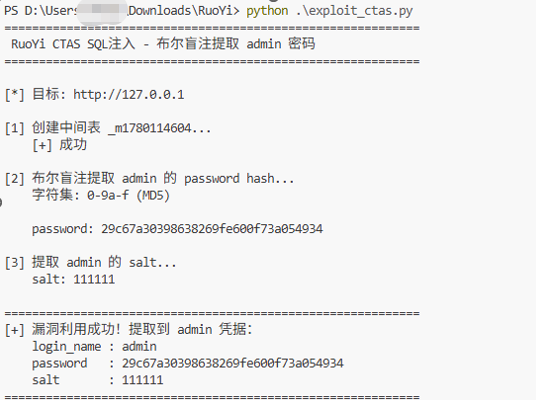 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 user6400/cve-2026-39031-lansweeper-lsrunase2-lsencrypt2
CVE-2026-39031 — offline plaintext password recovery for Lansweeper lsrunase 2.0 / lsencrypt 2.0 via a hardcoded RC4 key. PoC + technical advisory.
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
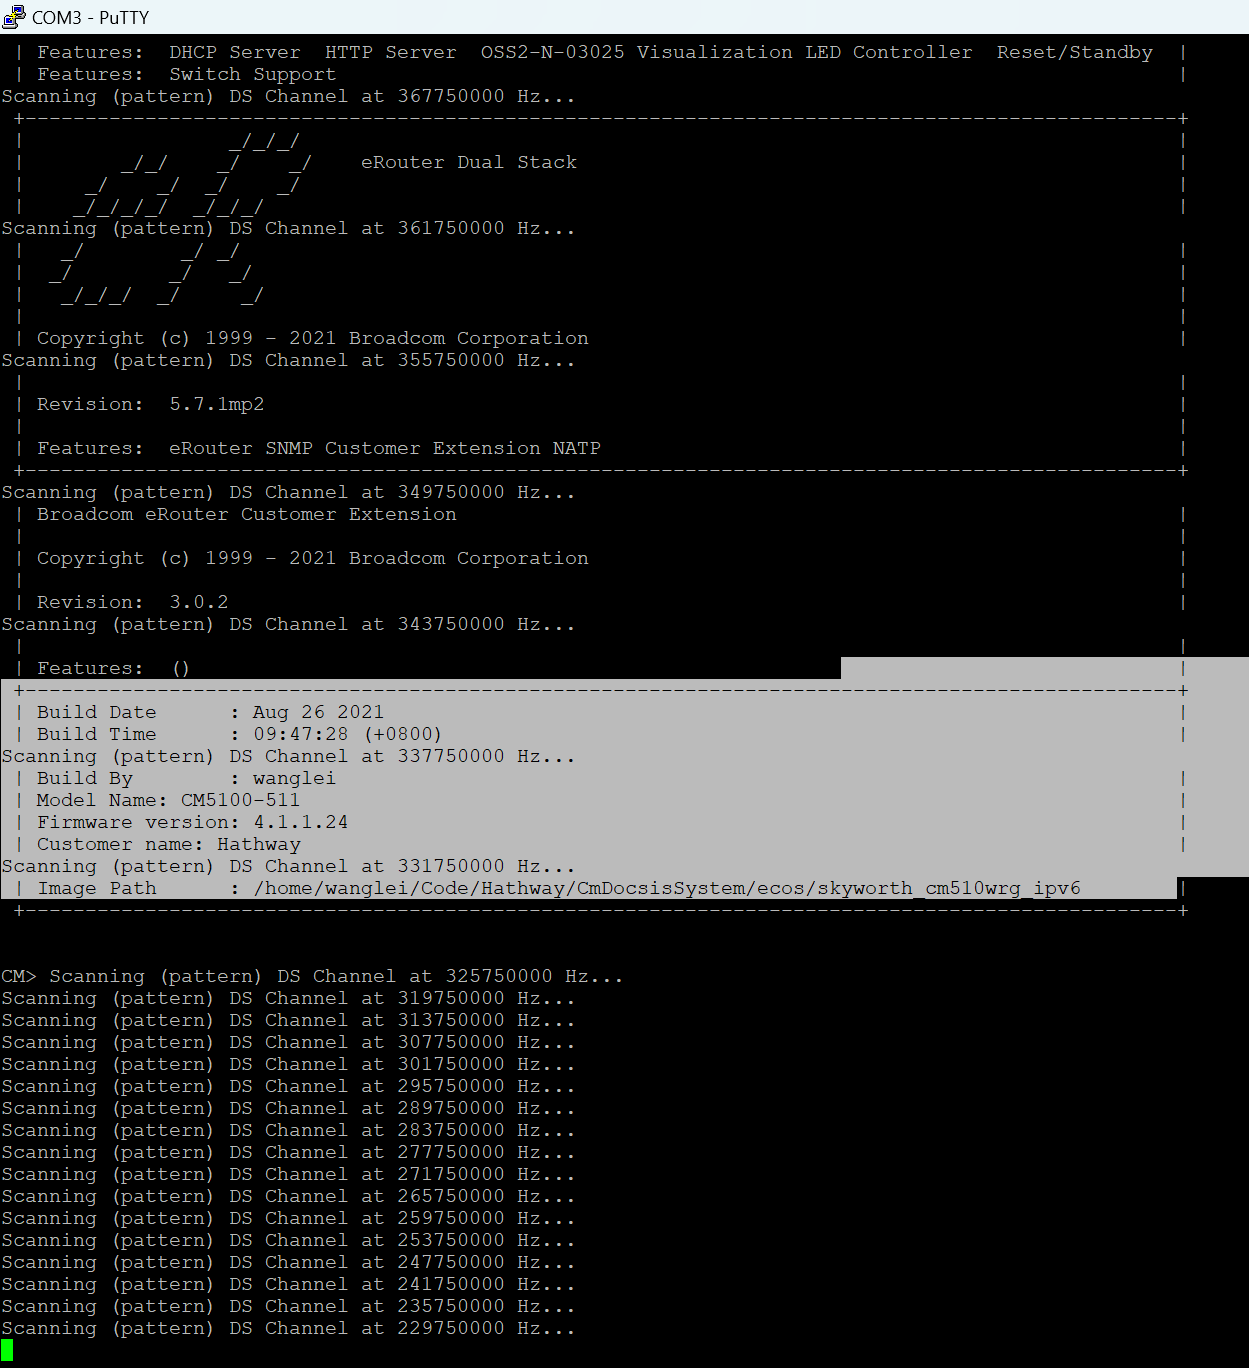 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
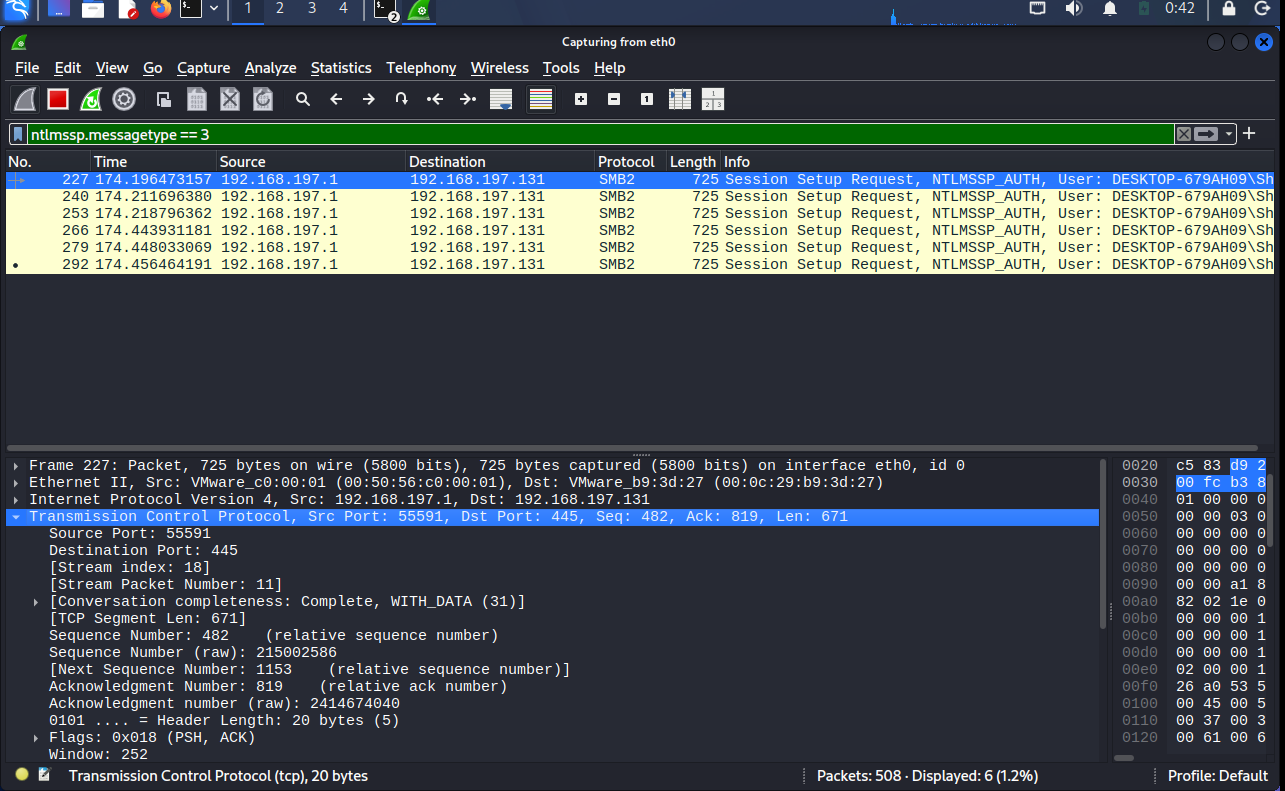 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 caelumisme/cve-2019-9053-poc
Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 kayes817/cve-2022-1257
Proof-of-concept exploit for CVE-2022-1257 that extracts and decrypts stored credentials from the McAfee Agent database (ma.db) using PowerShell.