CVE-2026-52614
 chinesespeople/cve-2026-52614
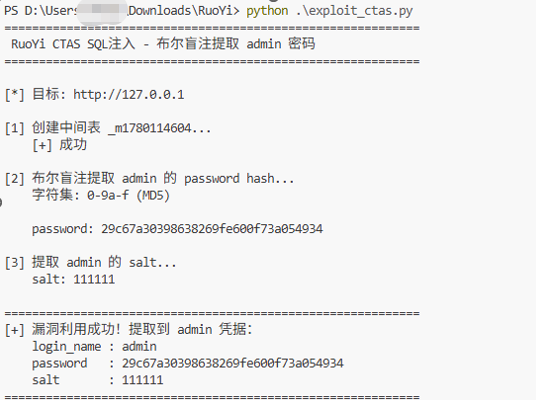
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
exploitationpassword-crackingpenetration-testing+2
chinesespeople/cve-2026-52614There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 cduram/cve-2023-39144
CVE-2023-39144 disclosure: cleartext password exposure in Element55 Maketime appliance admin pages, enabling privilege escalation via…
 sarpantkeltiek/cve-2024-37010
Exploit for the CVE-2024-37010: access other user's external storage & lateral movement
 ret2desync/cve-2024-38793-poc
Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)
 davcwikla/cve-2019-9053-exploit
Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 hackheart-tech/-exploit-lab
Exploits Python cve-2019-9053– by HackHeart