
pwned
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
information-gatheringosintpassword-cracking+1
246
wkovacs64/pwnedCLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 hashtopolis/server
Hashtopolis - distributed password cracking with Hashcat
 ibnaleem/rules
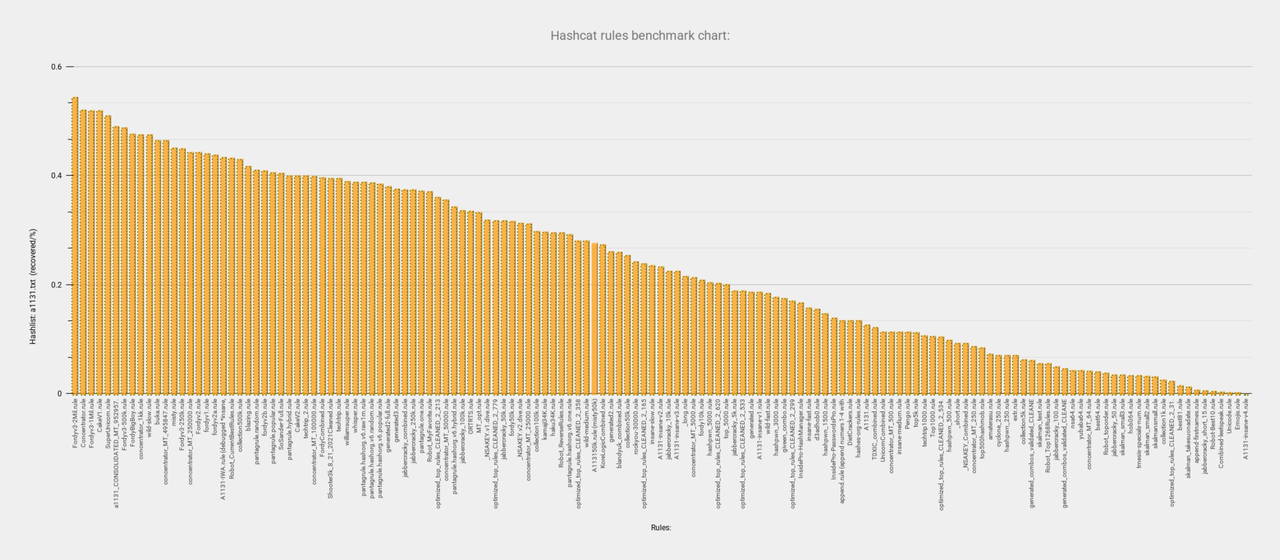
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
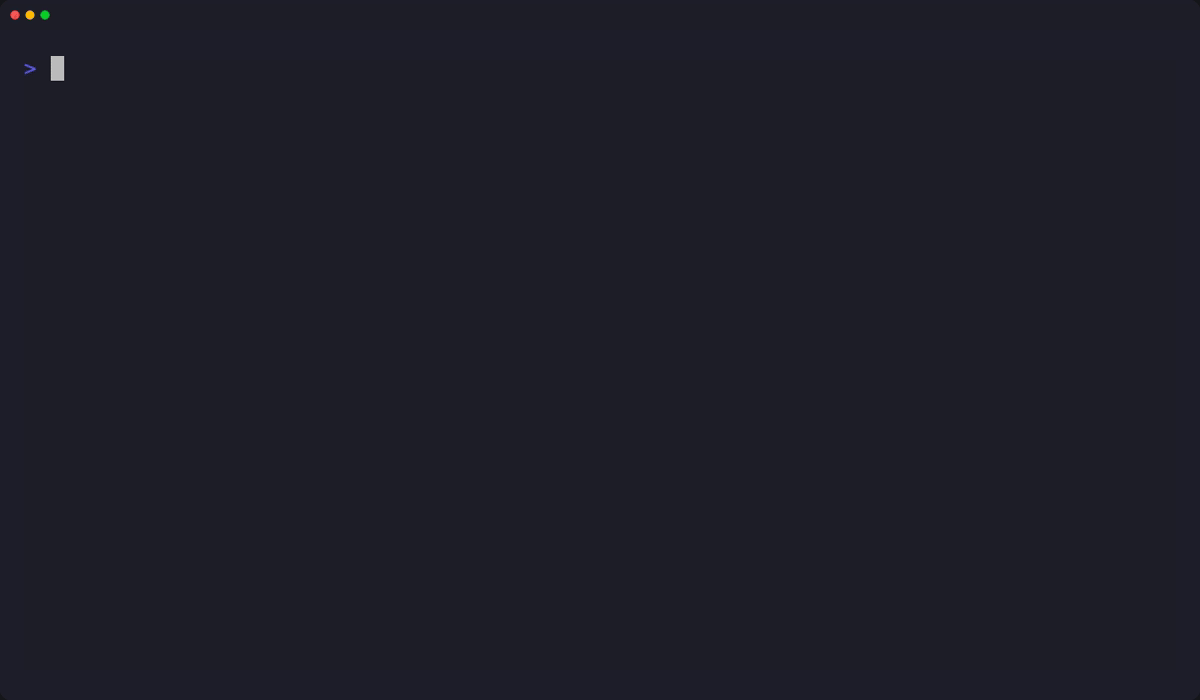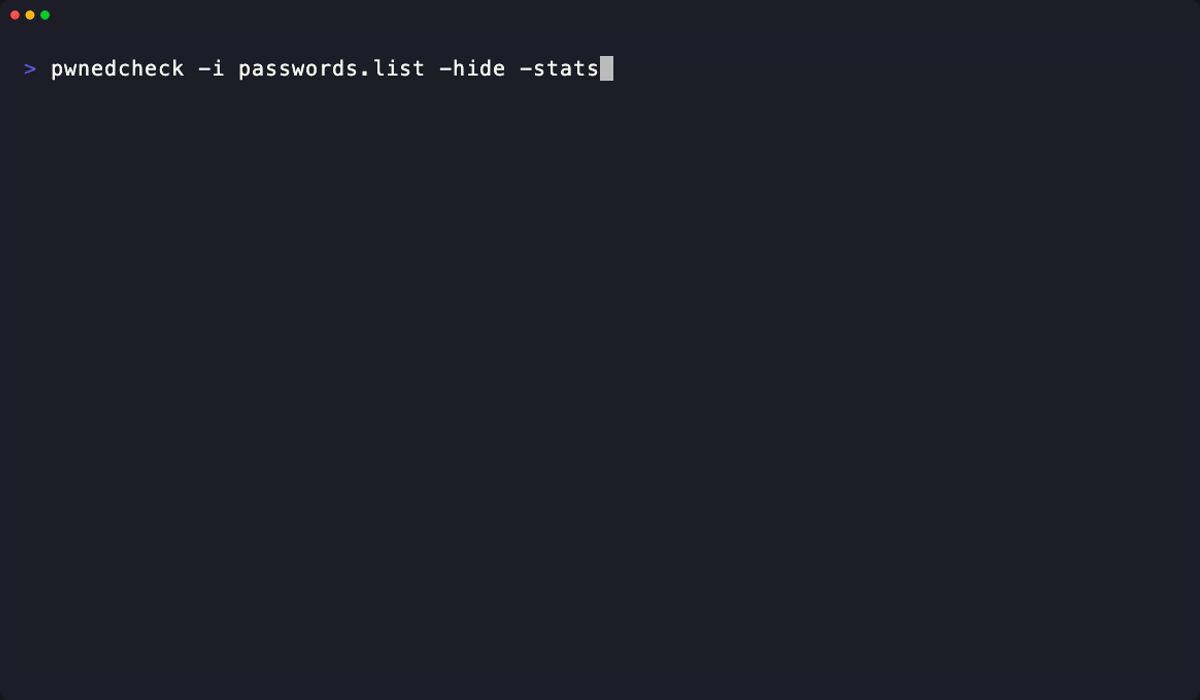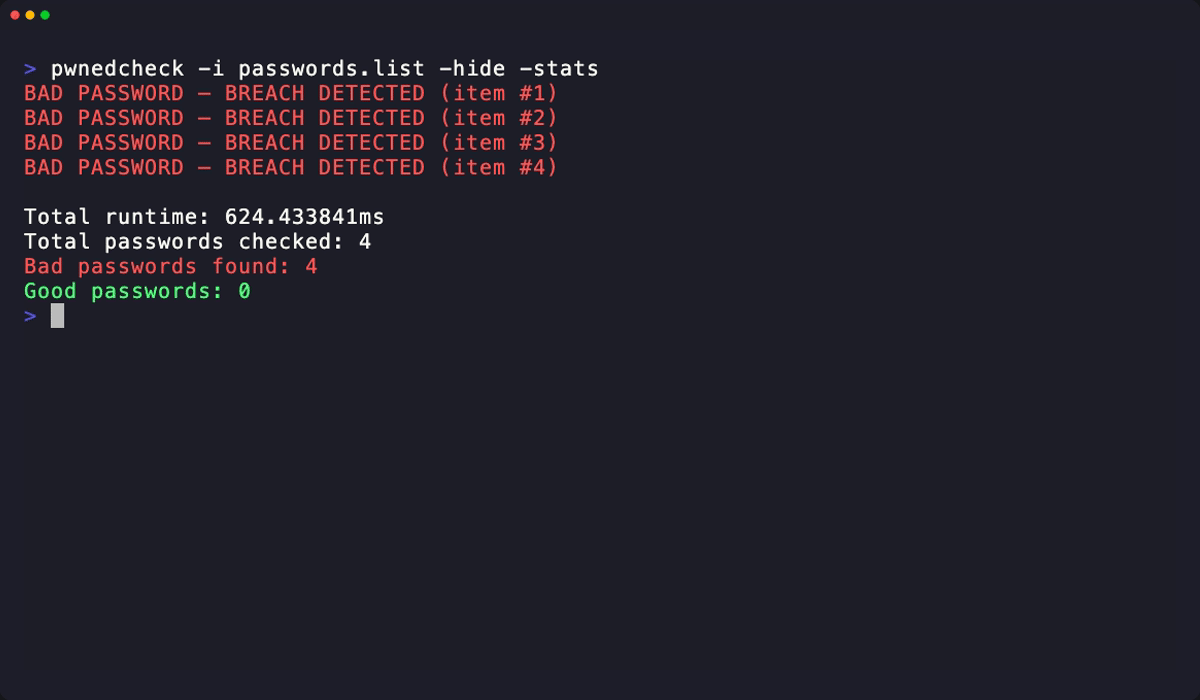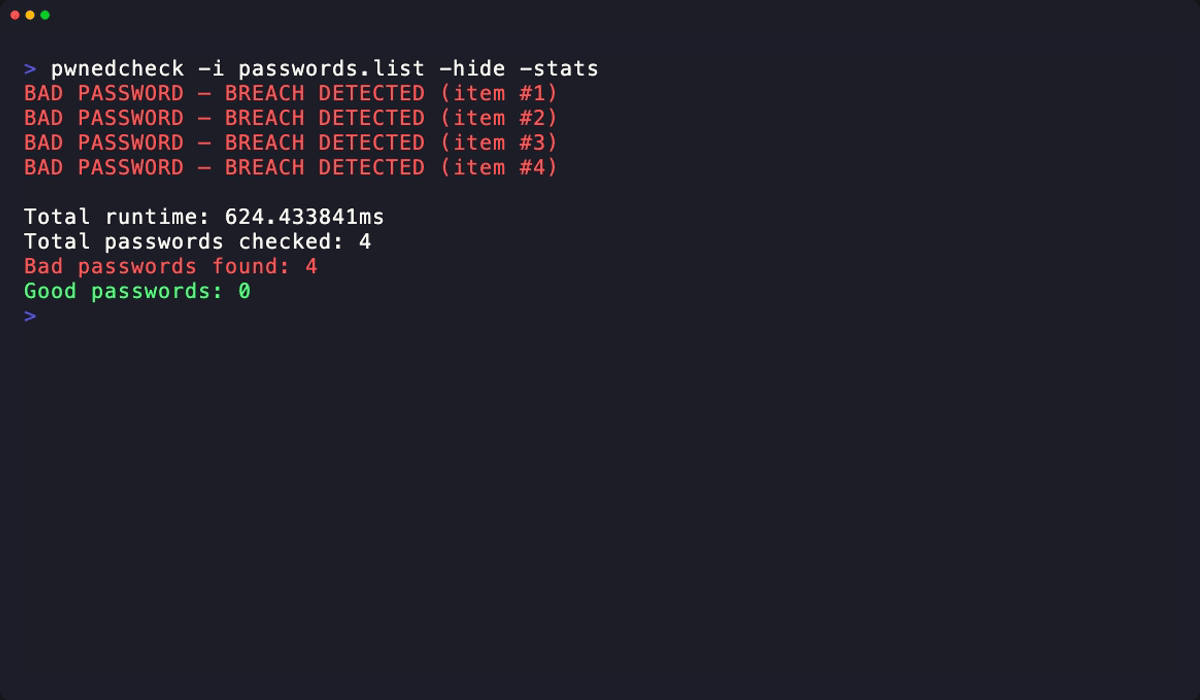 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 desireeontrial76/yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.
 aircrack-ng/aircrack-ng
Complete suite for WiFi network security auditing, including packet capture, injection attacks, deauthentication, fake AP creation, and WEP/WPA PSK…
 lithnet/ad-password-protection
Active Directory password filter featuring breached password checking and custom complexity rules
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 pluja/awesome-privacy
Awesome Privacy - A curated list of services and alternatives that respect your privacy because PRIVACY MATTERS.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 lefayjey/linwinpwn
Bash script wrapping Active Directory tools for automated enumeration, vulnerability checks, exploitation, and password dumping via LDAP, RPC,…
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
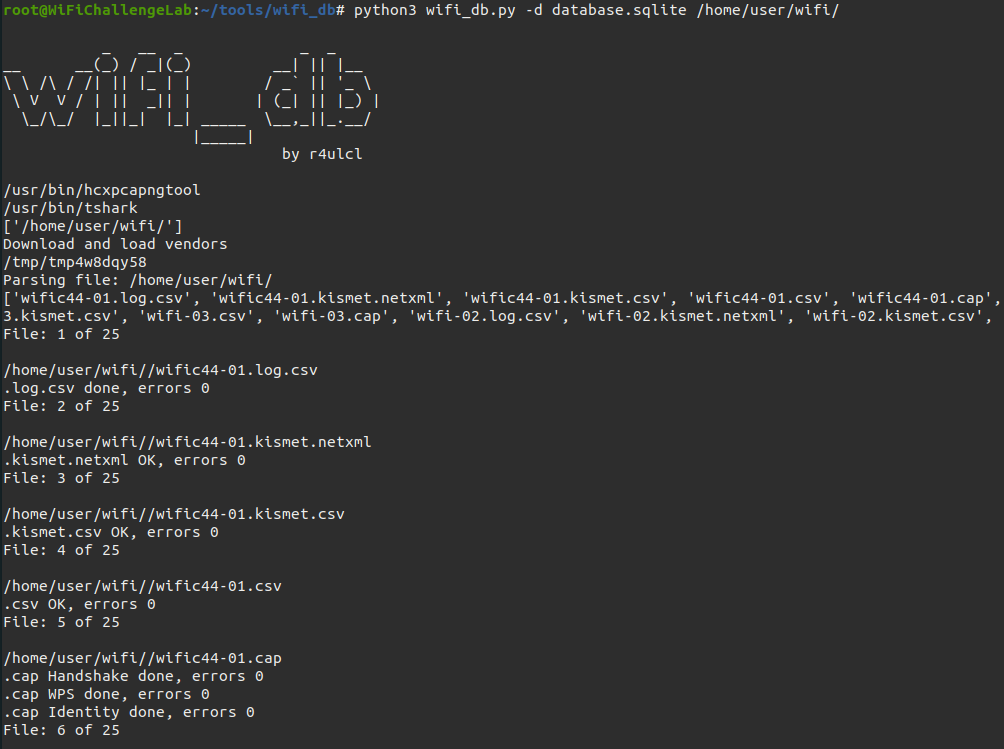 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…