
pwned
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
information-gatheringosintpassword-cracking+1
246
wkovacs64/pwnedCLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
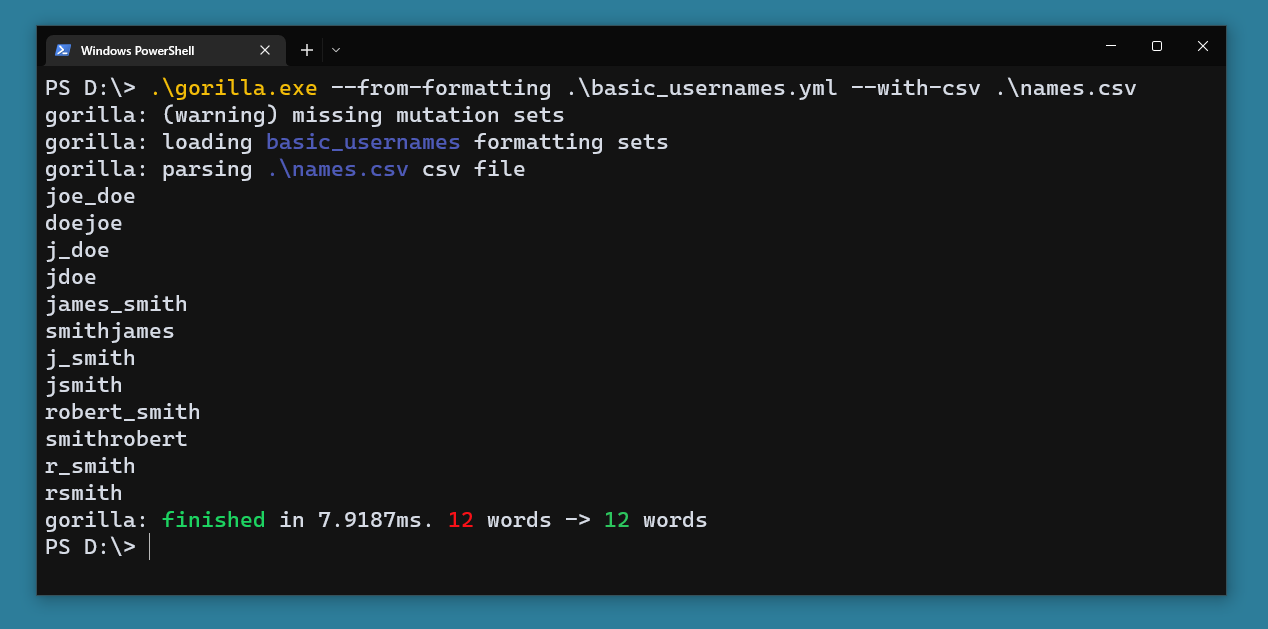 andreiverse/gorilla
tool for generating wordlists or extending an existing one using mutations.
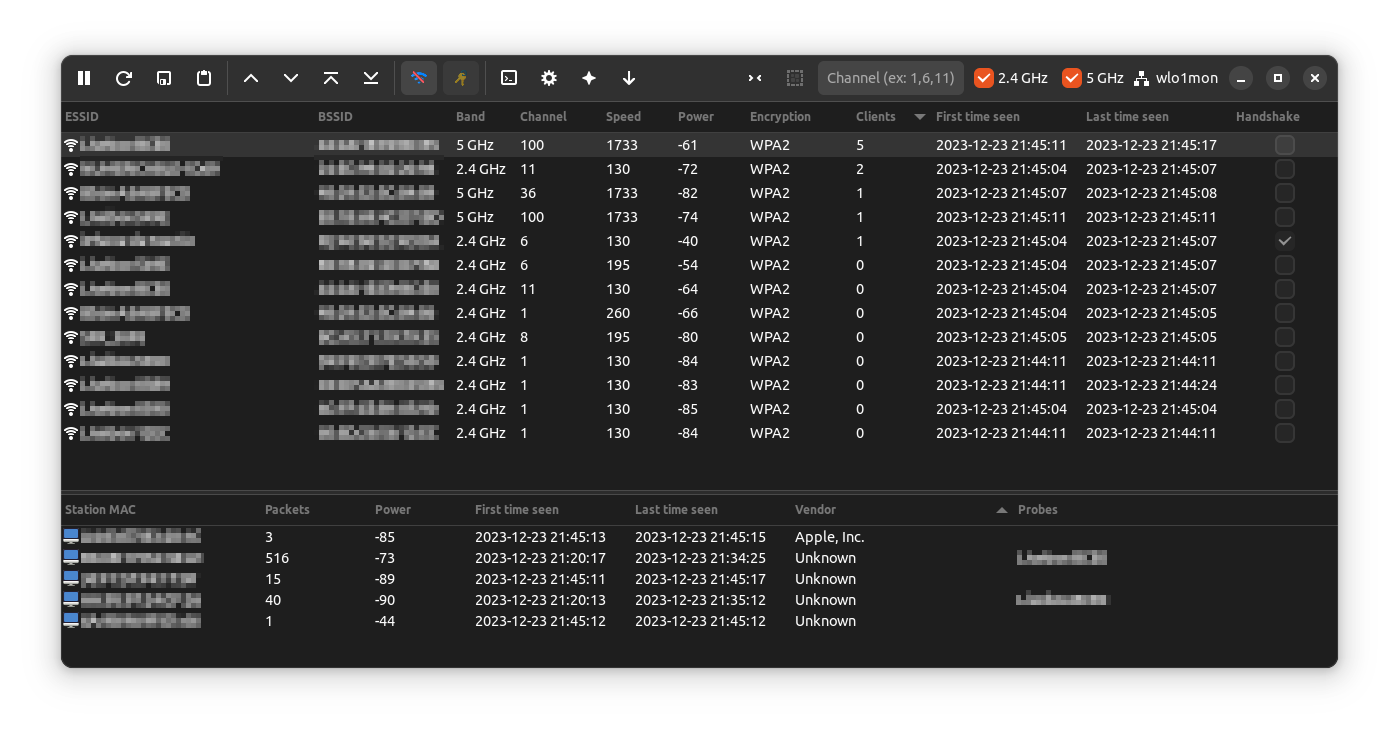 martin-olivier/airgorah
Rust-based GUI tool for WiFi security auditing: captures traffic, discovers clients, performs deauthentication attacks, captures handshakes, and…
 helviojunior/knowsmore
Correlates NTLM hashes, BloodHound data, and cracked passwords for Active Directory penetration testing. Imports NTDS.dit, syncs to Neo4j, analyzes…
 occasionpuffbird12/airstrike
Audit Wi-Fi security on Linux with monitor mode, handshake capture, and offline WPA/WPA2 password testing in one guided GUI
 lefayjey/linwinpwn
Bash script wrapping Active Directory tools for automated enumeration, vulnerability checks, exploitation, and password dumping via LDAP, RPC,…
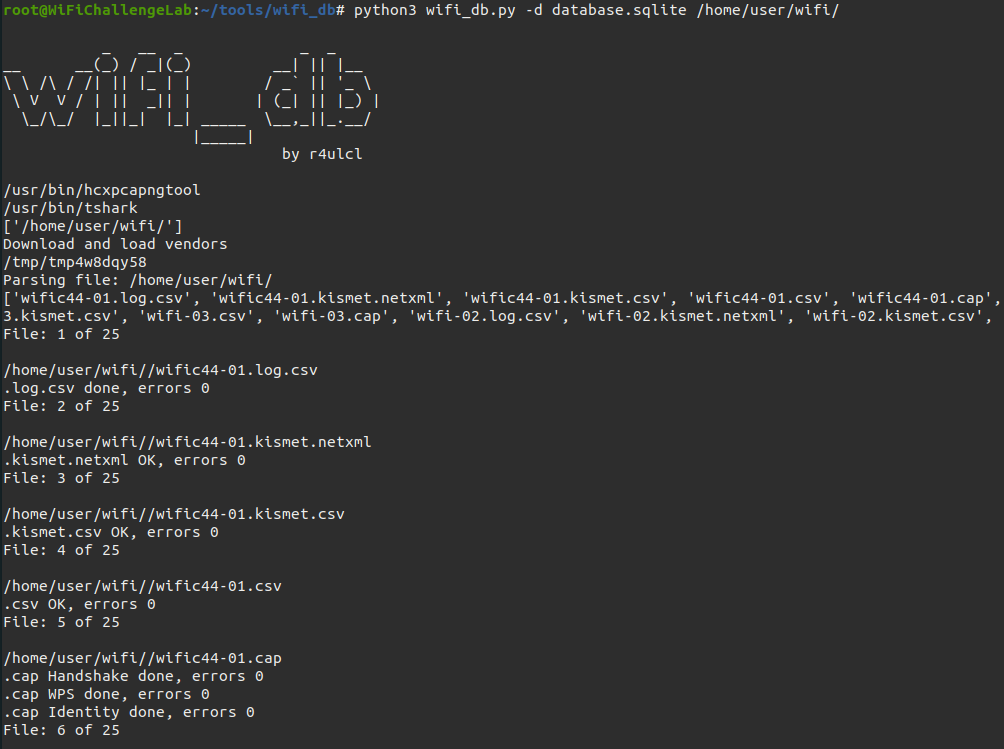 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
 evilsocket/legba
The fastest and more comprehensive multiprotocol credentials bruteforcer / password sprayer and enumerator. 🥷
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 hakluke/haklistgen
Turns any junk text into a usable wordlist for brute-forcing.
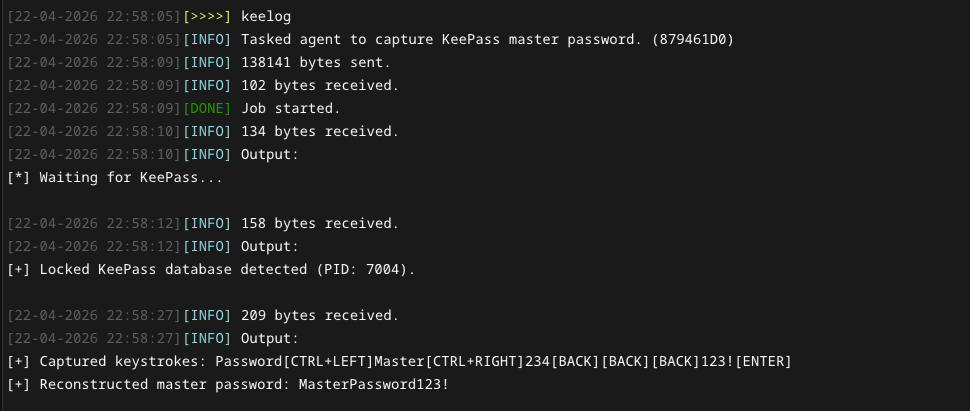 jakobfriedl/keelog-bof
Async BOF to capture KeePass master passwords by detecting and keylogging locked database windows.
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 mebus/cupp
Interactive password profiler that generates targeted wordlists by gathering personal details about a user, used for penetration testing and forensic…
 ivant7d3/cve-2025-44203
Exploit for CVE-2025-44203 targeting a race condition in HotelDruid 3.0.0/3.0.7 that leaks admin credentials and causes denial of service. Includes a…
 dhananjayasj/cve-2024-1698-notificationx-wordpress-plugin-sql-injection-to-admin-credential-extraction
Unauthenticated time-based blind SQL injection exploit for NotificationX WordPress plugin (CVE-2024-1698) that extracts admin username and password…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…