

digital-forensics-lab
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
ai-securityctfdigital-forensics+9
3.0k
frankwxu/digital-forensics-labFree hands-on digital forensics labs for students and faculty
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
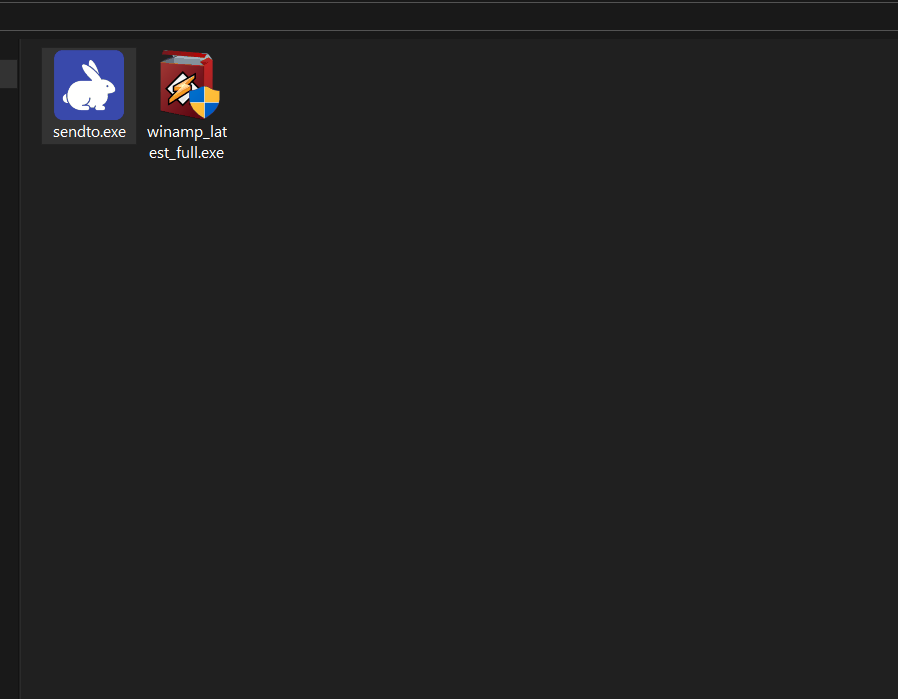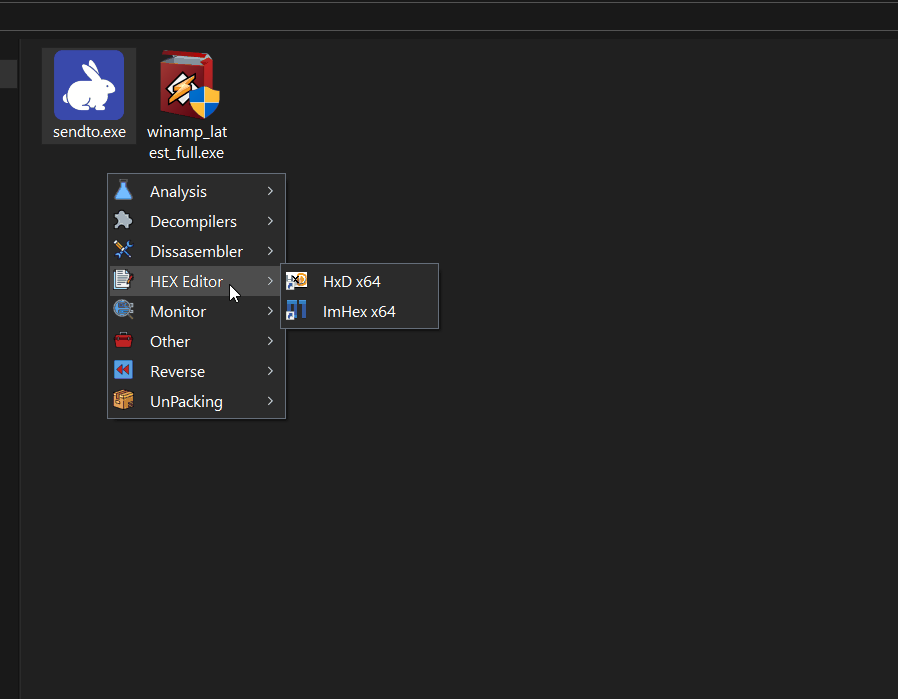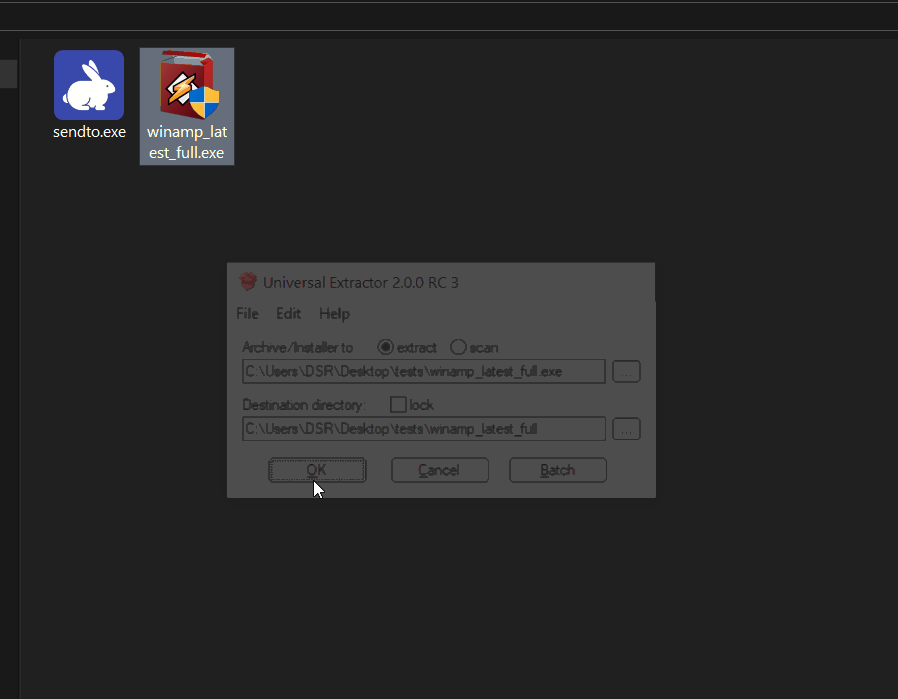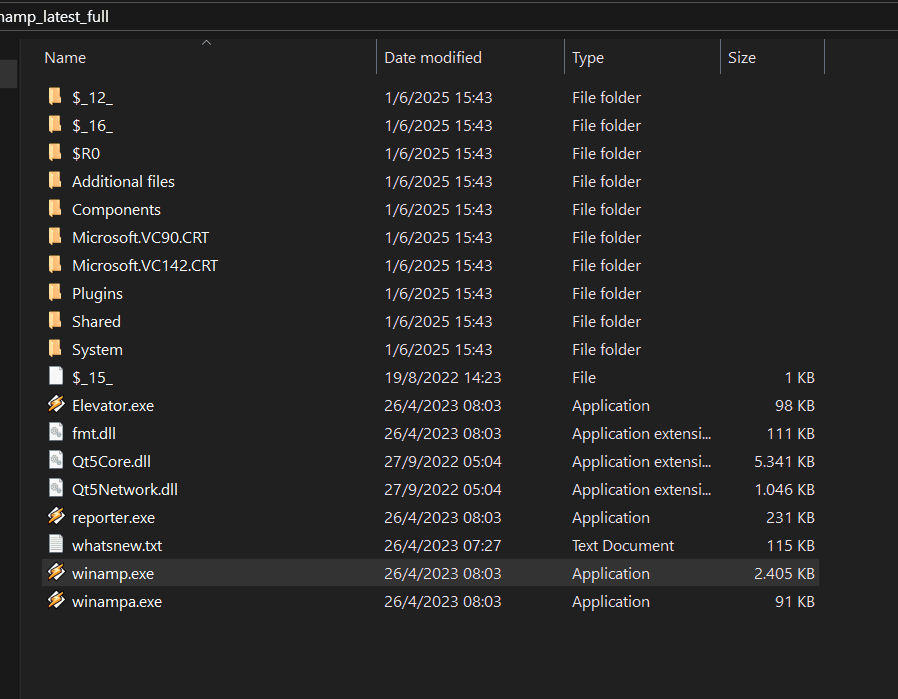 indetectables-net/toolkit
Curated Windows toolkit for reverse engineering, malware analysis, and password cracking. Includes 101 pre-configured tools with automatic updates…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
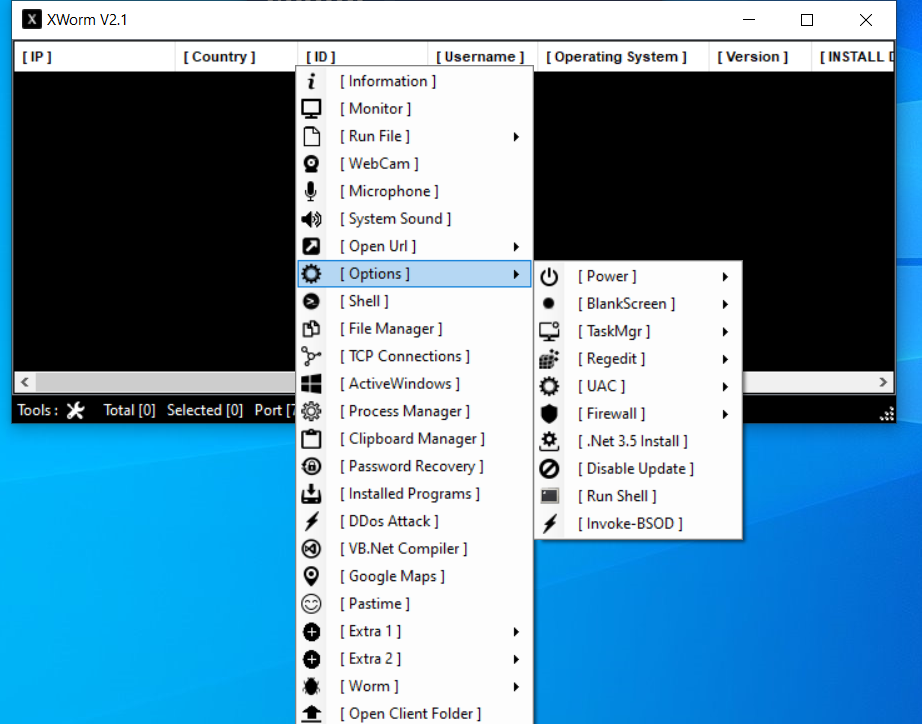
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
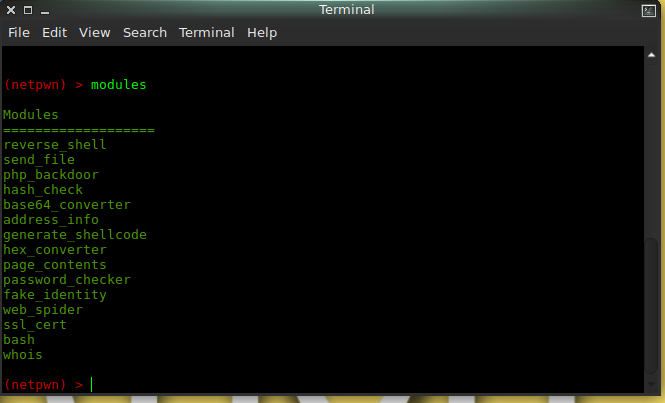 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
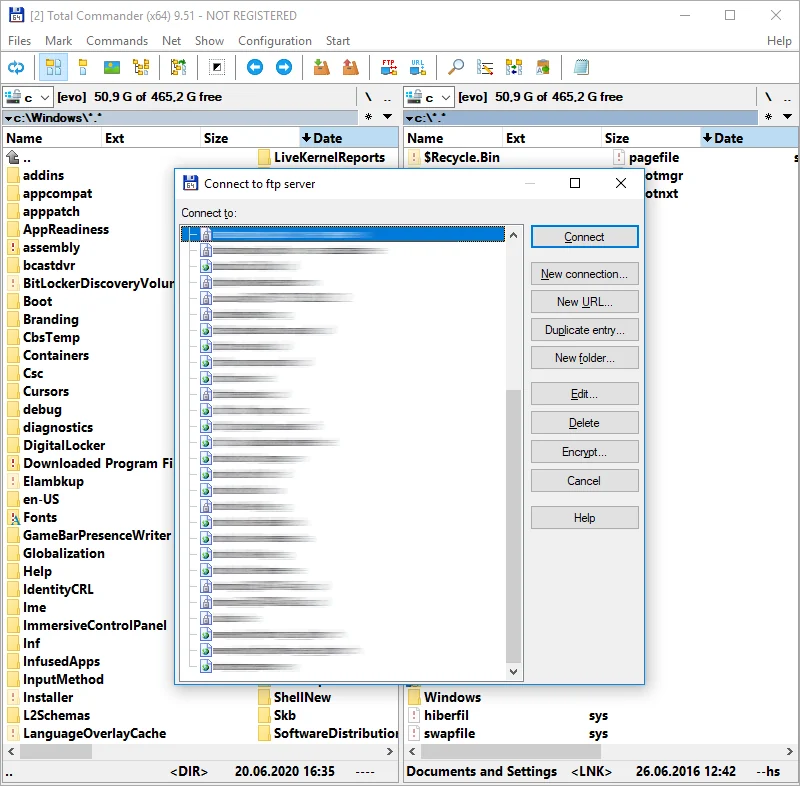 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 skelsec/pypykatz
Mimikatz implementation in pure Python
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
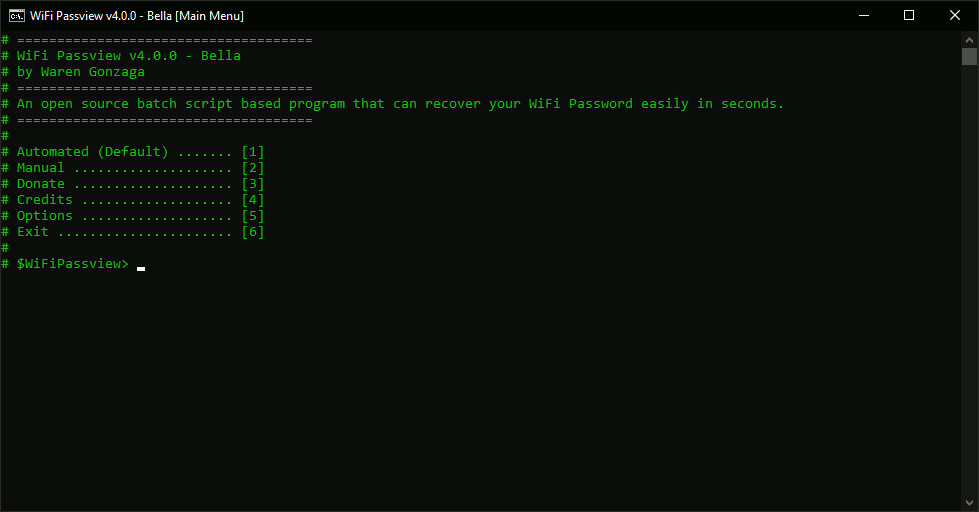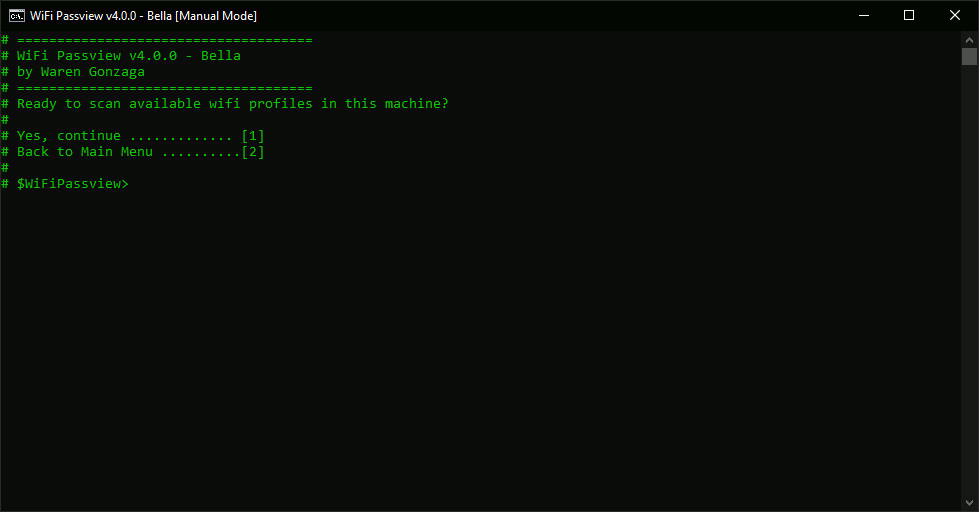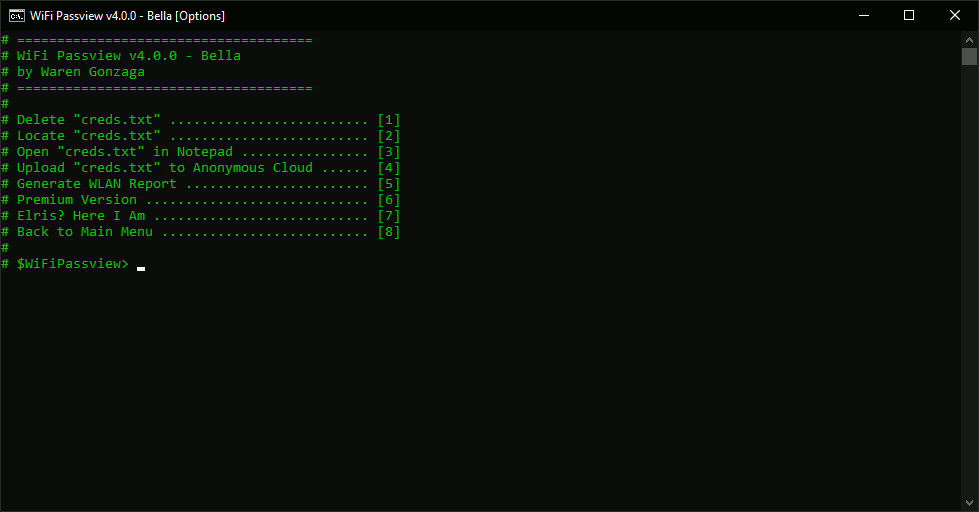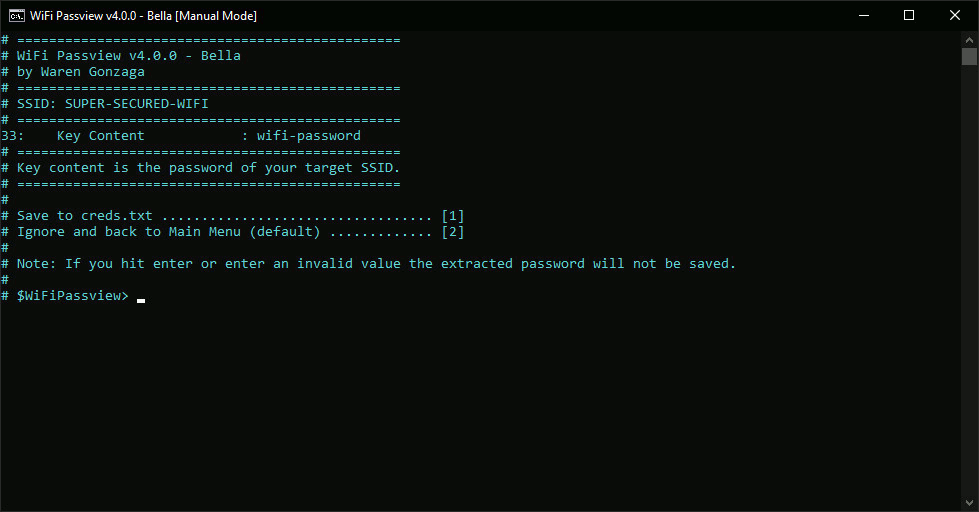 warengonzaga/wifi-passview
An open source batch script based WiFi Passview for Windows!
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…