Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubjeanback1/cve-2019-9053-exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
exploitationinformation-gatheringpassword-cracking+3
3 months ago
CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability preview

CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability

GitHubdhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability

Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
exploitationlateral-movementpassword-cracking+3
3 months ago
emploleaks preview

emploleaks

GitHubinfobyte/emploleaks

An OSINT tool that helps detect members of a company with leaked credentials
data-exfiltrationemail-harvestinginformation-gathering+8
7944 months ago
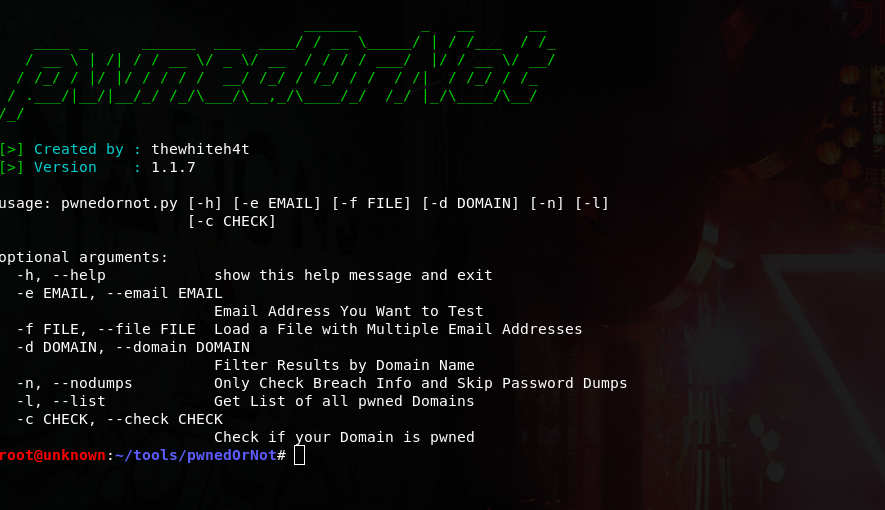
pwnedOrNot preview

pwnedOrNot

GitHubthewhiteh4t/pwnedornot

OSINT Tool for Finding Passwords of Compromised Email Addresses
information-gatheringosintpassword-cracking+1
2.6k5 months ago
CVE-2024-21413 preview

CVE-2024-21413

GitHubdionissh/cve-2024-21413

Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
email-securityexploitationpassword-cracking+3
7 months ago
cve-2024-21413-outlook-monikerlink-lab preview

cve-2024-21413-outlook-monikerlink-lab

GitHubviniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab

Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.

educationemail-securityexploitation+3
8 months ago
Email-exploit-Moniker-Link-CVE-2024-21413- preview

Email-exploit-Moniker-Link-CVE-2024-21413-

GitHubyass2400012/email-exploit-moniker-link-cve-2024-21413-

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
educationemail-securityexploitation+6
0 years ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

encryption-decryption-toolsforensicshash-analysis+8
11.0k1 year ago
CVE-2020-13941 preview

CVE-2020-13941

GitHubmbadanoiu/cve-2020-13941

CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr
authenticationexploitationlateral-movement+3
1 year ago
Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413 preview

Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413

GitHubartemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
educationexploitationlabs-practice+5
1 year ago
CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053- preview

CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053-

GitHubhf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
exploitationinformation-gatheringpassword-cracking+3
1 year ago
SocialPwned preview
Archived

SocialPwned

GitHubmrtuxx/socialpwned

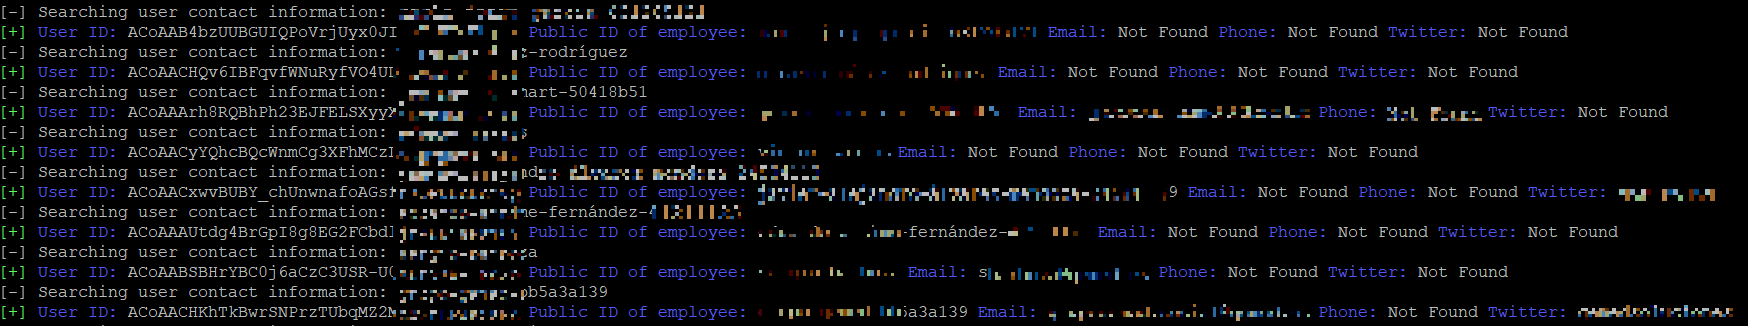
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to…
email-harvestinginformation-gatheringosint+5
1.3k1 year ago
CVE-2024-21413-Vulnerabilidad-Outlook-LAB preview

CVE-2024-21413-Vulnerabilidad-Outlook-LAB

GitHubd1se0/cve-2024-21413-vulnerabilidad-outlook-lab

Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
educationemail-securityexploitation+4
41 year ago
Sinister preview

Sinister

GitHubpushpenderindia/sinister

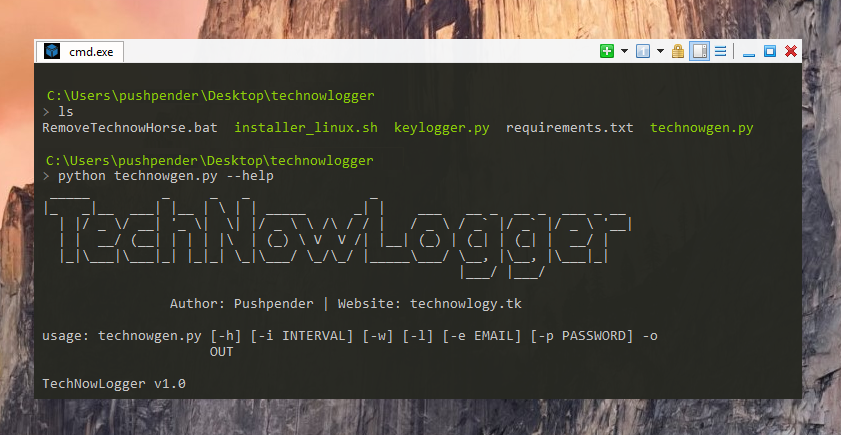
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info

data-exfiltrationinformation-gatheringpassword-cracking+5
4671 year ago
SSH-Private-Key-Looting-Wordlists preview

SSH-Private-Key-Looting-Wordlists

GitHubpinoywh1z/ssh-private-key-looting-wordlists

Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…

lateral-movementpassword-crackingpenetration-testing
562 years ago
https-github.com-xaitax-CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability preview

https-github.com-xaitax-CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability

GitHubfathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability

Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…

email-securityexploitationpassword-cracking+4
2 years ago
hashcrack preview

hashcrack

GitHubnccgroup/hashcrack

Guesses hash types, picks some sensible dictionaries and rules for hashcat
hash-analysispassword-attackspassword-cracking
1012 years ago
DragonCastle preview

DragonCastle

GitHubmdsecactivebreach/dragoncastle

A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.

lateral-movementpassword-crackingpost-exploitation
3073 years ago
Previous12Next