archlive
 p3ng0s/archlive
Physical access red team live ISO built on Arch Linux
password-crackingpenetration-testingpost-exploitation+2
p3ng0s/archlivePhysical access red team live ISO built on Arch Linux
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
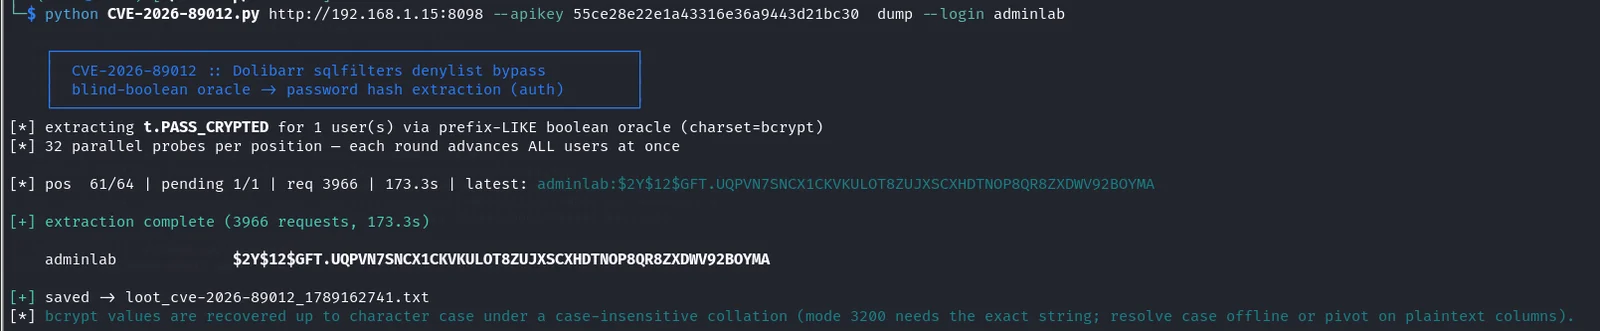 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 0xsyr0/vx-underground-wordlist
Wordlist to crack .zip-file password
 ignis-sec/pwdb-public
A collection of all the data i could extract from 1 billion leaked credentials from internet.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 manio/mtpass
MikroTik Password Recovery Tool