

EasY_HaCk
 sabri-zaki/easy_hack
Hack the World using Termux
exploit-frameworksinformation-gatheringnetwork-mapping+4
sabri-zaki/easy_hackHack the World using Termux
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
 incommatose/cve-2023-6063-poc
A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 verylazytech/cve-2024-4956
POC - CVE-2024–4956 - Nexus Repository Manager 3 Unauthenticated Path Traversal
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
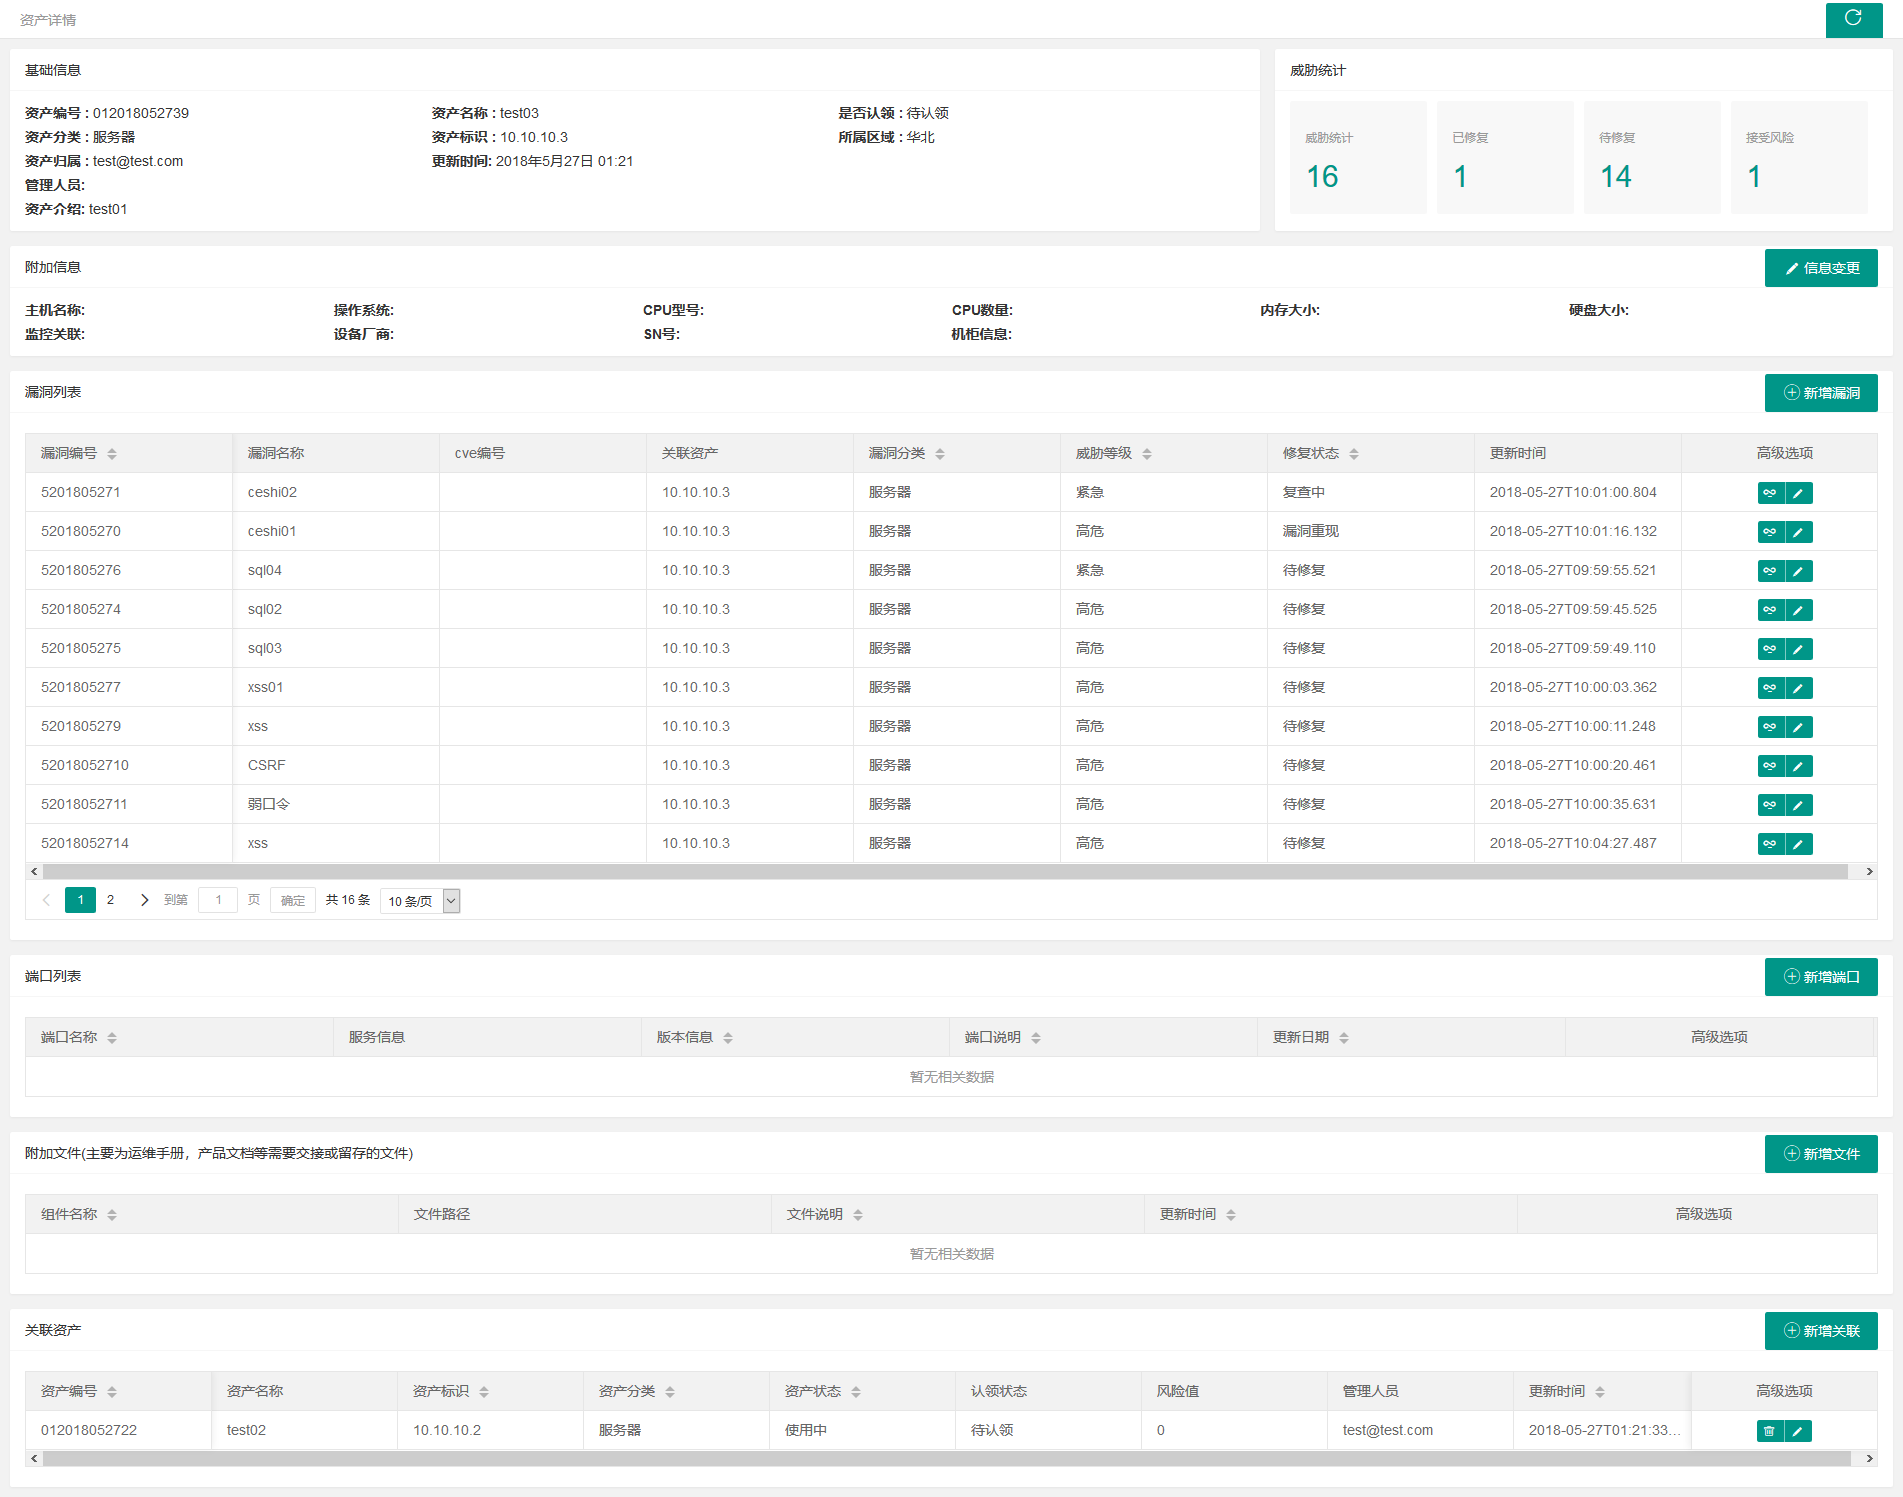 we1h0/securitymanageframwork
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)