

EasY_HaCk
 sabri-zaki/easy_hack
Hack the World using Termux
exploit-frameworksinformation-gatheringnetwork-mapping+4
sabri-zaki/easy_hackHack the World using Termux
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 brannondorsey/wifi-cracking
Crack WPA/WPA2 Wi-Fi Routers with Airodump-ng and Aircrack-ng/Hashcat
 cisc0-gif/kitt
Python-Based Pentesting Framework
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
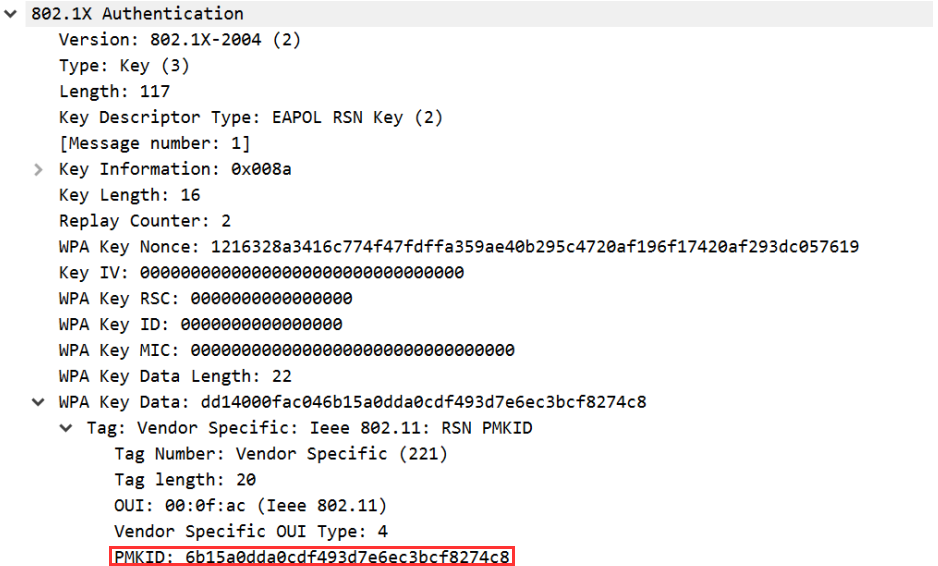 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 blackploit/hash-identifier
Software to identify the different types of hashes used to encrypt data and especially passwords
 blackarch/wordlistctl
Fetch, install and search wordlist archives from websites and torrent peers.
 martin-olivier/airgorah
Rust-based GUI tool for WiFi security auditing: captures traffic, discovers clients, performs deauthentication attacks, captures handshakes, and…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
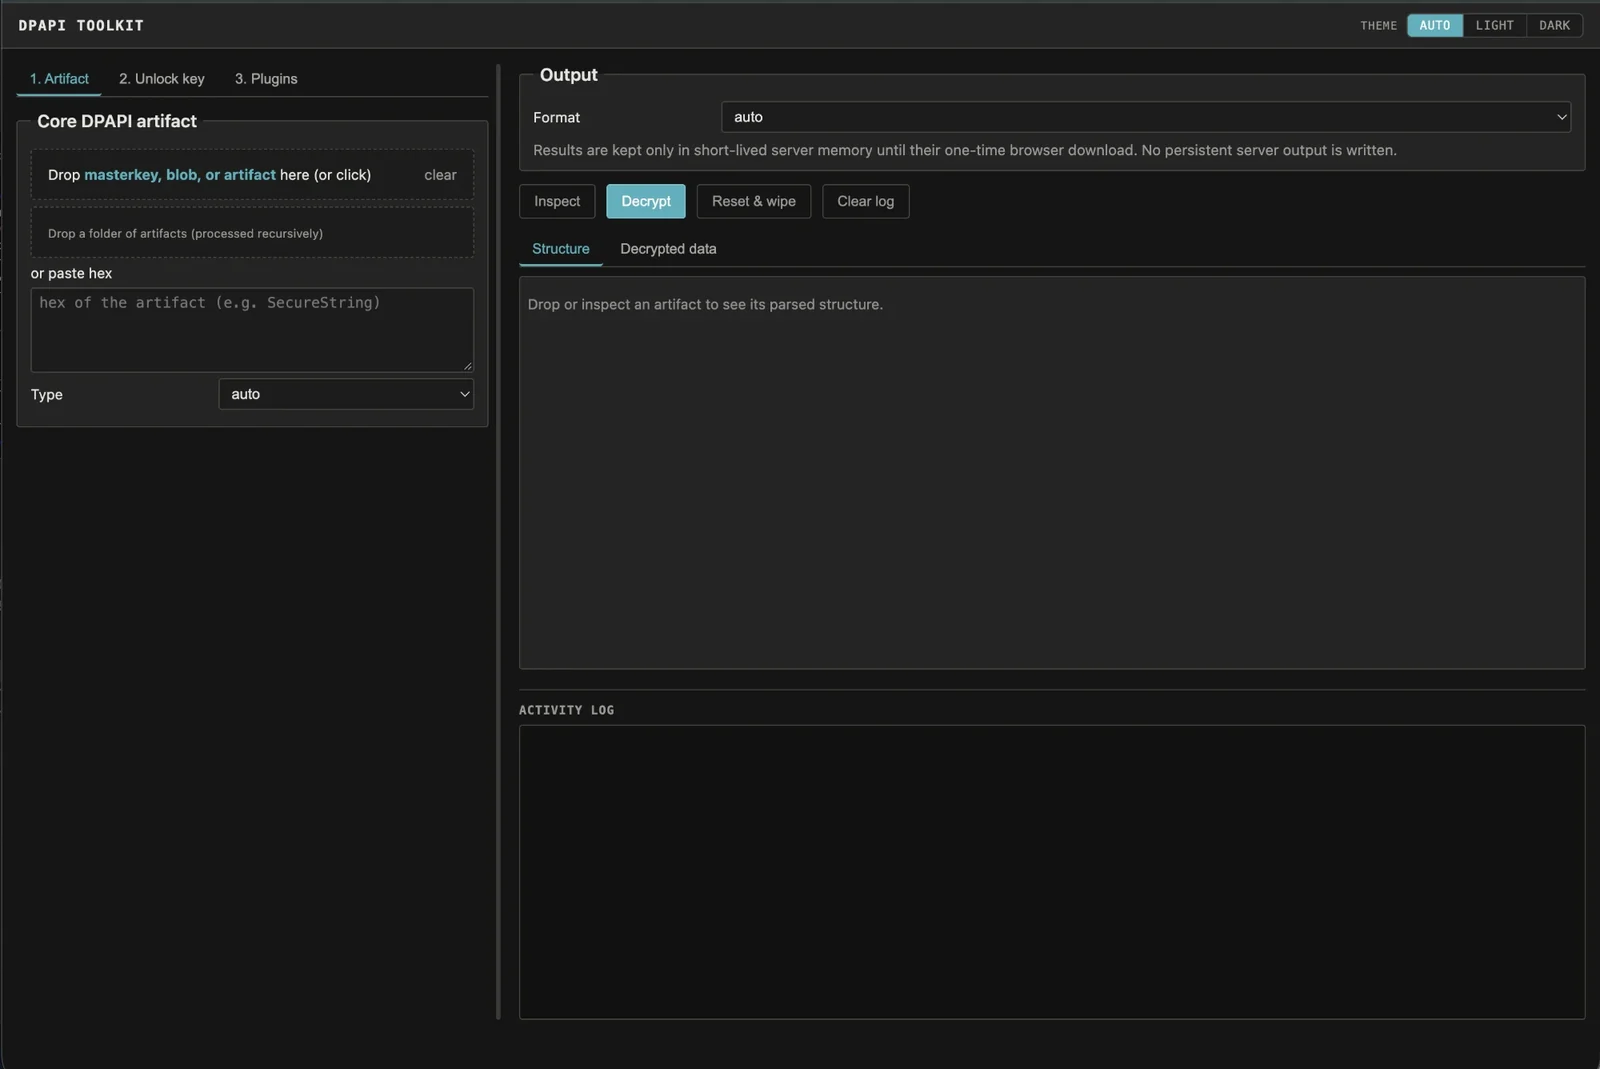 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…