

 arcaneiceman/kraken
Distributed brute-force password cracking system that parallelizes dictionary and crunch-based attacks across multiple machines via web and desktop…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 brannondorsey/passgan
A Deep Learning Approach for Password Guessing (https://arxiv.org/abs/1709.00440)
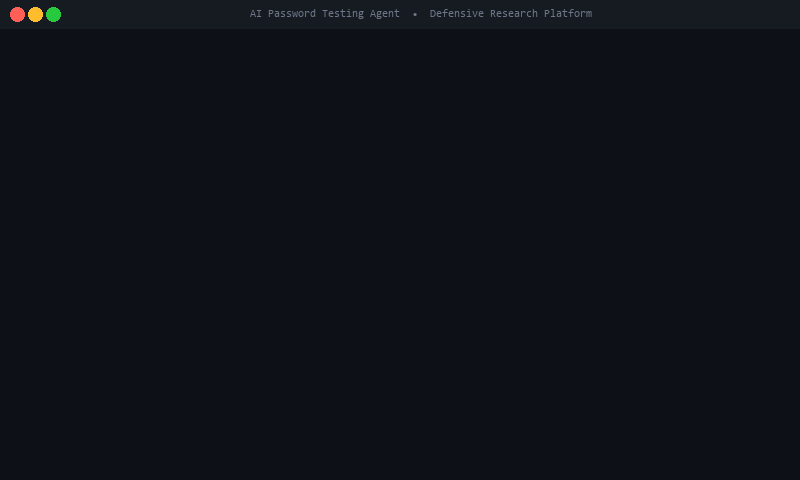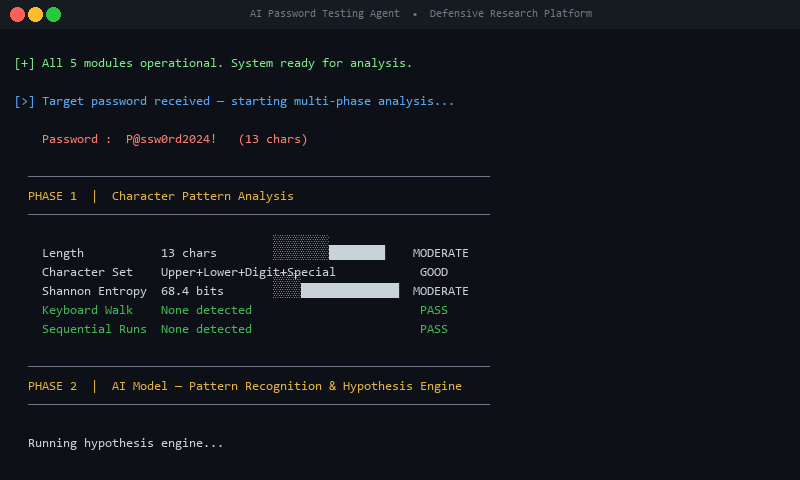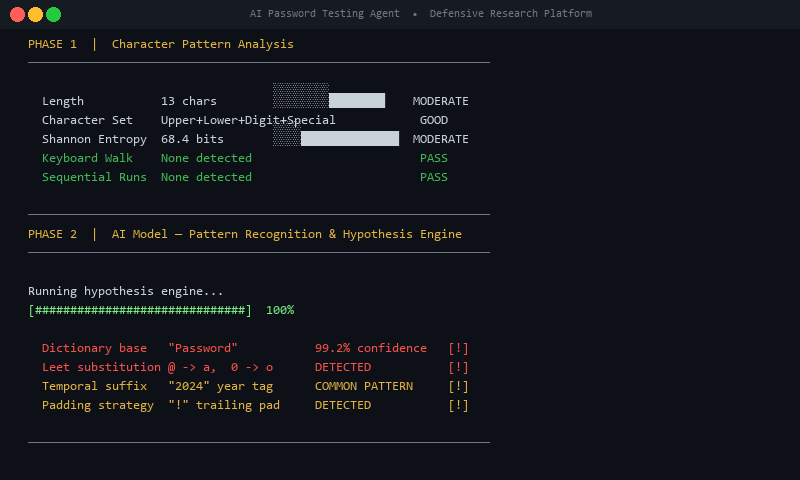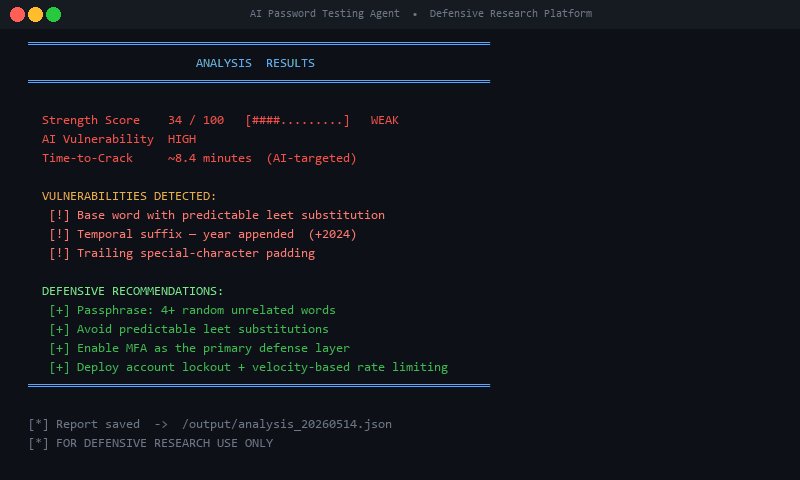 insider77circle/ai-password-testing-agent
An intelligent agent for testing password strength, identifying vulnerabilities, and exploring patterns in password creation.
 rndinfosecguy/scavenger
Crawler (Bot) searching for credential leaks on paste sites.
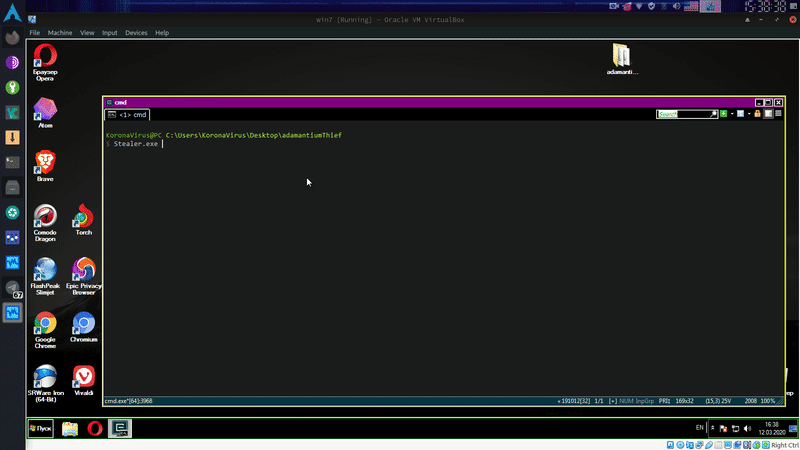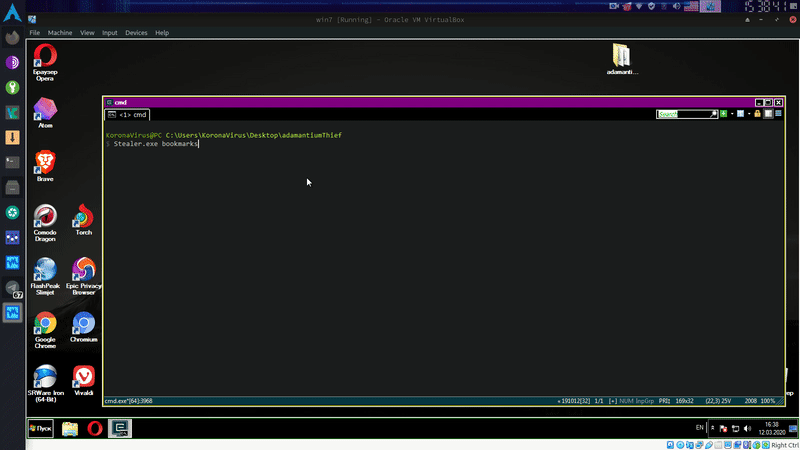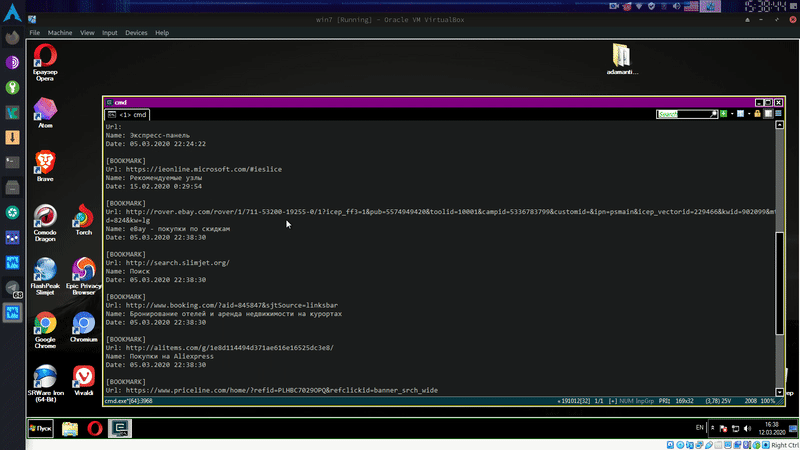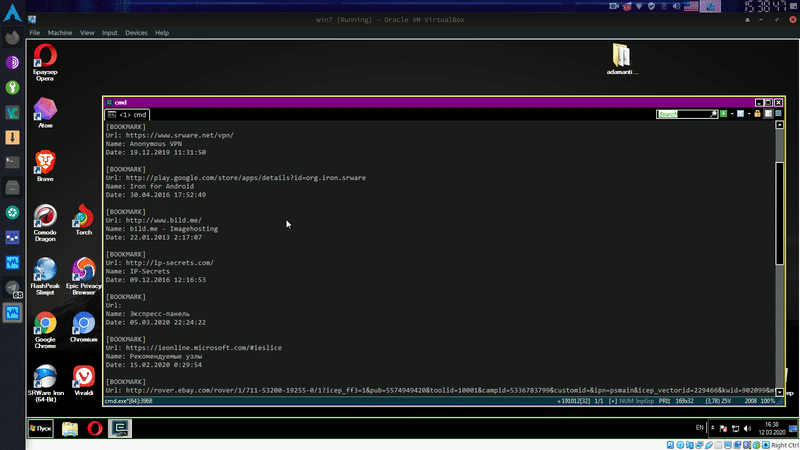 limerboy/adamantium-thief
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
 cvonkleist/vxworks_hash
code to reverse vxworks 5.x password hashes
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 jtesta/rainbowcrackalack
Rainbow table generation & lookup tools. Make Rainbow Tables Great Again!
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 gmikisilva/cve-2024-33901-proofofconcept
Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
 yucaerin/cve-2024-55555
Laravel Crypto Killer Mass Scanner (CVE-2024-55555)