
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 joelgmsec/autordpwn
The Shadow Attack Framework
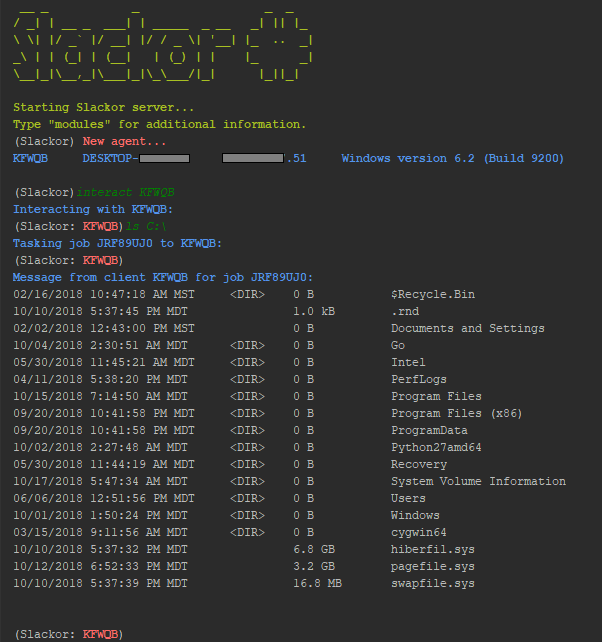 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
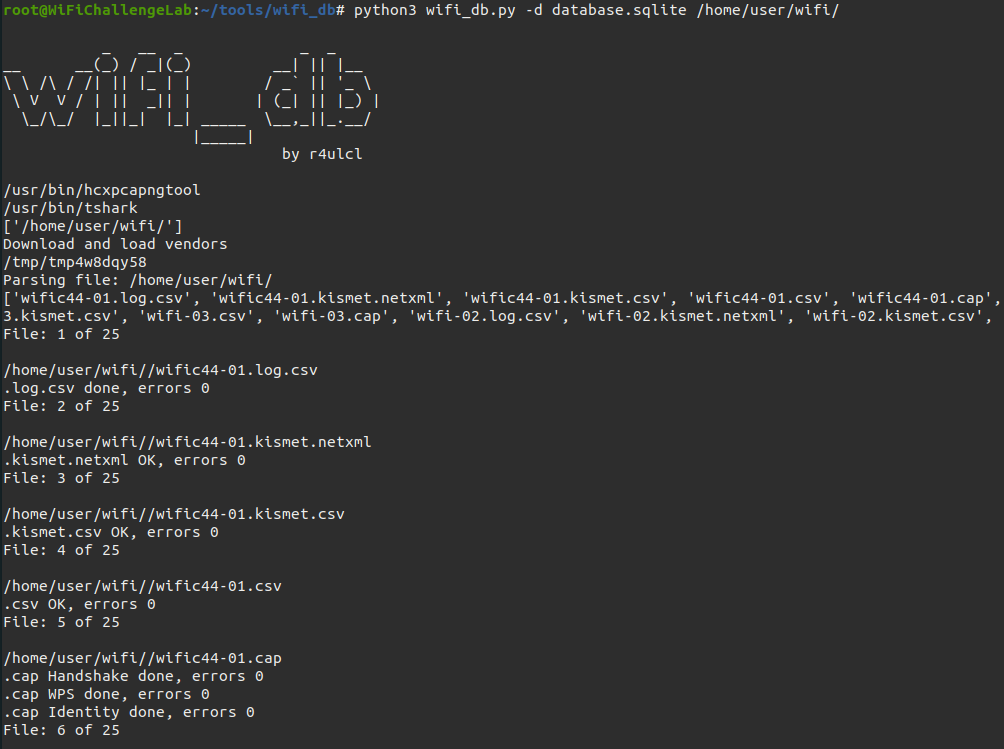 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 pinoywh1z/ssh-private-key-looting-wordlists
Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…
 mbadanoiu/cve-2020-13941
CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 chron1k/oxide_hive
Exploit for CVE-2021-36934