

Make-and-Break
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
educationexploitationexploit-frameworks+6
1
rayferrufino/make-and-breakBuilt a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
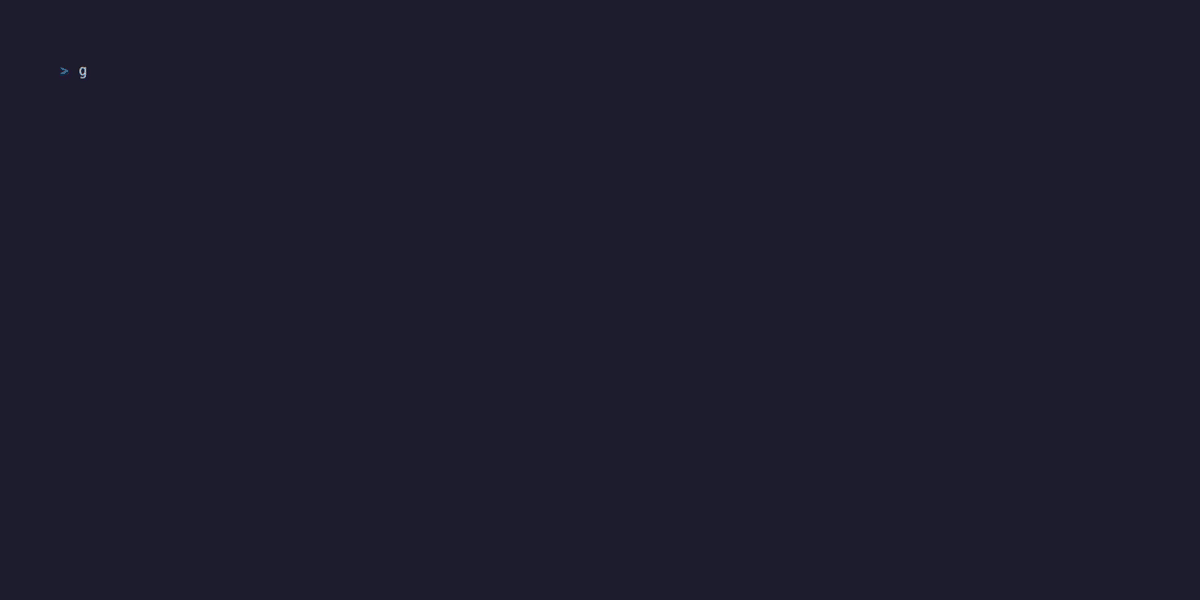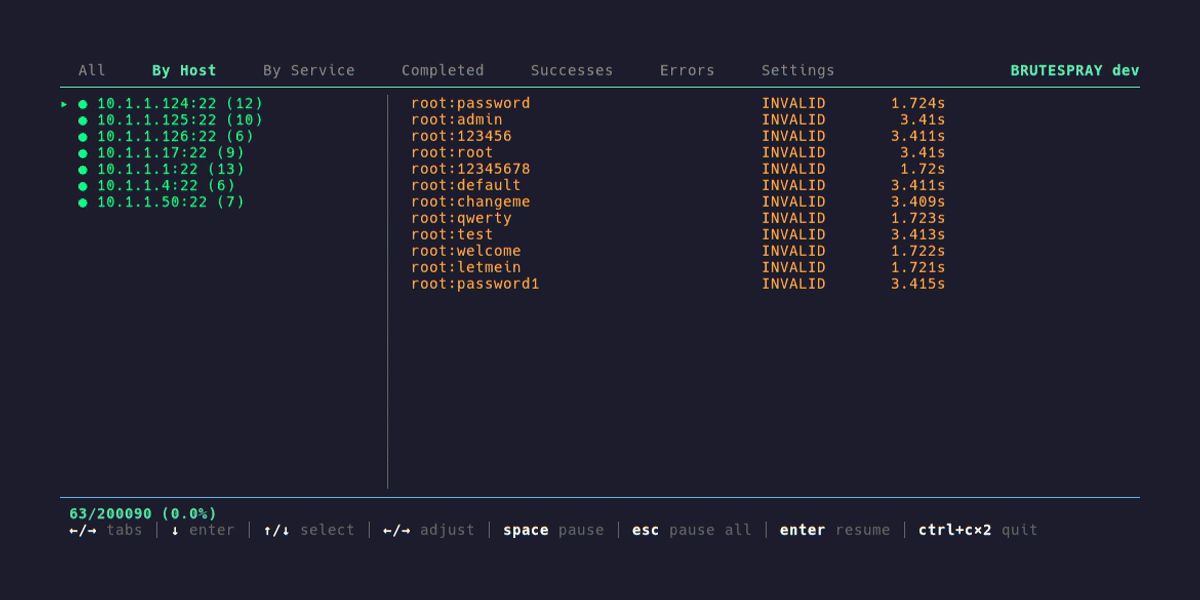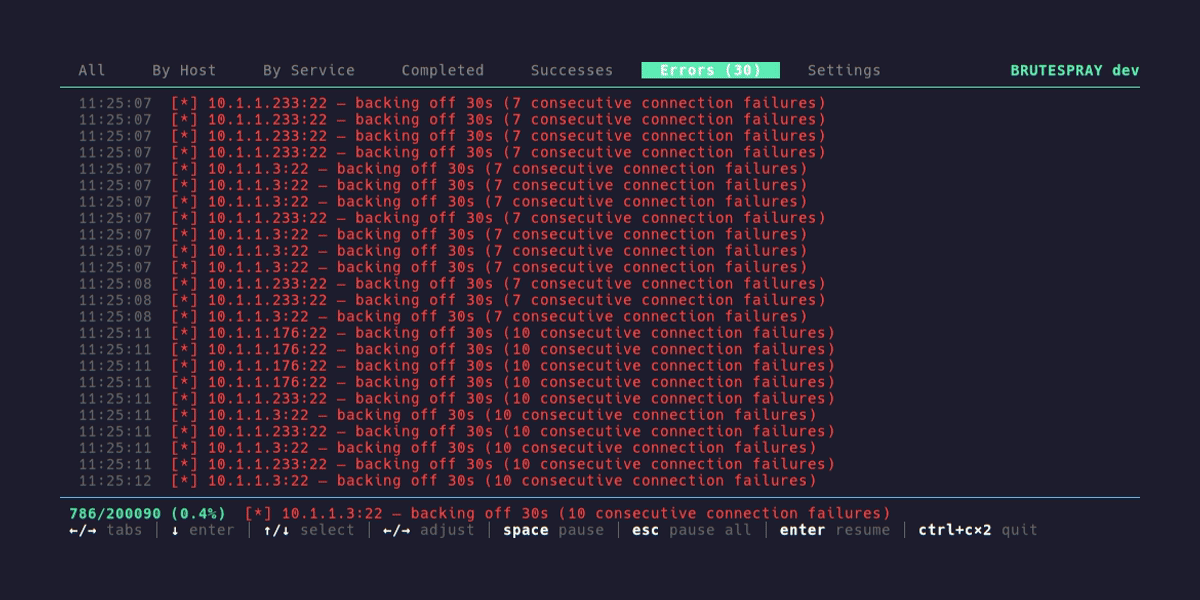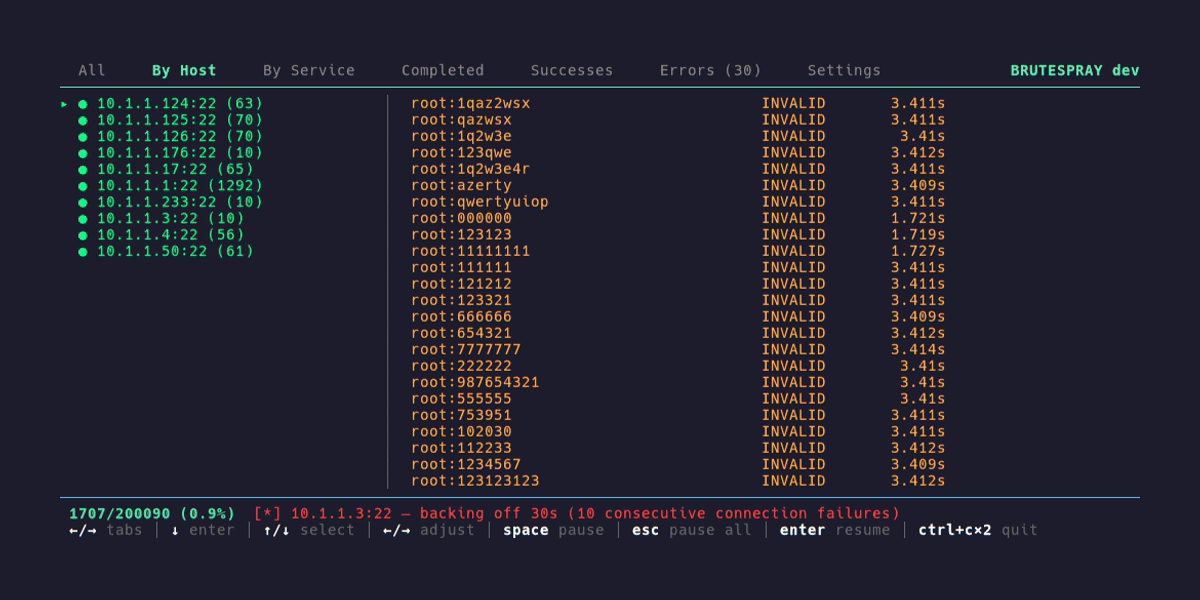 x90skysn3k/brutespray
Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+…
 hahwul/jwt-hack
JSON Web Token Hack Toolkit
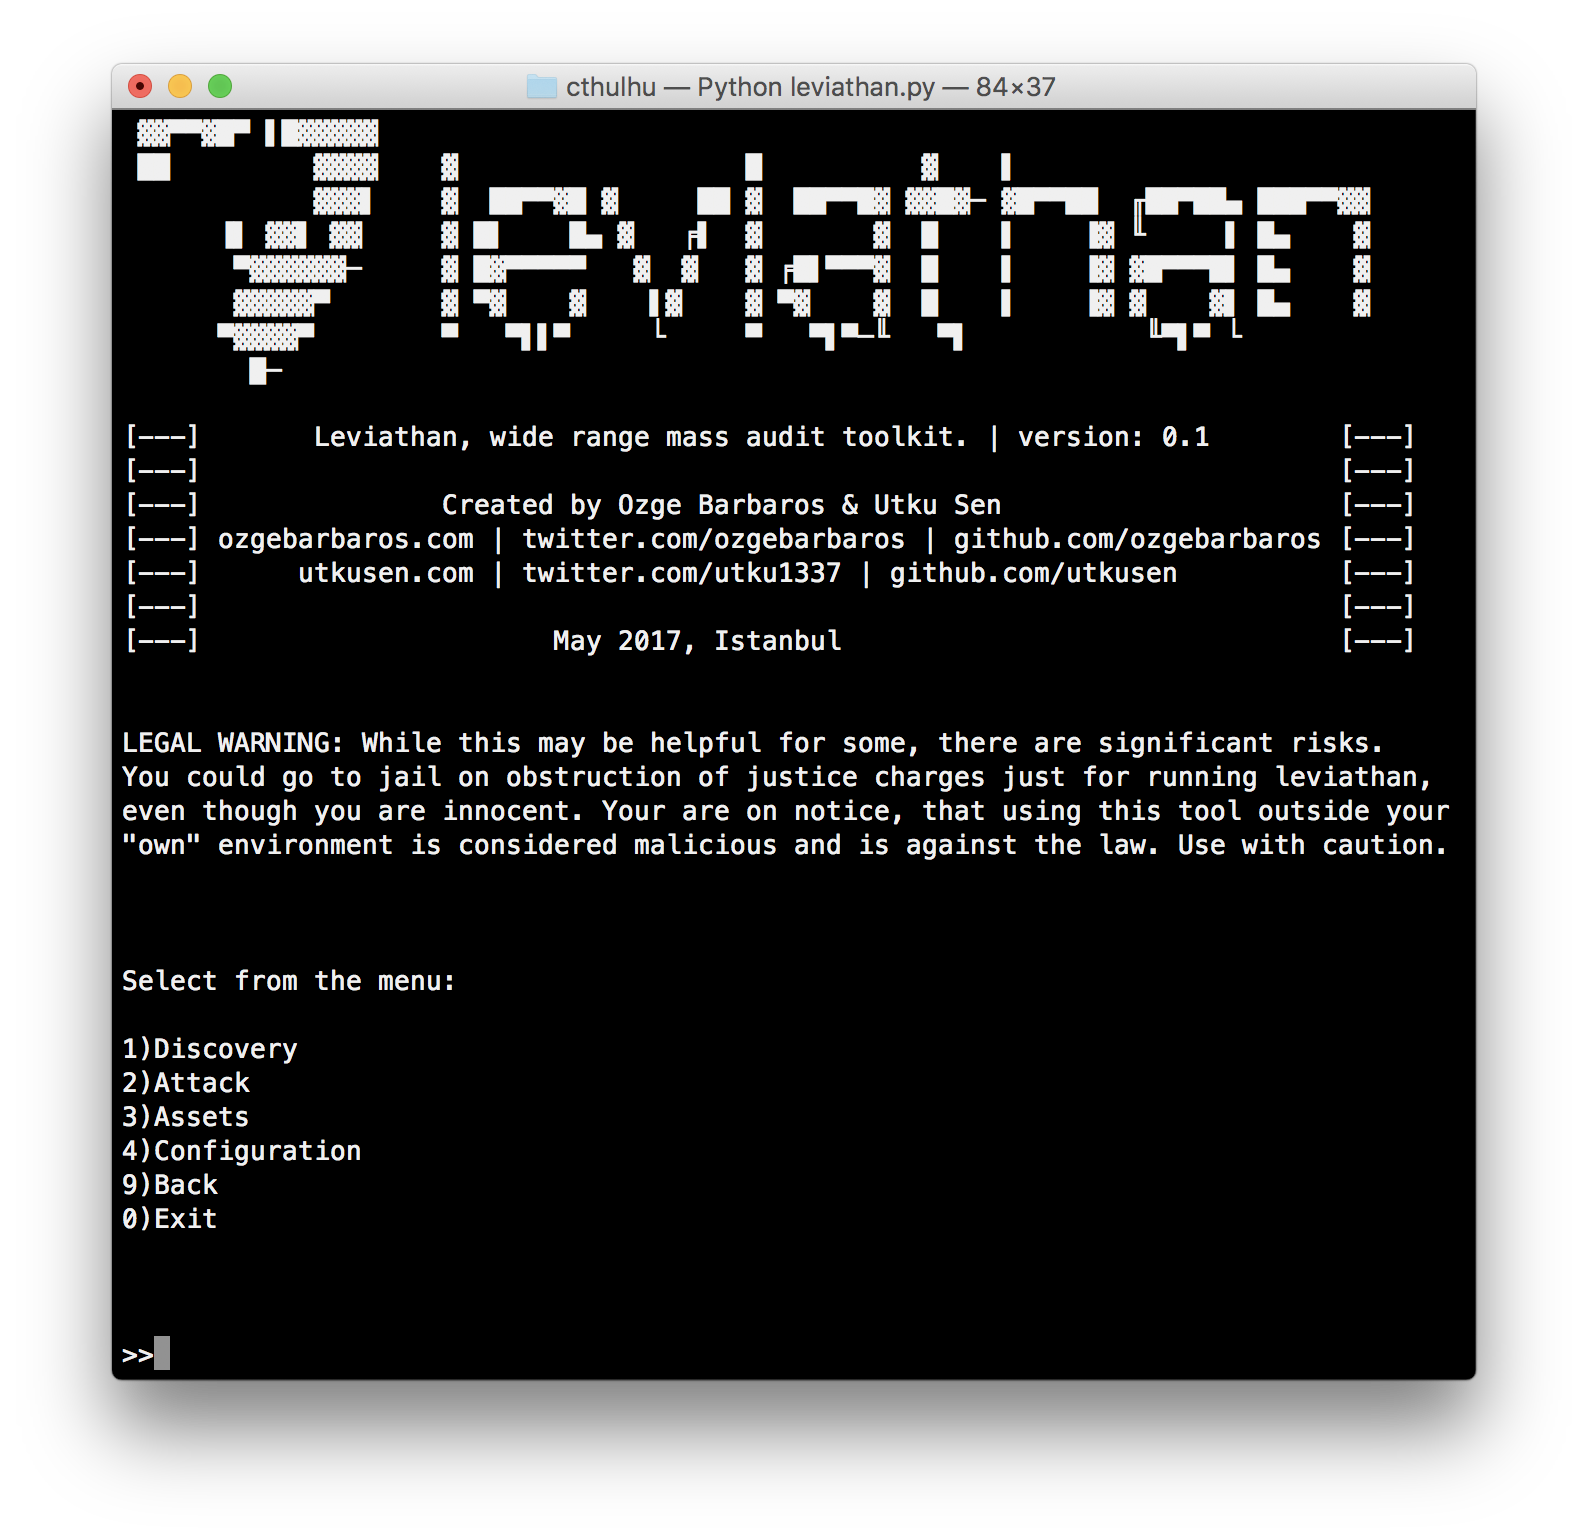 utkusen/leviathan
wide range mass audit toolkit
 helviojunior/knowsmore
Correlates NTLM hashes, BloodHound data, and cracked passwords for Active Directory penetration testing. Imports NTDS.dit, syncs to Neo4j, analyzes…
 entry33/aes256_passwd_store
AES-256 encrypted password manager with scrypt/SHA256 key derivation, supporting create, edit, query, and master password change operations with…
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 lithnet/ad-password-protection
Active Directory password filter featuring breached password checking and custom complexity rules
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 gquere/cve-2019-6693
Decrypts FortiGate configuration secrets (CVE-2019-6693) for versions below 6.2.0, extracting encrypted passwords and keys from dumped configs using…
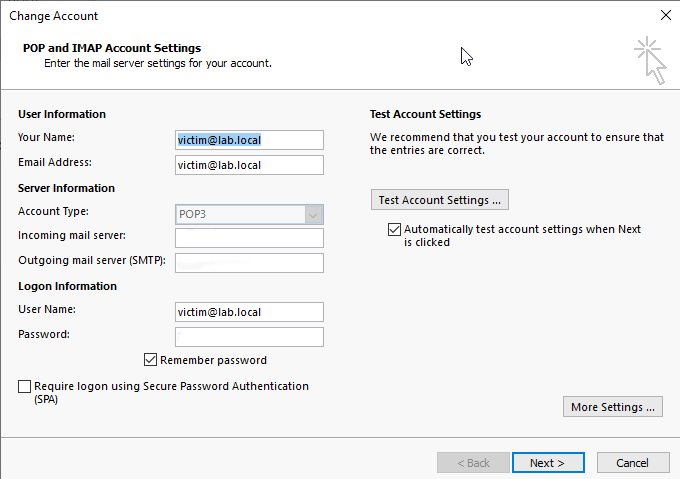 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…