
CVE-2026-63030
 4minx/cve-2026-63030
CVE-2026-63030 (wp2shell) POC.
exploitationpassword-attackspenetration-testing+2
4minx/cve-2026-63030CVE-2026-63030 (wp2shell) POC.
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
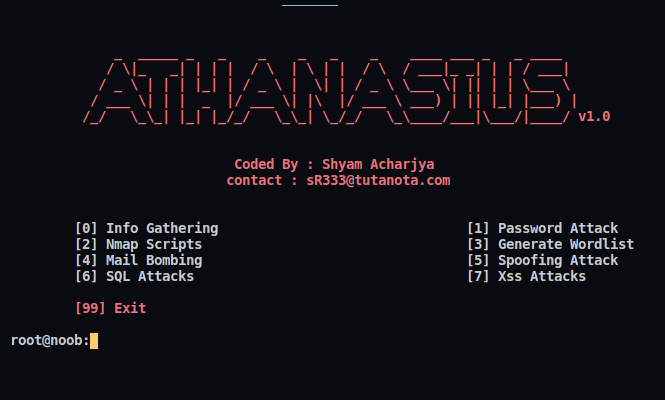 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
 karma-syndicate/xcrack-python-tools-for-hackers
Python Hacking Tool for Hackers And Spammers
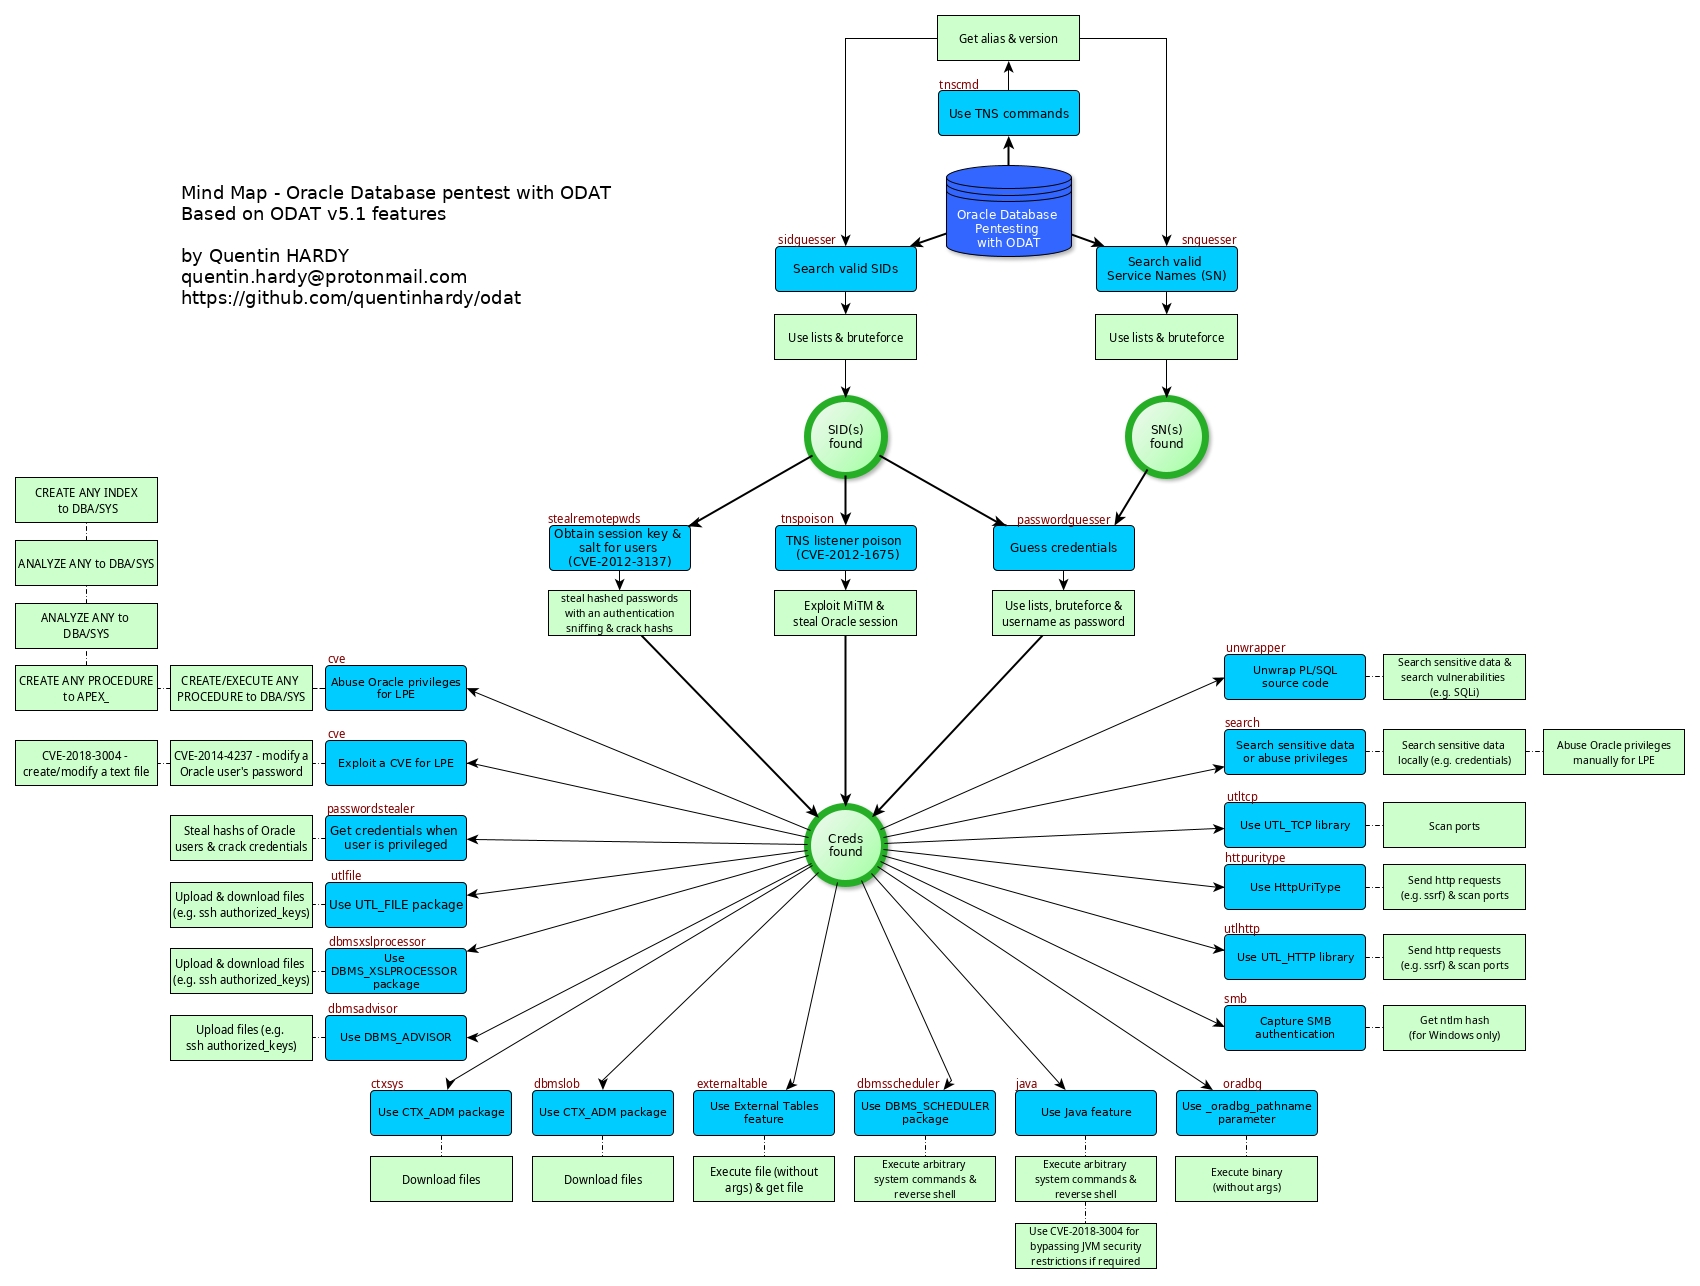 quentinhardy/odat
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
 b1u3st0rm/cve-2024-44812-poc
Proof of Concept Exploit for CVE-2024-44812 - SQL Injection Authentication Bypass vulnerability in Online Complaint Site v1.0
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
 oldboy21/ldap-password-hunter
Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…
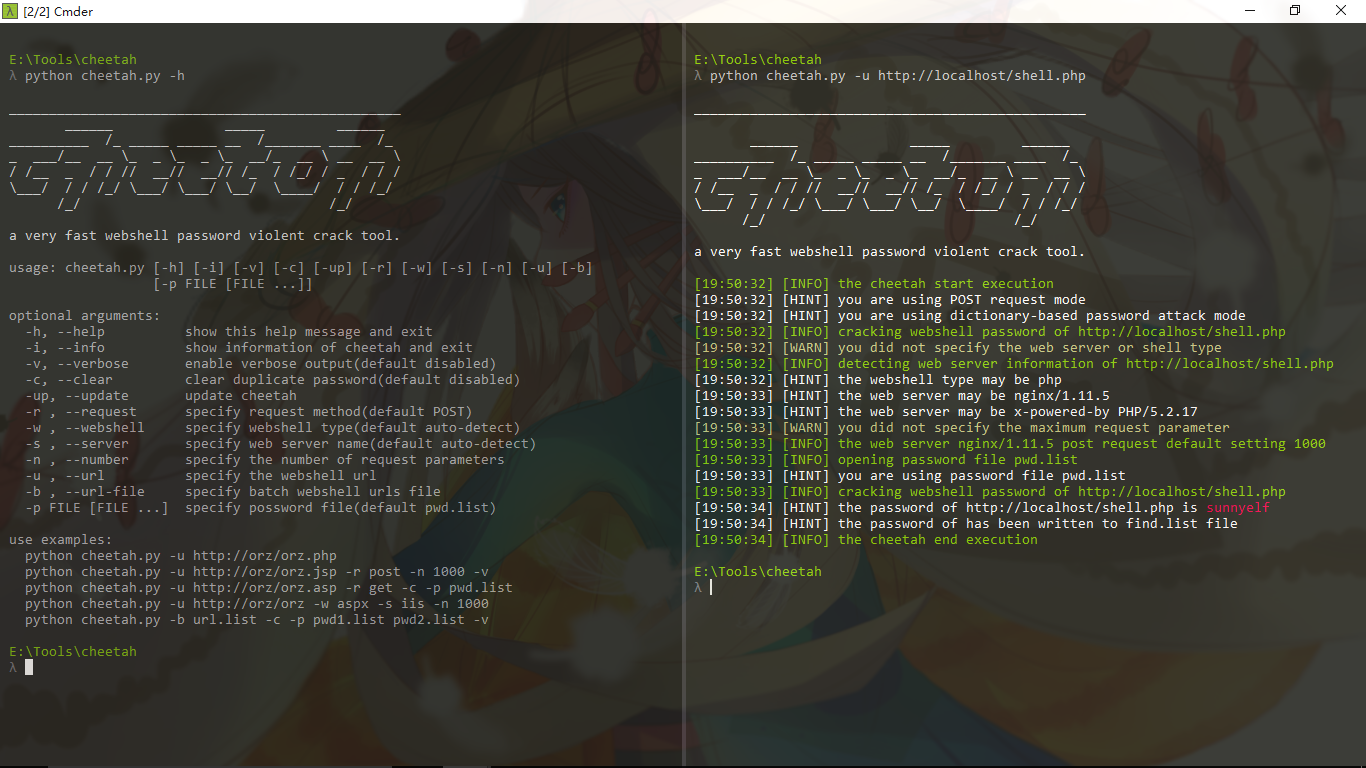 shmilylty/cheetah
a very fast brute force webshell password tool
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 initroot/wodat
Windows Oracle Database Attack Toolkit
 jas502n/openfire_decrypt
OpenFire 管理后台账号密码解密
 jas502n/database-druid
druid_decode