
CVE-2023-23397
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
email-securityexploitationpassword-attacks+3
132
trackflaw/cve-2023-23397Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
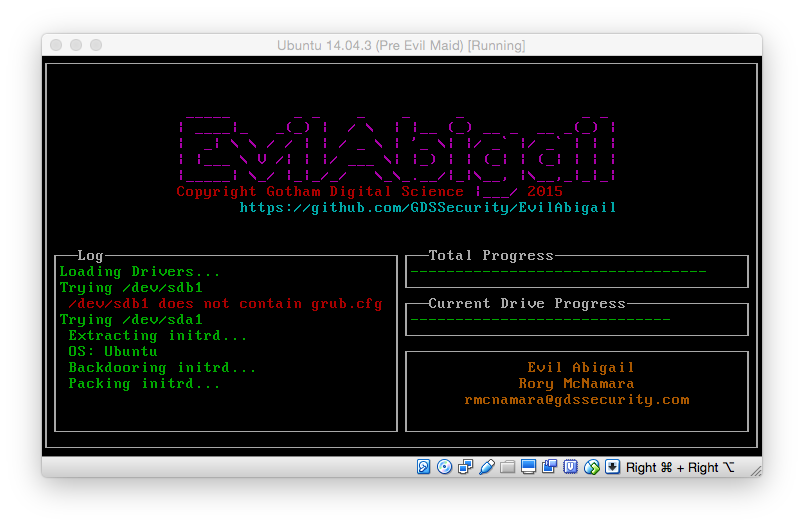 strozfriedberg/evilabigail
Automated Linux evil maid attack
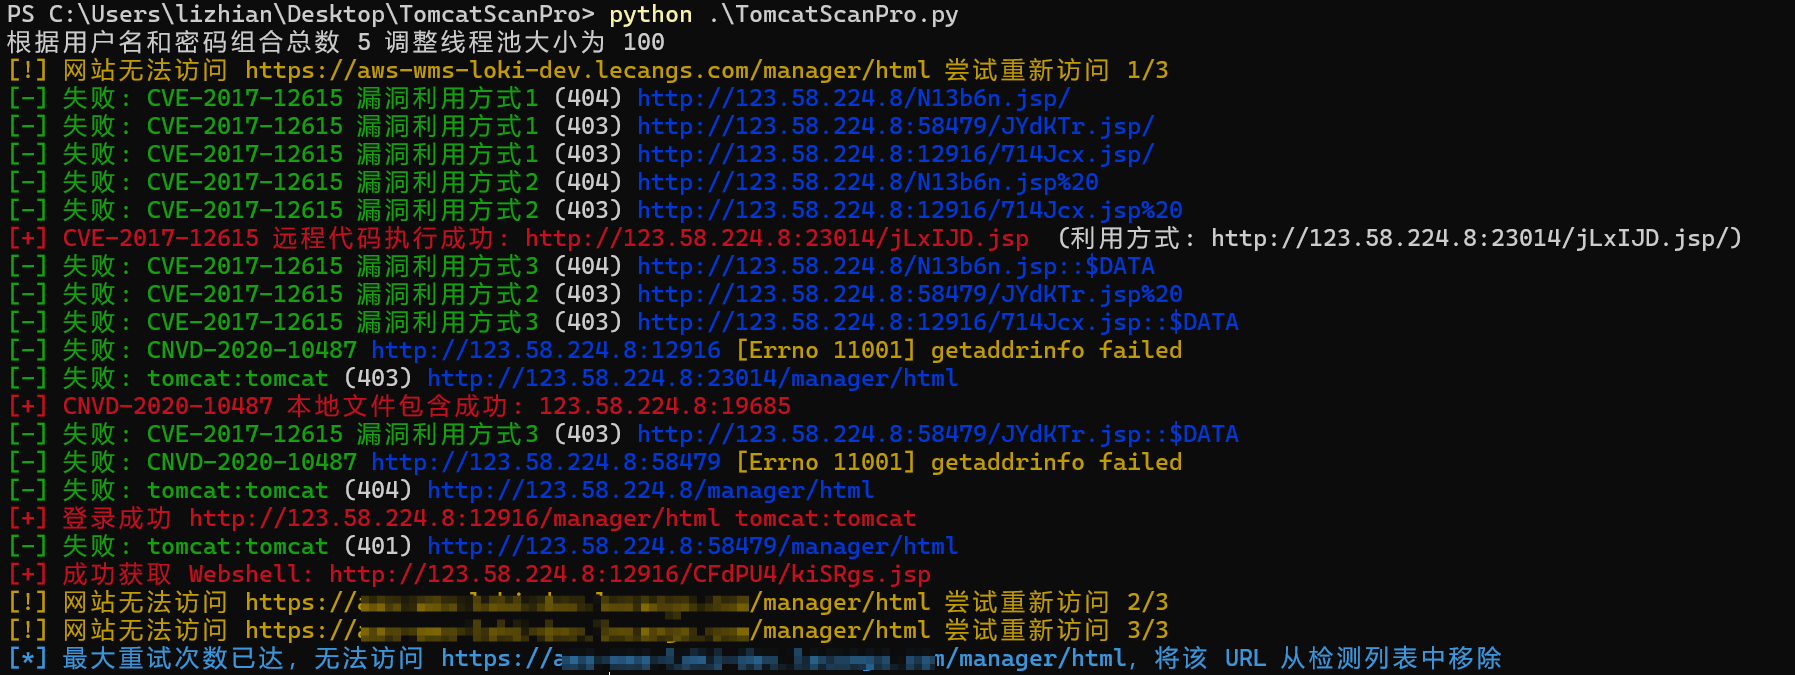 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
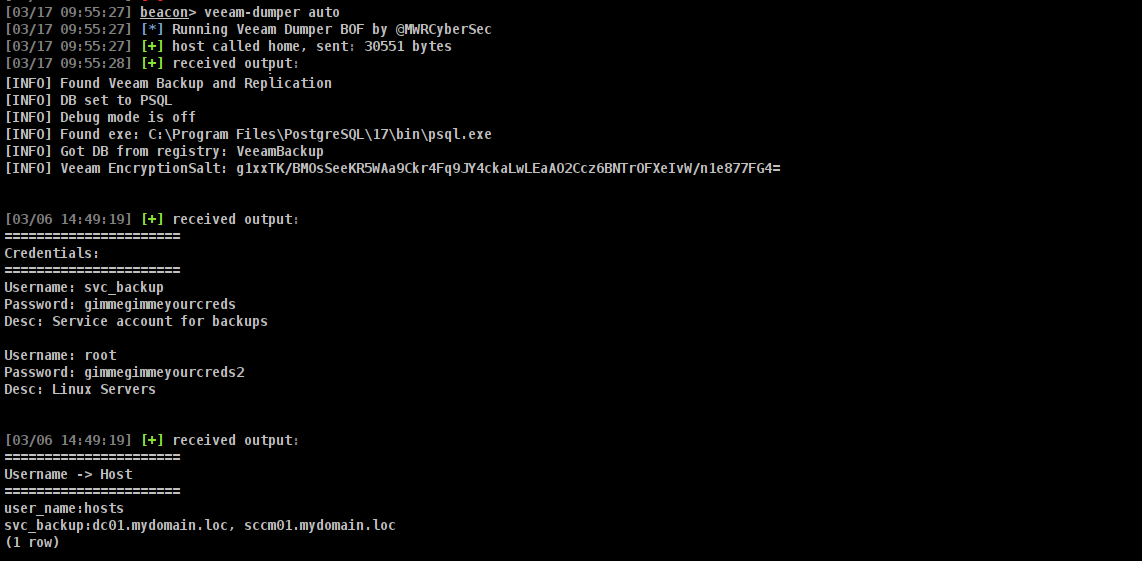 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…