Penetration-Testing-Walkthrough-Hacksudo-Thor

Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.

Security program for recovering passwords and pen-testing servers, routers and IoT devices using brute-force password attacks.

Modular credential validation framework with active and passive (regex-based) checking modes for penetration testers. Supports multiple services via…

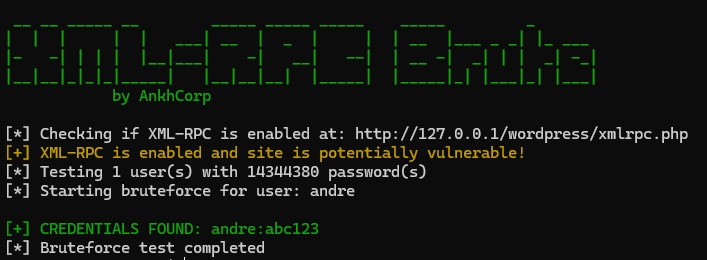
This tool tests WordPress installations for XML-RPC authentication vulnerabilities.

Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…

A tool to automate penetration tests

Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.

Black-box exploit for CVE-2025-21574 targeting MySQL servers. Automates credential brute-forcing, anonymous access attempts, and triggers server…

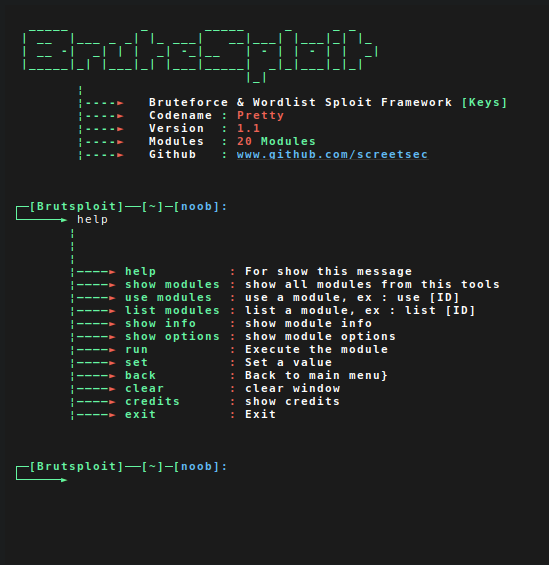
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…

Improved SMTP Checker / SMTP Cracker with proxy-support, inbox test and many more features.

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…

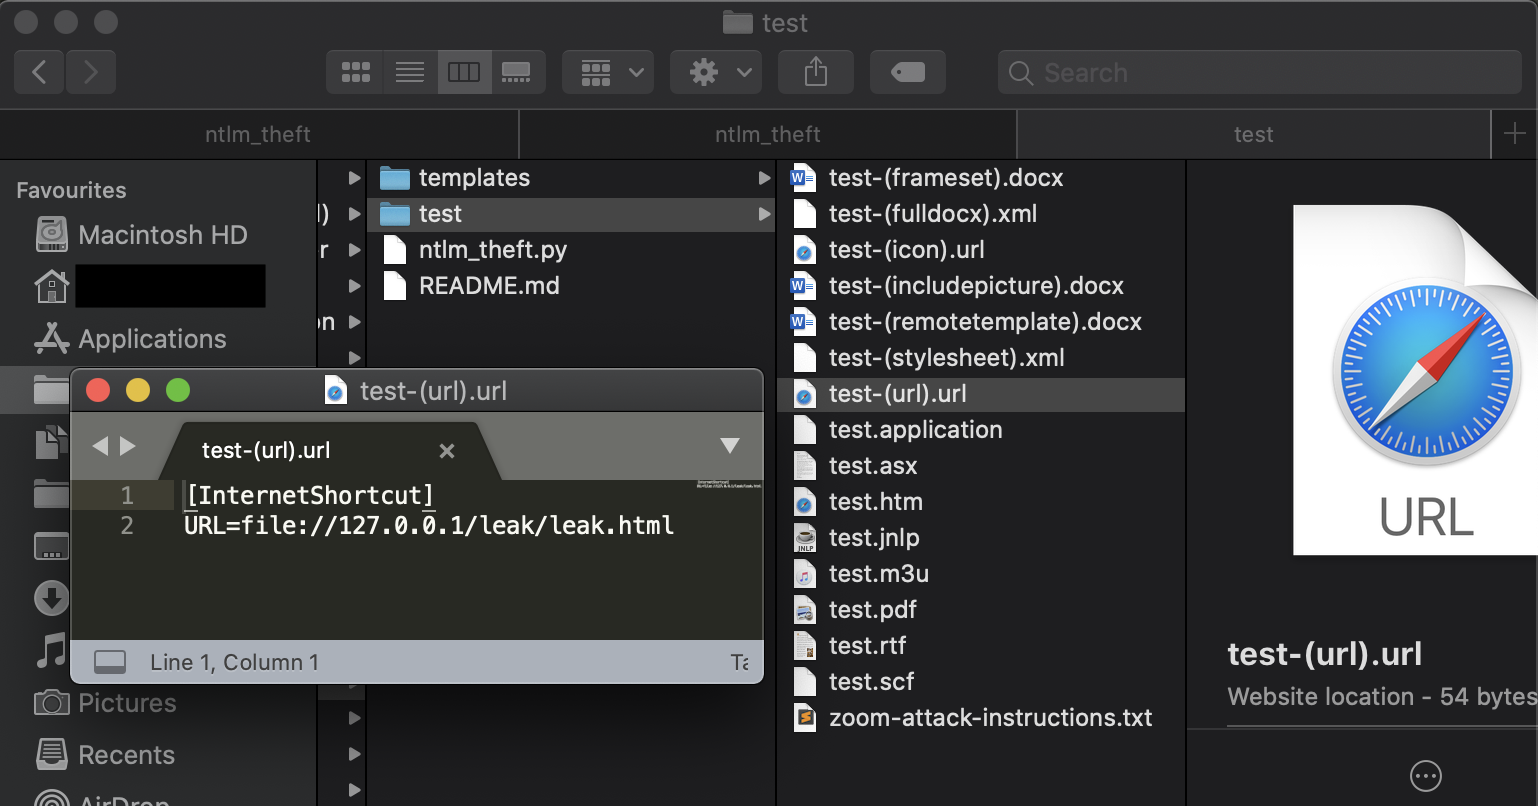
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)

Wavestone's web interface for password cracking with hashcat

An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords.

Python exploit script for CVE-2019-5420, targeting Ruby on Rails signed-session AES GCM key brute-forcing to achieve remote code execution in…

Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+…

Remotely test password strength of WordPress bloging software