
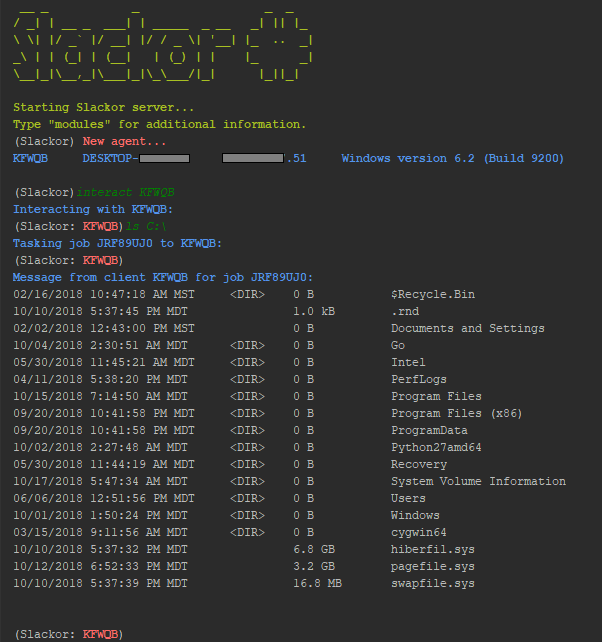
Slackor
 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
command-and-controllateral-movementpassword-attacks+8
4606 years ago
coalfire-research/slackorA Golang implant that uses Slack as a command and control server
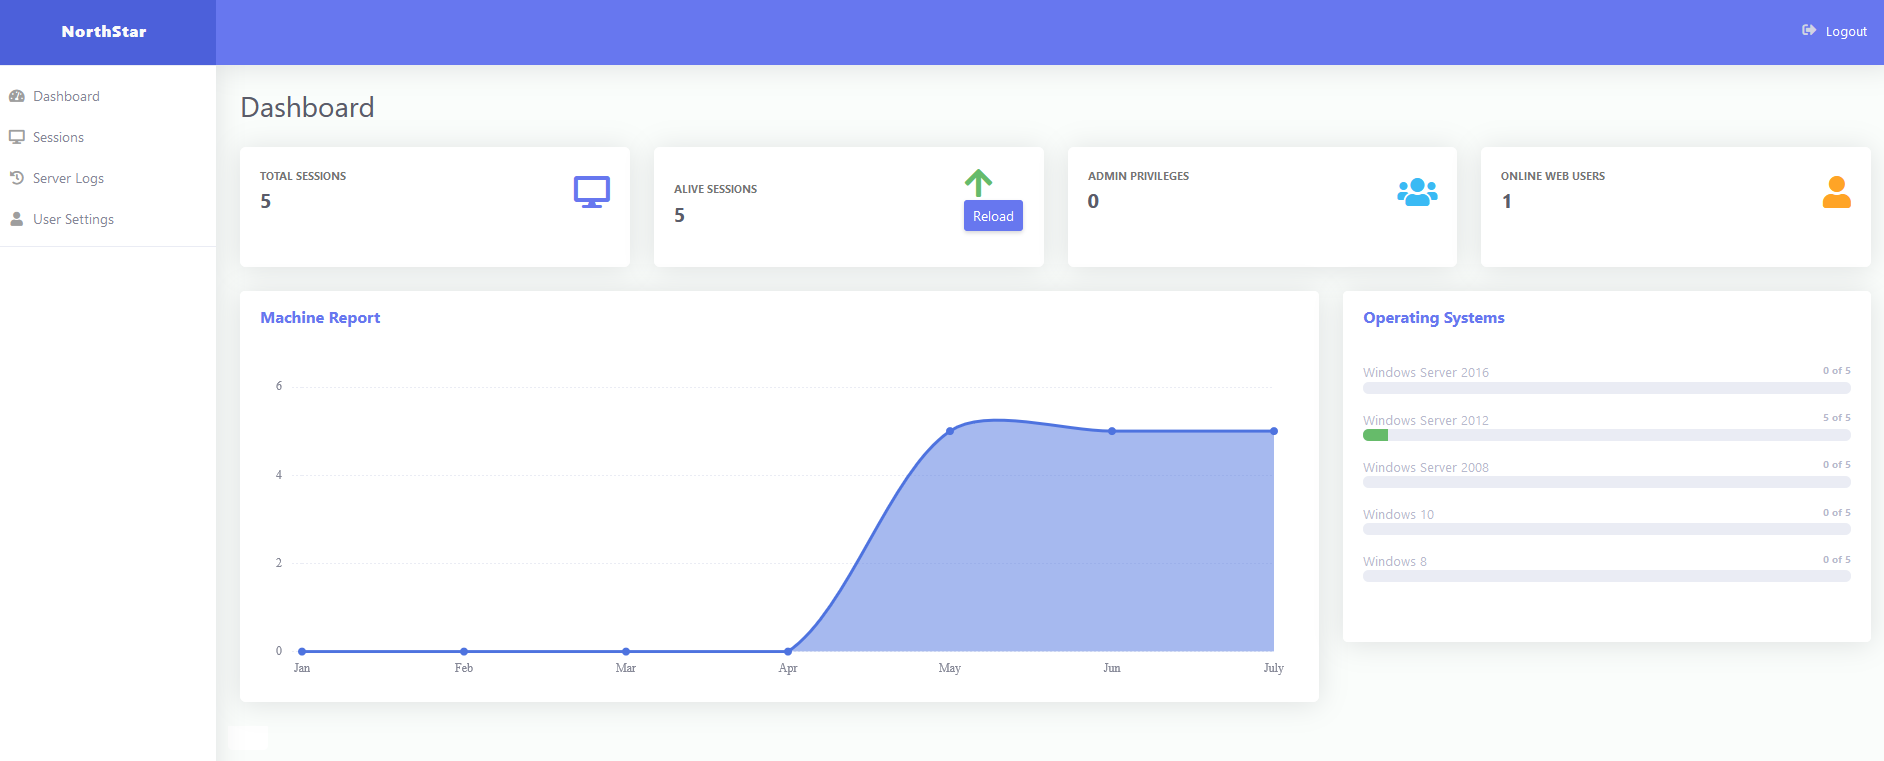 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 saykino/cve-2026-31282
Proof-of-concept for CVE-2026-31282: Totara LMS login page access control bypass enabling unauthenticated brute-force credential attacks. Includes…
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 rodolfomarianocy/xpl-modernwms-cve-2024-57698
It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…
 dearpan/cve-2018-9995
Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.
 sho-luv/zerologon
Zerologon Check and Exploit - Discovered by Tom Tervoort of Secura and expanded on @Dirkjanm's cve-2020-1472 coded example. This tool will check,…
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
 jonirinta-kahila/wpcracker
WordPress pentest tool
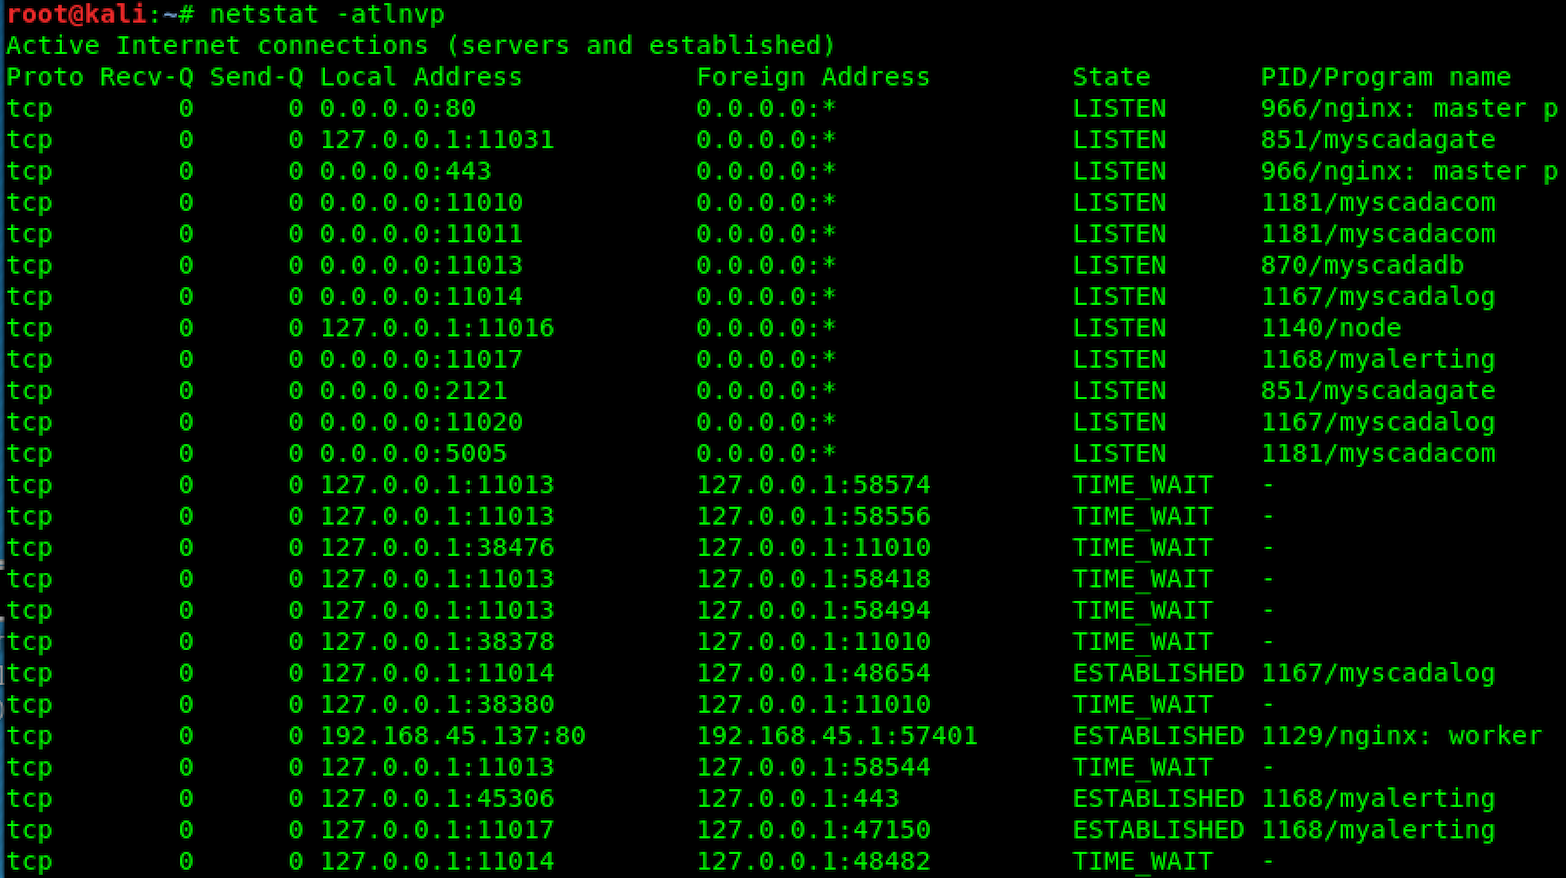 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 zeved/cve-2024-42049-poc
PoC for CVE-2024-42049
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…