
CVE-2025-49901
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
authentication-authorizationexploitationpassword-attacks+3
nxploited/cve-2025-49901WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 nxploited/cve-2025-3604
Flynax Bridge <= 2.2.0 - Unauthenticated Privilege Escalation via Account Takeover
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
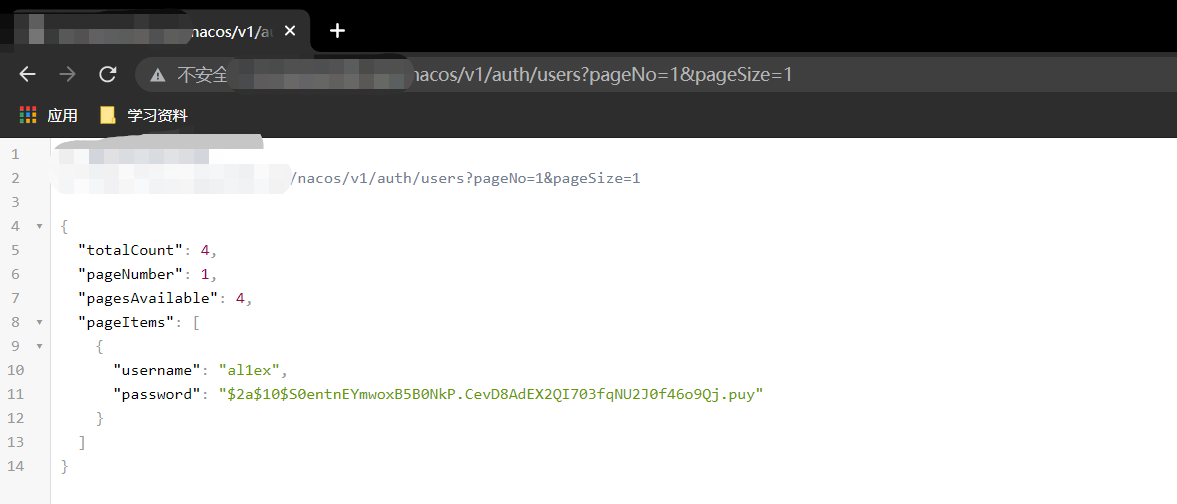 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD