ZerologonWithImpacket-CVE2020-1472

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…

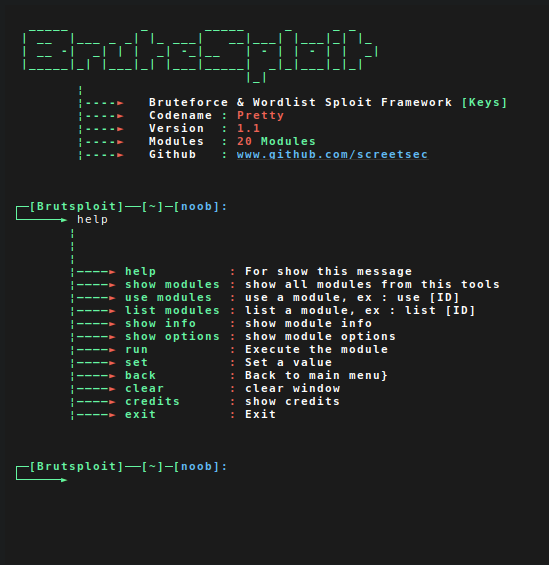
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…

TNC Toolbox: Web Performance <= 1.4.2 - Unauthenticated Sensitive Information Exposure to Privilege Escalation/cPanel Account Takeover

Mass Exploit Privileges Authentication (Subscriber to Administrator) - Wordpress Plugin ReviewX

CVE-2025-4322 – Unauthenticated Privilege Escalation via Password Update "Account Takeover" 🔥

This project offers a straightforward solution for retrieving forgotten PDF passwords using Google Colab. With just five simple steps, it efficiently…

HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…

This repository includes two PoC scripts for CVE-2025-57819 in FreePBX: one to create a new admin user (poc_admin.py), and another to extract…

HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…

Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.

Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

This repository contains a Python script to exploit two vulnerabilities: CVE-2019-18818 and CVE-2019-19609.

Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax

This is an exploit script to find out wordpress admin's username and password hash by exploiting CVE-2024-1698.

Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.