
CVE-2019-17240-Bludit-3.9.2-Auth-Bruteforce-Bypass
 mind2hex/cve-2019-17240-bludit-3.9.2-auth-bruteforce-bypass
Bludit 3.9.2 auth bruteforce bypass
authenticationexploitationpassword-attacks+2
mind2hex/cve-2019-17240-bludit-3.9.2-auth-bruteforce-bypassBludit 3.9.2 auth bruteforce bypass
 varandinawer/cve-2020-28874
CVE-2020-28874
 tiemio/ssh-key-and-rce-poc-for-cve-2021-41773
This repository contains a Proof-of-Concept for the CVE-2021-41773. This CVE contains a LFI and RCE vulnerablity.
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 njmbb8/cve-2024-42849
An issue in Silverpeas v.6.4.2 and lower allows a remote attacker to cause a denial of service via the password change function.
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 lucareggiannini/bludit-3-9-2-bb
Bludit 3.9.2 - bruteforce bypass - CVE-2019-17240
 pezwarinaan/cve-2014-0195
Exploit for CVE-2014-0195
 h3x0v3rl0rd/owa-password-sprayer
OWA Password Sprayer
 tieulong21prosper/detect_bruteforce
detect bruteforce using for cve-2021-34527
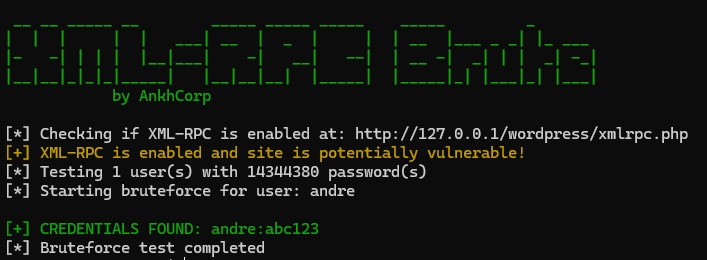 ankhcorp/xmlrpc-brute
This tool tests WordPress installations for XML-RPC authentication vulnerabilities.
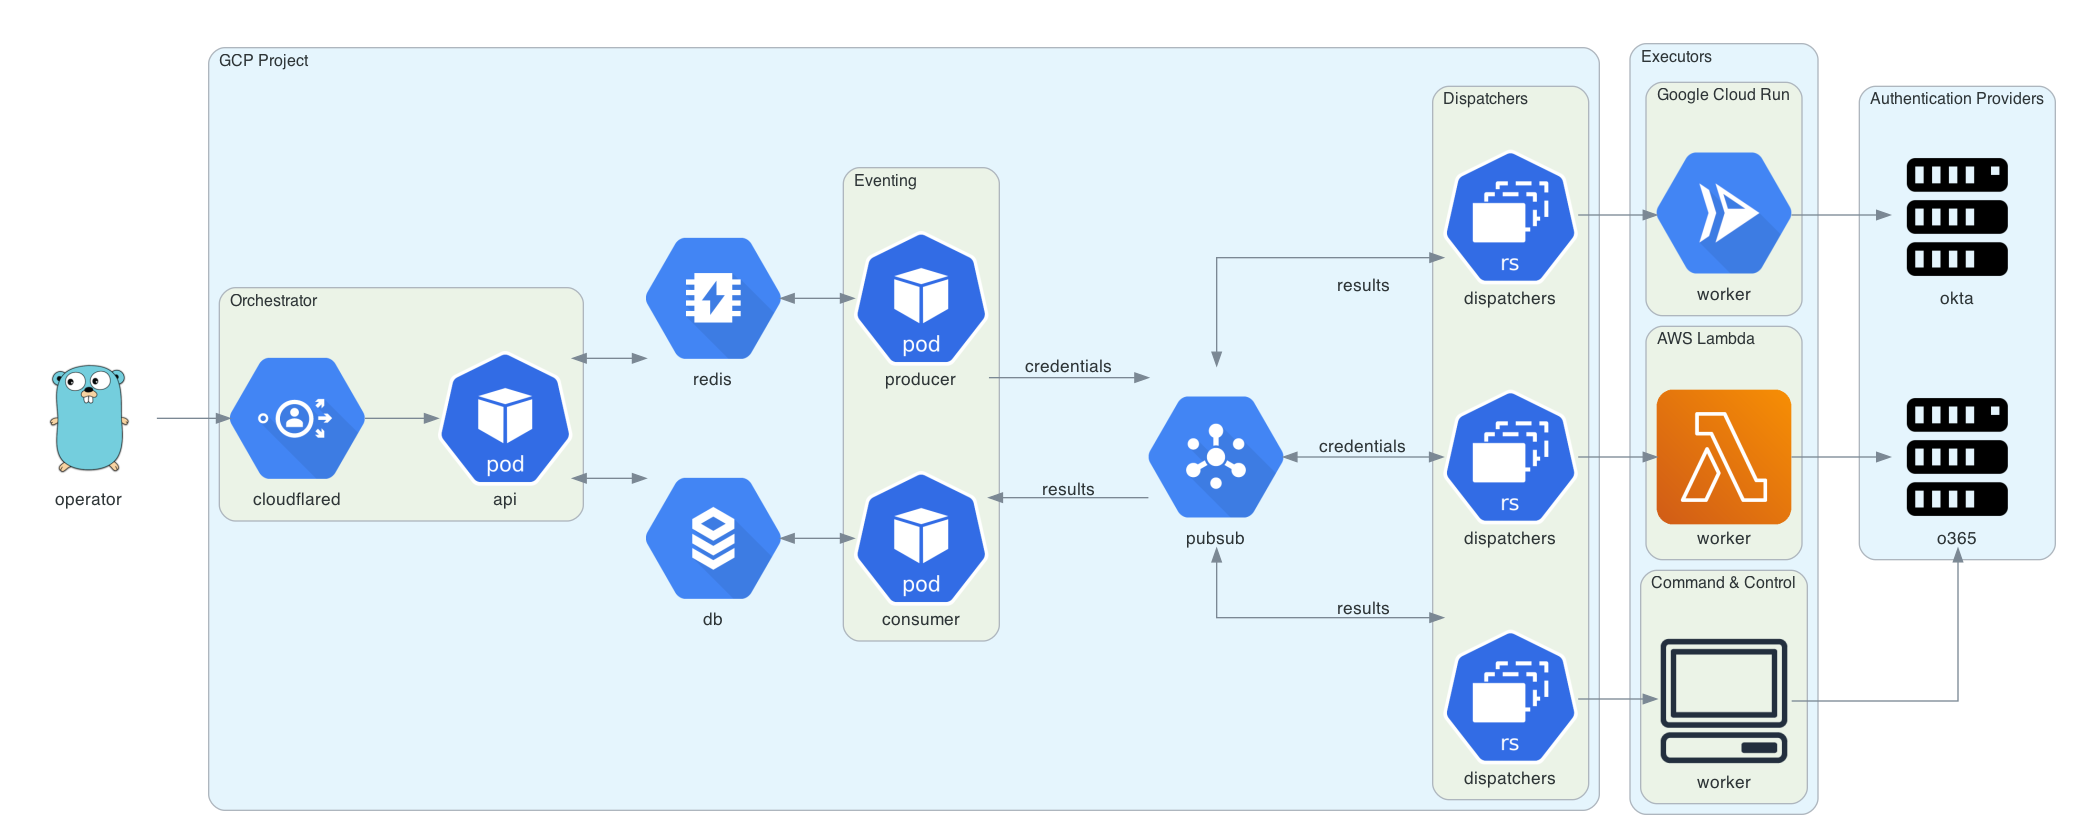 praetorian-inc/trident
automated password spraying tool
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…