
PXEThief
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
exploitationinformation-gatheringpassword-attacks+5
434
mwr-cybersec/pxethiefPXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 mrprogrammer2938/black-tool
Install the tools and start Attacking , black-tool v5.5.5 ! ⬛
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
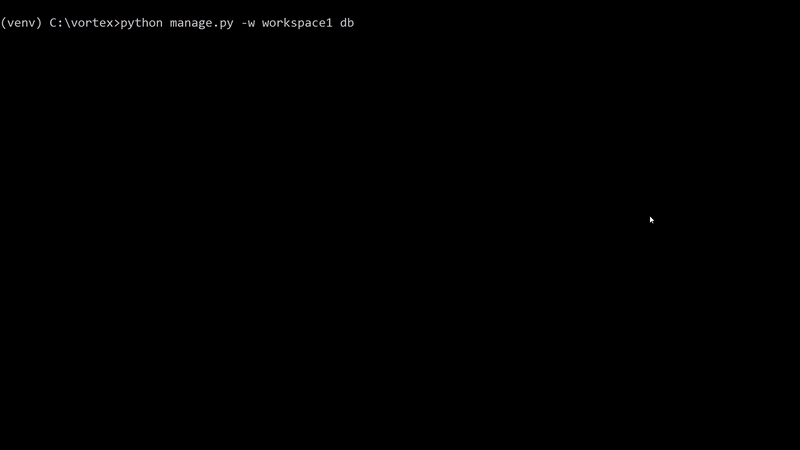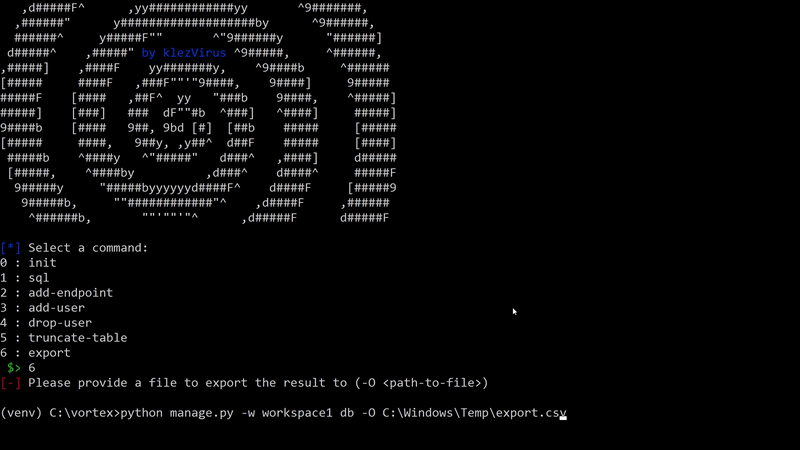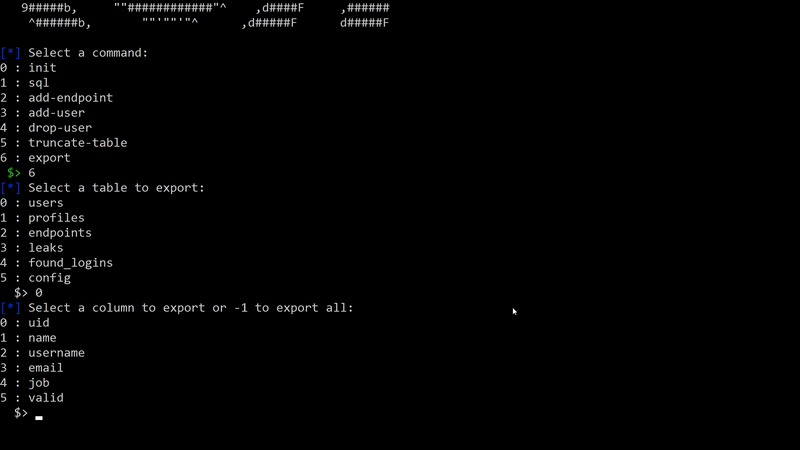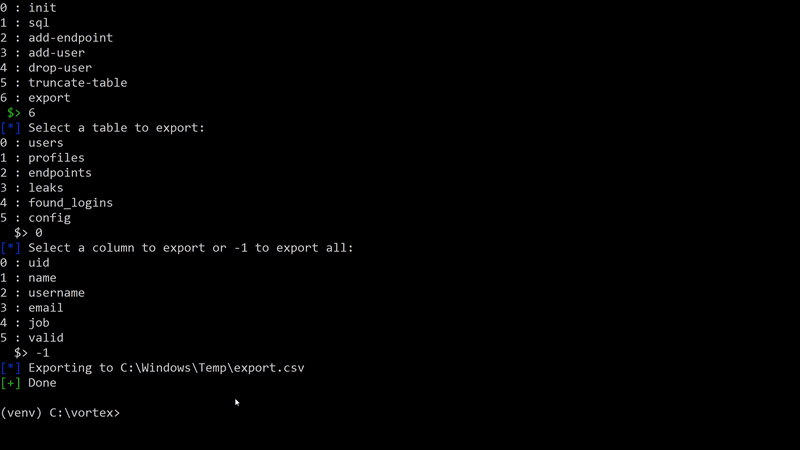 klezvirus/vortex
VPN Overall Reconnaissance, Testing, Enumeration and eXploitation Toolkit
 danmcinerney/pentest-machine
Automates some pentest jobs via nmap xml file
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 dievus/oh365userfinder
Enumerates valid Microsoft 365 accounts and domains via response analysis, with password spraying support and throttling detection to avoid lockouts.
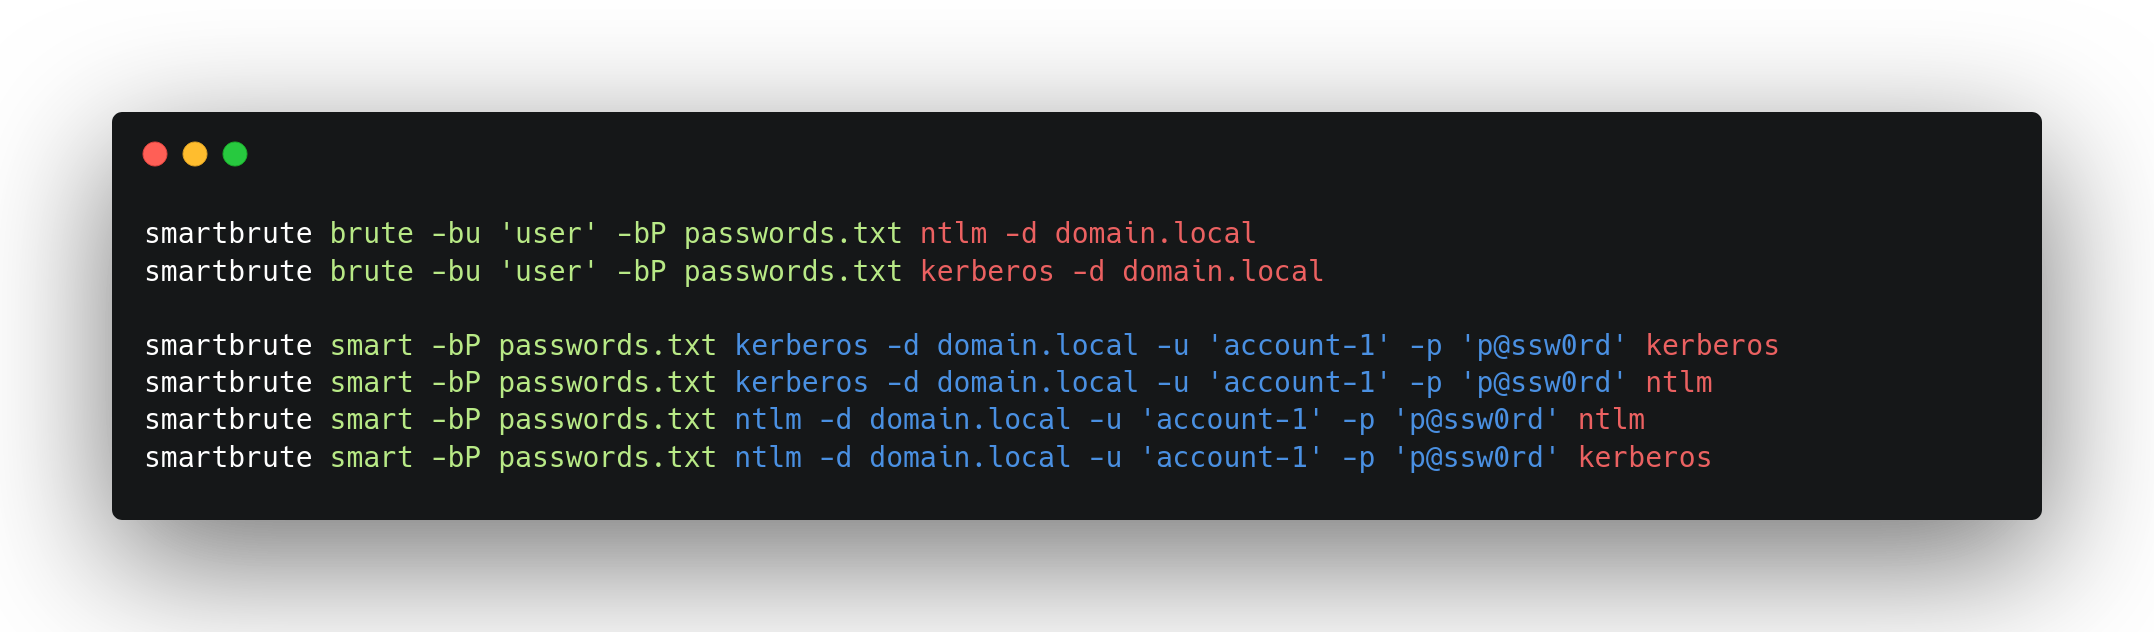 shutdownrepo/smartbrute
Password spraying and bruteforcing tool for Active Directory Domain Services
 jimywork/shodanwave
Shodanwave is a tool for exploring and obtaining information from Netwave IP Camera.
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
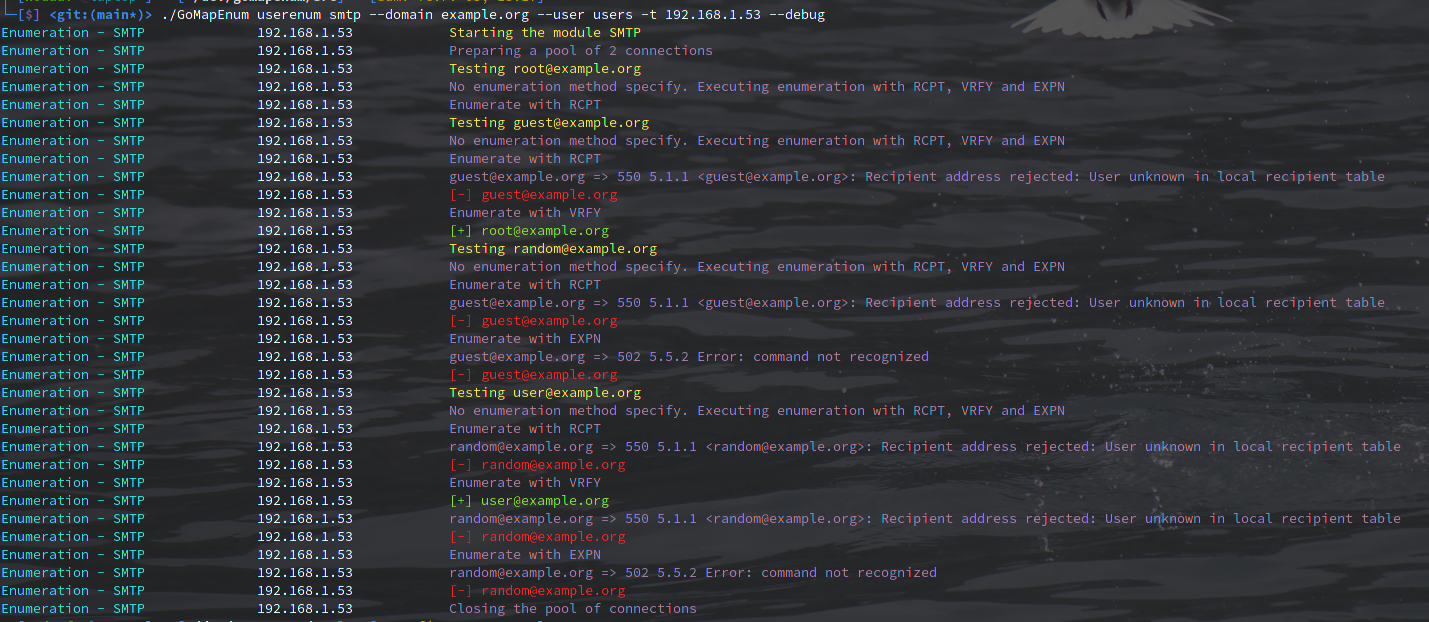 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
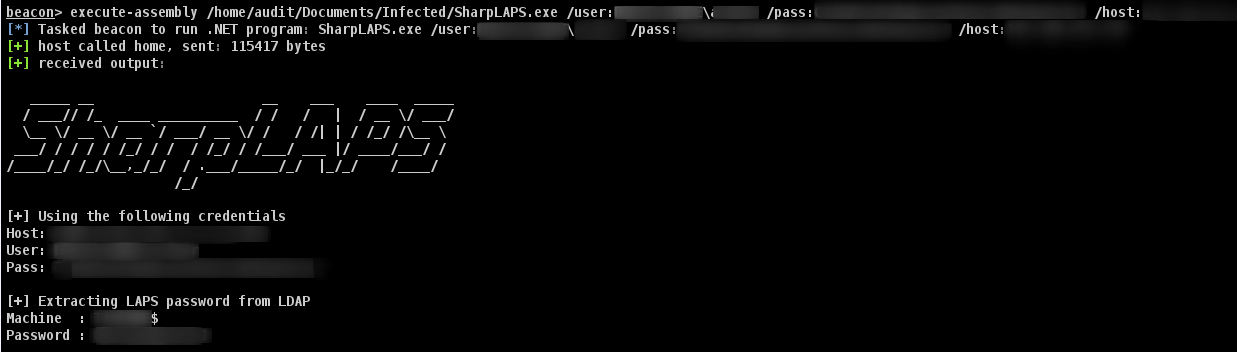 swisskyrepo/sharplaps
C# tool to retrieve LAPS passwords from Active Directory via LDAP, designed for in-memory execution within Cobalt Strike sessions using…
 philwantsfish/shard
A command line tool to detect shared passwords
 skelsec/kerberoast
Pure-Python toolkit for Kerberos-based attacks including ASREProast, SPNroast, and LDAP enumeration to identify and exploit vulnerable Active…
 danmcinerney/creds.py
Harvest FTP/POP/IMAP/HTTP/IRC creds
 rosesecurity/scrappy
Python utility that scrapes PDFs to generate targeted wordlists for brute force, forced browsing, and dictionary attacks, with word frequency,…
 trustedsec/ridenum
Rid_enum is a null session RID cycle attack for brute forcing domain controllers.
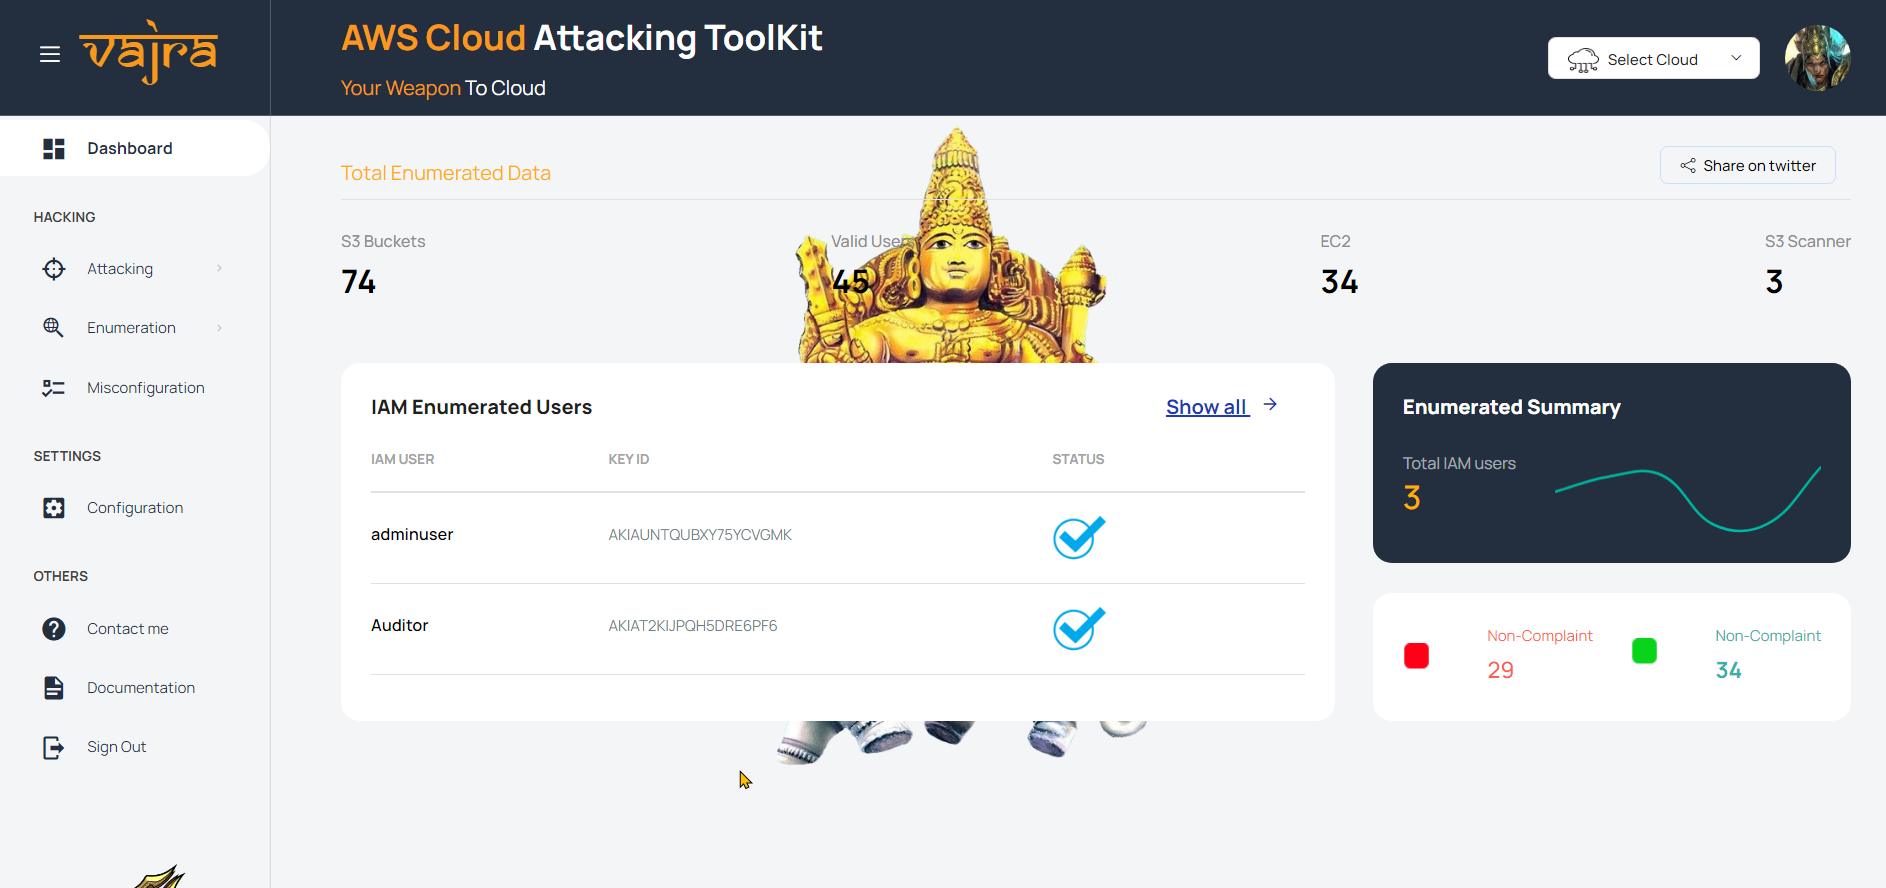 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…