xpl-ModernWMS-CVE-2024-57698

It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…

It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…

Strapi Framework, 3.0.0-beta.17.4

Telnet default credentials can lead to information disclosure and denial-of-service (DoS) attacks.

Bludit 3.9.2 - bruteforce bypass - CVE-2019-17240

Possible Account Takeover | Brute Force Ability

CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS

Decrypts Hikvision IP camera configuration files extracted via CVE-2017-7921 authentication bypass, revealing user credentials and device settings.

Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…

lame old keylogger

Targets versions ≤2.7.5 vulnerable to CVE-2023-5359

FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631

Project with sublist3r, massan, CVE-2018-15473, ssh bruteforce, ftp bruteforce and nikto.

DEPRECATED, bettercap developement moved here: https://github.com/bettercap/bettercap

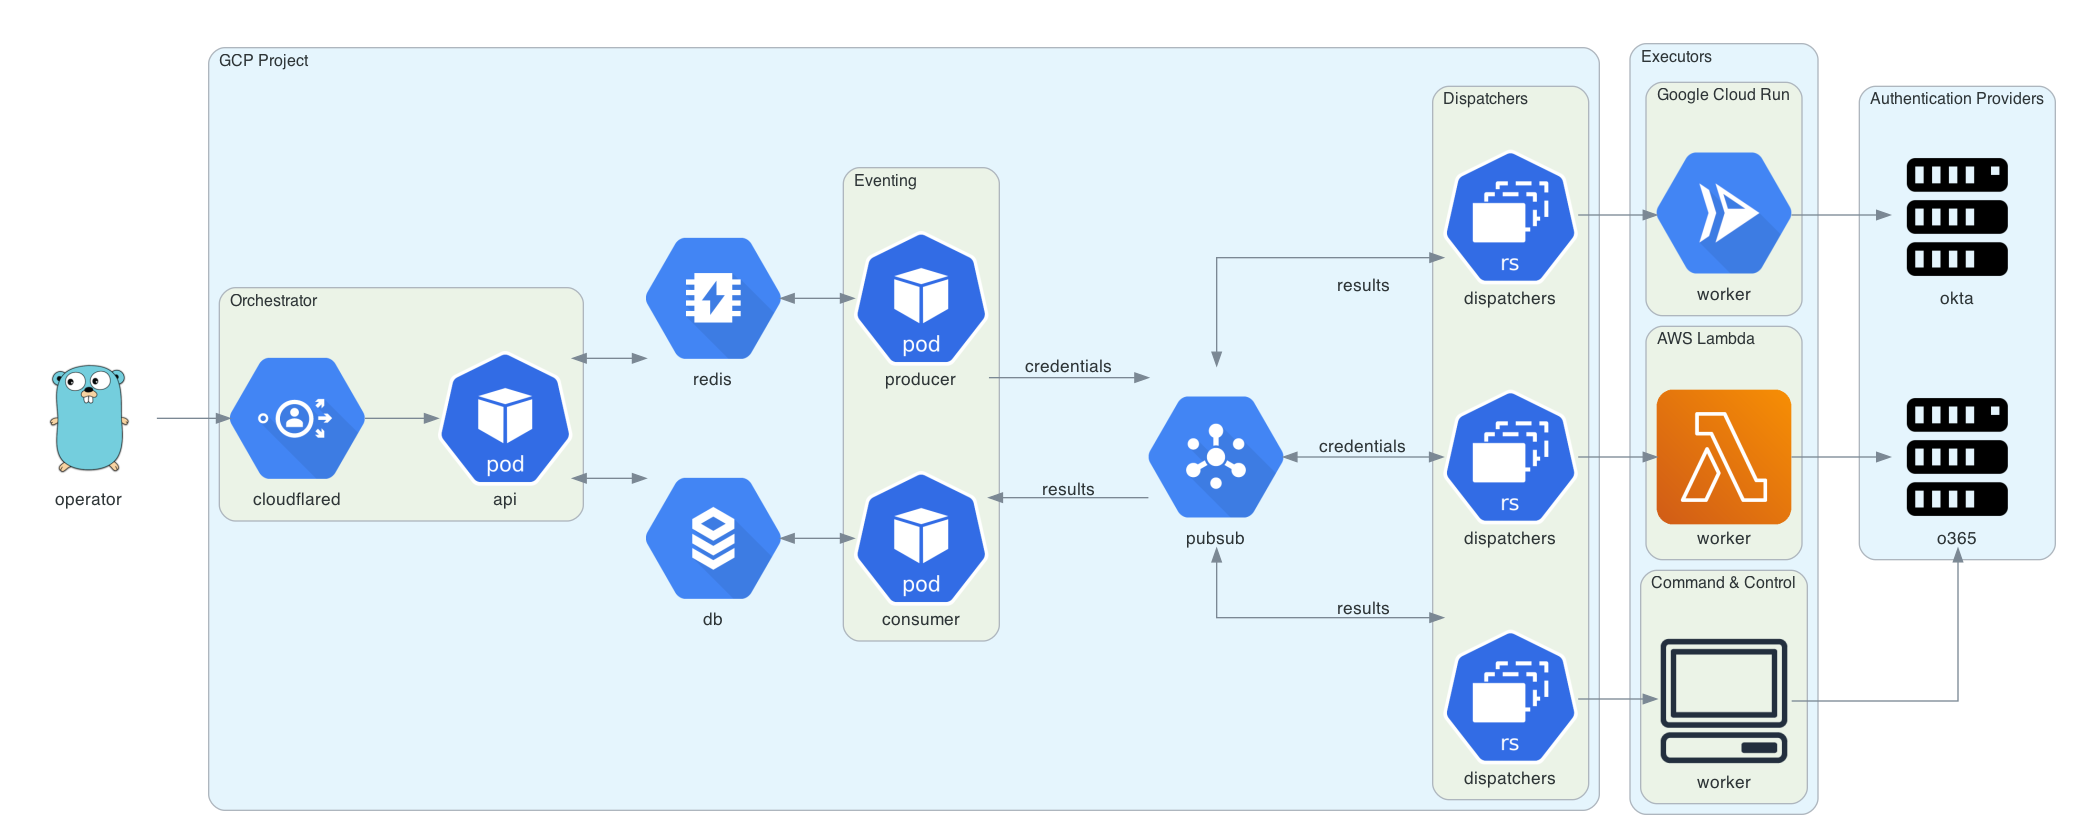
automated password spraying tool

Scripts to make password spraying attacks against Lync/S4B, OWA & O365 a lot quicker, less painful and more efficient

Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…

WPScan rewritten in Python + some WPSeku ideas