
CVE-2019-16113
 m4rm0k/cve-2019-16113
Bludit 3.9.2 - Remote command execution - CVE-2019-16113
exploitationpassword-attacksremote-access-tool+2
m4rm0k/cve-2019-16113Bludit 3.9.2 - Remote command execution - CVE-2019-16113
 yucaerin/cve-2025-4606
Sala - Startup & SaaS WordPress Theme <= 1.1.4 - Unauthenticated Privilege Escalation via Password Reset/Account Takeover
 kiphuong/cve-2016-6210
PoC of cve-2016-6210
 mauricelambert/gpp-encrypt
This little script encrypts password to gpp cpassword. It useful to create vulnerable lab AD (CVE-2014-1812).
 0xfml/cve-2023-30765
CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation
 sadshade/detrix-passwords-poc
Скрипт для расшифровки пароля пользователя в СЭД Detrix
 randomrobbiebf/wordpress-bf
Brute Force Wordpress Blogs.
 jra89/cve-2019-19633
lib/G/functions.php in Chevereto 1.0.0 through 1.1.4 Free, and through 3.13.5 Core, allows an attacker to perform bruteforce attacks without…
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 shadow-spinner/cve-2022-0847
exploit of CVE-2022-0847 which directly remove password of the root account
 gabrielavls/cve-2017-7921
CVE-2017-7921 exploit. Allows admin password retrieval and automatic snapshot download.
 mind2hex/cve-2019-17240-bludit-3.9.2-auth-bruteforce-bypass
Bludit 3.9.2 auth bruteforce bypass
 simonlee-hello/cve-2020-25540
ThinkAdmin v5 v6 任意文件读取漏洞利用,可自定义字典爆破
 hau-zy/keepass-dump-py
Re-write of original KeePass 2.X Master Password Dumper (CVE-2023-32784) POC in python.
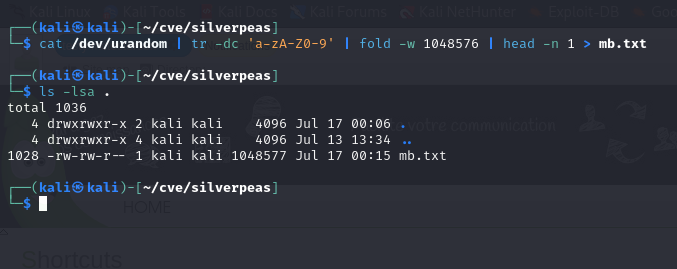 njmbb8/cve-2024-42849
An issue in Silverpeas v.6.4.2 and lower allows a remote attacker to cause a denial of service via the password change function.
 varandinawer/cve-2020-28874
CVE-2020-28874
 maen08/cve-2024-25277
Resources and PoCs
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341