
CVE-2026-8181
 xshadow-here/cve-2026-8181
CVE-2026-8181 | Burst Statistics 3.4.0 - 3.4.1.1 - Authentication Bypass to Admin Account Takeover
authenticationexploitationinformation-gathering+6
1
xshadow-here/cve-2026-8181CVE-2026-8181 | Burst Statistics 3.4.0 - 3.4.1.1 - Authentication Bypass to Admin Account Takeover
 0xdtc/bludit-3.9.2-auth-bruteforce-bypass-cve-2019-17240
Bludit 3.9.2 - Auth Bruteforce Bypass CVE:2019-17240 Refurbish In bash
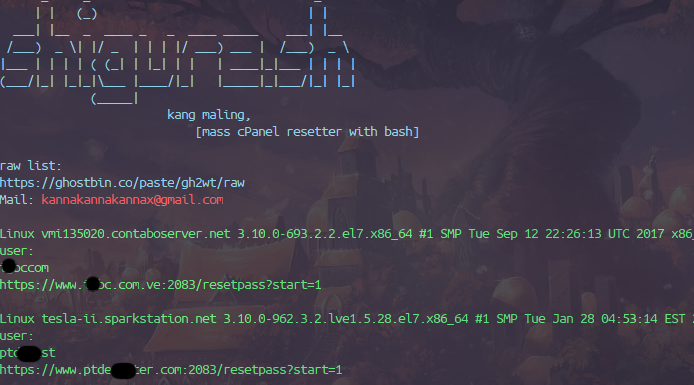 redsplit/shiguresh
CVE-2004-1769 // Mass cPanel Reset password
 npocmak/cve-2020-1472
https://github.com/dirkjanm/CVE-2020-1472
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 zwlsix/keepass-cve-2023-24055
KeePass CVE-2023-24055复现
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 haingn/hik-cve-2021-36260-exploit
Go-based brute-force exploit tool targeting Hikvision cameras vulnerable to CVE-2021-36260, with multi-threaded scanning and configurable…
 funoverip/mcafee_atd_cve-2019-3663
McAfee Advanced Threat Defense ATD 4.6.x and earlier - Hardcoded root password
 daeda1usuk/cve-2025-59390-
CVE-2025-59390 and ThreadLocalRandom Inverse
 starawneh/cve-2025-4094
CVE-2025-4094 – WordPress Digits Plugin < 8.4.6.1 - OTP Authentication Bypass
 jenderal92/owa-valid-login-checker
Owa Valid Login Checker
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 moften/cve-2025-24054
Vulnerabilidad NTLM (CVE-2025-24054) explotada para robo de hashes
 ssssuperx/cve-2024-28000
CVE-2024-28000 LiteSpeed Cache Privilege Escalation Scan&Exp
 huzaifahussain98/cve-2019-17525
D-LINK ROUTER "MODEL NO: DIR-615" with "FIRMWARE VERSION:20.10" & "HARDWARE VERSION:T1
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…