xpl-ModernWMS-CVE-2024-57698

It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…

It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…

Modifed ver of the original exploit to save some times on password reseting for unprivileged user

Proof-of-concept for CVE-2023-0860, demonstrating unauthenticated brute-force login attacks on Modoboa Mail Hosting and Management before v2.0.3.

8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting

Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…

Mini-paper on CVE-2017-2751, HP EFI password extraction.

Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…

Password cracking rules for Hashcat based on statistics and industry patterns

Pentest Tool to generate usernames/logins based on supplied names.

HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…

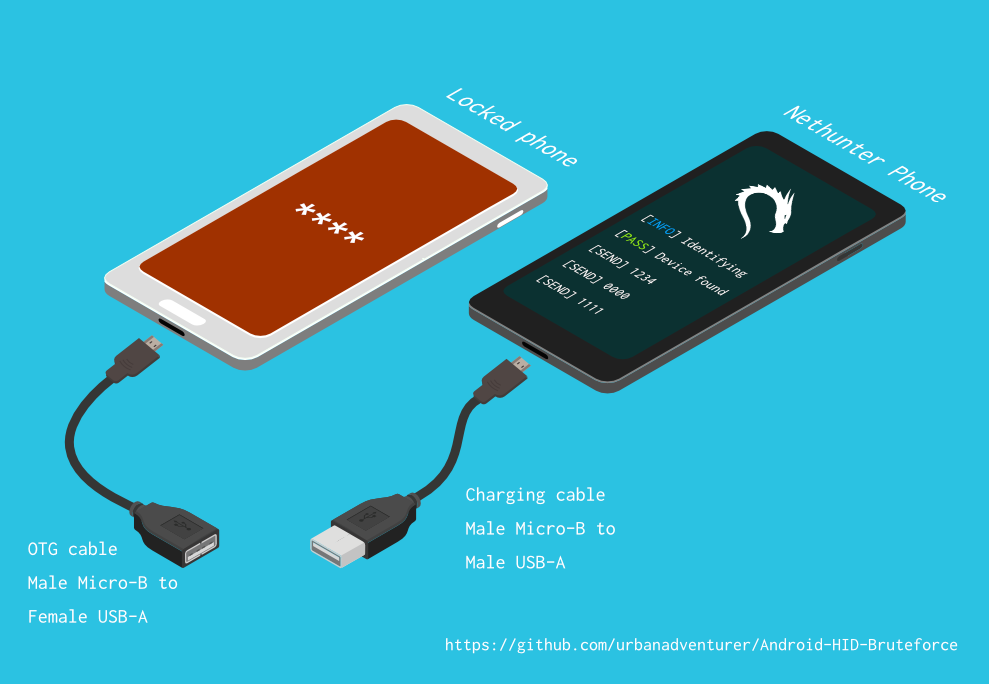
Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android…

Exploit for zerologon cve-2020-1472

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

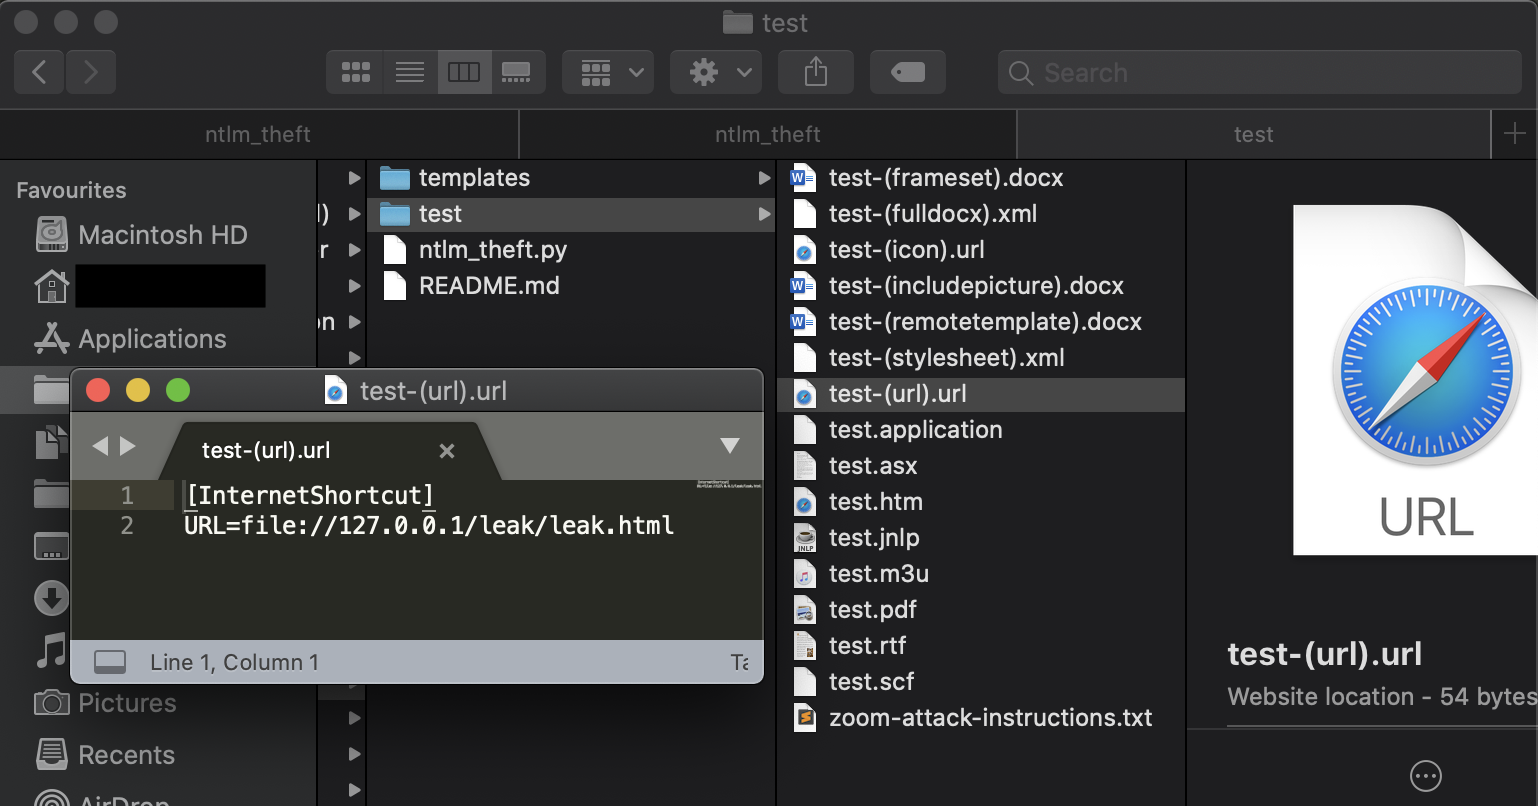
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)

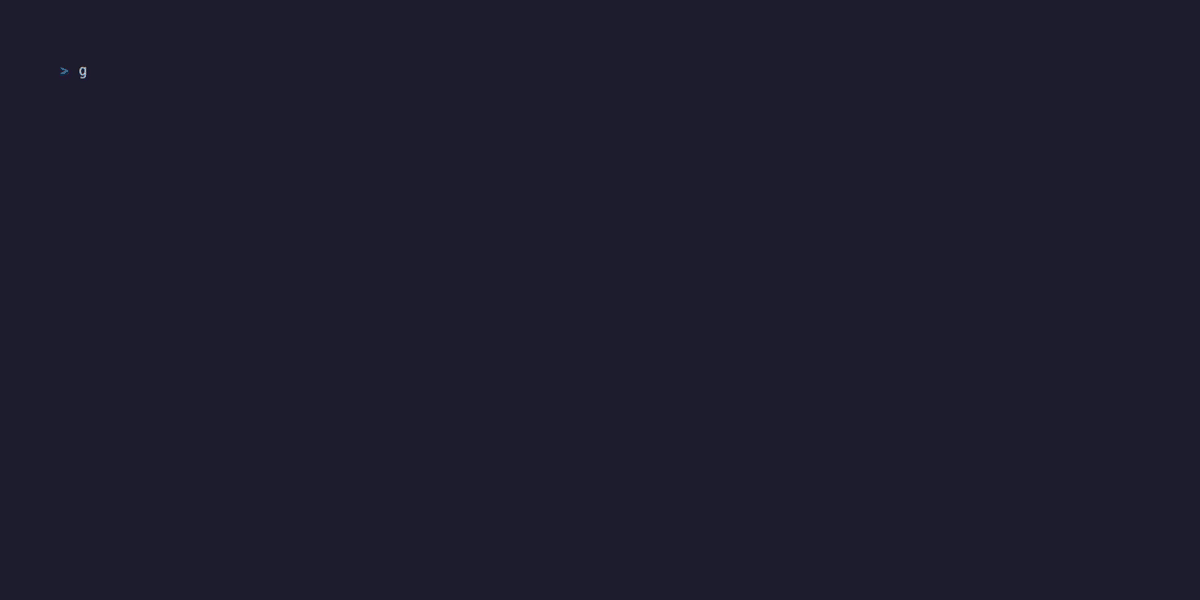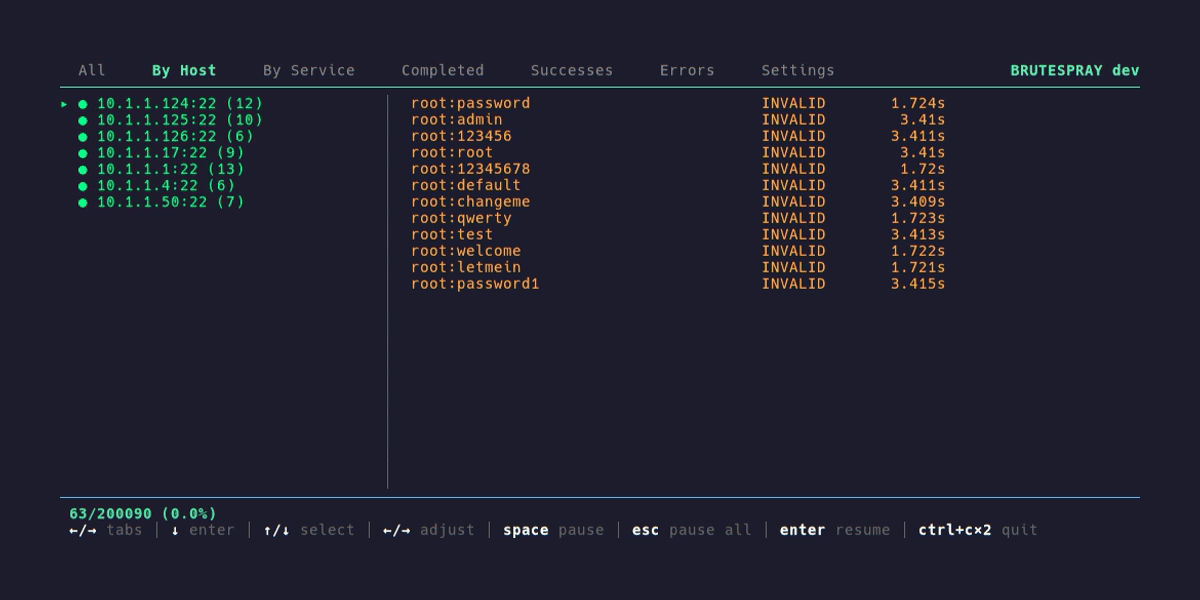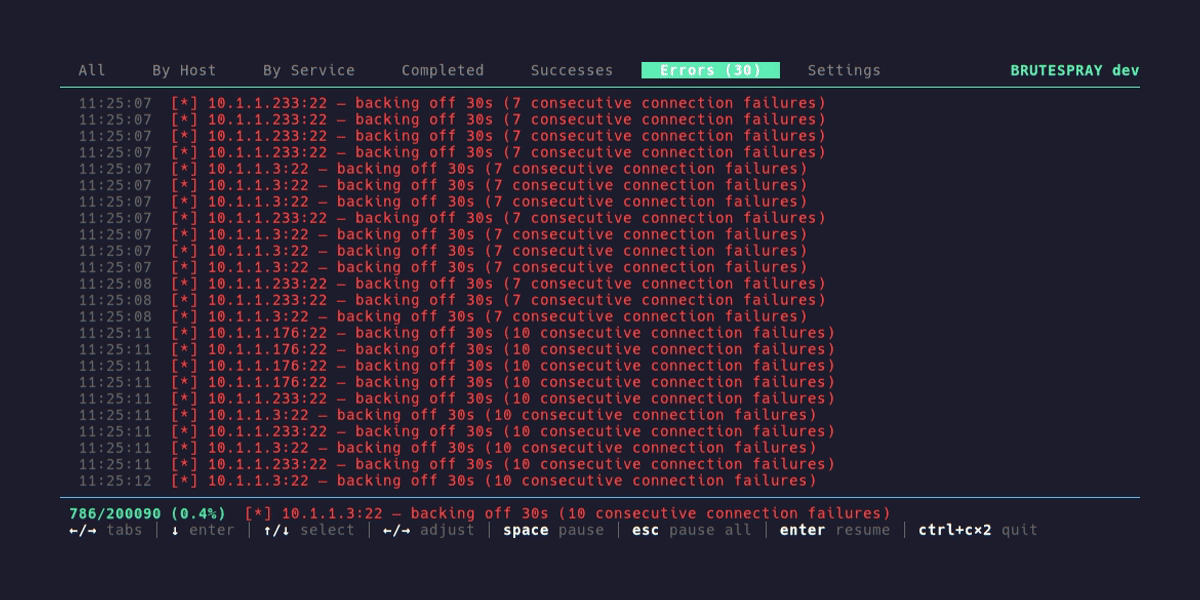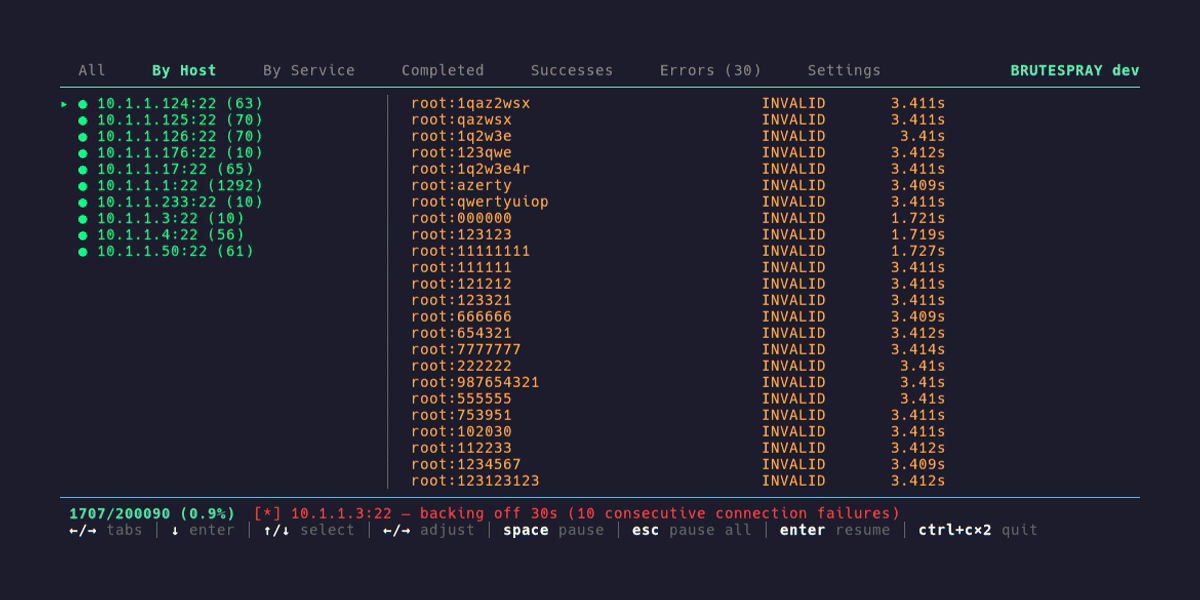
Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+…


HT-WPS Breaker (High Touch WPS Breaker)

A framework for constructing self-spreading binaries