
CVE-2022-0847
 shadow-spinner/cve-2022-0847
exploit of CVE-2022-0847 which directly remove password of the root account
binary-exploitationexploitationpassword-attacks+2
shadow-spinner/cve-2022-0847exploit of CVE-2022-0847 which directly remove password of the root account
 tiemio/ssh-key-and-rce-poc-for-cve-2021-41773
This repository contains a Proof-of-Concept for the CVE-2021-41773. This CVE contains a LFI and RCE vulnerablity.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 zvckster/cve-2025-63353
Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…
 am0nt31r0/password-analysis
Script in Go that analyzes a list of passwords based on in its entropy and weak passwords from a dictionary. Useful for penetration tests and…
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 someshkar/colabcat
:smiley_cat: Running Hashcat on Google Colab with session backup and restore.
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
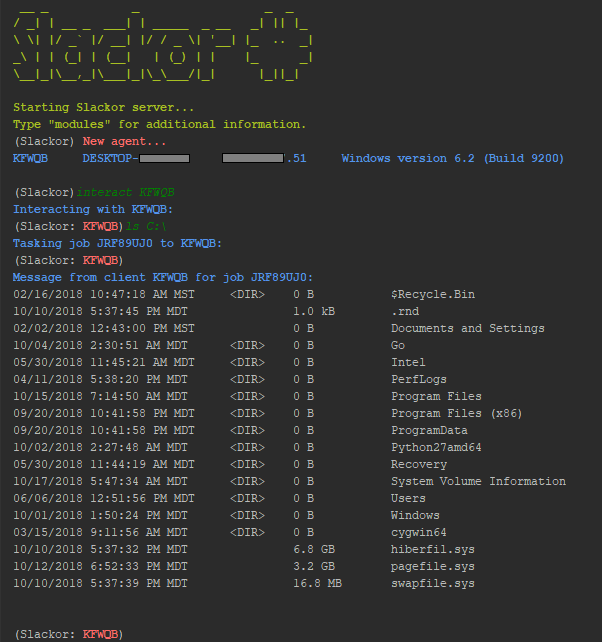 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 batchmcnulty/uberscan
Security program for recovering passwords and pen-testing servers, routers and IoT devices using brute-force password attacks.
 hook-s3c/cve-2018-18852
Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…
 androvirus/blacknet
Free advanced and modern Windows botnet with a nice and secure PHP panel developed using VB.NET.
 syedshehzadgillani/adminsnatcher
Let's Snatch The Admin Panel Of Any Website In Seconds.
 andripwn/cve-2018-18852
CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.
 mythicagents/xenon
A Mythic agent for Windows written in C