
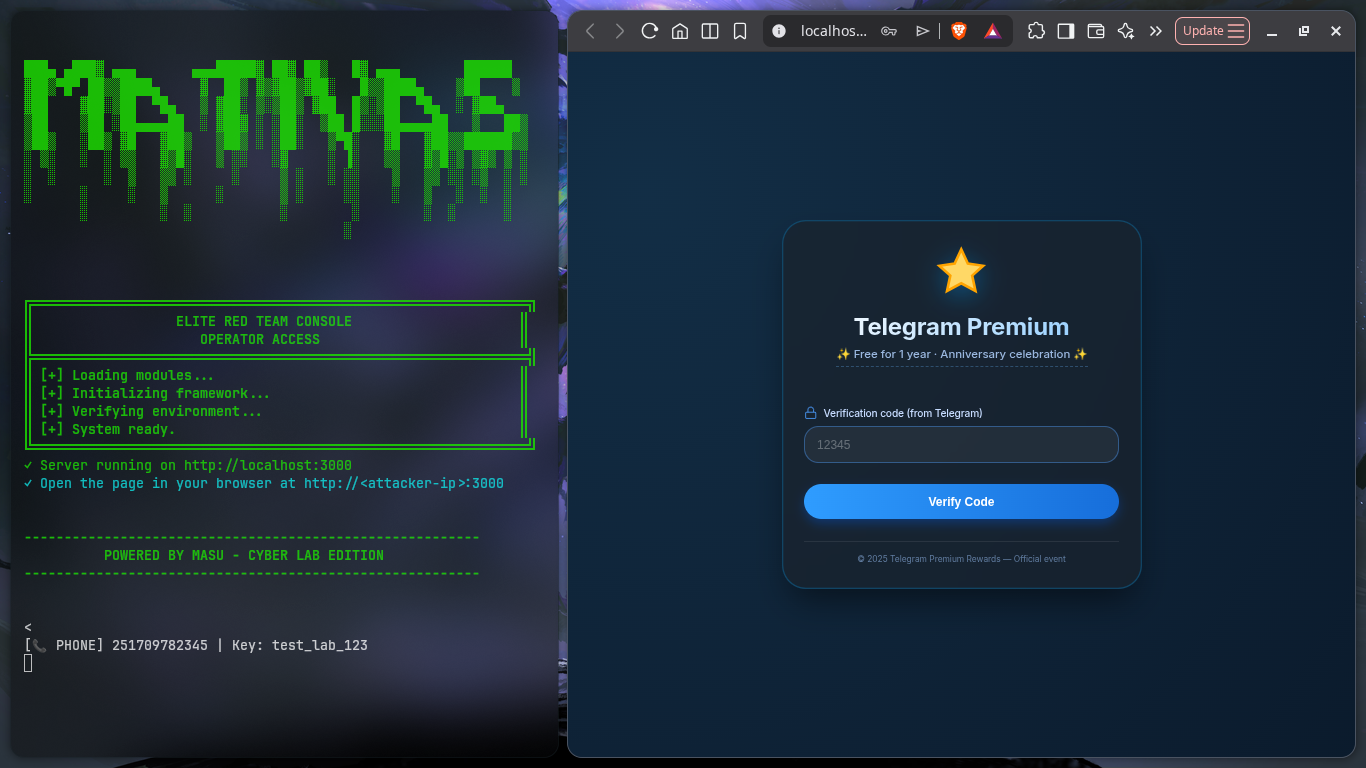
telegram-phish-simulator
 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
educationinformation-gatheringlabs-practice+6
2
maty156/telegram-phish-simulatorEducational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 r3fr4kt/codify-tjnull-oscp-
Walkthrough for Codify (Linux - Easy). Exploits vm2 RCE (CVE-2023-30547), SQLite DB hash extraction, Bcrypt cracking with John, and Privilege…

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
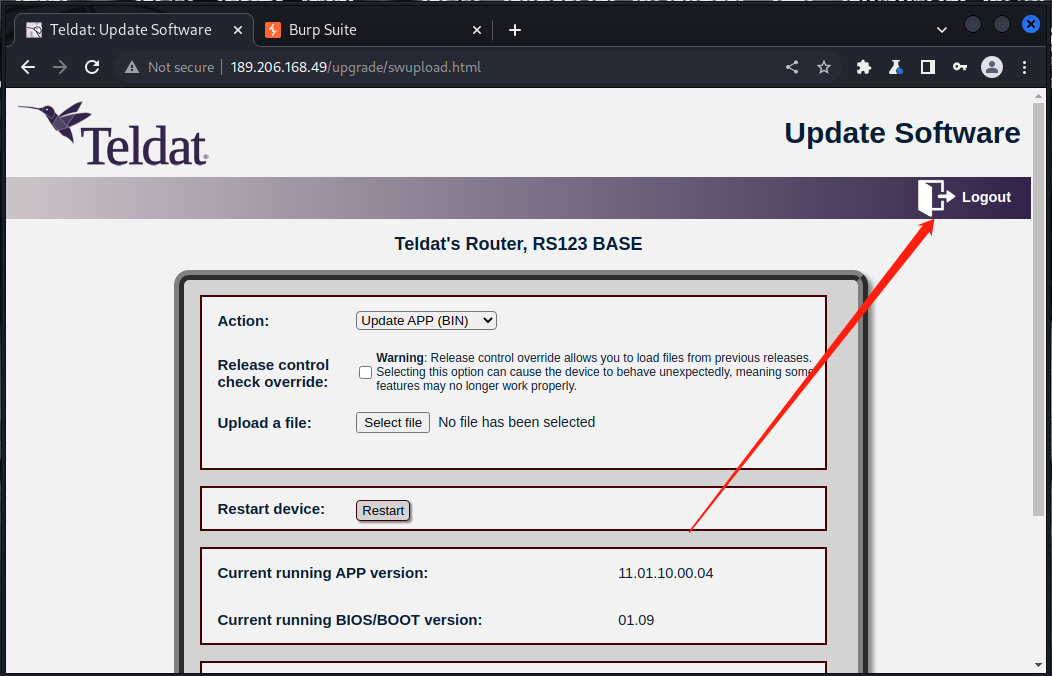 uyhacked/teldat-router-cve-2022-poc
POC for CVE-2022-39996 (Reflected XSS) and CVE-2022-39997 (Weak Password) in Teldat RS123/RS123w Router
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.
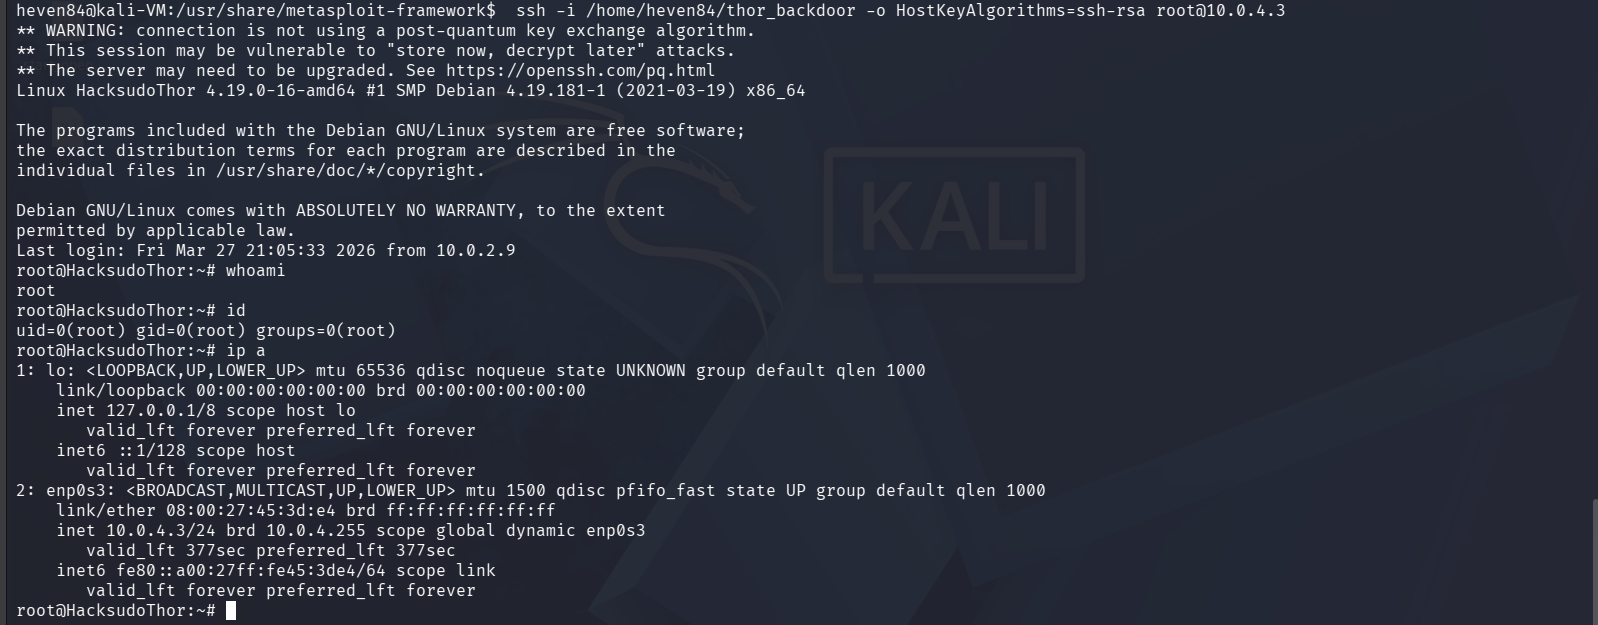 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 fernandobortotti/cve-2024-24919
Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…
 anonymous121029034720384234234/py-network-scanner
Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…
 enzocipher/cve-2023-5359
CVE-2023-5359 scanner for W3 Total Cache cleartext storage vulnerability. Detects exposed credentials (API keys, OAuth tokens) in publicly accessible…
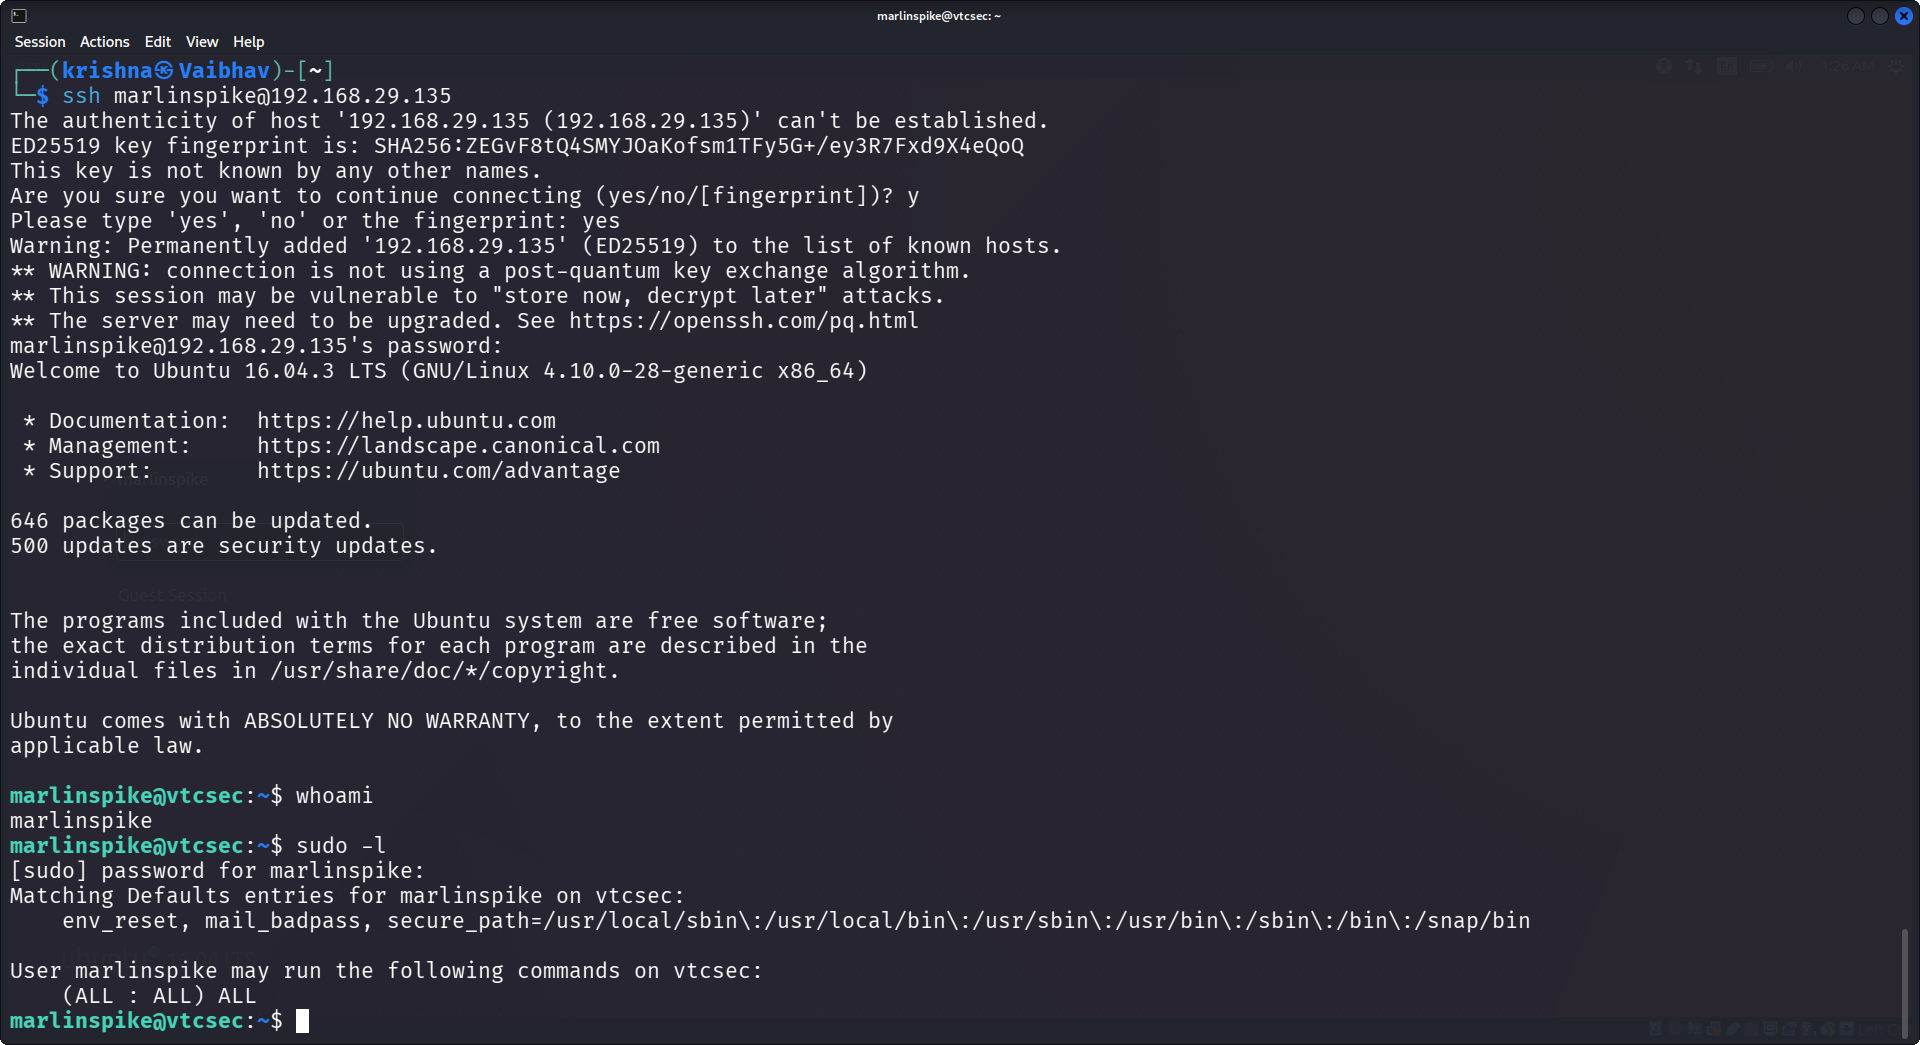 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 talha3117/openssh-4.7p1-cve-2008-5161-exploit
CVE-2008-5161 OpenSSH 4.7p1 Audit Helper Automates version checking and credential auditing of legacy OpenSSH 4.7p1 (Debian-8ubuntu1) targets by…
 dennisec/cve-2025-3102
Exploit script for CVE-2025-3102 targeting SureTriggers WordPress plugin (≤ v1.0.78). Detects vulnerable versions, exploits via REST API, and creates…
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 cmadhushanka/cve-2023-32784-exploitation
year 2 semester 1 Systems and Network Programming Assignment
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers