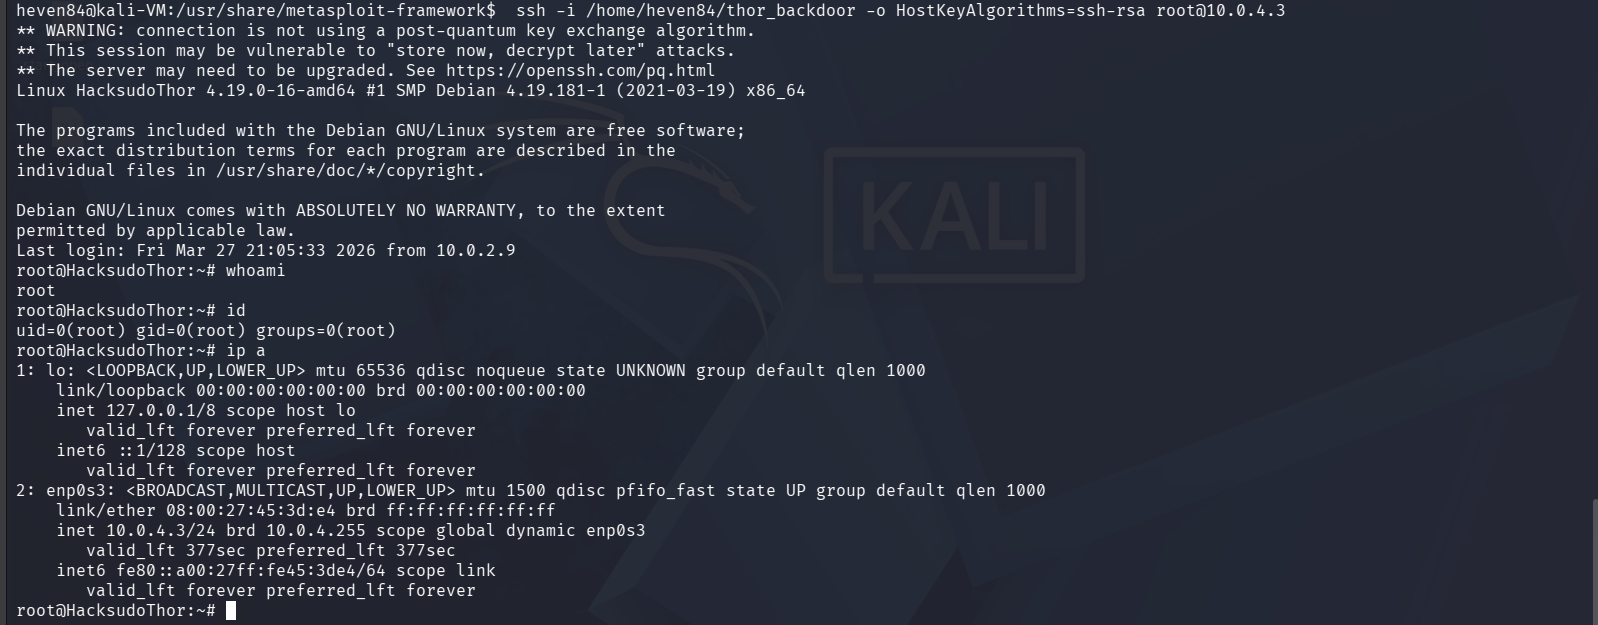
Penetration-Testing-Walkthrough-Hacksudo-Thor

Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…

Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…

Malicious shortcut generator for collecting NTLM hashes from insecure file shares.

An XMLRPC brute forcer targeting Wordpress written in Python 3. (DISCONTINUED)

Know the dangers of credential reuse attacks.


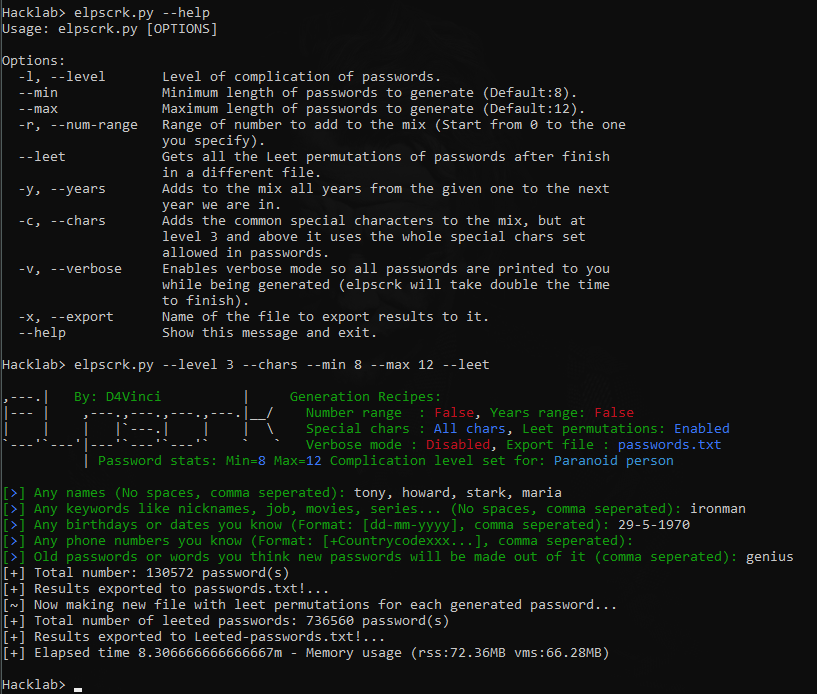
An Intelligent wordlist generator based on user profiling, permutations, and statistics. (Named after the same tool in Mr.Robot series S01E01)

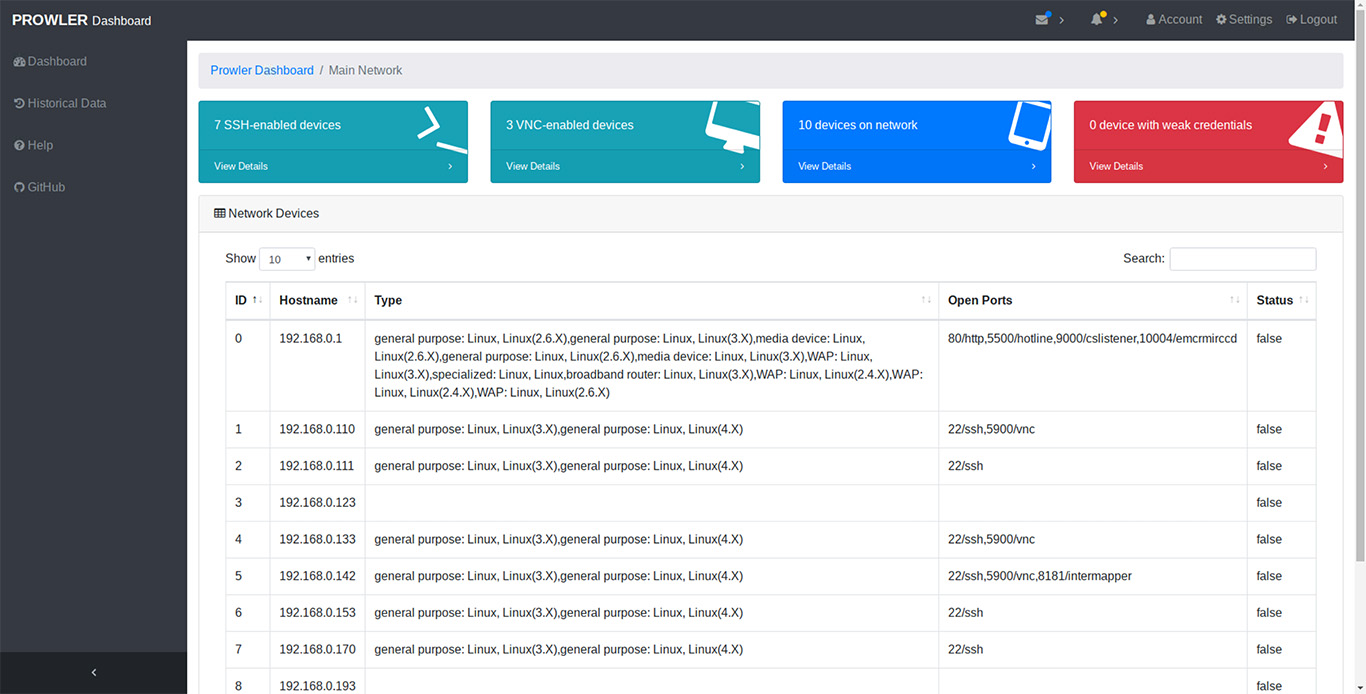
Distributed Network Vulnerability Scanner

Tool to spray AWS Console IAM Logins

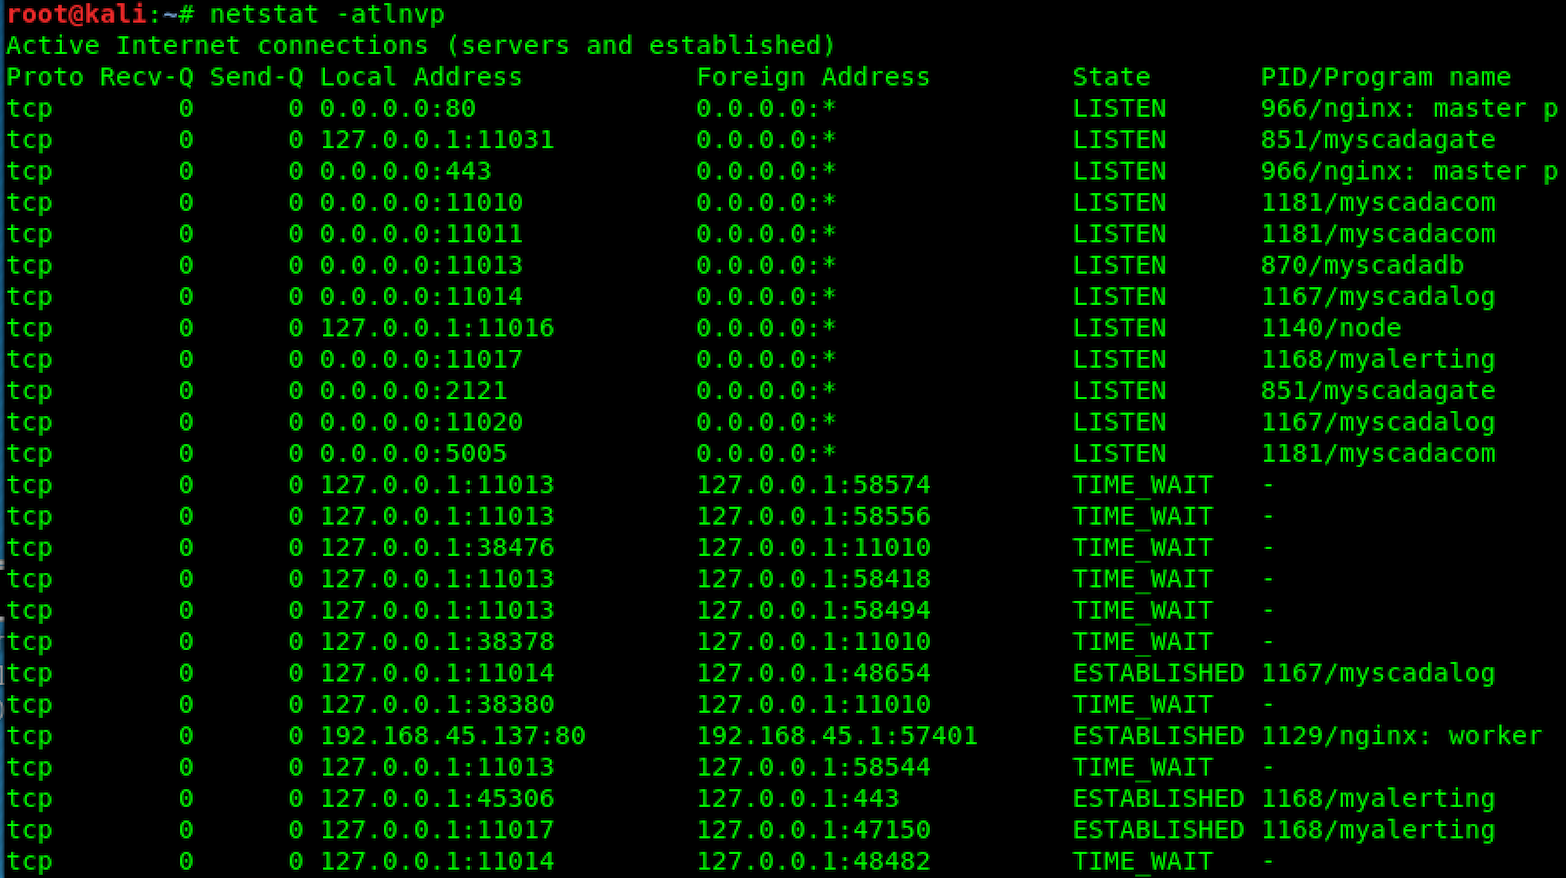
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…

Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

ZipRarHunter is a powerful command-line ethical hacking tool designed to crack passwords of ZIP and RAR archive files using a wordlist.

FTPBuster is a powerful command-line brute-forcing tool designed to brute-force FTP, SFTP, and explicit FTPS servers by performing dictionary-based…