mySCADA-myPRO-7-Hardcoded-FTP-Username-and-Password

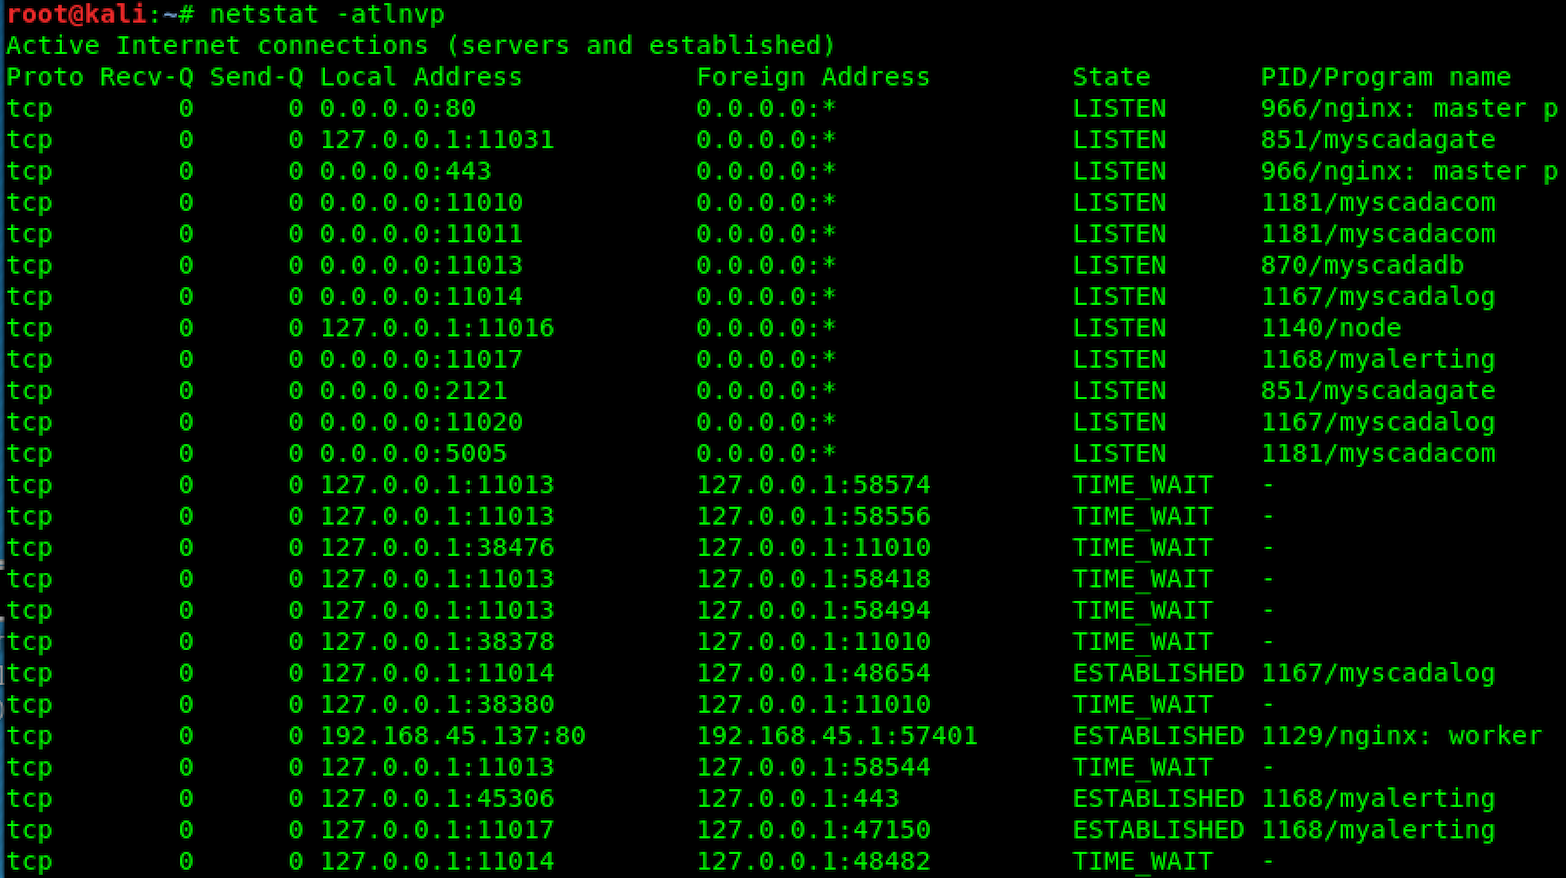
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…

User Enumeration vulnerability in Kaiten (workflow management system)

PoC - CVE-2025-24071 / CVE-2025-24054, NTMLv2 hash'leri alınabilen bir vulnerability

Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…

A vulnerability can allow an attacker to guess the automatically generated development mode secret token.

Security Vulnerability Report: CVE-2025-24071 - Windows File Explorer Spoofing Vulnerability

OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…

Proof-of-concept exploit for CVE-2025-4334, a privilege escalation vulnerability in the Simple User Registration WordPress plugin (<= 6.3), allowing…

CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…

An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords.

Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…

CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2

Proof-of-concept for CVE-2026-31282: Totara LMS login page access control bypass enabling unauthenticated brute-force credential attacks. Includes…

Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…