
e013
 keyboard-slayer/e013
VBScript tool that extracts and displays saved Wi-Fi passwords from Windows systems, outputting credentials to a text file for local access.
information-gatheringpassword-attackspost-exploitation+1
27
keyboard-slayer/e013VBScript tool that extracts and displays saved Wi-Fi passwords from Windows systems, outputting credentials to a text file for local access.
 markuta/bw-dump
A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.
 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 imthoe/cve-2019-14314
Python exploit for CVE-2019-14314: authenticated SQL injection in NextGEN Gallery 3.2.10 WordPress plugin, extracting password hashes from the…
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 duy-31/cve-2023-7028
An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 prior to 16.2.9, 16.3 prior to 16.3.7, 16.4 prior…
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 0xblarky/nextpass
A tool which can be used to generate password list or dictionary from the details of the target
 m1kb0k/cve-2022-25012-dvr4-weak-password-encryption
Decrypts weak encrypted passwords from Argus Surveillance DVR systems via CVE-2022-25012, reconstructing plaintext credentials from DVRParams.ini…
 julesbozouklian/poc_cve-2023-24055
PowerShell proof-of-concept exploit for CVE-2023-24055 that extracts cleartext passwords from KeePass by abusing trigger functionality and dumping…
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 c0gnit00/cve-2024-51482
CVE-2025-51482 POC, Dump Credentials From zm.Users
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
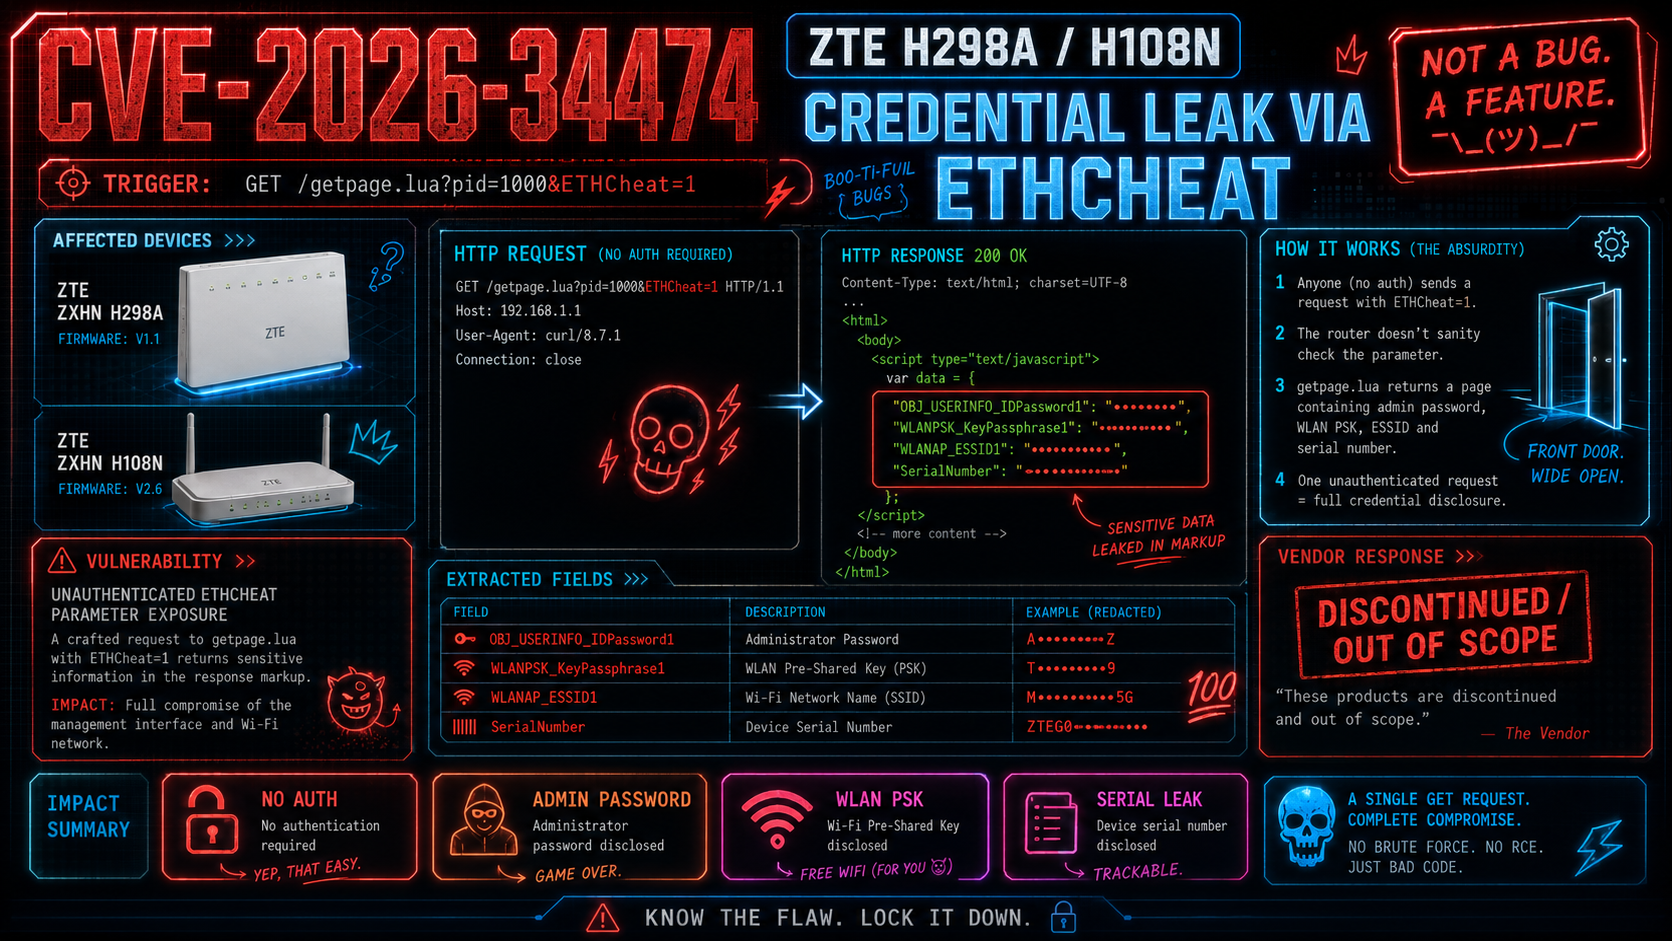 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 hell-moon/zerologon-exploit
Modified the test PoC from Secura, CVE-2020-1472, to change the machine password to null