
CVE-2017-14262
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
embedded-systems-securityexploitationiot-security+3
6
zzz66686/cve-2017-14262Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 babyshen/routeros-cve-2018-14847-bytheway
By the Way is an exploit that enables a root shell on Mikrotik devices running RouterOS versions:
 luismirandaacebedo/cve-2025-65857
Xiongmai XM530 IP Camera Hardcoded RTSP Credentials Exposure
 zzh217/cve-2018-9995_batch_scanning_exp
CVE-2018-9995_Batch_scanning_exp
 kienquoc102/cve-2018-9995-2
Python exploit for CVE-2018-9995 targeting DVR/NVR devices with login bypass, supporting reconnaissance via Shodan and Zoomeye dorks.
 legacyobj/cve-2024-24488
An issue in Shenzen Tenda Technology CP3V2.0 V11.10.00.2311090948 allows a local attacker to obtain sensitive information via the password component.
 dylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure
Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
 george0papasotiriou/cve-2026-23005-matter-commissioning-code-brute-force-without-rate-limit
Simulates a Matter commissioning code brute-force attack (CVE-2026-23005) using Python to demonstrate missing rate limiting and lockout on 8-digit…
 nanotrash/hikvision_brute
Brute Hikvision CAMS with CVE-2021-36260 Exploit
 wmasday/htc
Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995
 andripwn/cve-2018-18852
CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.
 mourafuseti/vulneravel-cve-2018-14847---credenciais-extraidas
VULNERAVEL CVE-2018-14847 - CREDENCIAIS EXTRAIDAS MIKROTIK EM PYTHON
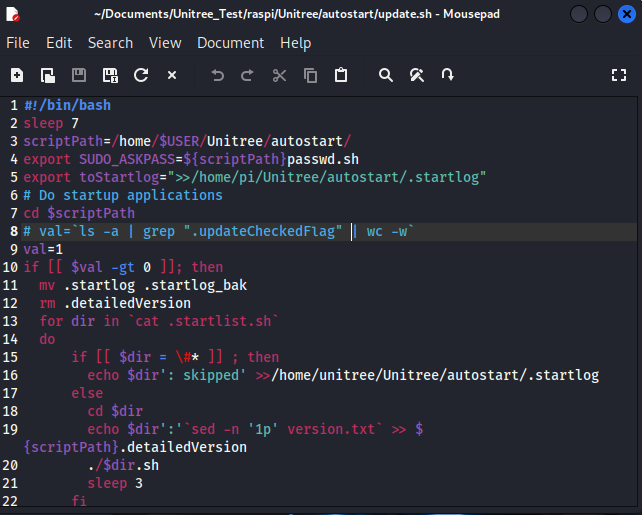 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 skylightcyber/cve-2023-28810
Exploit code for CVE-2023-28810
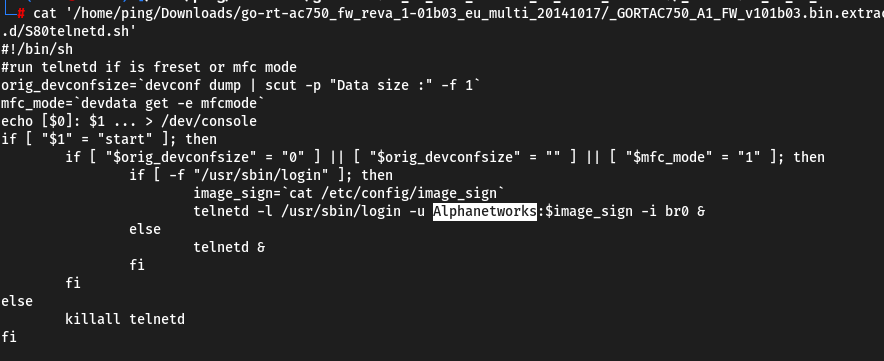 fallenskill1/cve-2024-22853
D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…
 dearpan/cve-2018-9995
Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.
