

CVE-2024-56429
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
database-securityexploitationpassword-attacks+2
lisa-2905/cve-2024-56429Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 njmbb8/cve-2024-42849
An issue in Silverpeas v.6.4.2 and lower allows a remote attacker to cause a denial of service via the password change function.
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 tiemio/ssh-key-and-rce-poc-for-cve-2021-41773
This repository contains a Proof-of-Concept for the CVE-2021-41773. This CVE contains a LFI and RCE vulnerablity.
 lucareggiannini/bludit-3-9-2-bb
Bludit 3.9.2 - bruteforce bypass - CVE-2019-17240
 jet-pentest/cve-2020-27747
Possible Account Takeover | Brute Force Ability
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
 pezwarinaan/cve-2014-0195
Exploit for CVE-2014-0195
 tieulong21prosper/detect_bruteforce
detect bruteforce using for cve-2021-34527
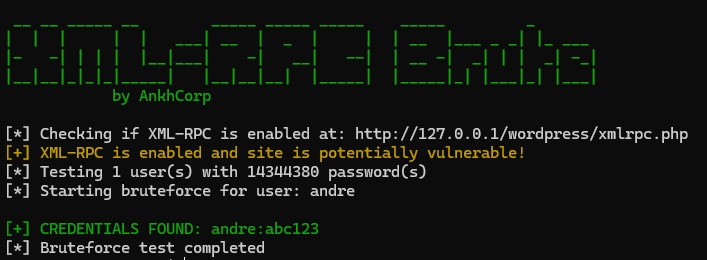 ankhcorp/xmlrpc-brute
This tool tests WordPress installations for XML-RPC authentication vulnerabilities.
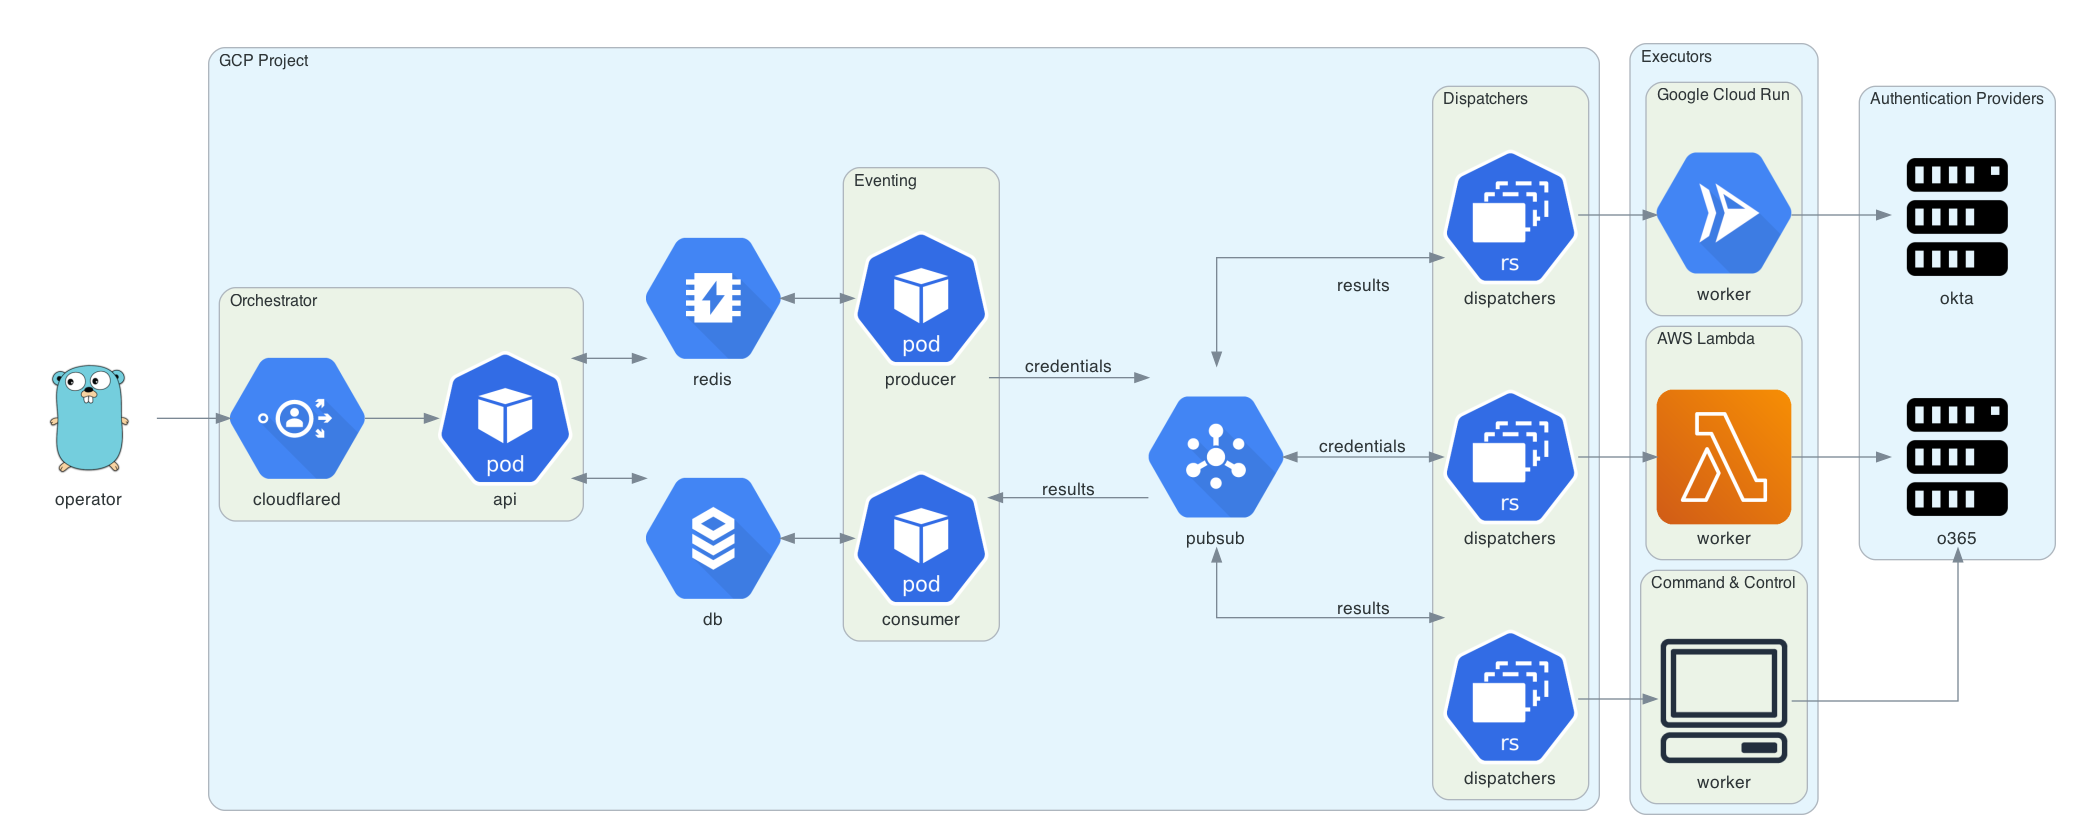 praetorian-inc/trident
automated password spraying tool
 securityriskadvisors/msspray
Password attacks and MFA validation against various endpoints in Azure and Office 365