
CVE-2024-29868
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
cryptographyexploitationpassword-attacks+3
1
devisions/cve-2024-29868Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…
 daeda1usuk/cve-2025-59390-
CVE-2025-59390 and ThreadLocalRandom Inverse
 remenis/cve-2025-63666
Tenda AC15 cookie exposure
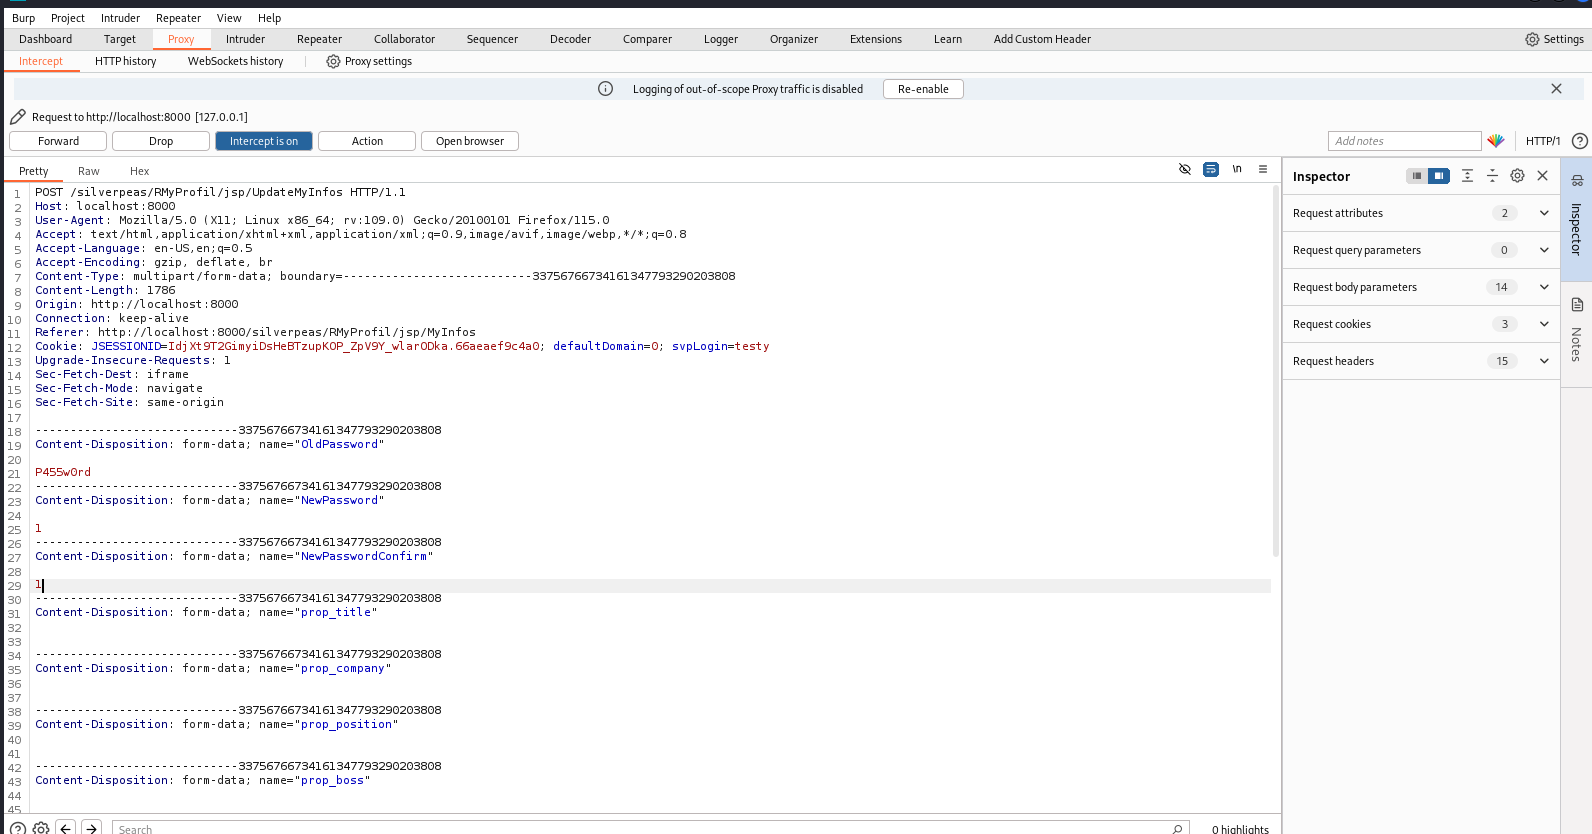 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 spyx/cve-2019-17240
Go-based brute-force tool exploiting Bludit bruteforce mitigation bypass (CVE-2019-17240) for automated password cracking against admin login pages.
 jenderal92/wordpress-default-password
python 2.7
 teteuxd2/cve-2025-5095-poc
Python POC for CVE-2025-5095
 manuelz120/cve-2021-45041
PoC for CVE-2021-45041
 triple-octopus/bludit-cve-2019-17240-fork
Better version of rastating.github.io/bludit-brute-force-mitigation-bypass/
 m4rm0k/cve-2019-16113
Bludit 3.9.2 - Remote command execution - CVE-2019-16113
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 0xvedette/cve-2020-12712
Decrypts passwords stored in SOS JobScheduler (S)FTP profiles by exploiting the use of the profile name as the 3DES encryption key, enabling recovery…
 tiemio/ssh-key-and-rce-poc-for-cve-2021-41773
This repository contains a Proof-of-Concept for the CVE-2021-41773. This CVE contains a LFI and RCE vulnerablity.
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 njmbb8/cve-2024-42849
An issue in Silverpeas v.6.4.2 and lower allows a remote attacker to cause a denial of service via the password change function.
 pezwarinaan/cve-2014-0195
Exploit for CVE-2014-0195
 lucareggiannini/bludit-3-9-2-bb
Bludit 3.9.2 - bruteforce bypass - CVE-2019-17240