
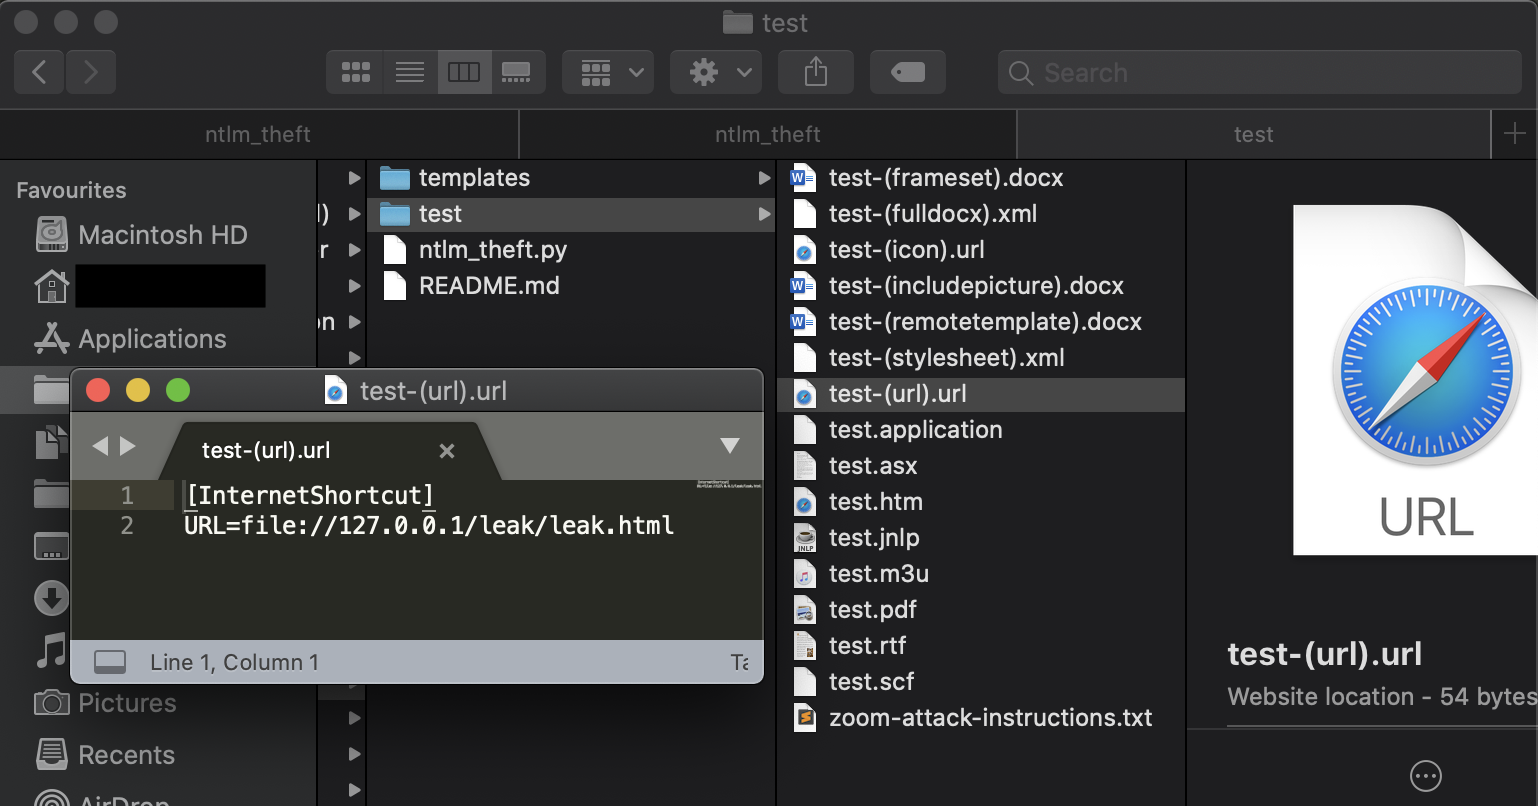
ntlm_theft
 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
information-gatheringpassword-attackspenetration-testing+2
1.5k
greenwolf/ntlm_theftA tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
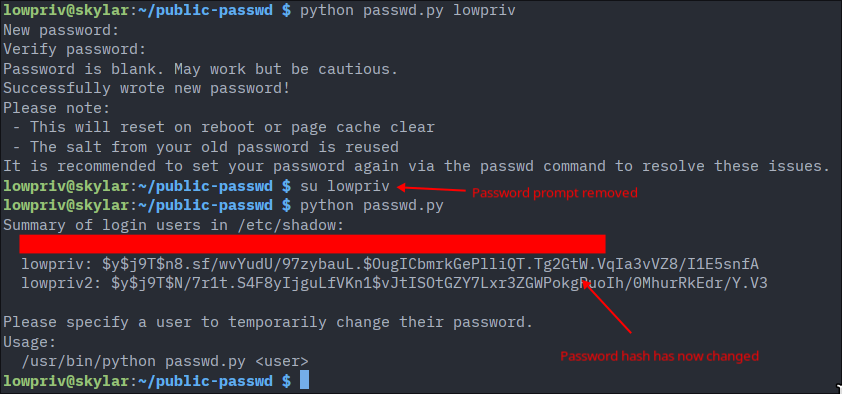 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
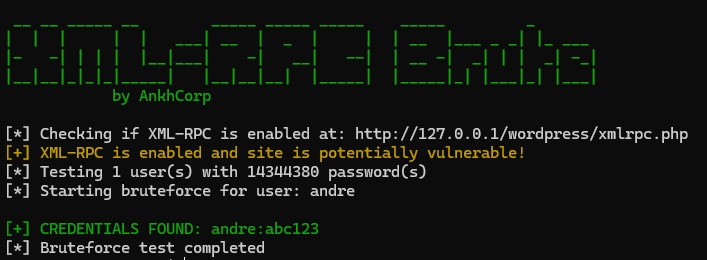 ankhcorp/xmlrpc-brute
This tool tests WordPress installations for XML-RPC authentication vulnerabilities.
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 eremiel/cve-2019-5420
Python exploit script for CVE-2019-5420, targeting Ruby on Rails signed-session AES GCM key brute-forcing to achieve remote code execution in…
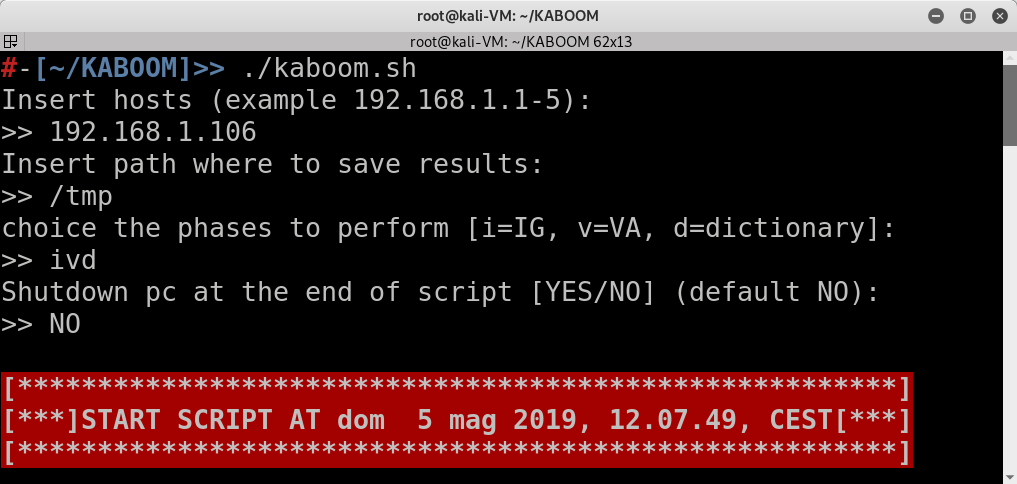 leviathan36/kaboom
A tool to automate penetration tests
 atarantini/wpbf
Remotely test password strength of WordPress bloging software