
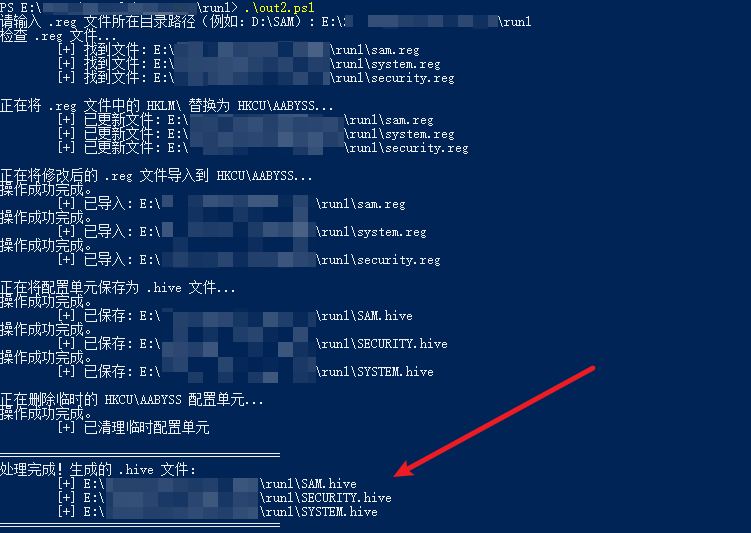
HashDump-BypassEDR
 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
hash-analysisids-ips-evasionpassword-attacks+3
261
aabysszg/hashdump-bypassedrWindows绕过EDR实现DumpHash
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 fin3ss3g0d/secretsdump.py
Enhanced version of secretsdump.py from Impacket. Adds multi-threading and accepts an input file with a list of target hosts for simultaneous secrets…